Electronic Signatures Meet Mathematical Contracts
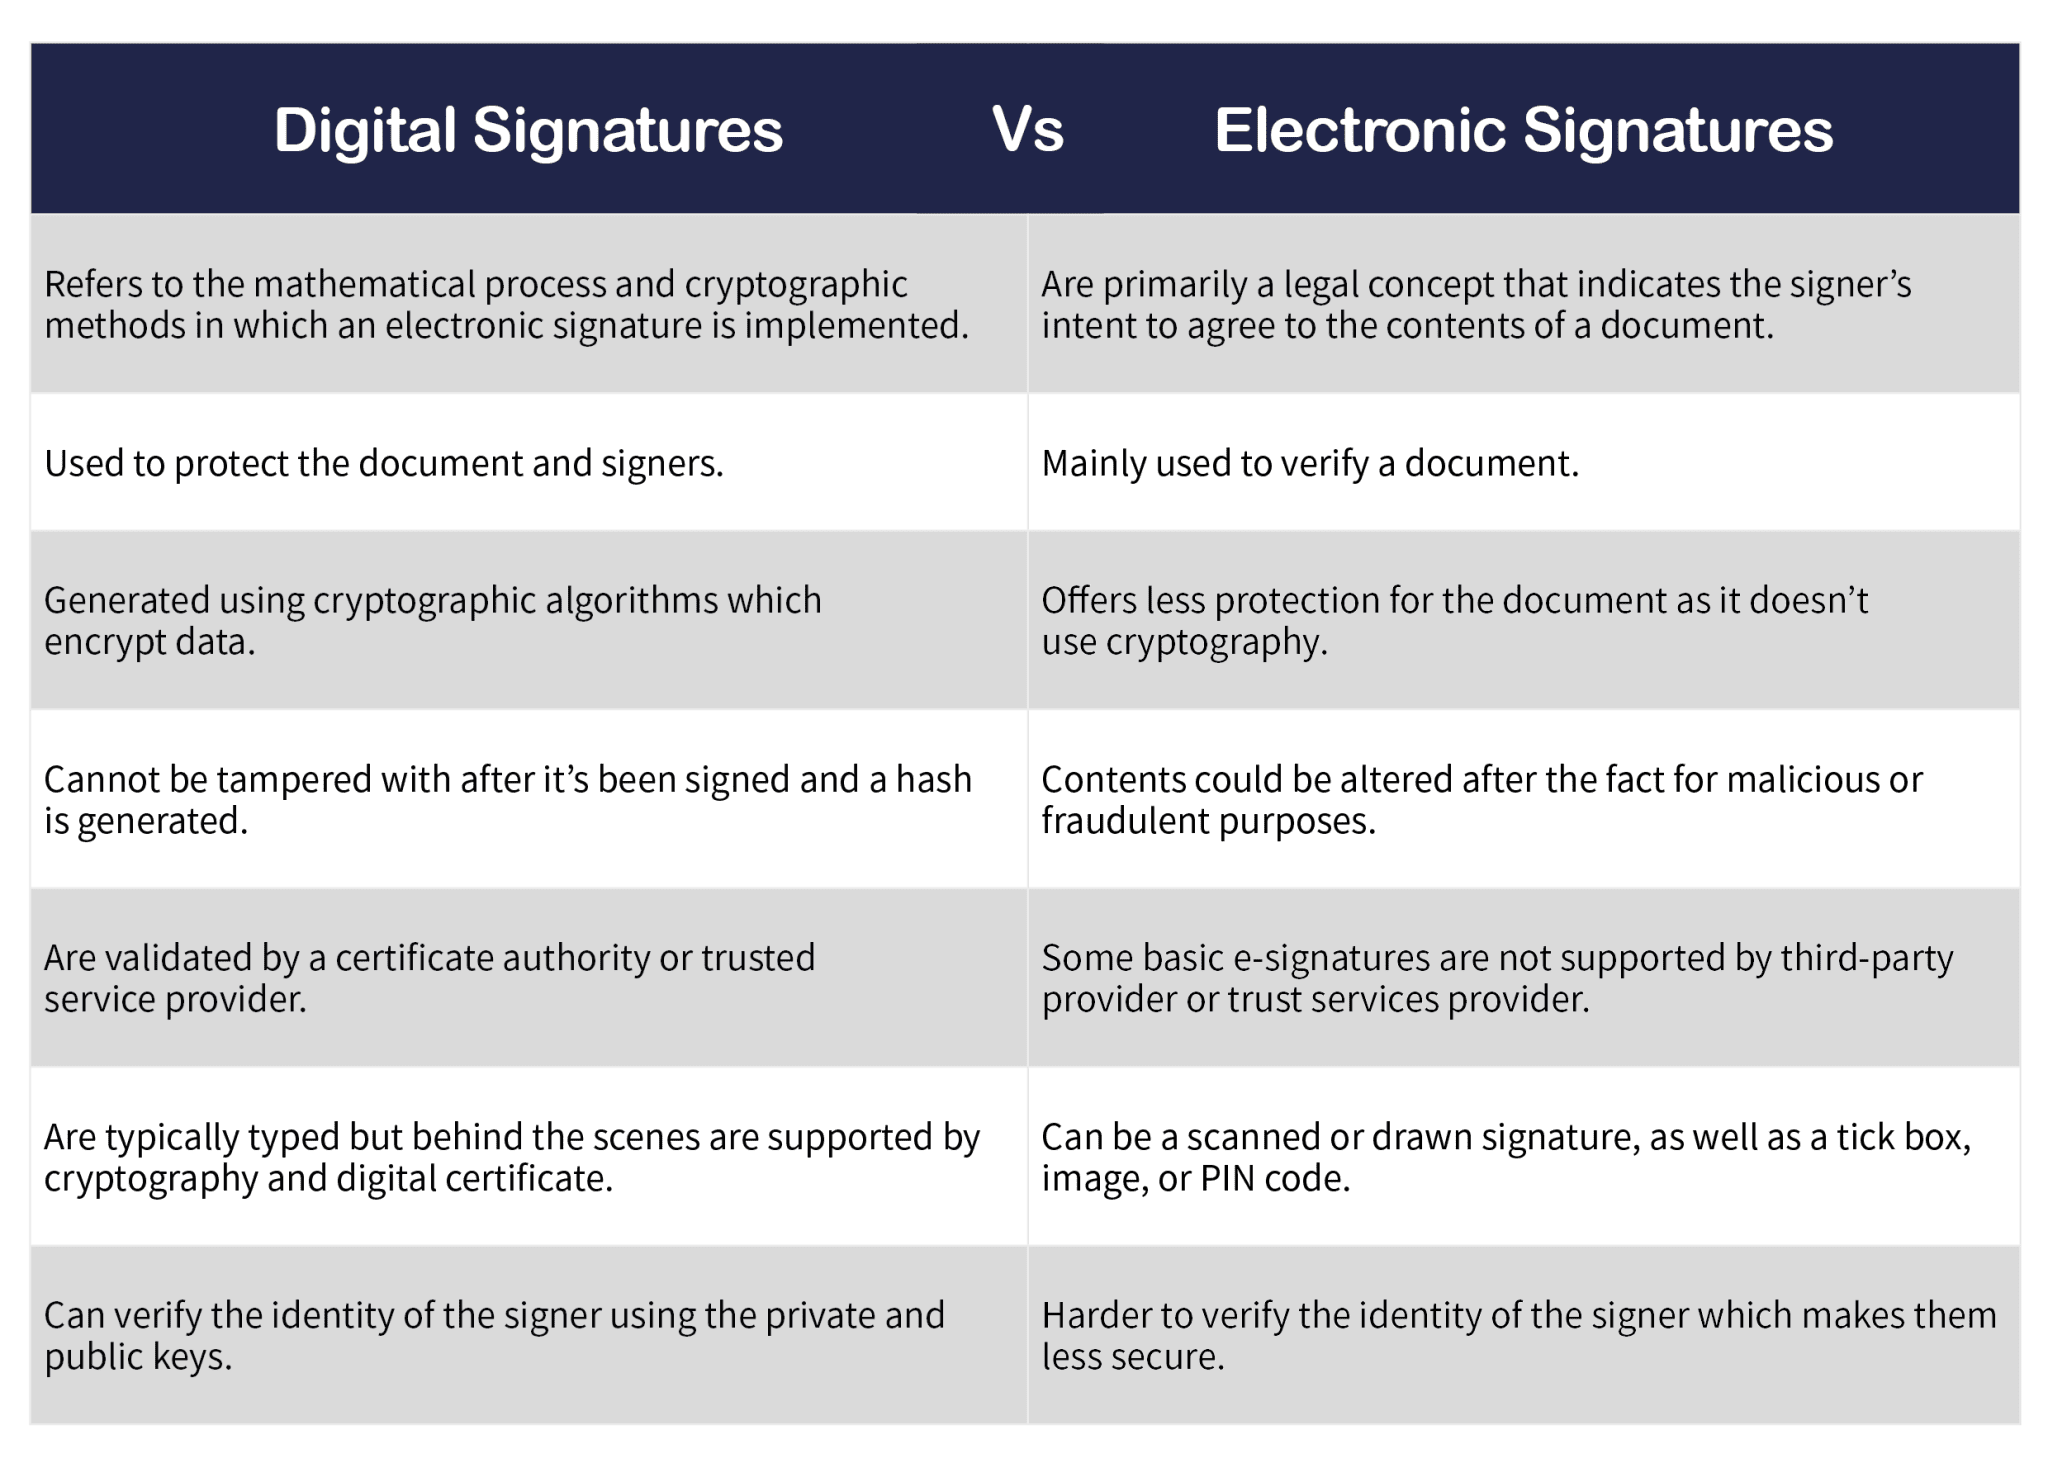
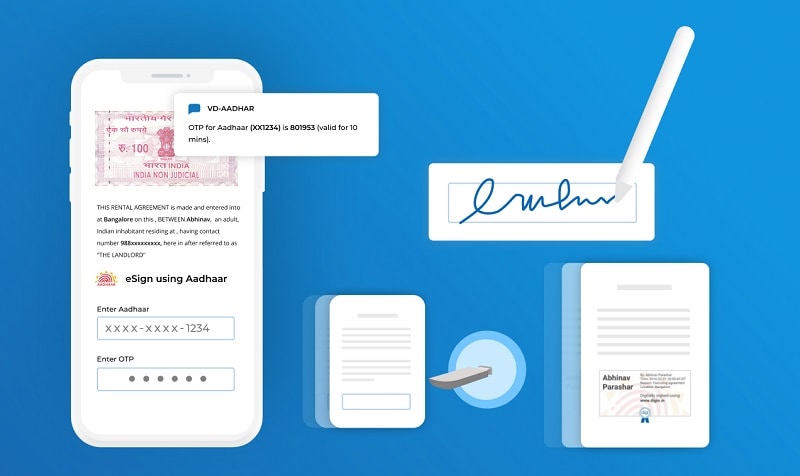
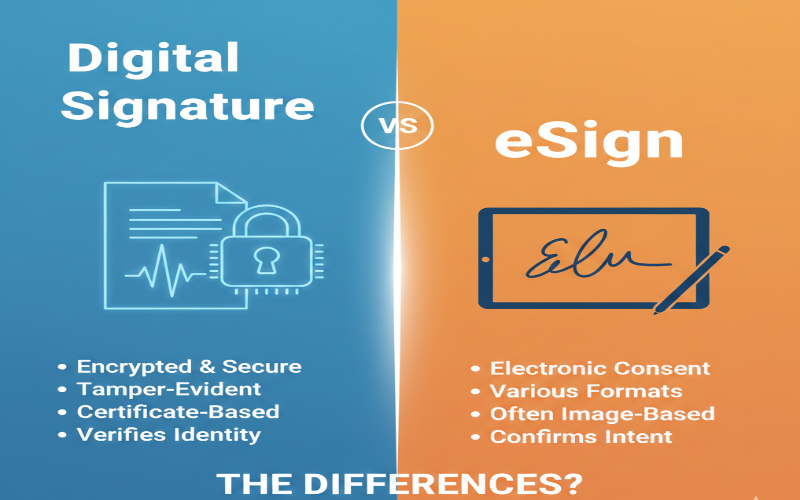
The intersection of e-signatures and mathematical verification isn't the flashiest topic in compliance technology, but it's where most enterprise failures happen. I've spent years watching companies implement digital signature workflows for contract math and then discover six months later that the signatures were valid but the underlying calculations were compromised. That's the problem this guide addresses. The Digital Frontier Of Esign Math How Electronic Signatures Are Revolutionizing Mathematical Verification And Contractu is less about the signatures themselves and more about ensuring the mathematical content those signatures protect hasn't been altered after the fact. A standard electronic signature using PKI-based technology signs a hash of the document. That hash is then encrypted with the signer's private key. When someone verifies the signature, they decrypt the hash with the public key and compare it to a newly computed hash of the received document. If they match, the document is intact and the signature is valid. This works fine for a PDF contract. It falls apart when the contract contains embedded calculations, dynamic spreadsheets, or formulas that can be re-evaluated. The core issue is what we call post-signature compute drift. I encountered this firsthand when a logistics company sent me their freight rate model. The spreadsheet was signed with a qualified e-signature under eIDAS. Everything looked valid on the surface. But the sheet contained Excel formulas that pulled from external API endpoints for fuel surcharges. Someone accessed the document three months after signing, changed a cell reference from the live API to a cached static value, and resubmitted. The signature still validated because the document had been properly signed when originally executed. But the numbers were completely different. The signature proved authenticity of the signed state, not correctness of the live computation.
The workaround I settled on was adding a secondary checksum layer. I required signers to include a separate integrity manifest file computed from the exact same formula state at signing time. This manifest used HMAC-SHA256 with a shared secret known only to the mathematical auditor. When verifying, you run the formulas in a sandboxed environment, compute the HMAC, and compare it to the manifest. If they diverge, the document may be signed but the math is suspect. This isn't standard practice in any e-signature platform I know of. It's something you build yourself on top.
The Practical Workflow For Signing Math-Heavy Contracts
Here's how this actually plays out in a real enterprise setting. A manufacturing company needs to sign a long-term supply agreement where pricing formulas depend on commodity indices. The contract isn't just a static document. It's a living model that recalculates quarterly. First, you establish what's called a binding computational snapshot. Before any signature is applied, the entire mathematical model is exported as a deterministic artifact. This means no external API calls, no volatile functions, no cell references that change based on system time. Every input is frozen into the document or an attached data package. The model is then rendered as a static representation alongside the editable version. Think of it as taking a photograph of the math at a specific moment in time, signed and sealed. Second, you apply the e-signature to both the static snapshot and the editable model. Most platforms support multi-signature regions. You sign the immutable version to establish a baseline. Then you sign the editable version to allow for authorized updates. The audit trail captures both signatures separately. This is critical because a single signature on a document with dynamic formulas creates ambiguity about what exactly was agreed to.
Get the Full Details

Third, you implement a formula integrity hash. This is different from the document hash. The document hash covers the file structure, formatting, and text. The formula integrity hash covers the actual computational logic. For Excel-based contracts, this means hashing the formula strings themselves, not the calculated values. Calculated values can change legitimately. Formula strings changing is suspicious. Python-based mathematical contracts require hashing the source code alongside the signature payload. I recommend using a separate hashing step rather than relying on the e-signature platform's built-in integrity checks. Those checks are designed for document preservation, not mathematical auditability. Fourth, you set up periodic re-validation. Quarterly or annually depending on the contract terms, an independent party should load the model, run it against frozen inputs, and verify the output matches the originally signed snapshot. Any variance triggers a review. This is where most companies skip steps because the process feels tedious. Don't skip it. I've seen three separate disputes arise from exactly this gap. The signatures were technically valid throughout. No one caught that the formulas had been incrementally modified across multiple revision cycles until a dispute required forensic examination.
Platform Selection And Technical Requirements
Not every e-signature platform handles mathematical contracts equally. DocuSign and Adobe Sign are the big names. They work fine for standard contracts. For anything involving live calculations, formula dependencies, or dynamic pricing models, you need a platform that supports custom metadata fields, structured audit trails, and API-accessible integrity data. DocuSign's API allows you to attach custom fields to envelope events. Adobe Sign offers similar capabilities through its Acrobat Sign API. Both let you store supplementary files alongside signed documents. That supplementary file is where your formula integrity manifest lives. If your contracts involve blockchain-based verification or smart contract logic, the landscape shifts. Some companies use hybrid approaches where the e-signature authenticates human consent while a separate on-chain hash validates the computational model. This adds cost and complexity but provides a higher assurance tier for high-value agreements. I'd only recommend it for contracts exceeding a certain threshold value or involving regulated industries. For standard commercial agreements, the four-step workflow above is sufficient. You also need to think about who can execute formula changes. A signed contract with dynamic pricing needs a change control process. I recommend defining this explicitly in the contract itself. The clause should state that any modification to pricing formulas requires re-execution of the full signature workflow, including both the human signature and the formula integrity hash update. Without this clause, a signatory can claim they never agreed to modified terms even if the technical audit trail shows the changes. Courts generally side with the signed document, but contractual language strengthens your position significantly.
Where This Approach Breaks Down
I want to be blunt about the limitations. The workflow I've described requires manual steps that don't scale well. Generating formula integrity hashes, maintaining snapshots, and running periodic re-validations takes engineering resources. Most legal teams don't have staff for this. The typical result is that companies either implement the full workflow on a handful of high-value contracts and ignore it for everything else, creating an inconsistent compliance posture. Or they skip it entirely and rely on the e-signature platform's default document-level hashing, which as I noted doesn't catch post-signature formula manipulation. Another hard limitation is platform dependency. If you build your formula integrity system around a specific e-signature platform's API, and that platform changes its data structure or retires the endpoint, your entire verification chain breaks. I've dealt with this. A client moved from one platform to another and lost three years of comparative audit data because the JSON schema for envelope metadata changed between versions. Always design your integrity manifests to be platform-agnostic. Store the hash artifacts as standalone files that can be verified independently of whichever e-signature provider you're using at any given time. The third limitation is the human factor. Even with perfect technical controls, someone can override the workflow. I've watched it happen. A project manager at a mid-size firm bypassed the formula integrity check because the quarterly re-validation was delaying a shipment contract. She said the vendor had already signed and the formulas hadn't changed. They hadn't changed in her assessment. The vendor's internal team had updated a parameter two weeks prior. The discrepancy didn't surface until the invoice arrived at an incorrect amount. The cost of the error exceeded the cost of the delay by a factor of ten. Process discipline matters as much as technical controls.

What To Do If You Don't Have Engineering Resources
For smaller organizations that can't build custom integrity systems, there are simpler approaches. One is using spreadsheet software with built-in version tracking and mandatory signature checkpoints. Excel's modern co-authoring features log formula changes with timestamps and user attribution. Pair this with an e-signature platform that stores the spreadsheet as a native file rather than flattening it to PDF. PDF flattening destroys formula integrity because the formulas become static rendered values. Always keep the native file format when dealing with mathematical contracts. Another option is using contract lifecycle management platforms that include mathematical validation modules. These are niche products but they exist. They automate the snapshot and re-validation steps I described above. The trade-off is reduced flexibility and higher licensing costs. For a small company signing fewer than twenty math-intensive contracts per year, the CLM route may be more efficient than building a custom solution. For a larger organization with hundreds of contracts, the custom approach pays for itself within the first year through avoided disputes and reduced forensic audit costs. The bottom line is that e-signatures alone are insufficient for mathematical contracts. The signature proves who signed and that the document hasn't been corrupted since signing. It doesn't prove that the formulas inside are correct, current, or unmodified. Adding a formula integrity layer on top of the e-signature closes that gap. It's not something any mainstream platform offers out of the box. That's why you need to build it or buy a tool that does. The alternative is assuming your signed contract is fully protected when it's actually leaving a significant verification blind spot.
Implementation Checklist
If you're moving forward with this, here's what you need to have in place before your next signing. First, define the scope of your mathematical contracts. Identify which agreements contain formulas, dynamic calculations, or references to live data sources. Don't try to apply this to every contract. It only matters where the math is material to the agreement. Second, choose your e-signature platform and verify API access for custom metadata and supplementary file storage. Third, build or procure a formula integrity manifest generator. This can be a simple Python script that extracts formula strings from Excel workbooks and computes SHA-256 hashes. Fourth, draft the contract clause requiring re-execution upon formula modification. Fifth, train the relevant team on the re-validation schedule and escalation procedures. The hardest part isn't the technical setup. It's getting legal and operations to agree on the process and stick to it. Most of the friction I see comes from operations teams treating the formula integrity step as bureaucratic overhead. They're right to push back if the process adds more time than it saves. The key is measuring the right metric. You're not saving time on individual signings. You're preventing disputes that take months to resolve. The ROI shows up in reduced legal exposure, not in faster contract execution. Frame it that way and you'll get better buy-in.