
So KTP Digital Identity Unlocking Actually Exists Now
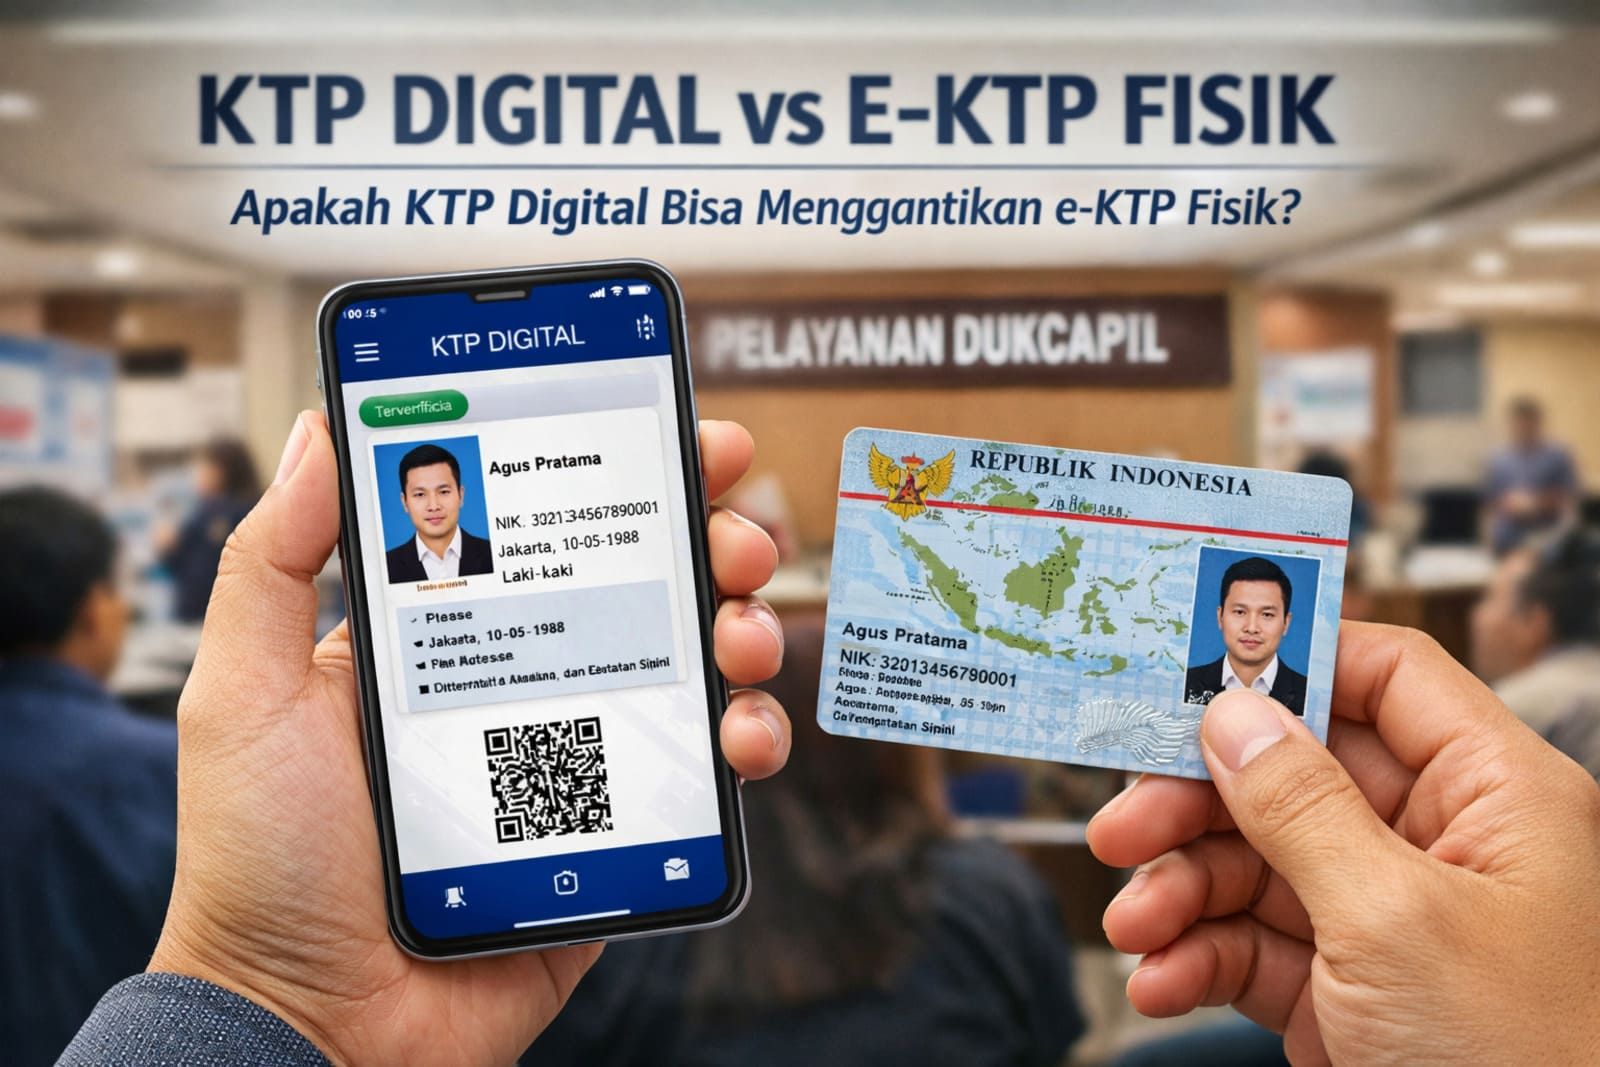
I first ran into this when my city's digital ID system got migrated to the new platform. The transition window was rough. People who hadn't synced their accounts within fourteen days found their previous credentials locked out entirely. I spent three evenings troubleshooting a handshake failure between the old KTP database and the newer verification layer that turned out to be a certificate rotation issue the helpdesk hadn't communicated clearly about. KTP stands for Kartu Tanda Penduduk, Indonesia's national identity card system. The digital unlocking piece refers to the biometric-linked API layer that lets government services, banks, and private platforms verify identity through facial recognition, fingerprint scans, and sometimes voice samples instead of physical document checks. It's not a single product you download. It's a protocol stack.
The Dawn Of KTP Digital Unlocking A Safer Smarter Future Of Identification
Here's how the actual flow works when you're implementing it or using it on the backend. The citizen presents their KTP number through a verified channel. That number gets hashed with a session-specific salt and sent to the Dukcapil server. The server returns a signed challenge token. The client then performs the biometric check against their registered template and sends the hash back. If the cryptographic signature validates and the match score clears the threshold, the service gets an OAuth-style access token scoped to whatever verification level the relying party requested. The verification level part matters more than people realize. KTP digital unlocking has three tiers: Level 1 is just name plus KTP number and photo. Level 2 adds fingerprint verification. Level 3 requires facial liveness detection and sometimes a voice sample. Most apps asking for "KTP verification" are only doing Level 1, which means a fraudster who scraped a KTP photo from a public database could theoretically pass it if the integration doesn't enforce liveness checks. I learned that the hard way when a test environment I was auditing accepted a high-resolution printed photo of a KTP as a valid liveness pass because the developer had set the anti-spoofing threshold too low during staging. We caught it before production, but it should have been caught by automated testing.
What You Actually Need To Integrate It
There is no universal KTP digital unlock SDK you can pull from GitHub. Dukcapil controls the access. You need to apply through their developer portal as an institutional partner, which means your organization has to be a registered government agency, licensed financial institution, or approved telecom provider. Individual developers and most startups get rejected during the compliance review phase. The compliance requirements are substantial. You need SOC 2 Type II certification or its Indonesian equivalent, a data protection impact assessment filed with the relevant authority, and your systems have to pass a penetration test conducted by an accredited third party before they'll even give you sandbox credentials. For the technical side, you'll be working with REST APIs that expect XML envelope formats for most requests, which is genuinely painful in 2024. The response payloads use signed JWTs with specific claim structures. The authentication flow between your server and Dukcapil's uses mutual TLS, so you need to provision certificates through their CA and rotate them every ninety days. Missing a rotation window will silently break your integration until you notice the auth failures piling up.
Get the Full Details
The rate limits are strict. Production endpoints typically cap at around fifty requests per minute per institution. If you're building something that needs bulk verification, like a payroll integration for a mid-size company, you'll hit that wall fast. We built a queuing layer with local retry logic and a small caching window for already-verified identities that reduced our outbound calls by roughly seventy percent during peak periods.
The Real Limitations Nobody Talks About
KTP digital unlocking only covers Indonesian citizens with valid KTP cards registered in the Dukcapil system. That excludes several million people. Migrant workers from other countries use different document types. Some remote communities in Papua and eastern Indonesia still have unresolved registration issues where the physical KTP exists but the biometric template was never properly enrolled or got corrupted during data center migrations. I ran into a case where a legitimate applicant's verification failed repeatedly because his fingerprint ridge patterns had degraded from manual labor, and the system's match score kept dropping below the 82% threshold. There's an appeal process through local Dukcapil offices, but it takes six to eight weeks and requires an in-person visit. During that window, the person can't access any government or banking services that rely on KTP digital verification. Another problem is the lateral trust issue. Passing KTP digital unlock verification proves the person is who they say they are at the moment of verification. It does not prove they are who they were at any prior point in time. Session hijacking, credential theft, and SIM swap attacks still work exactly as they always have. KTP digital unlocking solves one specific problem, not identity security broadly.
A Practical Workflow For Getting Started
If your organization qualifies for institutional access, here's the order that actually works without wasting months on the wrong sequence. Get your compliance documentation ready first. Dukcapil reviews your application alongside your legal and security paperwork, and incomplete submissions just sit in a queue indefinitely. While that processes, build your integration against the sandbox environment. The sandbox mirrors production behavior closely enough that catching format errors there saves significant rework later. Implement the certificate rotation logic before you ever touch production. I cannot stress this enough. Every integration I've seen that hit production without automated cert rotation broke within the first year, usually during a weekend when nobody was watching. Set up your own audit logging from day one. Dukcapil's servers will log your requests, but you need your own immutable audit trail for compliance purposes and for debugging when something goes wrong at 2 AM and you need to prove whether the failure was on your side or theirs. We use a simple append-only log table with hashed digests of each verification request and response pair. It takes maybe an afternoon to implement and has saved us during two separate incident investigations.

Plan your fallback path. Not every user will pass KTP digital verification on the first attempt. Have a secondary verification method ready, whether that's a manual document review queue, a phone-based OTP system, or a partnership with another identity provider that can serve as a backup for edge cases Dukcapil's system can't handle cleanly. The technology itself is solid. The verification accuracy for clean cases is high, and it has genuinely reduced identity fraud in sectors that adopted it early. But the implementation surface is narrow, the access barriers are high, and the operational overhead is consistently underestimated by teams that treat it like a standard third-party API integration. It isn't. Factor in the time, compliance costs, and ongoing maintenance before you commit to building on top of it.


