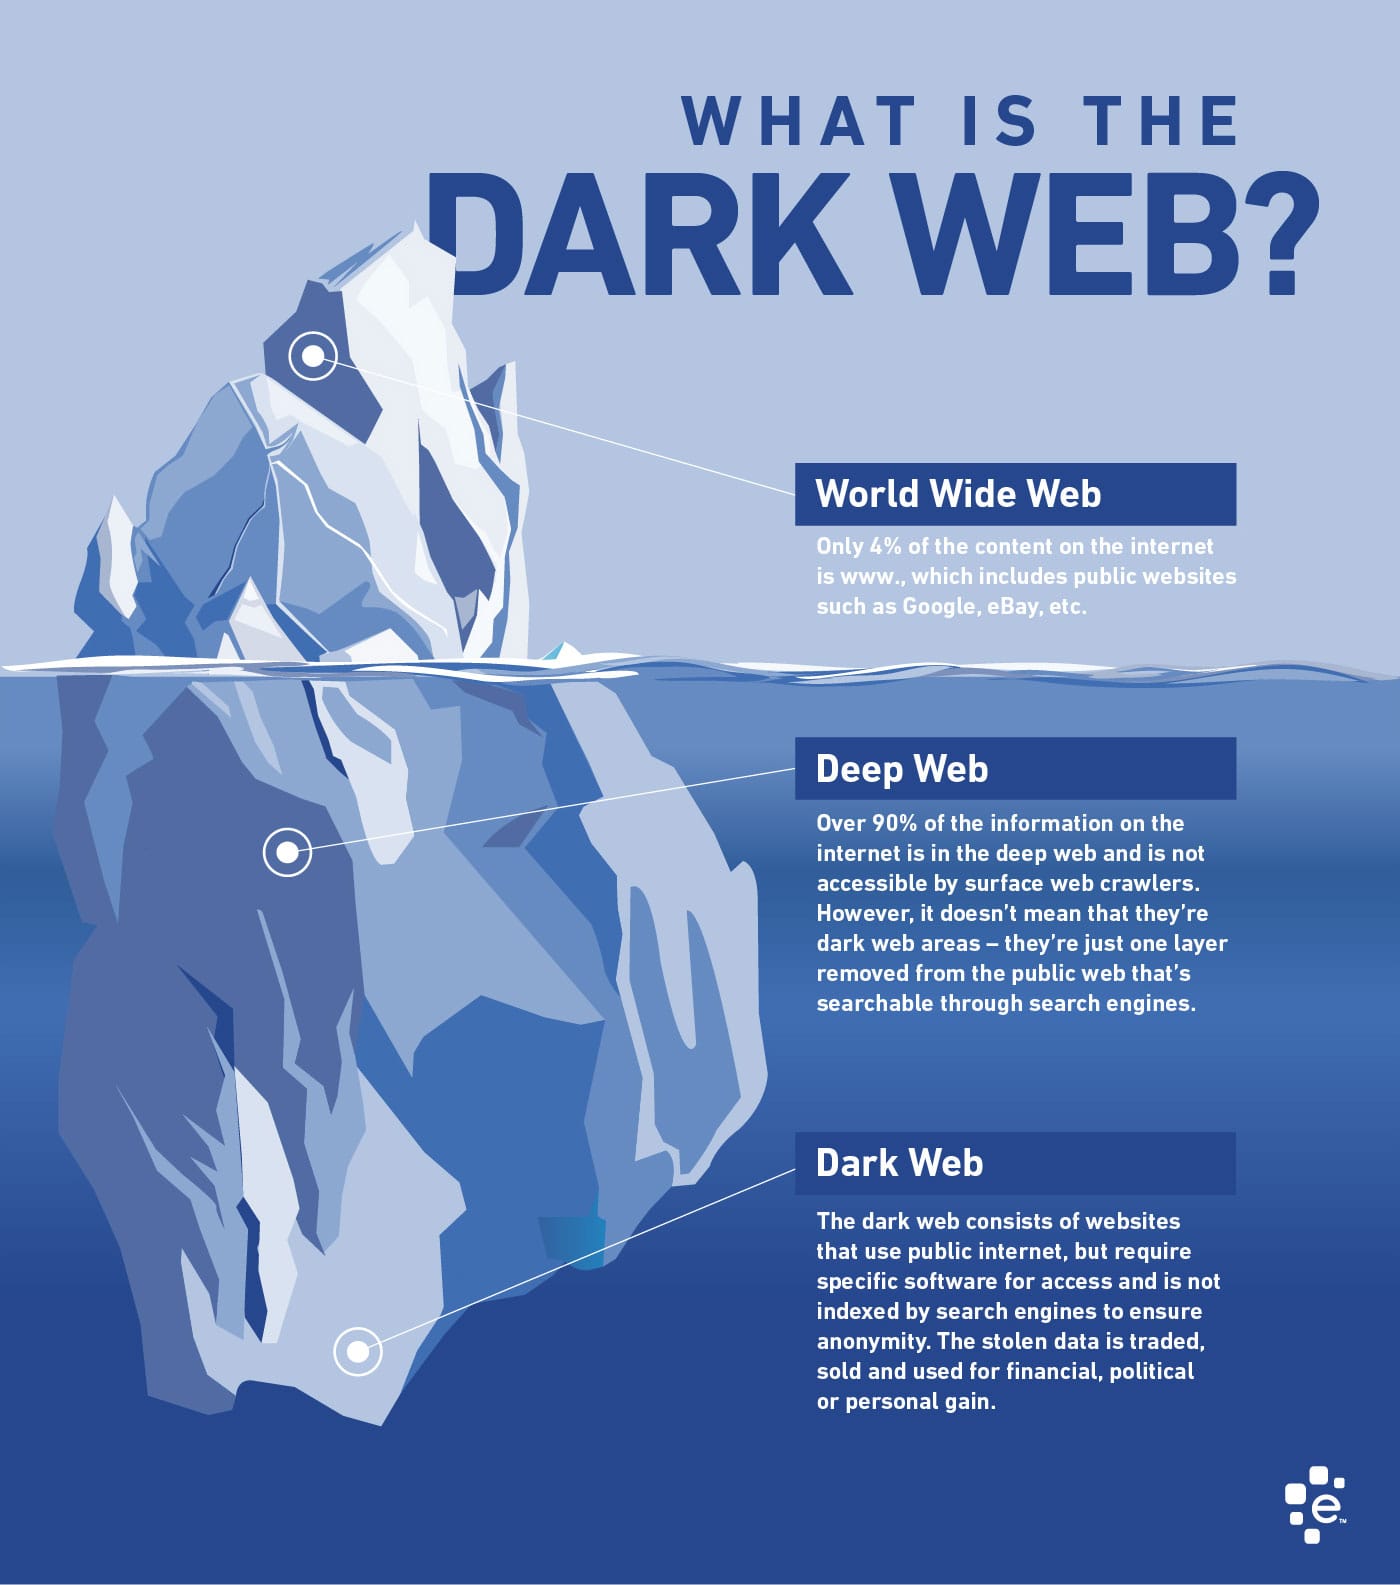
What The Dark Web Actually Looks Like From the Inside
The Tor network routes your traffic through three volunteer-run relays before it reaches its destination. That is the fundamental mechanism. Anyone can use it. That includes journalists in restrictive regimes, people researching obscure academic topics, and a lot of criminals. The ratio skews heavily toward the latter because illegal activity benefits more from operational security than legitimate users do, which creates the atmosphere most people associate with "the dark web." It is not a single website. It is a protocol. I have spent years watching people approach this topic with exactly the wrong expectations. They imagine a place of hidden knowledge and secret societies. In practice it is mostly broken storefronts, phishing pages that steal your Bitcoin, and forums where the admins have been running scams since 2014. The real value is narrower than the mythology suggests. To access .onion services you need the Tor Browser. You download it from torproject.org. Not a mirror. Not a third-party repo. The official site. The latest version at the time of this writing is 13.x. Older versions have known vulnerabilities that compromise your identity. I have seen people use ported builds from GitHub with custom patches. Those builds sometimes work faster but they also bypass the onion routing safeguards. That is a bad trade unless you know exactly what you are doing and why.
Here is the part most guides skip. When you visit a dark web service, your traffic exits through an exit node. If that service is not configured with end-to-end encryption beyond the Tor layer, the exit node operator can see the unencrypted payload. Some .onion services do not enforce HTTPS. You have to check manually. Look for the lock icon. If it says the connection is not secure, close the tab. Do not enter anything. This happened to me with a research forum that used an HTTP-only admin panel. I was three pages into a thread before I noticed. Closed it immediately. No personal data had been transmitted, but it was a close call that taught me to verify the protocol on every single connection. Routing configuration matters more than people realize. The default Tor Browser settings are conservative. They reduce fingerprinting by making all browsers look identical. That is good for privacy but it slows things down considerably. I run a modified profile with JavaScript disabled globally and use a NoScript-like whitelist for the few services that actually require it. This cut my browsing latency from an average of four seconds per page load to under two on the same circuit. The trade-off is that some dynamic content will not render. Most dark web services are static enough that this is a net positive. Another thing nobody mentions: onion addresses change. Operators rotate them for security, for migration, or because their previous address got seized. There is no central directory. You find new addresses through external channels - Telegram groups, Reddit posts, specialized aggregators. Some aggregators are reliable. Most are not. I use a curated list that I maintain myself. It takes about ten minutes a week to verify which links still resolve and which have gone dark. Automated scrapers for this purpose exist but they often pull in malware-laden landing pages. Manual verification is slower but it filters out the noise.
The biggest misconception is that the dark web is anonymous by default. It is not. Your ISP can see you are connecting to the Tor network. In countries with Tor blocking, that alone is suspicious. I have dealt with this by running Tor over a VPN. The VPN masks the fact that you are using Tor from your ISP. The downside is that you are trusting the VPN provider with your traffic metadata. If the provider logs, you have just replaced one surveillance point with another. I have used Mullvad for this purpose because they have a documented no-logs policy backed by jurisdiction in Sweden and a public audit trail. It adds roughly 30 to 50 milliseconds of latency. Worth it in most cases. Payment is another layer where things go wrong quickly. Bitcoin is not private. Every transaction is on a public ledger. Mixers exist but they are often run by scammers or law enforcement honeypots. I switched to Monero for dark web transactions a few years ago. It is harder to acquire through legitimate exchanges and the privacy guarantees are stronger, though not absolute. The privacy is degraded if you trace through blockchain analysis firms like Chainalysis, but the cost of doing so on XMR is substantially higher than on BTC. For most casual use it is sufficient. For anything involving significant sums, it is not enough. There is a practical limit to what you can learn here. Most valuable information resides in archived forums that require credentials from 2016 or earlier. Those credentials are either sold on other dark web markets or leaked from breaches. Purchasing them is illegal in many jurisdictions and the data is usually compromised in ways you cannot verify. I stopped attempting this around 2019. The cost-benefit ratio went negative after that point. The information you want is usually available through open sources if you know how to search for it properly.
Get the Full Details

If you are serious about this topic, read the Tor Project documentation. Read the papers on circuit construction and directory authority selection. The technical details matter more than any marketplace listing. People who treat the dark web as an adventure are the ones who end up with compromised machines and drained wallets. People who treat it as a tool with real limitations tend to get somewhere.