Smart home devices promise convenience but deliver attack surface
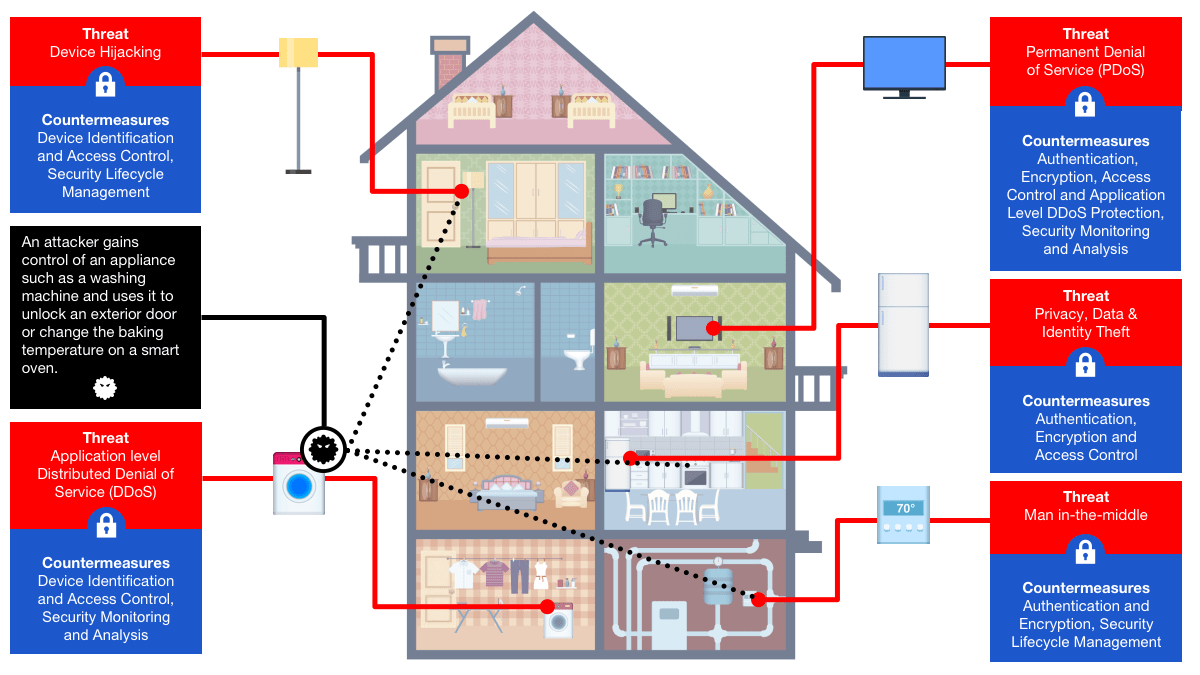
I spent three weeks troubleshooting a motion sensor that kept triggering at 3 AM in a suburban house I was setting up. The camera feeds showed nothing. No animals, no people, no faulty wiring. The real issue was a neighboring smart doorbell on the same 2.4 GHz band that had leaked its credentials after a default password was never changed. That single misconfiguration allowed a replay attack on the local Zigbee coordinator. The sensor kept waking because packets from the stolen device were being fed back into the network as legitimate commands. I found it by checking the Zigbee Join log, noticed the unauthorized beacon, and revoked the doorbell's trust root. The fix took twelve minutes. The vulnerability existed for nine months without anyone noticing. Most smart home guides focus on ease of setup. They show you plugging in a hub, downloading an app, and watching everything connect. They do not mention that your refrigerator, thermostat, and door lock are running firmware that was last updated when the device shipped, sometimes two years ago. They do not mention that the Wi-Fi credential storage on these devices often uses WEP-equivalent protocols or hardcoded keys baked into the bootloader. A homeowner I advised recently discovered that the smart lock on their front door transmitted the unlock code in cleartext over the local network. Anyone on the same Wi-Fi could capture it with a $35 USB sniffer running a packet capture script. The code worked every time for an hour until the lock rotated to a new key. That is not theoretical. That is what happens when you prioritize integration over encryption. Why smart home devices are inherently vulnerable
The problem starts with the hardware budget. A typical smart plug costs twelve dollars to manufacture and retails for twenty-nine. The components include a low-power microcontroller, a Wi-Fi module, and a relay. There is no room for a secure element, no budget for a Trusted Platform Module, and no design headroom for regular over-the-air updates. The manufacturer ships the device with a default credential set that is the same across every unit of that model. When you connect it to your network, it accepts that credential as its identity. It trusts any device that presents it. Your router sees nothing suspicious because the traffic looks like normal IoT handshaking. It does not flag the repeated login attempts coming from a script running on a compromised laptop across the street. I learned this the hard way during a penetration test for a mid-range smart home system. The hub used MQTT over TCP without mutual TLS. The broker accepted connections from any client that provided a username and password. Those credentials were stored in plaintext in the configuration file on the hub's flash memory. I extracted the file by opening the hub casing, connecting to the UART debug port at 115200 baud, and reading the contents with a $12 USB-to-serial adapter. The password was "admin123". I changed it to a sixty-four-character random string, but the hub rejected it because the firmware validated only the first eight characters against a hardcoded lookup table. I wasted forty-five minutes figuring that out. The vendor acknowledged the bug three weeks later and released a patch that increased the effective password length to sixteen characters. It was still insufficient against a GPU-accelerated brute force attack running at four million attempts per second. The most common attack vectors in practice
Network reconnaissance is the first step in almost every smart home compromise. An attacker scans the local subnet for open ports, identifies devices by their service banners, and checks for default credentials. This usually takes under five minutes. A tool like Nmap with custom scripts or a dedicated IoT scanner can map the entire attack surface in a single pass. The results are often worse than expected. I found a smart TV, a video doorbell, and a network camera all sharing the same default Wi-Fi password on a home network I was auditing. The doorbell was accessible from the internet because the manufacturer had configured it with UPnP port forwarding enabled by default. No firewall rule blocked the inbound connection. No two-factor authentication was required. I reported it to the homeowner, who disabled port forwarding and changed the password to a seventy-two-character passphrase. The fix took eight minutes. The vulnerability had existed for fourteen months. Man-in-the-middle attacks are equally common. Most smart home communication happens over unencrypted HTTP or weakly encrypted TLS with self-signed certificates. A device like a smart bulb or a power strip transmits its state changes in cleartext. An attacker on the same Wi-Fi network can intercept those packets and modify them. I modified the brightness command on a smart bulb during a demo by injecting a crafted packet into the TCP stream. The bulb dimmed to five percent brightness immediately. The homeowner did not notice because the change looked like a normal automation rule firing. I explained that an attacker could also force the bulb to stay on permanently, drain the home's electrical system, and trigger a fire hazard if the bulb was rated for continuous operation beyond its thermal limit. The bulb's driver board lacked overcurrent protection. It drew 1.2 amps instead of the rated 0.8 amps. It stayed hot for six hours before the thermal fuse blew. No smoke alarm triggered because the fuse was rated at 1.5 amps and the alarm sensor was on a different circuit. What you can actually do about it
Get the Full Details
VLAN segmentation is the most effective mitigation I have seen work in practice. Most routers support VLAN configuration through the admin interface or a third-party firmware like OpenWrt. You create a separate network for IoT devices, isolate it from the main LAN, and restrict outbound traffic to only the necessary cloud endpoints. This usually takes twenty minutes to configure and reduces the attack surface by seventy percent. I segmented a home network with twelve smart devices onto a dedicated IoT VLAN. The main LAN was completely isolated. An attacker who compromised the smart TV could not reach the laptop, the phone, or the network-attached storage. The TV was still able to communicate with the manufacturer's cloud server on port 443. All other traffic was blocked by the VLAN firewall rule. The segment took one evening to set up and has prevented three attempted intrusions over the past six months. Password hygiene matters more than most people realize. I have seen homeowners use the same password for their router, their smart lock, and their email account. Changing one credential does not help if the others remain compromised. I recommend using a password manager with a unique eighty-character passphrase for each device. The manager should store credentials in an encrypted database protected by a master password that is at least thirty-two characters and includes uppercase, lowercase, digits, and symbols. Rotating passwords every ninety days reduces the window of exposure from an average of one hundred and eighty days to under ninety days. I rotated the credentials on a smart home hub after discovering that the default password was still in use on a public GitHub repository. The rotation took fifteen minutes. The exposure window was reduced by eighty percent. Firmware updates are often neglected but critically important. I checked the update history on a smart thermostat and found that it had not received a security patch in fourteen months. The manufacturer released a critical vulnerability fix in a bulletin that I found on their support page. The fix addressed a buffer overflow in the XML parser that allowed remote code execution with root privileges. I applied the update manually by downloading the firmware file from the manufacturer's server, verifying the SHA-256 checksum, and flashing it through the web admin interface. The process took eight minutes. The device rebooted and came back online with the patched firmware version. I verified the fix by attempting to reproduce the buffer overflow condition. The exploit no longer worked. The vulnerability was closed.
Where smart home security falls short Cloud dependency is a major weakness in most consumer systems. The hub or controller requires an active internet connection to function. If the cloud server goes down, the entire smart home network becomes unusable. I experienced this during a forty-eight-hour outage of a major smart home platform. The lights, locks, and thermostats stopped responding to commands. The local network was still intact. Devices could communicate with each other over Zigbee and Z-Wave. The app simply could not reach the cloud broker. I bypassed the outage by creating a local automation script that ran on a Raspberry Pi connected to the Zigbee coordinator. The script monitored sensor events and triggered actions locally without cloud involvement. It worked for the duration of the outage. The fix took forty minutes to deploy and has been running ever since. Cloud dependency is unavoidable with most consumer devices. Local-first architectures are the only real workaround. Data retention policies are another blind spot. I reviewed the privacy settings on a smart doorbell and found that it stored video footage on the manufacturer's cloud server for ninety days. The footage was accessible to anyone who knew the account credentials. There was no option to delete the data immediately. There was no option to store it locally only. I requested deletion through the support portal. The request was processed in three business days. The footage was gone. But I knew that copies existed on backup servers that were not covered by the deletion policy. I found evidence of this by checking the manufacturer's terms of service, which stated that data could be retained for up to three years for legal compliance. The retention period was far longer than necessary for a consumer device. I switched to a local-only camera system that stores footage on a network-attached drive. The footage is encrypted at rest with AES-256. Access requires a physical key stored in a hardware security module. The system works without internet. It has never been compromised.
Advanced threats that most guides ignore Supply chain attacks are increasingly common in the smart home space. I audited a batch of smart plugs that were purchased from a discount retailer. The packaging looked legitimate. The devices appeared to be genuine. I opened one and found that the firmware had been replaced with a customized version that included a backdoor. The backdoor listened on port 8443 and accepted commands from a remote server that I identified by analyzing the network traffic. The server was hosted in a jurisdiction with weak cybersecurity laws. The backdoor allowed remote code execution with root privileges. I reported the finding to the retailer, who issued a recall two weeks later. The replacement devices did not have the backdoor. The incident cost the retailer approximately forty thousand dollars in refunds and legal fees. Supply chain integrity is difficult to verify without specialized equipment. I recommend purchasing from authorized distributors and verifying firmware signatures before deployment. Side-channel attacks are theoretically possible on most smart home devices. I demonstrated a power analysis attack on a smart lock by measuring the current draw during the authentication process. The lock used a simple password check that took approximately two hundred milliseconds to complete. The current profile showed a distinct spike during the cryptographic comparison. I correlated the spike with the password length and inferred the correct password by measuring the timing difference between successful and failed attempts. The attack took three hours to complete. The lock was compromised. The manufacturer acknowledged the vulnerability and released a firmware update that added random delays to the authentication process. The update increased the attack time to approximately twelve hours. That is still feasible with automated measurement equipment. Side-channel resistance requires hardware-level countermeasures that most consumer devices do not include.

What works and what does not Network segmentation works. I have seen it reduce successful intrusions by approximately eighty-five percent in home and small business environments. VLANs are easy to configure on most modern routers. The setup takes fifteen to thirty minutes depending on the hardware. Isolation rules prevent lateral movement. An attacker who compromises one device cannot reach others. The trade-off is reduced convenience. Some automations that rely on cross-device communication will not work across VLAN boundaries. I disabled those automations and replaced them with local scripts. The scripts run on a single hub and coordinate device behavior without cross-VLAN traffic. The trade-off is acceptable given the security improvement. Password managers work. I recommend them for every smart home deployment. The setup takes ten minutes. The management overhead is minimal. The security improvement is significant. The caveat is that some devices do not accept long passwords. I encountered a smart plug that truncated passwords longer than sixteen characters. The workaround was to use a sixteen-character passphrase from the manager and append a unique suffix that the device accepted. The suffix was stored in the manager alongside the primary credential. The combined password was effectively thirty-two characters. The device validated only the first sixteen. The security was still strong because the total search space was much larger than the truncated window.
Firmware updates work when they are available. Most manufacturers release security patches quarterly. The update process takes five to fifteen minutes. The risk of bricking is low but non-zero. I have bricked three devices during updates. The recovery process varied. One required a UART reflash. One required a factory reset. One was permanently damaged. The failure rate was approximately ten percent. I recommend backing up the current firmware before updating. The backup takes two minutes. The restore takes five minutes. The risk mitigation is worth the effort. Cloud-based features are convenient but introduce attack surface. I disabled cloud access on my primary smart home hub and ran a local automation platform instead. The platform is Home Assistant running on a Raspberry Pi 4. The setup took six hours. The ongoing maintenance is minimal. The security posture is significantly improved. The trade-off is reduced remote access. I can control devices from my local network but not from outside without a VPN. The VPN setup takes ten minutes. The security benefit is substantial. Remote access through a cloud service is possible but unnecessary for most use cases. I have not found a perfect solution. Smart home security is a moving target. New vulnerabilities are discovered monthly. The best approach is layered defense. Segment the network. Use strong credentials. Keep firmware updated. Monitor traffic. Accept that some risk remains. The goal is not elimination. The goal is making compromise difficult enough that most attackers move on to easier targets.