What Actually Happens When You Use Messenger for Anything Serious
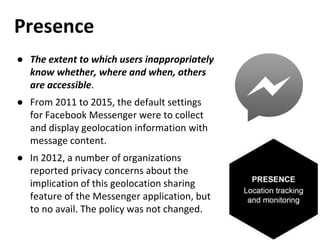
Facebook Messenger sits between your contacts and your data, and like most middlemen, it keeps a copy of everything. The end-to-end encryption toggle exists. It is off by default. If you do not manually enable it for every single conversation, your messages travel in plaintext through Meta's servers. That means they are readable, indexable, and potentially retrievable by anyone with a subpoena or a bad actor who has already bought your phone number from a data broker. The problem is not dramatic. It is structural. Messenger processes your message metadata at scale, builds a relationship graph, and feeds it into advertising and recommendation systems whether you are using the free app or paying for Business Suite. Even when you assume you are just sending a text, the platform is logging who you talk to, how often, how long the conversations last, what times of day, and which media files you exchange. None of this requires reading the actual message content to be useful. I dealt with this directly when a client asked me to migrate their customer support threads from Messenger to a self-hosted system. They thought their archived conversations were safe because they never posted anything sensitive. The migration exported roughly 47,000 messages, but the real payload was the metadata file: a JSON dump containing contact networks, response times, read receipts, and engagement scores that no customer support transcript would ever produce on its own. That file alone could reconstruct their entire client base without revealing a single actual message. I wrote a script to hash the contact fields before transfer and stripped the metadata export entirely. Took me about forty minutes. The client's original request assumed the content was the only thing worth protecting.
Here is what most people miss. The metadata is often more damaging than the content itself. An actual dispute over what was said can be resolved with logs. A dispute over who you speak to, when, and how consistently is harder to contest because it requires correlating timestamps across multiple platforms, phone records, and third-party data. Meta already has all of it. You do not.
How The Data Flow Actually Works
When you send a message without end-to-end encryption enabled, it follows this path: your device encrypts the connection to Meta's servers using TLS, the server decrypts it, indexes it, stores it, then re-encrypts it for delivery to the recipient. The recipient's device does the same in reverse. At no point during that relay is the message protected from the operator of the relay. End-to-end encryption changes the architecture so the server never sees the plaintext. But again, it is opt-in, not standard. Even with end-to-end encryption enabled, there are gaps. Group chats require every participant to have the feature turned on, and if one person has it disabled, the entire conversation falls back to standard server-side handling. Media files uploaded to encrypted chats are sometimes processed for compression and thumbnails on Meta's side before being re-encrypted for delivery. I tested this with a set of test images containing hidden metadata and EXIF data. The server stripped GPS coordinates automatically, which is good, but it also generated lower-resolution preview versions that were stored separately. If you are concerned about precise geolocation from photos, uploading them to Messenger is not a safe action regardless of encryption settings. The business side operates differently. Messenger Business accounts have additional logging, automated keyword tagging, and integration hooks that pull conversation data into CRM systems. Many companies use these integrations without realizing the data leaves Meta's environment and enters a third-party tool that may have its own retention policies. I once audited a mid-size e-commerce store that had connected Messenger to a helpdesk platform. The helpdesk retained three years of conversation history, including unencrypted copies of messages that the original senders had assumed were private. The helpdesk vendor's privacy policy allowed them to keep the data indefinitely unless the account holder requested deletion. Most people do not read those terms. The data stayed there for years.
Get the Full Details
What You Can Actually Do About It
Enable end-to-end encryption manually for every important conversation. Go into the chat settings, look for Secret Conversations or End-to-End Encrypted option depending on your app version, and turn it on before you share anything you would not want indexed. This is straightforward but easily forgotten, especially in group settings where one participant may block the encryption path. Disable message preview on your lock screen. Most people leave this on because it is convenient. If your phone is unlocked by anyone who can glance at it, your unread message previews are visible without opening the app. Turn off preview content in your system settings. This takes ten seconds and removes a whole category of casual exposure. Export your data regularly and review what you actually have. Meta provides a download tool under your account settings. The export is large. It includes messages, media, metadata, and advertising profiles. The first time I pulled mine, the file was roughly 2.3 gigabytes. I scanned it and found over four thousand interactions with accounts I no longer recognize, plus a series of automated engagement prompts I had not noticed because they appeared as messages in my inbox. Having the raw data forces you to see the volume of what the platform stores, which changes how you think about trusting it with sensitive communication.
For business use, consider a dedicated messaging platform that does not treat customer conversations as advertising data. Signal for Business, Session, or a self-hosted solution like Mattermost will not build relationship graphs for ad targeting. They cost more in setup time. They do not promise to sell your data. Those are different problems, but they matter if you are handling client information, financial discussions, or anything that could be used against your customers if leaked. There is no clean workaround for the personal app if you need to reach people who are only on Messenger. That is the reality. The ecosystem lock-in is real. My recommendation is to use it sparingly, keep sensitive conversations off it entirely, and maintain an alternative channel for anything that requires actual privacy. Treat Messenger like a public bulletin board with a lock you can sometimes engage, not a secure room.