Why Your Password Manager Isn't Saving You Anymore
The last three years of my incident response work have involved watching organizations get hit by attacks that would have been unthinkable five years ago. It's not that threats got smarter in isolation. The problem is how quickly the attack surface has expanded for average users and enterprises alike, combined with AI lowering the barrier to entry for people who previously couldn't write functional exploit code. I've seen small businesses get locked out of their own data within twenty minutes of a phishing email being opened. The time between initial access and ransomware deployment keeps shrinking every quarter. I need to be blunt about something most security articles won't tell you. Password managers are a false sense of security if you're using them wrong. Here's what actually matters: multi-factor authentication, network segmentation, and endpoint detection that can catch lateral movement before it becomes a breach. Most people focus on the wrong layer. They buy the most expensive password manager on the market and leave their corporate VPN running on personal devices with unpatched software. That's like bolting your front door while leaving the back window wide open.
The Alarming Rise Of Cybersecurity Threats Protecting Your Digital Life
Threat actors are no longer just targeting banking credentials. They're going after supply chains, cloud configurations, and identity providers. A single compromised vendor can expose thousands of downstream customers. When you hear about a data breach affecting millions of people, the initial compromise was almost never direct. It went through a third-party service provider, a misconfigured S3 bucket, or an API endpoint that someone forgot to patch. The average dwell time before detection in 2024 was still over eighty days for mid-sized organizations. I spent two weeks last year helping a logistics company remediate a breach that started with a single unpatched virtual private server they'd spun up for a temporary vendor project. The box was in a public subnet, running an outdated version of Apache, and the credentials were hard-coded into a configuration file. Someone brute-forced the SSH port, planted a cryptominer, and then used that server as a pivot point into their internal network. It took them three weeks to find it. The fix wasn't dramatic — it was closing the VPC routing table, rotating every credential that had touched that environment, and implementing proper asset discovery so nothing ever gets forgotten again.
What Actually Works Right Now
Network segmentation is the single most effective control available, and it's also the least implemented. I see too many organizations treating their entire infrastructure as a flat network where a compromised workstation can reach the domain controller. If you segment properly, a ransomware infection on the marketing VLAN stays on the marketing VLAN. It doesn't spread to accounting, HR, or the production database. This isn't theoretical. I've seen it work in live incidents where a breach was contained to a single isolated segment because the network architecture forced the attacker to jump multiple hops with no lateral trust paths. Implement zero-trust principles at the application level, not just the network level. This means every service authenticates every other service, regardless of whether it's inside or outside the perimeter. Mutual TLS between microservices, short-lived certificates, and policy-based access controls that evaluate context like device health and location, not just identity. Most organizations stop at SSO and think they've solved the problem. They haven't. SSO is a convenience feature, not a security control. Email security is another area where people dramatically overestimate their protection. SPF, DKIM, and DMARC are baseline requirements, not solutions. I've watched attackers bypass three-layer email gateways using CEO fraud templates written by GPT-4 variants. The emails looked professional, used correct branding, and came from domains that had passed every automated check. The only reason we caught that one was behavioral analysis flagging an unusual outbound payment request at 2:47 AM from a CFO who typically processes payments between ten and four.
Get the Full Details
The Technical Ground Rules
Keep a current asset inventory. This sounds stupid until you're trying to respond to an active compromise and you can't find the server that's actually infected because someone documented it as a test environment and never updated the records. Automated discovery tools like NetBox, Nmap scans with daily schedules, and cloud asset management platforms can keep this current. The goal is knowing everything that exists on your network within a forty-eight-hour window. Endpoint detection and response (EDR) is table stakes now. But EDR alone doesn't prevent breaches. It detects them faster. Pair it with a SIEM that correlates events across endpoints, network traffic, and cloud logs. A successful detection pipeline looks at a process spawning a reverse shell on one endpoint, correlated with a DNS query to a known malicious domain from another host in the same subnet, correlated with an anomalous authentication event three hours earlier from the same user account. One of these events in isolation is noise. All three together is a confirmed compromise. Backup strategy is where most people fail. You need immutable backups. Not copy-on-nas that can be accessed and encrypted by ransomware. Not cloud backups with the same credentials as your primary systems. Immutable backups are write-once-read-many storage that cannot be modified or deleted within a retention window. I've seen three separate organizations lose data to ransomware in a single quarter because their "backups" were on the same network they were trying to protect. The attackers found them, encrypted them, and the organizations had nothing to restore from.
Where Security Falls Apart
Zero Trust architectures don't scale well for small organizations. The complexity of implementing micro-segmentation, certificate management, and policy enforcement across a large environment is real. For a team of twenty people, the overhead of a full Zero Trust implementation often costs more in engineering time than the actual security benefit justifies. A hybrid approach makes more sense: segment what you can, enforce MFA everywhere, maintain clean backups, and monitor aggressively. Don't try to build a fortress. Build layers. AI-powered security tools have a significant blind spot. They're trained on historical threat data, which means they're excellent at detecting known attack patterns but poor at identifying novel techniques. I've seen WAFs and IDS systems completely miss zero-day exploit attempts because the payloads didn't match any known signature. Human analysts reviewing alerts are still necessary because they can connect dots that pattern-matching engines miss. A threat hunter noticing that a user account is making API calls at unusual hours from a geographic location that doesn't match their travel history is doing something no automated system reliably catches yet. Compliance frameworks like SOC 2, ISO 27001, and NIST provide structure but don't guarantee security. I've audited organizations that were fully compliant and still suffered breaches through vectors that weren't covered by their compliance scope. Compliance checks boxes. Security requires continuous validation. Penetration testing, red team exercises, and purple team drills are what actually reveal gaps. A checklist review will tell you that you have a backup process. A successful restore test during a simulated breach tells you whether that process actually works when your operations depend on it.
Practical Steps for Individuals
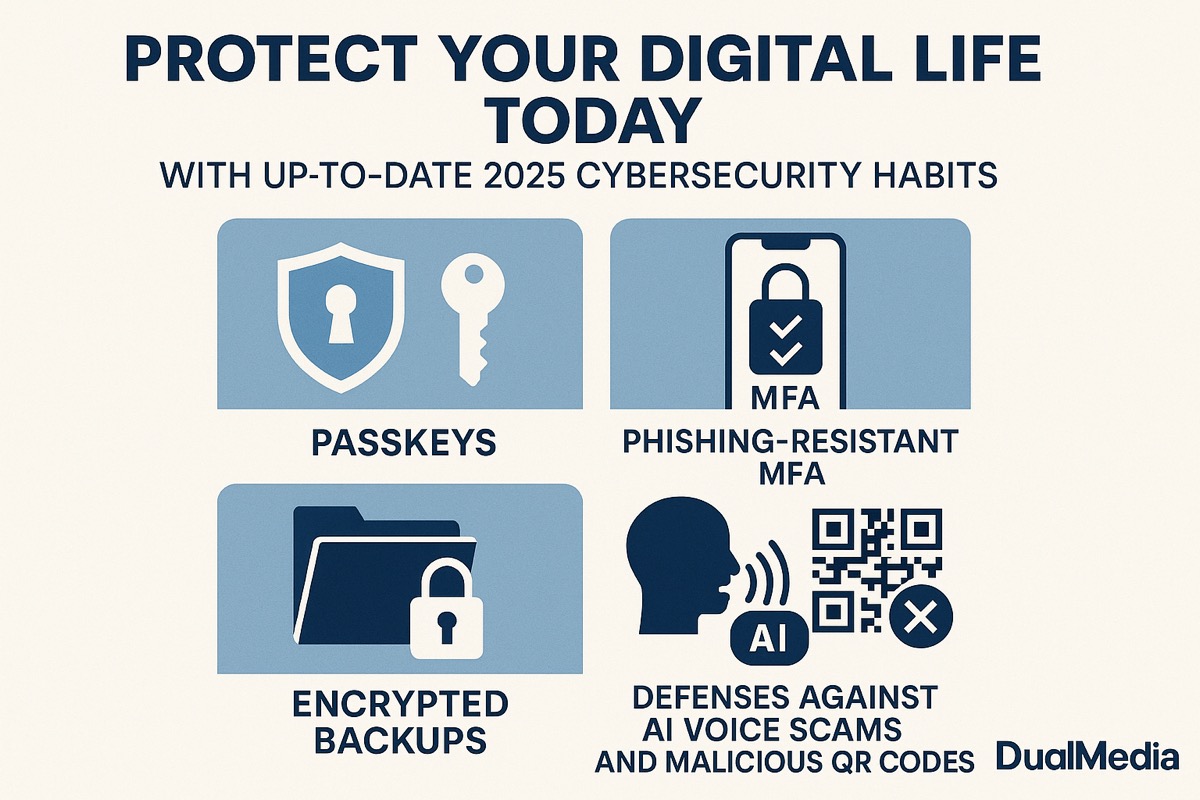
Use a password manager with a hardware security key for your primary accounts. YubiKeys or similar FIDO2 devices prevent phishing attacks because the authentication token is bound to the specific domain. A password entered on a lookalike phishing site won't authenticate because the security key checks the origin. This one change eliminates the most common attack vector by far. Enable multi-factor authentication everywhere. Not SMS-based authentication if you can avoid it. SIM-swapping attacks are real and well-documented. Use authenticator apps or hardware keys. I've had clients whose phones were physically lost and their accounts accessible because they relied on SMS codes. Anyone who can intercept a text message can intercept the authentication code. Authenticator apps generate codes locally. They can't be intercepted in transit. Keep your systems patched. Automatic updates should be enabled on every device that touches your network. I've seen ransomware infections that started with unpatched PrintNightmare vulnerabilities on workstations that hadn't been rebooted in six months. The patch was available. The organization just never enforced it. Update policies and patch management tools eliminate this class of vulnerability entirely.

Monitor your accounts for breaches. Have I Been Pwned notifications turned on. Set up Google's Password Checkup. Run your email addresses through breach notification services regularly. Knowing your credentials appear in a data breach early gives you time to change passwords before attackers attempt credential stuffing on your other accounts.
The Hard Truth
Security is not a product you buy. It's a process you maintain. No single tool prevents all threats. The attackers only need one gap. You need every gap closed, continuously. When I look at the current threat landscape, the trend lines are not encouraging. Attack automation tools are making it cheaper and faster to launch campaigns at scale. The number of unique malware variants has increased exponentially. State-sponsored actors and organized crime groups are operating in the same ecosystem, sharing tools and techniques. The cost of a breach continues to rise. The organizations and individuals who handle this best aren't the ones with the biggest budgets. They're the ones who treat security as a continuous practice rather than a project with an end date. They test their backups quarterly. They run phishing simulations monthly. They segment their networks and verify that segmentation actually blocks lateral movement. They invest in detection before they invest in prevention, because prevention will always have gaps and detection is what catches what prevention misses.