Formal Notation In Practice
You pick up a specification document at work and three pages into it there is a block of symbols that looks like mathematical notation crossed with programming syntax. That is formal notation. It is not magic. It is a way to remove ambiguity from descriptions of systems, algorithms, protocols, and requirements so that two people reading the same thing arrive at the same conclusion about what the thing does. I spent years writing requirements for embedded software systems. The first time I tried to do that without any formal notation, I lost about six weeks to miscommunication. Someone read a timing constraint one way. I read it another. The hardware did neither of those things. We ended up shipping a product that worked under some conditions and failed under others in a way that was nearly impossible to reproduce. After that, I started learning Z notation, B-method, TLA+, and basic sequent calculus. Not because they were trendy. Because I needed to stop guessing what my own documents meant.
The Abcs Of Formal Notation Definition Uses And Applications
Formal notation is a symbolic language with strict grammar and semantics. Unlike natural language, every symbol has a defined meaning. Unlike programming languages, which describe how to execute something, formal notation often describes what should be true. You will see it used for specifications, verification, protocol design, and in academic work where precision matters more than readability. The definition part is straightforward. Formal notation uses a constrained alphabet and a set of formation rules. If a string of symbols follows those rules, it is a well-formed formula. If it does not, it is garbage. The semantics assign meaning to well-formed formulas. Model theory gives meaning through structures. Proof theory gives meaning through derivations. Most engineers encounter the proof-theoretic side when they are asked to verify that a system satisfies a property. Here is a practical example that actually came up on my desk last year. I was reviewing a specification for a real-time scheduler. The requirement said something like the system must service all interrupts within two milliseconds of arrival. That sentence is not formal. It is not even precise. Two milliseconds from what moment? Arrival at the CPU? Arrival at the interrupt controller? Arrival in software? Is that a hard deadline or an average? I rewrote it in temporal logic as a formula: for all interrupt events e, response_time(e)
= 2ms. That still had an ambiguity around which response time definition to use, so I added the metric definition as a separate axiom. The formal notation did not solve everything. It forced me to expose the ambiguity and make a choice instead of hiding behind vague wording.
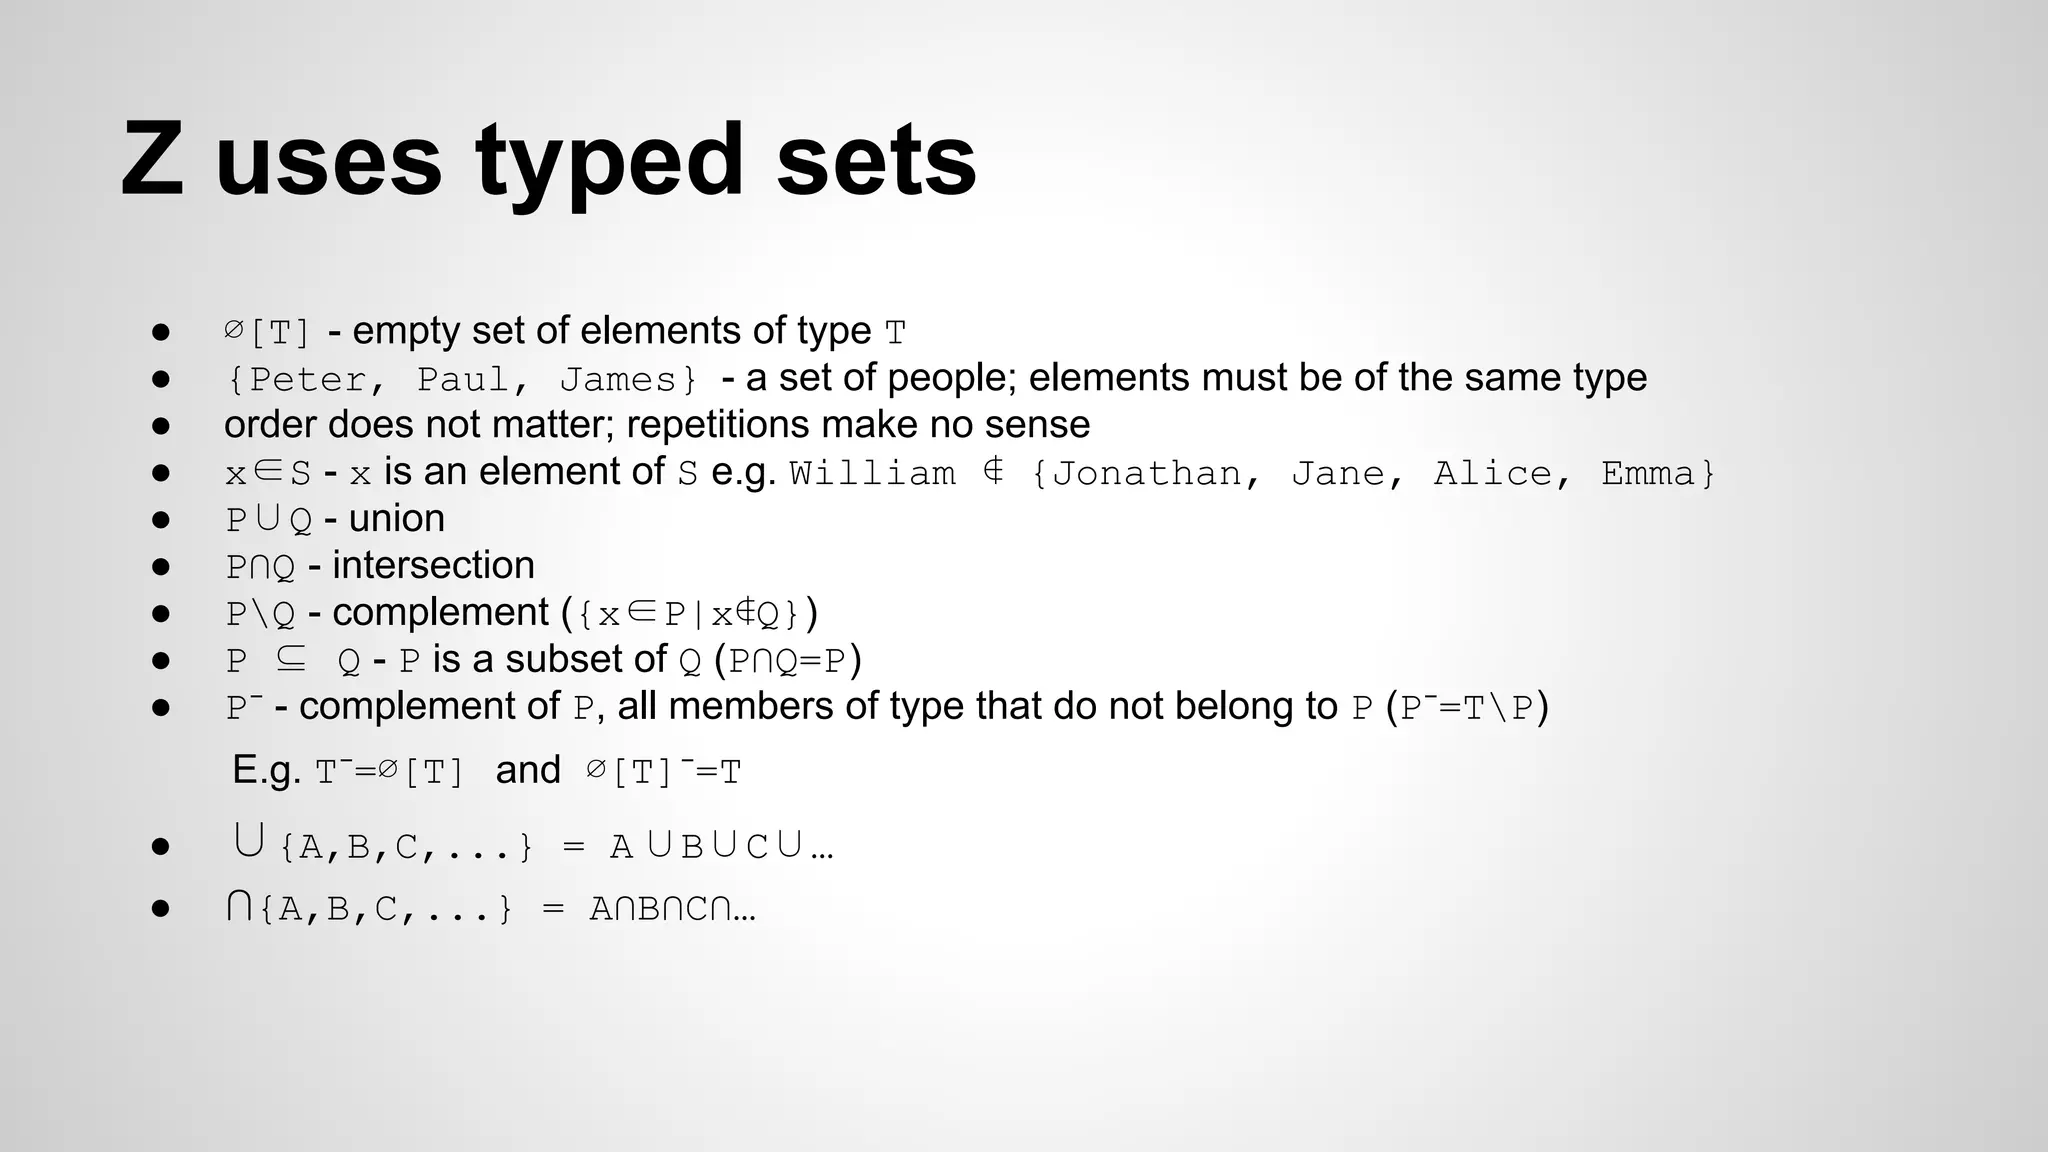
Common formal notations you will run into Z notation is used for specifying software systems using set theory and first-order logic. It is heavy on schema blocks. The learning curve is steep but once you read it you can express state transitions precisely. B-method is similar to Z but designed for refinement and implementation. It lets you go from an abstract specification to executable code while preserving correctness proofs. It is used in safety-critical systems like metro control and aerospace. The tooling is mature but not particularly friendly to people who are not willing to learn the whole ecosystem.
Get the Full Details
TLA+ is the most accessible one for most working engineers. It uses temporal logic to specify behaviors over time. You write a specification and then use the TLC model checker to verify properties. I use it when I need to check whether a distributed algorithm has a deadlock scenario. It caught a race condition in a message queue design that nobody on the team had considered. The specification took me about four hours to write. The bug would have taken me about six weeks to find through testing. Process algebras like CCS and CSP describe concurrent systems. They are more common in academia and protocol specification than in day-to-day engineering work. You will encounter them when reading about telecommunications standards or security protocol analysis. How to actually use formal notation without wasting your time
Start with something small. Pick a module or a component and write its specification in one of these notations. Do not try to formalize the entire system at once. That approach fails almost every time. I learned this the hard way during a project where I tried to specify a complete authentication protocol in TLA+. I got through about forty percent of it before realizing I did not understand the threat model well enough to formalize it correctly. Throwing more notation at incomplete domain knowledge just produces false confidence. The model checked out. The actual system had fundamental design flaws that the notation could not capture because I had not specified the right things. Use the formal notation to find the gaps in your understanding, not to prove that you already understand everything. That is the counter-intuitive part most people miss. Formal notation does not confirm your intuition. It breaks your intuition by making implicit assumptions explicit. When you hit a point where you cannot write the formula, that is usually because you do not actually know what the system should do at that point yet. Stop and figure that out before you continue. Tooling matters more than you might expect. TLA+ has a decent IDE and the model checker is fast enough for most practical use cases. Z has several tools but they are scattered and documentation quality varies. B-method tooling is integrated but the learning cost is significant. For quick verification of small protocols, I sometimes just write things out by hand using basic propositional and predicate logic. It is faster for small problems and avoids tool setup time entirely.
Where formal notation fails It does not handle uncertainty well. If requirements are genuinely vague or likely to change, formal notation locks you into a specific interpretation that may become wrong as the project evolves. I have seen teams spend weeks formalizing a specification that got rewritten three months later because the business needs changed. The formal work was not wasted in the sense that it improved understanding. But it was wasted in the sense that the output had to be discarded. For projects with stable requirements, the investment pays off quickly. For exploratory projects, it is usually a poor use of time. Formal notation also does not replace testing. A verified model is only as good as the specification. If the specification does not match the real world, verification proves nothing useful. I once verified a caching algorithm against a specification that assumed network messages were delivered atomically. The model checked out perfectly. The actual distributed system had a subtle ordering bug that the specification did not capture because atomicity was not explicitly modeled. Testing caught it. Formal verification did not because the problem was in the specification, not the implementation.
The other limitation is team adoption. If you are the only person who can read and write the notation, it becomes a bottleneck. I have watched good formal methods work die in organizations because the rest of the team treated it as an academic exercise rather than a practical tool. The workaround is to pair formal specification with informal documentation and to use the formal notation selectively on the parts of the system where ambiguity is most dangerous. Do not formalize everything. Formalize the parts that have killed projects before. A specific edge case that took me too long to solve I was working on a distributed consensus protocol where nodes could partition temporarily. The specification needed to express that during a partition, the system maintains consistency for reads but may delay writes. Getting the temporal logic right for this required me to introduce a new predicate for partition-aware liveness. I kept running into cases where the standard liveness property conflicted with the consistency requirement under certain partition scenarios. The issue was that I was trying to express two competing invariants without a priority mechanism. I solved it by introducing a ranking function that treated consistency as a hard invariant and write availability as a liveness property that only applies when the partition heals. This is not a standard pattern. It took me about three days of working through counterexamples to get it right. The workaround was essentially to accept that some requirements cannot be simultaneously satisfied at all times and to make the tradeoff explicit in the formalism rather than burying it in prose.
If you want to start learning, the best entry point is TLA+ and the free book accompanying it. It is more practical than the academic textbooks on Z or B-method. For formal notation in requirements engineering, there is no single canonical resource. You end up learning by doing and by reading specifications that other people have written. Read the NASA standards documents on formal methods. Read the specifications for protocols you use. The examples are usually clearer than the introductions. Formal notation is a tool, not a methodology. It does not make you a better engineer by itself. It makes you better at handling precision problems. Use it when ambiguity is expensive. Skip it when speed and iteration matter more than correctness proofs. That is the actual answer to most questions about when to use it.