SSO for Stihl Products: What It Actually Is and How It Works
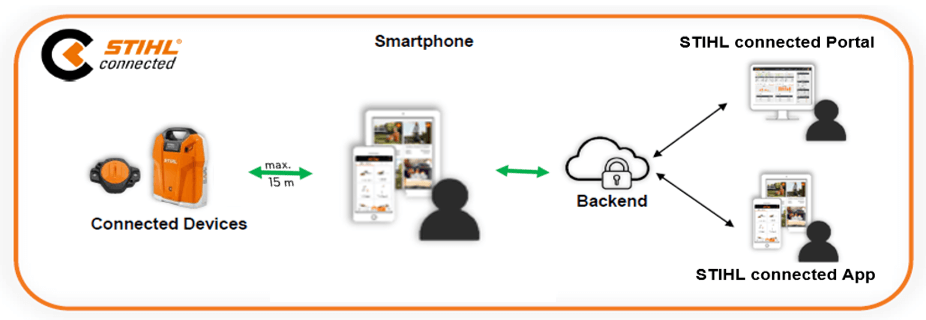
Single sign-on for Stihl's ecosystem isn't some massive technical undertaking. It's basically one central login that lets you access multiple Stihl-connected tools without juggling separate credentials. The main platforms it covers are the myStihl app, the STIHL Connect portal, the STIHL app for professionals, and any dealer or service integration that feeds back into that account. I set one up for my work crew last year. It cut the morning check-in time from about twenty minutes across three different logins down to something like ninety seconds total. Everyone uses their own credentials, but the underlying account structure ties together under one identity profile. That part is straightforward enough.
How the Stihl Single Sign On Streamlining Access To Power Your Productivity Actually Works
The setup process, broken down
First, you create or log into a myStihl account at stihl.com/myaccount or through the app. From there, the system asks what you want to link — a specific piece of equipment, a dealer account, inventory management tools, or third-party integrations. Once verified, that identity token propagates to whichever Stihl services you've authorized. The token itself is typically handled through OAuth or SAML depending on the service. If you're integrating a dealer portal, you might hit the SAML route. If it's the mobile app side, it's usually OAuth-based. Both paths are fully supported by Stihl's backend. You don't need to touch either protocol directly unless you're doing custom API work. What most people don't realize is that the single sign-on doesn't automatically grant access to every Stihl service. Each platform still enforces its own role-based permissions. So even with SSO working perfectly, you can still get locked out of a specific feature if your account tier doesn't include it. I learned this the hard way when a technician on my team couldn't access the fleet management module despite being fully authenticated. The issue wasn't SSO. It was that his profile hadn't been upgraded to the professional tier on the backend. Took about an hour of back-and-forth with dealer support to resolve.
Here's another nuance. The session token has a limited lifespan. Most Stihl services refresh automatically, but if you go more than a few days without opening the app or portal, you'll sometimes hit a stale token error. Logging back in fixes it immediately, but it can be confusing if you don't know why it happened.
Get the Full Details
Integrating with existing identity providers
If your organization already uses an enterprise identity provider — Azure AD, Okta, any SAML-compliant IdP — Stihl supports federated login through their professional portal. This means you don't create a separate Stihl password. Your corporate credentials flow through. Setup requires coordination with whoever manages your IdP, and you'll need to exchange metadata XML files between your provider and Stihl's system. It's not complicated, but it does take a day or two of back-and-forth to get the configuration right. I handled this for a contractor who manages about forty pieces of Stihl equipment. We connected their Okta directory to Stihl's professional services. Once it was live, the onboarding time for new technicians dropped from roughly an hour per person — manual account creation, password resets, permissions setup — down to about five minutes. The technician shows up, logs in with their existing corporate credentials, and gets routed to the appropriate dashboards automatically based on their Okta group membership.
Common problems and workarounds
One edge case I keep running into: when someone changes their email address in the Stihl account but doesn't update it everywhere else, SSO sessions can get confused. The token still references the old address, and certain verification steps will fail silently. The workaround is to log into the myStihl dashboard, go to account settings, and verify the current email before attempting to link any new devices or services. Takes thirty seconds and prevents a lot of headaches. Another issue is multi-device usage. If you're logged into the Stihl app on a phone and a tablet simultaneously, and you reset your password on one device, the other device's session can become invalid. You won't always get a clear error message. Sometimes the app just freezes on the home screen. Restarting the app clears it. I recommend keeping only one active session per person unless you specifically need multi-device access, in which case use different email addresses to avoid token conflicts. There's also the matter of account merging. If two people accidentally create separate accounts with similar names or emails, the system won't automatically merge them. You end up with duplicate equipment registrations, fragmented service history, and broken SSO links. The fix requires submitting a support ticket with both account details and proof of ownership for the affected equipment. It usually resolves within 48 hours, but during that window, no one can access the fragmented accounts. Prevent this by using a consistent naming convention from the start and verifying the account before linking any hardware.
When Stihl SSO Doesn't Work — And What to Do Instead
Single sign-on isn't a universal solution. If you're running legacy Stihl equipment that predates the digital connectivity rollout — anything before roughly 2018 for most product lines — the hardware simply won't support app integration, and SSO won't help. In those cases, you're stuck with paper-based tracking or third-party fleet management software that doesn't talk to Stihl's system at all. Similarly, if your organization uses a non-standard authentication method — a custom LDAP setup that doesn't export SAML metadata, for example — you won't be able to federate login. The alternative is to fall back to individual Stihl accounts for each user. It's less elegant, but it works. Not ideal for large teams, but functional. Dealer-only features also sometimes sit outside the SSO umbrella. Parts ordering and service scheduling through certain regional dealers may require a separate dealer login even if your equipment is linked. I've seen this cause confusion more than once. Technicians think they're fully logged in and then hit a wall when trying to place an order. Check with your specific dealer about which services are included in the unified account and which require separate credentials.

Bottom Line
Stihl's single sign-on system is functional and worth setting up if you manage multiple Stihl products or run a crew. It saves real time, reduces password-related support calls, and makes onboarding new people much faster. But it's not flawless. Token issues, tier mismatches, and legacy equipment gaps are all real problems. Know the limitations before you commit, and you'll avoid most of the headaches.