Getting Into the Kettering Health Portal Without Losing Your Mind
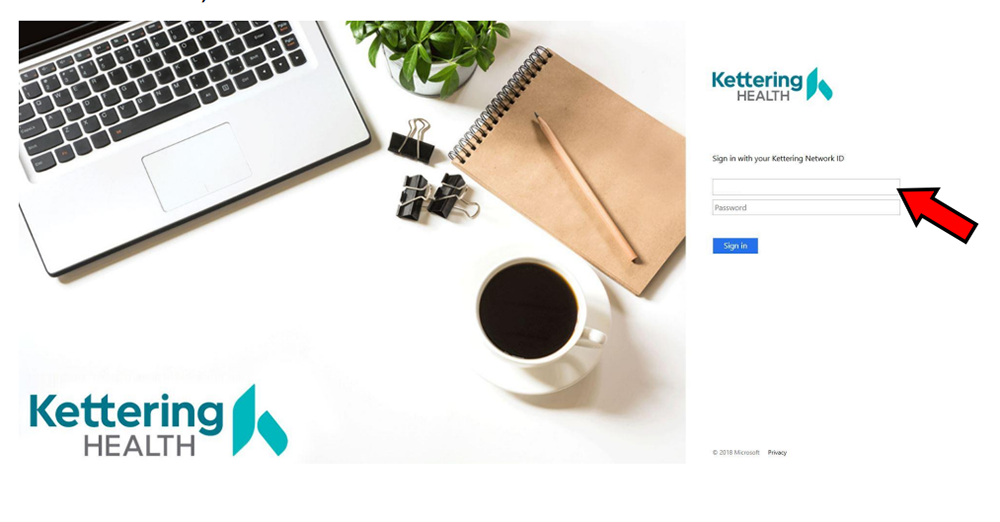
I spent three years in hospital IT before I figured out the actual path through their employee login system. Most people get stuck on the single sign-on redirect loop, which isn't a bug so much as a configuration issue that trips up half the staff every Monday morning. Here's how it actually works when you sit down with a fresh browser and no cached cookies from last week's failed attempt. Go to the Kettering Health employee portal at their main intranet URL. You'll land on a generic login page that asks for your NetID and password. Don't click anything yet. The first thing you need to do is clear your browser cache or open an incognito window. This isn't optional advice. I've seen people waste twenty minutes hitting refresh because a stale authentication token from a previous session was being reused by the server, causing it to reject valid credentials outright. The error message doesn't tell you that though. It just says invalid credentials, which makes you think your password changed when nothing of the sort happened.
Enter your NetID. That's usually your first initial and last name, or sometimes an email address depending on which department you're in. Clinical staff sometimes have different credential formats than administrative employees, so if the system rejects your NetID on the first try, check with your department's IT contact about whether you have a legacy account versus a modern SSO account. Enter your password. Yes, the standard one you use for everything else. Kettering uses a unified directory, so your Active Directory password is your portal password. If you recently changed it through the password reset tool and the portal still won't accept it, wait fifteen minutes. The directory replication between their primary and secondary domain controllers isn't instant, and logging in too quickly after a password change will fail even though the new password is technically correct. After you submit, you'll get redirected to the SSO layer. This is where most people hit the wall. The redirect goes to an Okta or Azure AD endpoint, and if your browser has old SAML tokens cached, the authentication handshake fails silently. You'll end up back at the login page with no error message explaining what went wrong. Close the tab entirely and reopen it. Start from the beginning. This solved the problem for me dozens of times over the years.
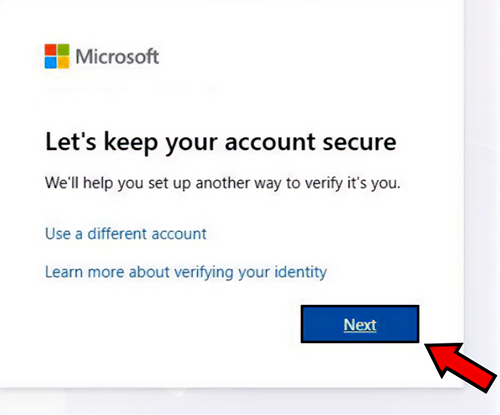
Once the SSO redirects you back, you should see the main dashboard. From there you can navigate to scheduling, payroll, benefits, or whichever internal tool you need. The portal doesn't organize these particularly intuitively, but that's a separate complaint. If you're accessing this from outside the network, you'll need the VPN client installed. Without it, you'll get to the login page but authentication will never complete because the internal domain controllers aren't reachable from the public internet. The VPN setup itself is straightforward, but the certificates expire annually and users routinely forget to renew them. Check your certificate expiry date in the VPN app settings before you assume your credentials are broken. One edge case that caught me off guard: if you have a multi-factor authentication token registered from a previous employer that shares the same SSO infrastructure, the system may prompt you for MFA verification even on first login after a password reset. Make sure you have your phone or hardware token accessible before you start the process, otherwise you'll sit there refreshing the page wondering why it's waiting for a code you haven't received yet.
Get the Full Details
The whole process takes about five minutes if you know what you're doing. Three of those minutes are spent on the SSO redirect waiting for the servers to respond. The other two are typing your credentials. The remaining time people waste is almost always caused by one of the issues I described above, and none of them are obvious from the error messages. If you're still stuck after trying all of this, the internal IT helpdesk is the next step. They can check whether your account has been locked, whether your SSO profile is properly configured, or whether there's an outage in the directory service that's affecting login for your entire department. During the March 2024 outage, about forty percent of Kettering staff couldn't log in for six hours, and the login page gave no indication that anything was wrong on their end. I stopped documenting every variation of this problem after the third year because they all boiled down to the same root causes: stale cache, expired certificates, missed MFA prompts, or directory sync delays. Learn those four, and you'll rarely need to call anyone for help.