Browser Security Isn't About One Thing
You want to know how to stay safe online without turning your life into a series of passwords and pop-ups. I spent roughly six years as a security analyst before moving into infrastructure, and the thing nobody tells you is that browser hardening is mostly about managing trade-offs. You can lock it down so tight that half the tools you rely on stop working. Or you can leave it open and collect telemetry like everyone else. The middle ground is where most people actually need to operate. Let me start with what you should configure first because most guides get this backwards. Content blocking is more important than your browser choice. A well-hardened Chrome installation with aggressive ad-blocking will be safer than a vanilla Firefox with nothing but a password manager. Here's what I actually do:
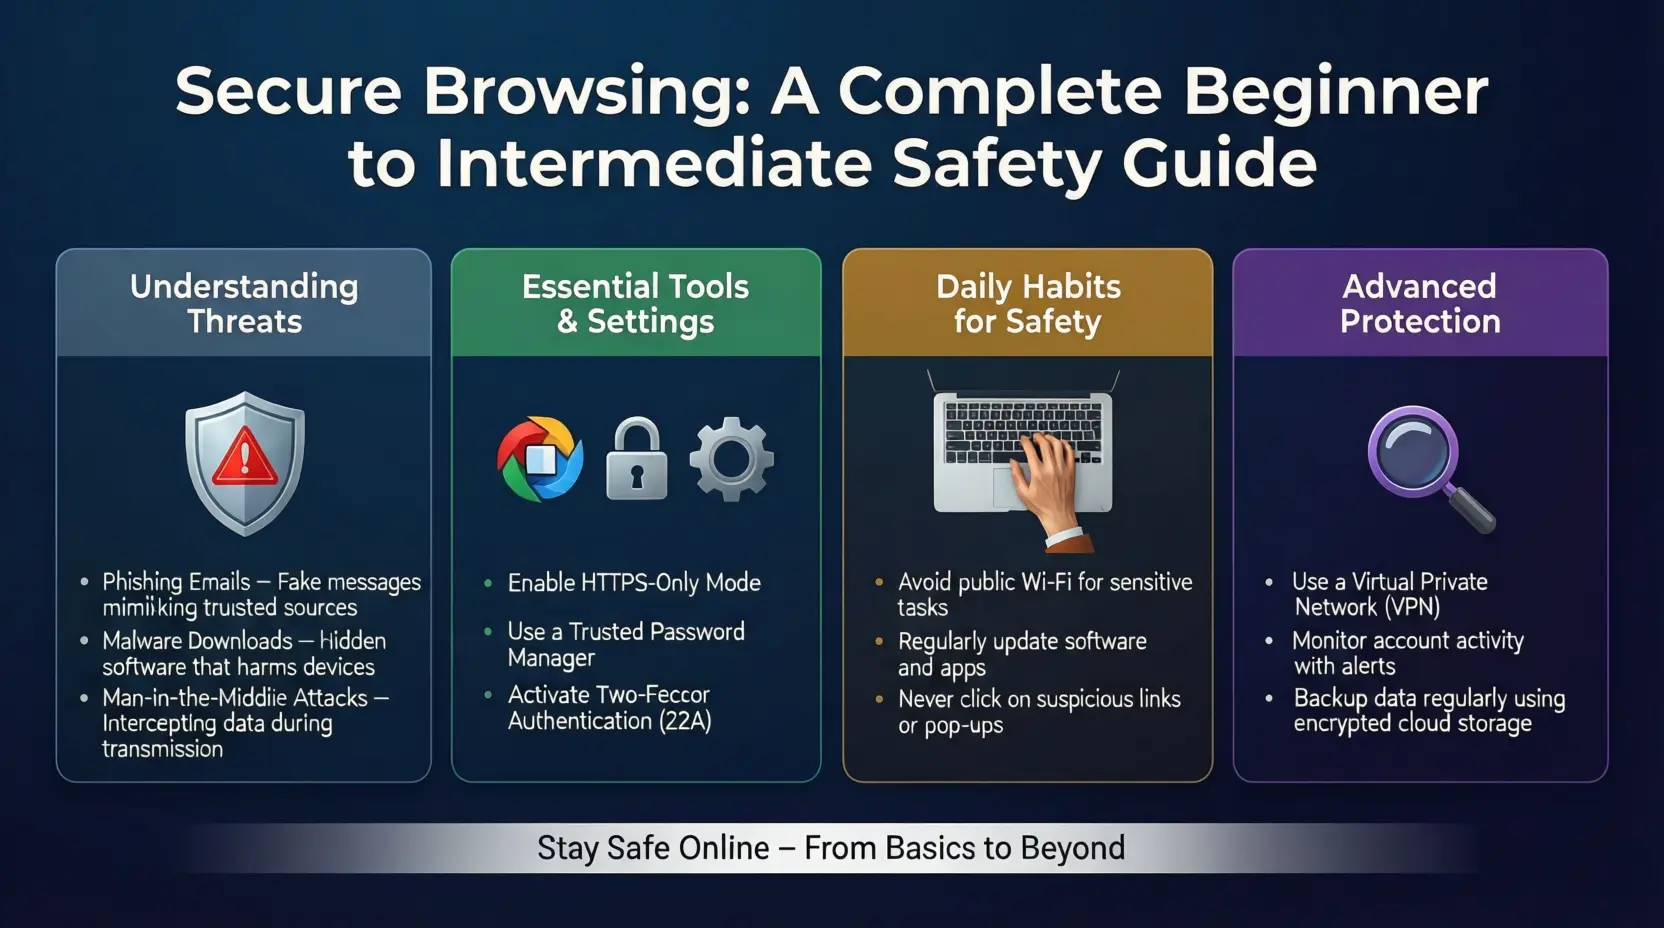
First, uBlock Origin on Chromium-based browsers. Not uBlock, just the full version. This filters requests at the network level before they ever reach your browser's JavaScript engine. Trackers, ads, cryptominers — they all get blocked at the DNS or HTTP request stage. This alone reduces the attack surface by a significant margin. Second, a strict CSP (Content Security Policy) setup. Most users don't touch this. Your browser already enforces some of this automatically through its built-in protections. But enabling features like X-Content-Type-Options: nosniff and frame-ancestors restrictions on sites you control matters if you're running anything. For regular browsing, it's less relevant but still worth understanding. Third, the HTTPS-only mode. Enable this in your browser settings immediately. It forces TLS connections everywhere and won't fall back to plaintext HTTP even when the site doesn't support it properly. Some sites will break, but they're doing something wrong.
Fourth, disable third-party cookies by default. Modern browsers have this option now. Third-party cookie tracking is one of the few remaining reliable surveillance vectors that doesn't require executing JavaScript at all.
Get the Full Details

Stay Safe Online The Essential Guide To Safer Web Browsing
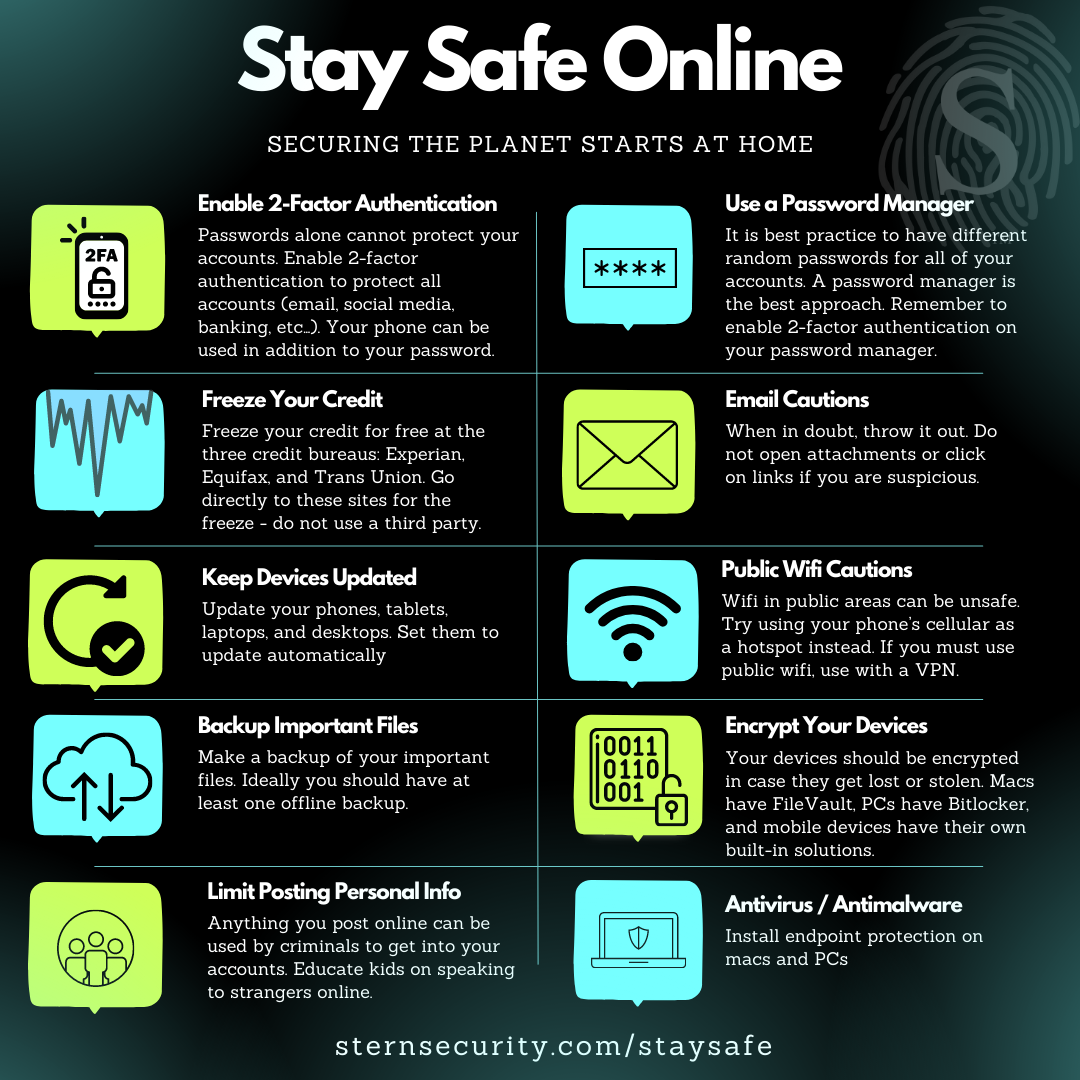
When I first went through the process of hardening browsers professionally, I made the mistake of thinking "secure" meant "impossible to use." There was a project where I needed to test a legacy government portal that used outdated TLS ciphers and required specific SSL handshake configurations. Standard hardened browsers refused to connect at all. I ended up running a completely separate browser profile with no extensions, disabled protections, and a dedicated user agent string just to access that one service. It took me about three hours to set up the isolation properly. The workaround was straightforward: configure your primary browser for maximum protection, then create an isolated profile for legacy or problematic sites using browser-level sandboxing. This is the part that matters more than any single tip: compartmentalization. Your main browsing session shouldn't be the same one where you check email, shop, or log into banking. Each activity domain should have its own browser profile or container. Firefox has Multi-Account Containers built in. Chrome users can use profiles with different cookie stores and extension sets. The separation prevents cross-site tracking and limits the blast radius if one profile gets compromised. Password management is non-negotiable. Bitwarden or KeePassXC. Neither has subscription fees. Generate unique passwords for every site. The 2FA implementation matters more than the password itself though. Hardware security keys like YubiKey are the gold standard. They resist phishing because the authentication context binds to the actual domain. SMS codes are trivially interceptable. App-based TOTP is better but still vulnerable to session hijacking. I've seen accounts compromised through 2FA bypass even when strong passwords were in place.
What Most People Get Wrong
Browser extensions are the biggest vulnerability vector most people ignore. Each extension has access to your browsing data. A malicious or poorly maintained extension can read everything you visit, inject scripts into pages, or modify responses before they reach you. I once audited a setup where a "security" extension was actually exfiltrating form data to an unknown endpoint. The extension had over two million downloads and a four-star rating. The rule is simple: minimize extensions. Remove anything you haven't used in the past thirty days. Check the permissions each extension requests. If a calculator app asks for "read and change all your data on websites," remove it immediately. Extensions are legitimate software but they're also a trust boundary you're handing over control of your entire browsing session to. Another common pitfall: believing that incognito or private browsing makes you anonymous. It doesn't. It only prevents local history storage. Your ISP, your employer's network monitoring, and the sites you visit still see everything. Private browsing is useful for not leaving traces on a shared computer. It's useless against anyone who can observe your network traffic.
DNS-level filtering is underutilized. Services like Cloudflare's 1.1.1.2 or NextDNS can block malware domains, tracking endpoints, and known bad content at the DNS resolution level. This catches threats before they reach your browser entirely. It's particularly effective against drive-by downloads and malicious redirects that rely on DNS poisoning or typosquatting. Setting this up on your router means every device on your network gets protection without individual configuration.
Realistic Limitations
No amount of browser hardening protects you from targeted attacks by someone who already has access to your device. If malware is running on your system with elevated privileges, your browser configuration is irrelevant. Endpoint detection and regular system updates matter far more than extension choices at that point. Social engineering remains the primary attack vector regardless of how locked down your browser is. A convincing phishing page can bypass every content filter and extension because it's asking you to voluntarily hand over credentials. The technical layers only stop automated or opportunistic threats. They don't stop a human being deciding to click somewhere they shouldn't. The perfect browser configuration doesn't exist because threat models differ. If you're a journalist working with sensitive sources, your requirements are fundamentally different from someone who primarily shops and reads news. Start with the baseline protections I outlined above. Then add or remove layers based on your actual risk profile. Over-hardening is as counterproductive as under-hardening because it usually results in people just turning everything off when it becomes unusable.
The current browser landscape gives you enough tools to get genuinely safer with maybe thirty minutes of initial setup. Most of that time goes toward choosing and installing the right extensions and configuring profile isolation. The ongoing maintenance is minimal — just periodically review installed extensions and keep your browser updated. That's it.