Understanding Statefram Login and the Single Pane of Glass Approach
Statefram Login The Single Pane Of Glass Revolutionizing Enterprise Access Control
Statefram is an identity governance and access control platform. It consolidates user provisioning, role management, and compliance reporting into one interface. The login experience it provides isn't fundamentally different from other enterprise IAM tools. What it does differently is how it handles bulk operations across multiple directories and applications without requiring you to log into each system separately. I spent about three weeks configuring Statefram for a mid-size organization that had roughly forty applications scattered across on-premises Active Directory, Azure AD, and a handful of SaaS vendors. The setup itself is documented fairly well in their knowledge base, but the documentation doesn't cover what happens when the applications don't behave. Here's the practical side of things.
How the Login and Provisioning Flow Actually Works
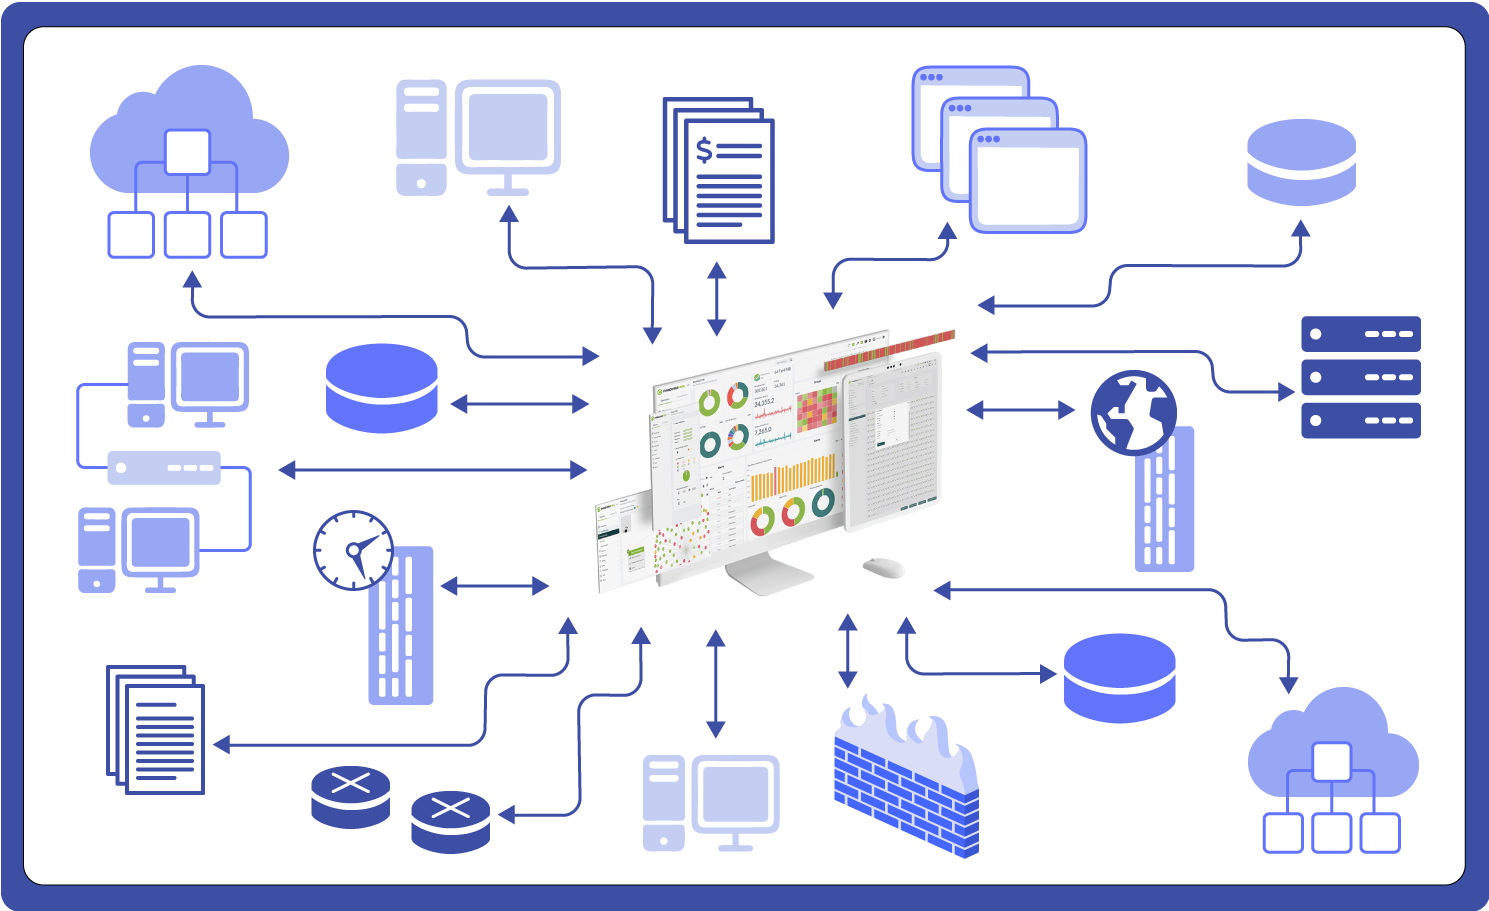
When a user attempts to access any integrated application through Statefram, they authenticate once against the Statefram login portal. After that, Statefram handles the provisioning of that user account across all connected directories and applications based on the role mappings you've defined. The single pane of glass part means you can see and manage all of those connections from one dashboard instead of touching forty separate admin consoles. The provisioning engine uses attribute mapping rules. You define what happens to a user record when they move from hiring to termination. Statefram pushes those changes to connected systems. Most people get stuck at the attribute mapping stage because they assume every application accepts the same format for common fields like username, email, and department. They don't. Some systems expect a samAccountName. Others want a GUID. A few legacy systems use completely custom field names that aren't documented anywhere. I ran into this exact issue with a proprietary HR system that used a non-standard LDAP schema. The provisioning would fail silently on that application while succeeding everywhere else, which made debugging take longer than it should have. The workaround was to add a test user profile in Statefram's provisioning queue, enable verbose logging for that specific application connector, and then manually review the outbound payload before allowing it to sync. You can export the JSON payload directly from the event log. It showed exactly which attributes were being rejected. From there it was just a matter of remapping the fields in the integration template. That process took about twenty minutes once I knew where to look.
Configuration Steps That Actually Matter
Start by connecting your identity sources. Statefram supports AD, LDAP, Azure AD, Okta, and a few others out of the box. Add each directory as a source before you attempt any application provisioning. The order matters less than making sure you verify connectivity for each source individually. Testing the connection from within the platform will save you time later. Define role templates next. These are the foundation of your access policies. Each role maps to a set of attributes and application permissions. Keep roles flat and avoid nesting them initially. Nested roles introduce ambiguity during access reviews and can cause provisioning conflicts you'll spend hours untangling. Start with five to ten core roles and expand from there. Connect your applications after roles are in place. Statefram has pre-built connectors for many common SaaS platforms. For custom applications, you'll use either SCIM or REST API integration. SCIM is faster to implement but less flexible. REST API integration gives you more control over what gets synced and when. I prefer REST API connectors for anything beyond standard SaaS tools because they let you control the exact timing of provisioning events and add conditional logic based on user attributes.
Get the Full Details

The login policy configuration is where most organizations make mistakes. Default settings in Statefram allow any authenticated user to self-service password resets and basic access requests. This is convenient but opens up a review gap. If your compliance requirements include audit trails for password reset events, configure the policy to require manager approval for all reset requests. The toggle is straightforward in the access policy section. Don't skip this step if you're handling regulated data.
The Role Assignment Workflow in Practice
Role assignment in Statefram works on a combination of attributes and manual overrides. When a user's profile matches a role's attribute criteria, the platform automatically assigns that role and triggers provisioning to all connected applications. Manual assignments override automatic ones. This sounds simple but creates edge cases you won't notice until you have hundreds of users and a mix of both assignment types. The main issue I encountered was with contractors who should have been auto-provisioned based on department but were also manually added to an access request queue. The platform processed both routes simultaneously, which sometimes resulted in duplicate access records in the target application. The fix was to add a rule that prioritizes auto-assignment over manual requests for users matching the contractor attribute pattern. Once that rule was in place, the duplicate entries stopped immediately.
Access Reviews and Compliance Reporting
Statefram handles access reviews through scheduled campaigns. You define the review scope, select the reviewers, and set a deadline. Reviewers receive notifications and can approve, deny, or request modifications to existing access. The platform tracks all actions for audit purposes. The reporting module has pre-built templates for SOX, HIPAA, and GDPR compliance. These are useful starting points but often need customization for your specific environment. The default SOX report, for example, doesn't include segregation of duties violations unless you explicitly enable that check in the policy settings. It's easy to miss because the option is buried in the compliance configuration menu rather than the reporting dashboard. I found that the real value in reporting comes from the custom report builder. It lets you pull any attribute, role assignment, and provisioning event into a single dataset. From there you can create exports in CSV or PDF format. The export functionality works reliably, but the PDF generator occasionally truncates tables with more than fifty columns. If you need wider reports, export to CSV and format in your spreadsheet tool instead.
Known Limitations and Where It Falls Short
Statefram isn't designed for large-scale identity federation scenarios. If you need SAML-based single sign-on across dozens of identity providers, other platforms handle that more gracefully. Statefram focuses on access governance rather than identity brokering. The SSO capabilities exist but are limited to the applications you integrate directly. Another limitation is the connector dependency model. When a third-party application updates its API without warning, your Statefram connector can break. The platform doesn't automatically adapt to API changes. You need to monitor the connector status dashboard regularly and update integration templates as needed. This is true across most IAM platforms but worth mentioning because it affects uptime in production environments. For organizations with fewer than fifteen integrated applications, the cost and configuration overhead may not justify the deployment. A simpler solution like Azure AD Premium or Okta Identity Governance might be more appropriate. Statefram's strength shows when you're managing between twenty and one hundred applications across hybrid environments. Below that threshold the single pane of glass advantage diminishes relative to the setup effort required.
Security Considerations for the Login Portal
The Statefram login portal supports MFA enforcement at the platform level. Configure this before migrating any production user accounts. Without MFA enforced, the entire access governance framework is weaker than the underlying applications it's meant to protect. Statefram integrates with standard MFA providers including Duo, Azure MFA, and YubiKey. The integration steps are documented but the policy enforcement settings are easy to overlook during initial setup. Session timeout settings also warrant attention. The default idle timeout is thirty minutes. If your organization has stricter requirements, adjust this in the security policy section. The change takes effect immediately for new sessions but doesn't terminate existing active sessions. Plan the configuration update during a maintenance window if you need to enforce it across all users simultaneously.
What to Expect During Implementation
A typical implementation for a twenty-application environment takes between two and four weeks depending on how cleanly your existing identity sources are structured. Environments with messy AD schemas or undocumented custom applications will extend that timeline. Budget additional time for the access review setup phase because configuring reviewers, schedules, and notification templates requires coordination with department heads who are usually unavailable during the initial rollout period. The platform's support documentation is adequate but not comprehensive. When you hit issues that aren't covered in the knowledge base, the support ticket response time averages between four and eight business hours. For urgent production problems, the live chat option is faster but availability depends on your support tier. Most recurring issues I've encountered have been solvable by adjusting attribute mapping rules or connector timing parameters. The platform is stable once the initial configuration is correct.