Setting Up Secure Remote Access at Scale
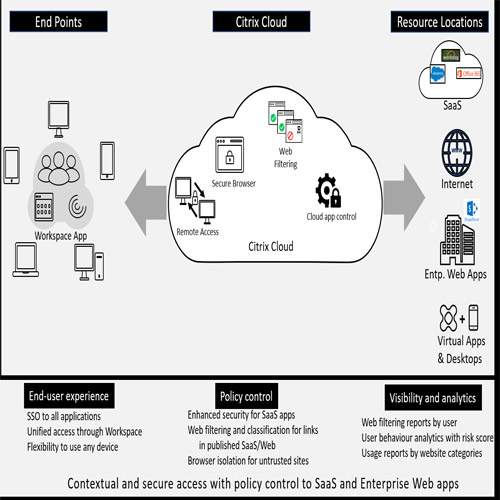
Stanford deployed Citrix as part of a broader effort to consolidate how thousands of faculty, staff, and students access sensitive research systems, clinical data, and legacy applications from off-campus. The integration isn't some standalone product you can buy off the shelf — it's a tightly configured environment built around Citrix Virtual Apps and Desktops, Citrix Gateway, and conditional access policies that align with university identity standards. When I first worked on a migration similar to this, I assumed the hard part would be getting the VDA agents onto the servers. It wasn't. The hard part was figuring out why half the users couldn't launch anything after cut-over, and it turned out to be a TLS handshake timeout between Gateway and the internal NetScaler, caused by an outdated cipher suite that the university's own security team had flagged weeks earlier. The core architecture uses Citrix Gateway as the single external entry point. Users authenticate through the gateway using a combination of multi-factor authentication and SAML-based federation with Stanford's identity provider. Once authenticated, they receive a ticket that grants access to published applications or virtual desktops hosted either on-premises or in AWS. The Citrix Director dashboard gives IT visibility into session health, latency, and failure points across the entire farm. One thing most people miss is the relationship between the Citrix License Server and the Delivery Controllers. They have to trust each other's certificates, and if your PKI doesn't chain back correctly — which happens more often than you'd think in a university setting with multiple legacy CAs — the controllers will sit in an "Unavailable" state and you won't get any session launches. I spent an entire Tuesday afternoon checking certificate chains only to find that the root CA on the license server hadn't been imported into the delivery controller's trust store. Simple fix, but completely invisible in the logs until you know exactly where to look.
The security side relies heavily on Conditional Access policies. Citrix Gateway integrates with risk-based authentication, so a login attempt from an unrecognized device or unusual geolocation triggers step-up verification. This is where the integration with university-wide security tools matters most. Stanford connects this to its SIEM and threat intelligence feeds, so compromised credentials don't automatically translate into persistent sessions. The system also enforces device compliance checks before granting access to certain high-value resources like HIPAA-covered research environments. For application publishing, the team uses both hosted and local applications. Hosted apps run on dedicated server infrastructure and stream to the user's device. Local apps — things like specialized research software installed on a physical machine in a lab — are accessible through remote PC functionality, which routes the session back through the gateway to the on-campus machine. This is useful but introduces a different set of latency constraints. If your user is connecting from Singapore and their target machine is in Stanford, California, you're going to feel it on anything interactive. HDX Adaptive Display helps by adjusting compression based on available bandwidth, but it can't solve physics. Network design is where these deployments typically break or succeed. You need proper DNS resolution from the gateway back into your internal farms, and the gateway itself needs to be configured with the correct SSL optimization settings for your user demographics. If most of your users are on high-latency cellular connections, turning on SSL offloading on the gateway and enabling ICA TCP instead of RTP makes a noticeable difference. I once saw a pilot group's average session quality score jump from 3.2 to 4.7 on the HDX scoring system just by switching the transport protocol and adjusting the image caching policy.
There's also the matter of printer mapping and peripheral redirection. Users complain about these first because they're the most visible failures. Citrix supports bidirectional printer mapping through the gateway, but the printer drivers have to be installed on the VDA or thin client, not just the endpoint. A common workaround is to use PDF printer redirection for document-heavy workflows and let users print to a network queue from there. For specialized lab equipment that requires direct USB passthrough, Citrix offers USB redirection through the Receiver or Workspace app, but it's finicky across browser-based clients. I recommend keeping a list of confirmed-compatible devices and steering users toward them.
Get the Full Details
Deployment Steps
Start with inventory. Map out every application and desktop that needs to be remote-accessible, classify them by sensitivity level, and decide which ones go through the gateway and which stay internal-only. This classification step directly determines your firewall rules and your authentication requirements downstream. You cannot skip it. Phase one: Gateway configuration. Install and configure Citrix Gateway with SSL profile, authentication policies, and AAA extensions. Bind your SAML identity provider. Test authentication in isolation before connecting to anything else. This usually takes one to two days for a properly sized team. Phase two: Delivery Controller and VDA setup. Deploy Delivery Controllers in an active-active pair for redundancy. Install VDAs on server operating systems for hosted resources. Join them to the domain and configure firewall rules so the gateways can reach the controllers on the required ports — 80, 443, 1494, and 2598 at minimum, though you may need additional ports depending on your HDX settings. Validate that the controllers can register with the license server before proceeding.
Phase three: Publishing and testing. Create resource groups based on user roles. Publish applications and desktops with appropriate access policies. Run a pilot with a small group covering both ideal-network and worst-case-network scenarios. Monitor Citrix Director closely during this phase. Session Reliability should be enabled to handle intermittent connectivity without dropping the connection entirely. Phase four: Scale and integrate. Roll out to the broader population in waves. Integrate monitoring into your existing SIEM. Set up alerting for controller failures, license server issues, and unusually high session counts. The goal is to catch problems before users start calling the help desk.
Known Limitations and Failures
Citrix is not a silver bullet. It struggles with high-bandwidth, low-latency requirements like GPU-intensive rendering or real-time video editing over unconstrained networks. The platform also depends heavily on the underlying Windows infrastructure being stable. If yourVDAs are running on aging hardware or poorly tuned images, no amount of Citrix tuning will fix the experience. License costs scale with the number of concurrent users, not just named users, which can create budget pressure during periods of high concurrent demand like exam weeks or grant submission deadlines. Some departments at Stanford have dealt with this by implementing device-based licensing for shared lab computers and user-based licensing for individual researchers. Another realistic concern is browser-based access through Citrix Gateway. While Workspace for web works well for most applications, it lacks full support for peripheral redirection and certain kernel-level features that the native client provides. If your users need local printer access or specific USB device connectivity, the browser client will fall short and you'll need to push the native Workspace app to those machines.
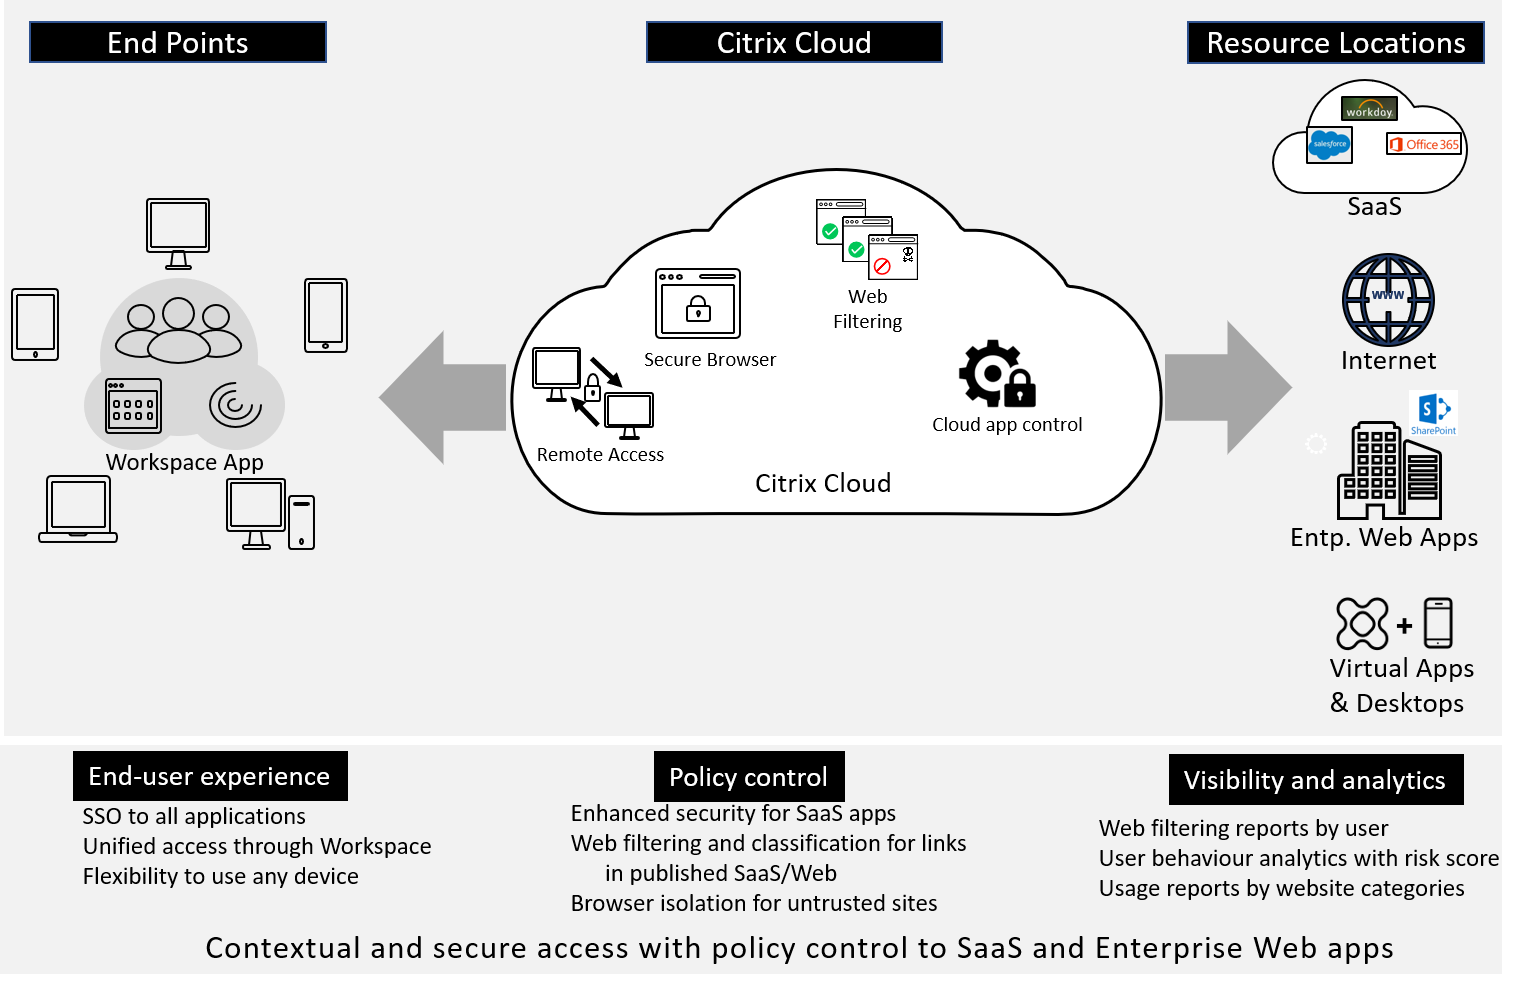
Finally, the integration with conditional access and zero-trust frameworks is evolving. Citrix has made progress here, but organizations that require strict device posture validation before any session starts will find that the native Citrix endpoint checking has gaps compared to dedicated EDR solutions. Most mature deployments layer an endpoint detection tool on top rather than relying on Citrix's built-in posture assessment alone.