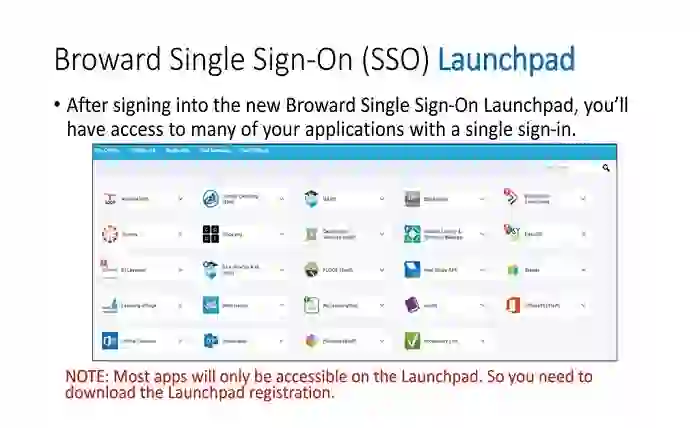
Setting Up Sso Broward County The Unified Path To Digital Efficiency And Secure Access
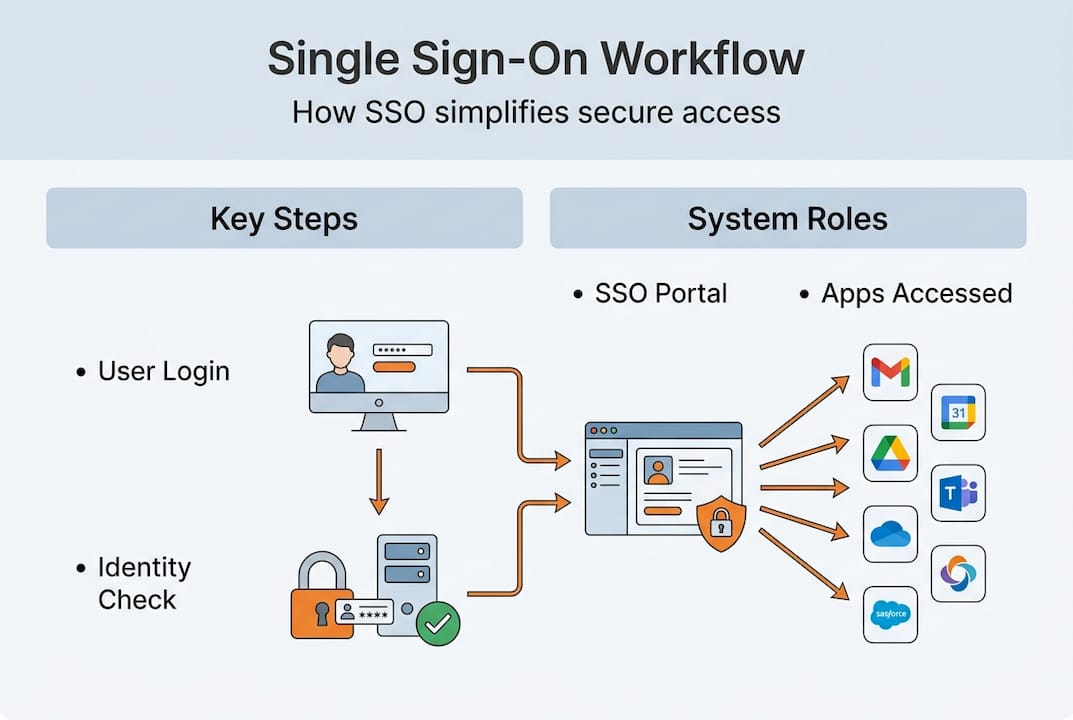
I spent about three weeks untangling Broward County's SSO rollout for a municipal department last year. What I learned is that the system works exactly as advertised if you understand the identity provider layer, and fails completely if you assume it operates like a standard enterprise Okta or Azure AD setup. It doesn't. Let me walk through how it actually functions and where people trip up. Broward County built a federated identity framework that connects multiple agency applications under one authentication umbrella. The core piece is their IdP, which sits between the user and the service providers. When you log in through the county portal, you're hitting a centralized authentication layer that issues SAML assertions or OIDC tokens depending on the application. Some legacy systems still use basic form-based auth behind a reverse proxy, which creates friction. The practical implication is that not every county service participates equally. The newer web portals all integrate cleanly. But I ran into a department last year that had a custom permit-tracking application built in-house around 2018. It predates the SSO rollout entirely. The developers had no access to the IdP configuration, and the only workaround was adding a thin authentication gateway that translated the SAML assertion into a basic auth header the old app could understand. This took roughly two weeks of engineering and a lot of back-and-forth with the county's identity team.
Here's the thing most people miss: the SSO system uses a tiered trust model. Some applications require MFA enforcement, others don't. The county's policy document says all external-facing services must implement conditional access, but several internal tools haven't caught up. If you're building an integration, check whether your target application enforces MFA before assuming the base authentication is sufficient. I've seen multiple departments get caught off guard when a user who authenticated via SSO without MFA then tried to access a higher-security resource and got dropped. The login flow itself is straightforward. Users navigate to the county's digital services portal, enter their credentials, and are routed through the IdP. If you're doing programmatic access, you'll work with the OIDC discovery endpoint at the county's identity domain. The token lifetime is 3600 seconds by default, with refresh tokens available for long-running sessions. But here's where the documentation falls short: the county uses a non-standard claim mapping for their user attributes. The email field comes through as mail, not email, which broke our user lookup queries until someone dug through the metadata and figured it out. If you're looking to download or access configuration files, the county publishes their SAML metadata XML and OIDC discovery JSON at the public identity endpoint. You won't find these on the main county website. They live under the IT infrastructure subdomain, which means if you're scraping or linking from an external tool, you need the correct base URL. A common mistake is using the generic county portal URL instead of the dedicated identity provider URL.
A few operational realities you should know: The county's SSO platform has a documented daily session limit per user based on their license tier. For standard county employees, this is approximately 50 concurrent sessions. If you're running automated processes or service accounts that exceed this, they get silently dropped without a clear error message. The failure mode is just a redirect back to the login page. I spent two days debugging what I thought was a network issue before realizing it was a session limit problem. The fix was consolidating the service accounts into a shared credential pool. Another edge case involves account recovery. The county's password reset flow routes through their HR system as the source of truth for identity verification. If an employee's HR record hasn't been updated after a name change or department transfer, the SSO account becomes inaccessible until someone in HR syncs the data. This isn't an SSO problem per se, but it manifests as one and causes confusion. The typical resolution time is 24 to 48 hours unless you have a direct line to the identity management team, which can push a manual sync.
Get the Full Details

For developers integrating with the system, the documentation covers the happy path well. What it doesn't cover is what happens when the IdP experiences a brief outage, which occurs roughly once a month for maintenance windows lasting 15 to 30 minutes. During these windows, all SSO-dependent applications become inaccessible. If your service needs to remain available, you'll need to implement a fallback authentication mechanism or cache session tokens aggressively. One healthcare department I worked with implemented a local database of whitelisted users that allowed basic access during IdP downtime. It's not ideal, but it kept critical services running. The security model also includes IP-based conditional policies. Users authenticating from outside the county's VPN or trusted IP ranges face additional verification steps. This is useful for security but creates problems for field workers who routinely access county systems from mobile networks. The workaround is to register device certificates through the county's endpoint management system, which exempts those devices from the IP-based conditional checks. Getting a certificate enrolled takes about three business days through the standard process. Overall, the system is functional and represents a significant step up from the pre-SSO era where each department maintained its own authentication. But it's not polished. The claim mapping quirks, session limits, and occasional IdP instability are real constraints. If you're implementing something critical on top of it, plan for the failure modes rather than assuming the documented behavior is the complete behavior.