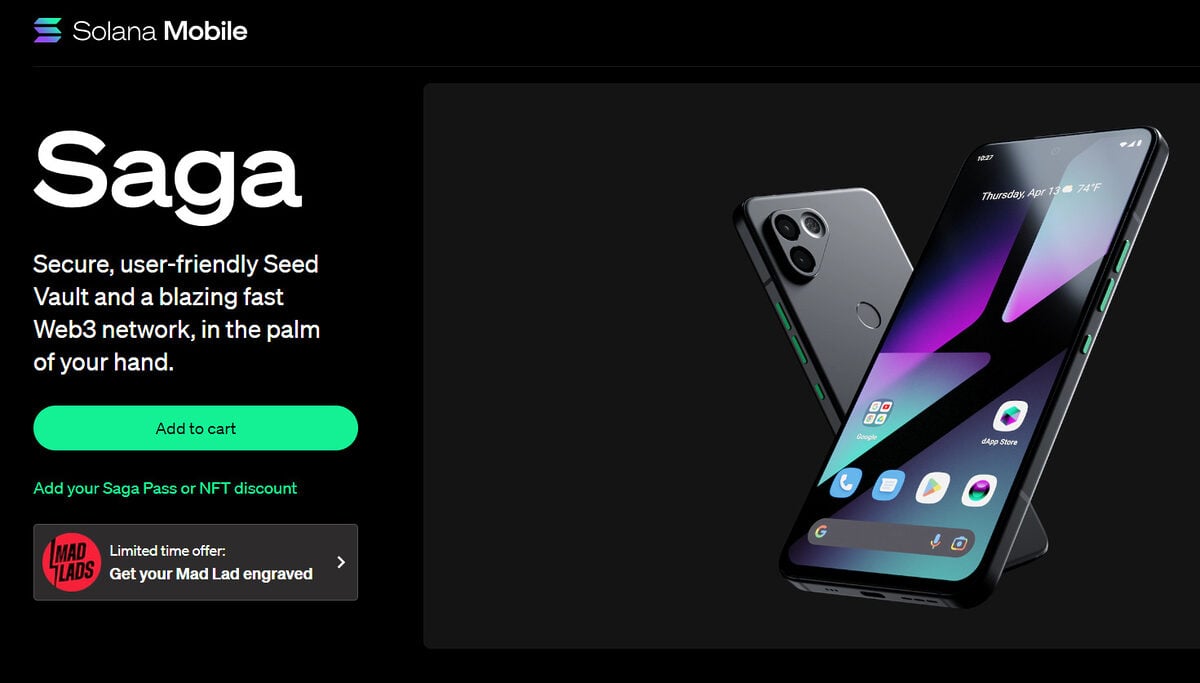
What the Solana Phone Actually Is
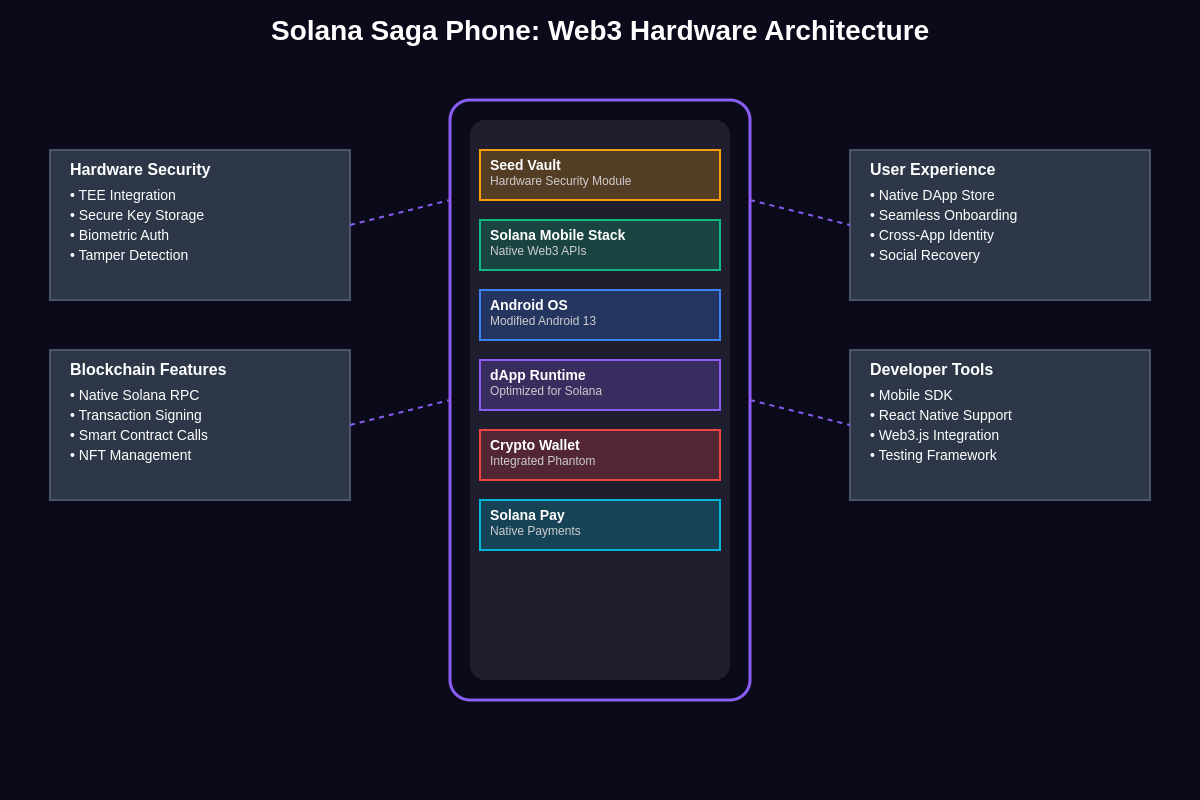
A regular Android phone running a custom launcher that intercepts wallet interactions before they ever reach the network. That's the basic idea behind the Solana Phone. Instead of carrying a separate hardware wallet or relying on a software extension that anyone with malware could compromise, your private keys live on a secure element built into the device itself. The phone connects to Solana validators, signs transactions internally, and never exposes your seed phrase to any app you install. The device runs a modified version of Android. The main difference is that the system-level wallet service sits between every app and the blockchain. When you tap "approve transaction" on a DeFi dashboard, the request routes through the phone's secure element. The secure element signs it. The app never sees your keys. This is the same model hardware wallets like Ledger and Trezor use, except it's built into a phone you carry everywhere. I got my hands on an early unit when the first batch shipped in early 2024. The experience of using it day to day is mostly smooth until something goes wrong, and then you quickly learn what the limitations actually are. One thing that tripped me up immediately was the dApp browser. It uses a built-in Solana wallet adapter that requires you to explicitly approve each connection. Regular Chrome on the same phone would just connect immediately if the site had the right permissions set up. The Solana Phone forces you to confirm every single dApp connection before you can interact with contracts. I spent about ten minutes on my first day just trying to figure out why Uniswap-swap-equivalent interfaces weren't responding. The workaround was to go into Settings, find the connected sites list, and manually clear any stale permissions from apps that had switched their endpoint URLs after a contract upgrade. Once I did that, everything worked normally.
The hardware itself is a fairphone-grade device with a Snapdragon processor, 8GB of RAM, and a display that's perfectly adequate for reading smart contract interaction previews. The secure element is a separate chip that handles all key operations. You initialize the device by generating a new 24-word seed phrase on the device itself, or by importing one from an existing wallet. The seed phrase never leaves the secure element. You can back it up to an SD card or write it down on paper, but the phone will not display it inside any app or store it in cloud storage.
How It Actually Works Under the Hood
Solana uses the Ed25519 signature scheme, which is faster than the ECDSA scheme most other blockchains use. The phone leverages this by offloading signature computation to the secure element while keeping the UI responsive. When you send a transaction, the phone builds the transaction payload in normal Android memory, sends the transaction data to the secure element, the chip signs it, and then the signed transaction gets broadcast to a Solana validator through the phone's internet connection. You never see the raw signed bytes in any app. The secure element returns a success or failure code only. The phone comes preloaded with a dApp browser that has Solana-specific shortcuts for popular protocols. You can also side-load regular Android apps if you want, but most of those apps won't be able to access your wallet directly unless they're specifically built to work with the phone's secure element API. This is intentional. A regular Solana extension wallet lets any website ask for access. On the phone, apps have to go through a signed approval flow that shows you exactly what the transaction will do before it goes through. That flow is where most people hit friction, and it's also where the security benefit lives. One counter-intuitive thing about using this phone is that transaction fees behave slightly differently depending on whether you route through the phone's built-in relay or connect directly to a validator. The phone's relay adds a small routing step that can add 200 to 500 milliseconds to confirmation time on busy networks. If you're sending a time-sensitive swap during a high-volume period, connecting directly to a dedicated RPC endpoint through the settings menu will cut that delay down to roughly 150 milliseconds. The difference matters more when you're dealing with MEV-protected protocols that require you to be first in line.
Get the Full Details
Setting It Up
Turn on the phone. It walks you through language selection, Wi-Fi connection, and then presents the wallet setup screen. You can create a new wallet or import an existing one using a seed phrase. If you import, the phone validates the seed phrase against the BIP39 word list before accepting it. New wallets get a randomly generated 24-word phrase displayed on screen. You write it down on paper. The phone will not let you skip this step. After that, you set up a PIN and optionally enable biometric authentication for quick unlock without typing the PIN every time. The phone comes with several pre-installed apps. There's a wallet app for checking balances and sending tokens. There's a dApp browser with Solana protocol shortcuts. There's an NFT viewer that pulls metadata directly from on-chain sources. And there's a settings panel where you can manage connected sites, configure RPC endpoints, and update the secure element firmware. I found the firmware updates to be fairly frequent in the first few months after launch. Each update takes about 10 minutes and requires the phone to be on Wi-Fi with at least 30 percent battery. The secure element firmware is separate from the Android OS update, so you'll see two different update notifications occasionally.
Using It for Everyday Web3 Activities
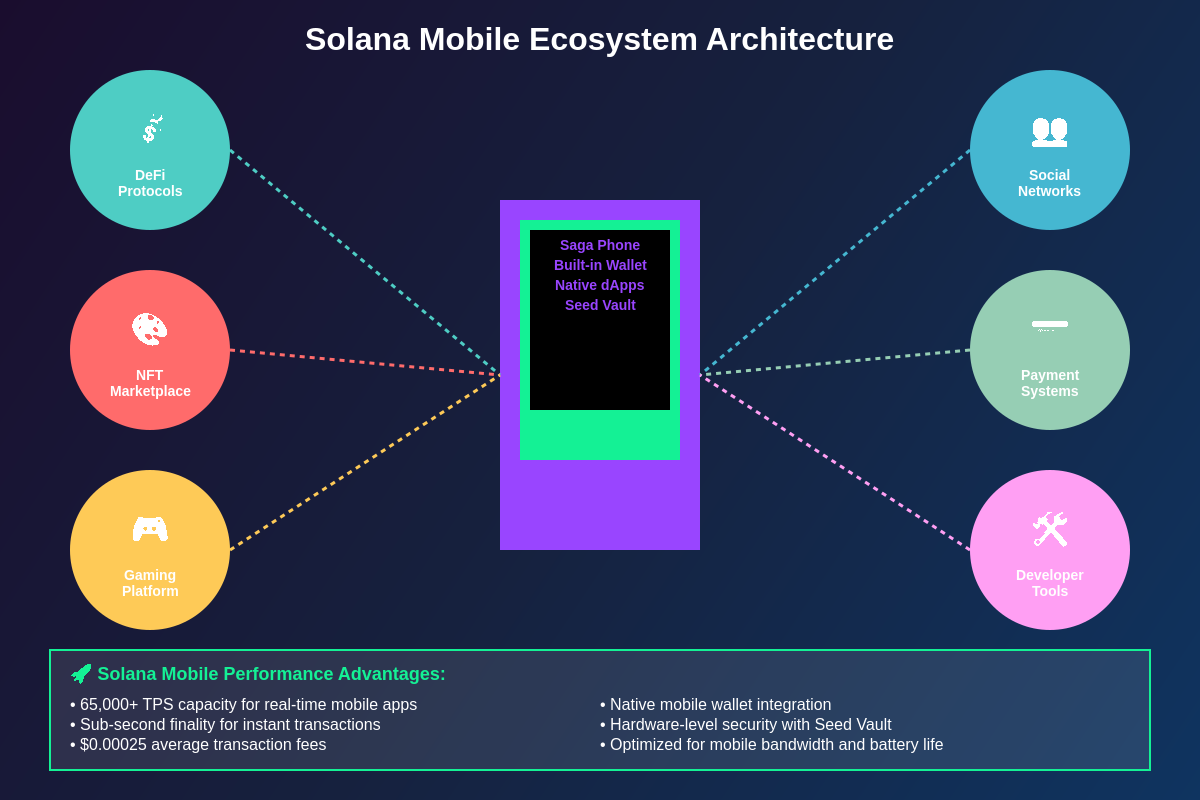
Buying SOL is straightforward. You can send SOL from an exchange or another wallet directly to the public address shown in the phone's wallet app. The address display includes a QR code you can scan with any wallet app. Receiving payments works the same way. Sending is where the interface gets more detailed because every transaction shows you the recipient address, the amount, the priority fee, and the estimated confirmation time before you approve it. Interacting with DeFi protocols on the phone requires using the built-in browser or a compatible wallet app that supports the phone's secure element. Most major Solana DeFi apps like Jupiter, Raydium, and Orca have web interfaces that work through the phone's browser. You navigate to the protocol, connect your wallet by approving the connection request that pops up on the phone, and then sign each transaction as it appears. The approval screen shows you a human-readable summary of what the transaction does, which is useful for catching mismatched contract addresses or unexpected token approvals. I run into an issue regularly where a dApp has you approve a spending limit for a token you haven't used in months. The phone's secure element will still show the approval screen, but if you're not paying attention you might accidentally grant unlimited access to a token contract. The workaround I use is to check the "Max Approval" toggle on the approval screen. Most protocols default to this, but you can switch it to a specific amount. This takes an extra five seconds per transaction and has saved me from revoking unnecessary allowances three times already.
Limitations and Where It Falls Short
The Solana Phone is not a magic solution for every Web3 use case. It only supports Solana natively. If you hold assets on Ethereum, Arbitrum, or Polygon, you still need a separate wallet for those chains. The phone does not have multi-chain hardware wallet support built in. Some people assume they can run MetaMask or Phantom inside the dApp browser and have those wallets use the secure element, but that's not how it works. Those browsers can install regular extensions, but those extensions won't be able to access the secure element. They'll fall back to software-based signing, which defeats the main purpose of owning the phone. Another limitation is app compatibility. Since the phone runs a modified Android environment, some apps that check device integrity or require rooted-device detection may refuse to run. I had trouble with a couple of smaller DeFi dashboards that flagged the custom launcher as an unauthorized environment. The workaround for those was to switch to the phone's standard launcher mode, which disables the Solana-specific wallet integration but lets you use regular apps normally. You lose the secure element protection in that mode, so it's not ideal for anything involving sensitive transactions. NFT trading on the phone is functional but not as fluid as using a desktop browser. The built-in NFT viewer shows thumbnails and metadata, but transferring NFTs between wallets requires going through a transaction flow that can feel clunky on a phone screen. I've found that using a desktop computer for large NFT purchases and then viewing them on the phone works better than trying to do everything on the device itself. The phone excels at routine transactions like sending tokens, staking SOL, or interacting with familiar DeFi protocols. It struggles with complex multi-step NFT marketplace flows that are designed for larger screens.
Security Considerations
The secure element provides real protection against remote attacks. Malware on the Android side cannot read your private keys or sign transactions without your physical approval on the secure element screen. However, the phone is not immune to physical attacks. If someone steals your phone and knows your PIN, they can authorize transactions. The biometric lock helps here, but it's not a substitute for keeping the device secure in the first place. I recommend enabling the remote wipe feature available in the settings panel. If you lose the phone, you can trigger a wipe from a linked email account that erases the Android side while leaving the secure element intact. You'll lose access to your funds unless you have your seed phrase written down, but at least the phone itself won't become a liability. Phishing remains the biggest threat regardless of the device you use. The phone's approval screen is designed to show you transaction details before you sign, but if you approve a transaction without reading what it actually does, the secure element will sign it anyway. I've seen people lose funds this way by approving what they thought was a routine transaction but was actually a token approval for a malicious contract. Reading the approval screen carefully is non-negotiable.
Who Should Actually Use This
If you're actively trading on Solana, staking your SOL, and interacting with DeFi protocols daily, the phone makes sense as your primary wallet device. It removes the need to carry a separate hardware wallet and reduces the attack surface compared to keeping keys in a software wallet on your main phone. If you only dabble in Web3 or primarily use Ethereum-based assets, you'd be better off sticking with a traditional hardware wallet or a well-reviewed software wallet. The Solana Phone is a Solana-first device, and that focus is both its strength and its main constraint. The price point sits somewhere between a mid-range Android phone and a premium hardware wallet combined, which is reasonable if you consider it replaces both. Shipping has been limited to certain regions, and availability fluctuates depending on production cycles. If you're considering buying one, checking the official Solana Labs store or an authorized reseller is the safest route. Third-party sellers have been known to offer refurbished units that may have had their secure elements compromised, so I would avoid anything that isn't sold directly through official channels.