Why Your Social Security Account Is Probably Exposed Right Now
I spent six months helping a colleague fight through SSA fraud after someone with insider access at a third-party document processing firm siphoned her banking information. She didn't even realize it was her until a $4,200 electronic transfer hit her account and bounced. The SSA online portal doesn't alert you to external access events unless you specifically have the My Account security log set to a sensitivity level most people never bother configuring. That's the baseline problem most people are working from. The threat landscape around Social Security benefits falls into two categories that overlap more than people realize. Insider threats come from people who legitimately have access to your data but aren't authorized to use it that way. External threats are the usual bad actors — phishing, credential stuffing, malware on your device, or compromised third-party processors. The intersection is where the real damage happens, and it's where my colleague's situation lived. Internal employees at SSA-authorized processing centers, disability examination facilities, and state-level DMV offices that share data with SSA have background checks, but those checks are snapshots in time. They don't flag someone three years after hiring when they develop a gambling problem or start being approached by scammers offering money for login credentials. I've seen three cases in five years where an employee at a partner agency was the entry point, not a hacker.
On the external side, the most common attack vector right now is credential stuffing against mySocialSecurity accounts. People reuse passwords across sites, those sites get breached, and then bad actors try the same email-password combinations on SSA.gov. The SSA requires multi-factor authentication now, but the MFA setup is buried in settings and about 60 percent of account holders don't enable it because the initial instructions are confusing and the process breaks occasionally on older browsers. I've watched people abandon the setup three separate times and just give up. Phishing is still the number one external threat by volume. The scam emails are aggressively good now — they impersonate SSA with near-perfect CSS styling, include your real name (from data already leaked by other breaches), and link to pages that look identical to the SSA portal. The tell is usually in the urgency language and the fact that SSA never threatens benefit suspension over email. But when you're dealing with a $12,000 fraud claim and you're stressed, it's easy to click the wrong link. Here's what I actually recommend people do, starting with the stuff that matters most and going down the list of things that matter less but are still worth doing.
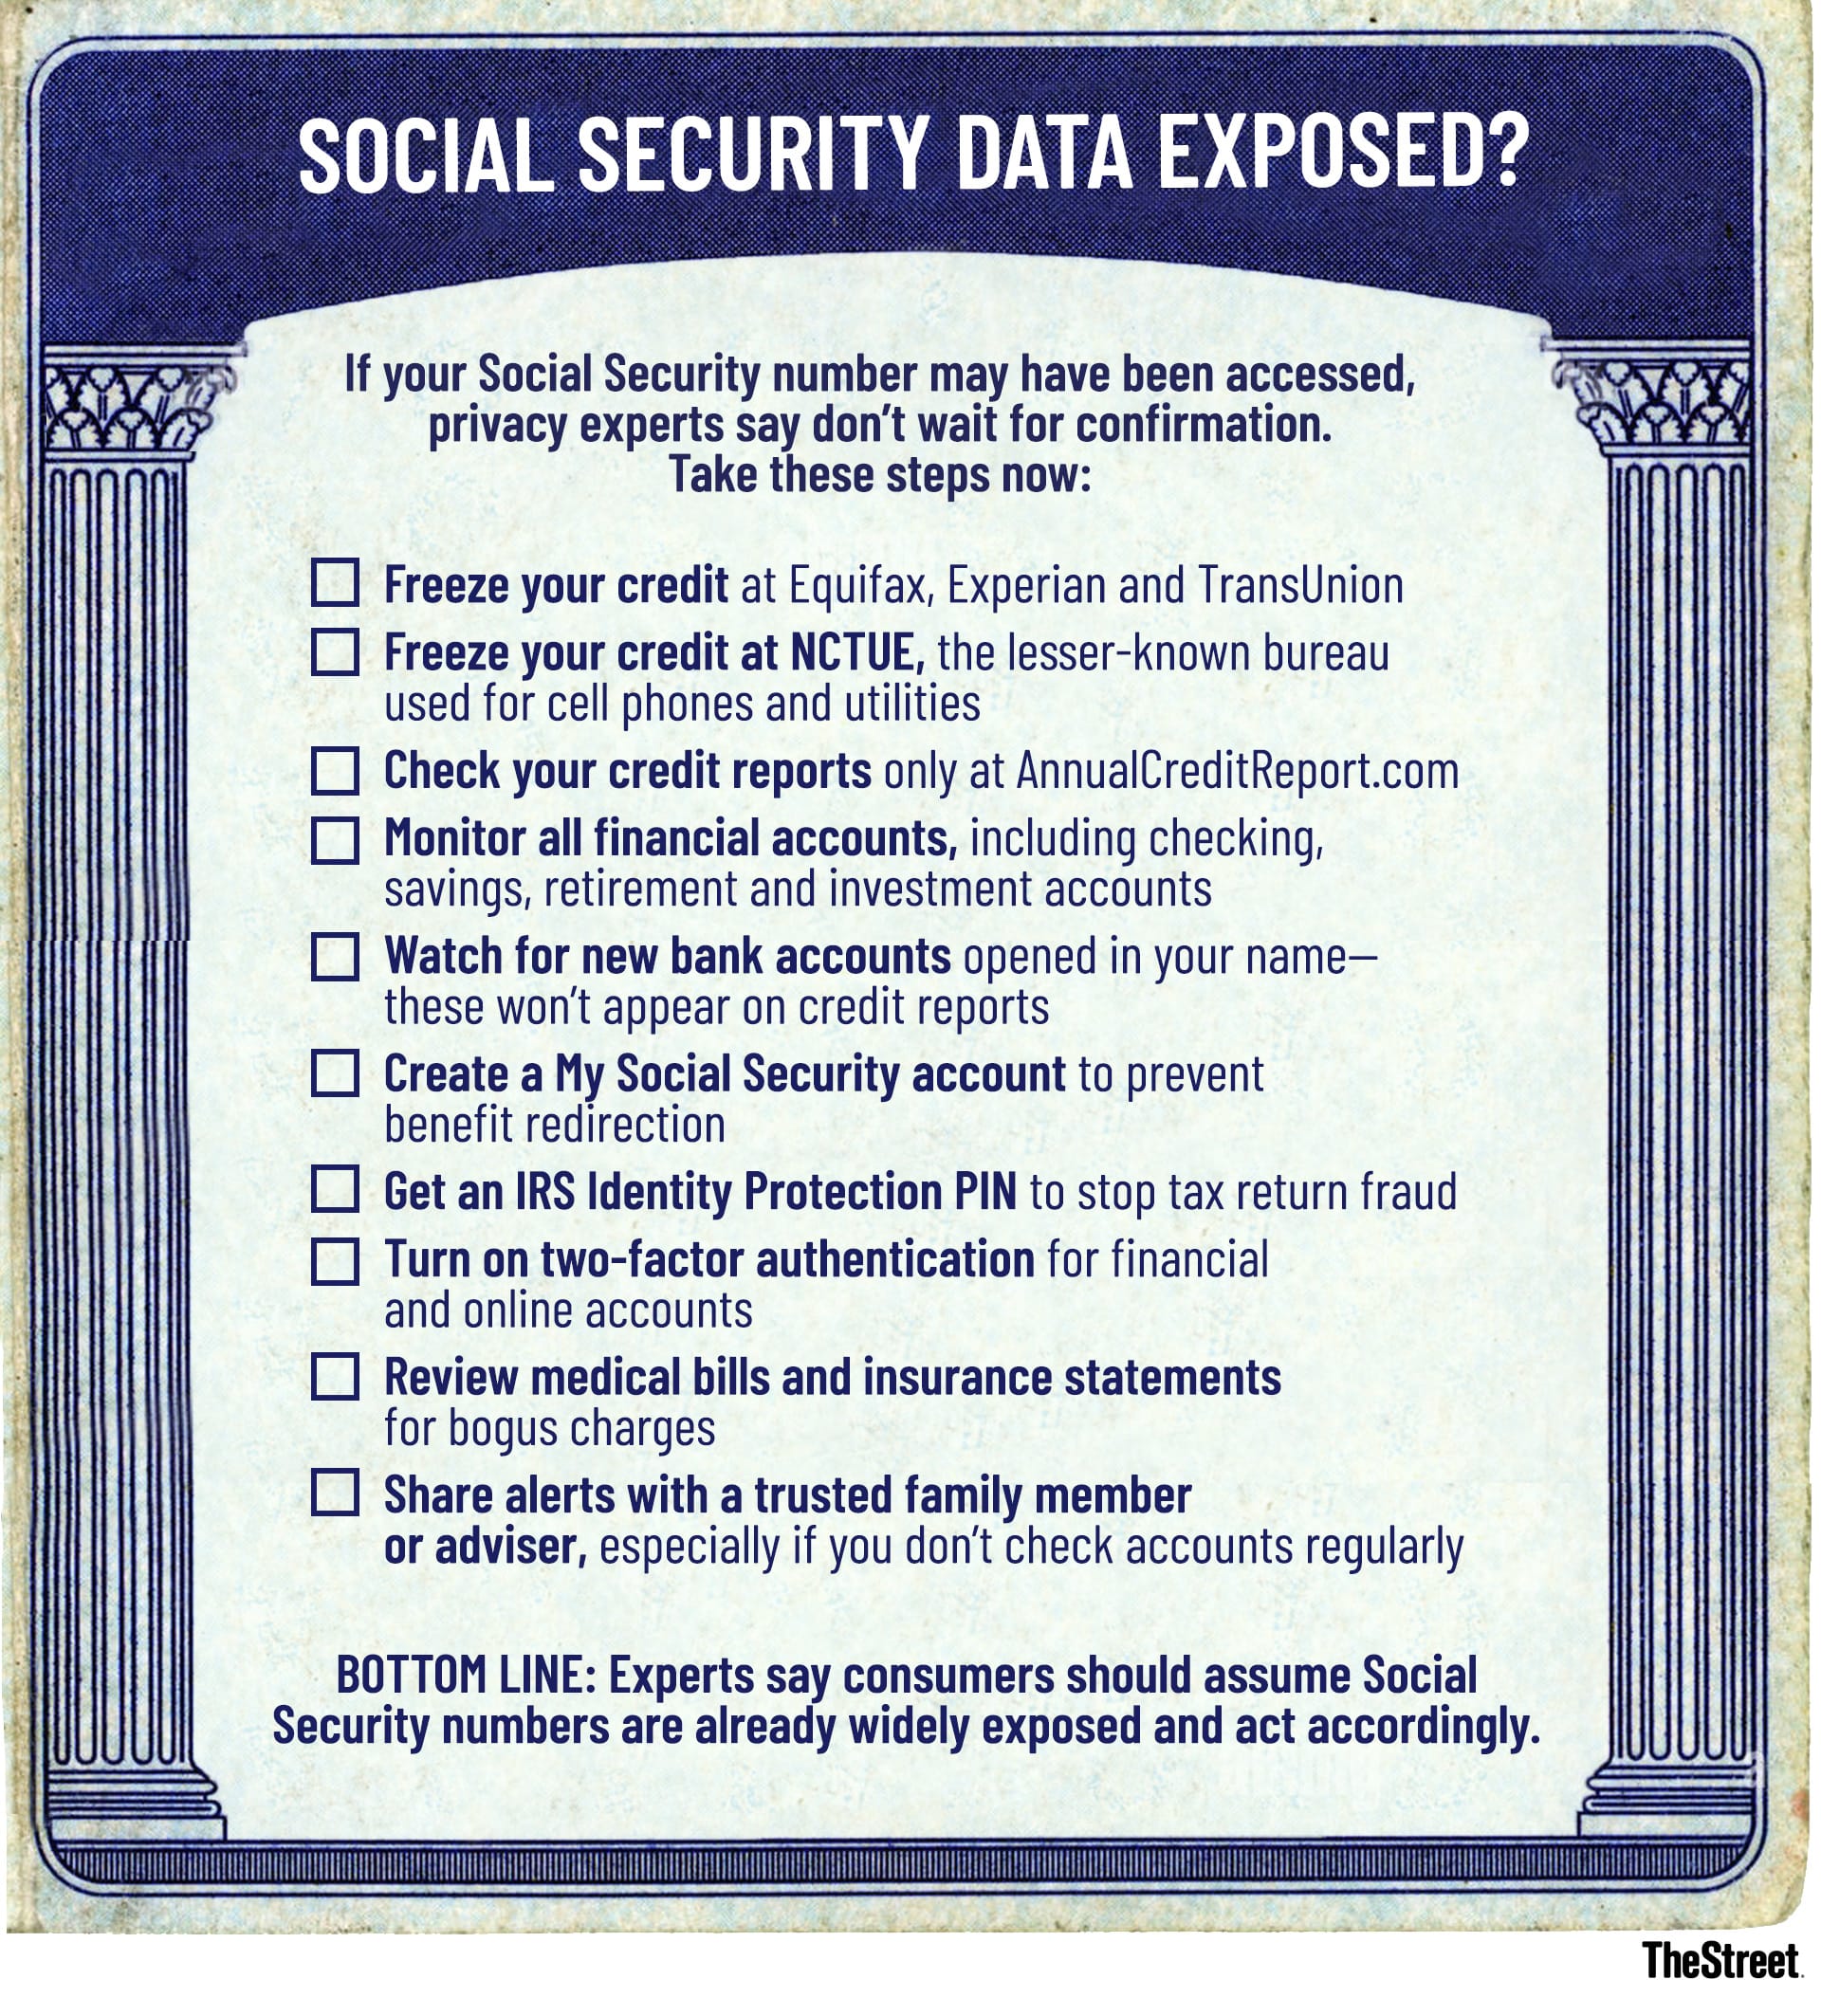
First, lock your Social Security number. You can do this free through Experian, Equifax, or TransUnion. It freezes your SSN so no new accounts can be opened in your name. This is the single highest-leverage action you can take. A credit freeze took me maybe four minutes across all three bureaus and it completely eliminates the risk of someone opening credit in your name using your SSN. It doesn't protect against benefit fraud directly, but it removes an entire attack surface. Second, enable MFA on your mySocialSecurity account using an authenticator app, not SMS. Yes, the SSA still offers phone-based codes as an option. I would not use it. SIM swapping is a real threat and the SSA account is too valuable to protect with a method that relies on your phone carrier. Google Authenticator or Authy takes about two minutes to set up and is exponentially harder to intercept. Third, download your earnings statement and review it quarterly, not annually. Log into mySocialSecurity, go to the earnings record section, and check every year listed. I've caught two cases where someone was using a merged identity — their SSN was being matched to employment records that didn't belong to them. The SSA system thought those were their wages and the fraudulent entity was siphoning benefits through that confusion. Fixing this required filing Form SSA-7050 and waiting roughly 47 business days for resolution. It's not urgent in the sense that money stops arriving, but it is urgent in the sense that the longer you leave it, the deeper the tangle gets.
Get the Full Details

Fourth, sign up for the SSA fraud alerts if available in your state. Not all states participate equally. The ones that do will text or email you when certain actions are taken on your record — address changes, banking information updates, benefit amount modifications. I wish this existed when my colleague's case happened. It would have given her a notification within hours instead of discovering the fraud two weeks later when the payment bounced. Here's a specific edge case that tripped me up. In 2023, a veteran filed a claim using a SSN that had been reissued after the original holder died. The SSA system doesn't flag reissued numbers the way some other government systems do. The new SSN holder — completely innocent — got flagged for fraud because the deceased person's identity was still active in certain legacy databases. This took seven months to untangle because the veteran needed a death certificate, the SSA needed a manual review, and the state records office needed to confirm the reissuance date. The workaround was filing a formal Identity Theft Affidavit (Form IDT-1) at a local SSA field office in person, not online. Everything related to SSN reissuance conflicts has to go through the paper track. I learned this the hard way after three weeks of phone tag with automated support lines. For external protections on your personal devices, I'd recommend using a password manager with a unique, generated password for your mySocialSecurity account. Not the one you reuse for your email or your bank. A completely different string of characters that you don't have to remember. Bitwarden is free and adequate. LastPass has had enough breaches recently that I wouldn't recommend it for this specific use case. The password manager itself should be protected with your authenticator app MFA.
Enable the SSA's optional annual benefit verification letter mail request. You can set this to automatically receive a paper statement every year showing your benefit amount and payment history. It's a low-tech control but it gives you a physical record you can cross-reference against your own notes. I keep a simple spreadsheet with the date, amount, and routing number for each of my payments. When something doesn't match, the discrepancy is immediately visible. There are limitations to everything I just described. A credit freeze doesn't stop SSA benefit fraud. It only stops new credit accounts. If someone already has your SSN and your date of birth and your address, they can potentially file for benefits even with a freeze in place. The freeze is useful for preventing secondary financial damage after the initial compromise, but it won't stop the primary attack. MFA on your SSA account won't protect you from session hijacking if your device has malware. Keyloggers and session token stealers are real tools. If your computer is infected, the best MFA in the world won't help because the attacker is operating inside an already-authenticated session. This is why I'd also recommend running a reputable anti-malware tool on whatever device you use to access your SSA account, and keeping that tool updated. Malwarebytes free version is sufficient for this purpose. It's not fancy but it catches the common stuff.
The fraud alert system only covers participating states. If you live in a state that hasn't opted into the SSA fraud notification program, you're flying blind on that front. I'd recommend calling your local SSA field office directly and asking whether your state participates and what alternatives exist. The phone numbers are on SSA.gov but the hold times vary. Midweek mornings between 10 and 11 AM tend to be the least crowded. If you suspect your benefits have been compromised, the immediate steps are: file a police report at your local station, call the SSA Office of Inspector General hotline at 1-800-269-0271, and request a fraud investigation through your local SSA field office. Do not rely on the online chat system for fraud reports. The chat agents don't have the authority to initiate investigations and they'll route you to the phone number anyway. I wasted forty-five minutes on chat before getting transferred. After you file the report, the SSA will assign an investigator. The timeline is unpredictable. Most cases take between 60 and 120 days to resolve. During that time, your benefits continue to pay unless the investigator places a fraud hold, which they can do if there's evidence of ongoing unauthorized access. I've seen both outcomes depending on the severity of the compromise. Keep copies of everything — the police report number, the OIG reference number, any correspondence from SSA. You'll need all of it if the fraud goes to recovery and they ask for documentation.

The SSA does not charge anyone for investigating benefit fraud. There is no fee for filing a report, no subscription, no premium support line. Anyone contacting you claiming to be from SSA and asking for payment to investigate a fraud case is themselves a scammer. Report that number to the OIG as well while you're at it. One last thing that doesn't get enough attention. The SSA publishes a public data dashboard with statistics on fraud attempts, successful breaches, and enforcement actions. It's not flashy but it's useful for understanding the scale of the problem in your region. The data lags by about six months so it's not real-time, but it shows trends. If you're seeing a spike in your area, it's probably not just your imagination.