SNI Explained What It Is How Its Used And Why It Matters For Modern Internet Security
Server Name Indication is a TLS extension that lets you specify which hostname you're trying to reach during the initial handshake. It was created around 2003, standardized in RFC 3546, and has become absolutely essential because the internet runs on virtual hosting.
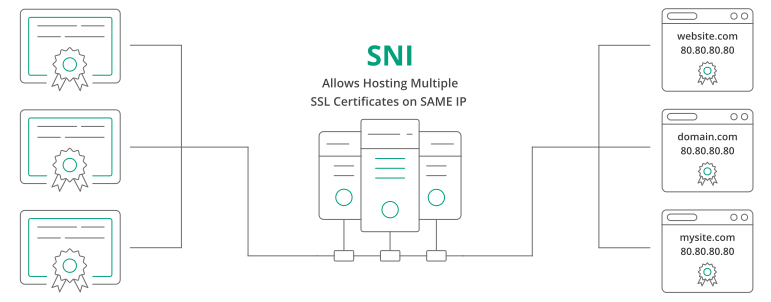
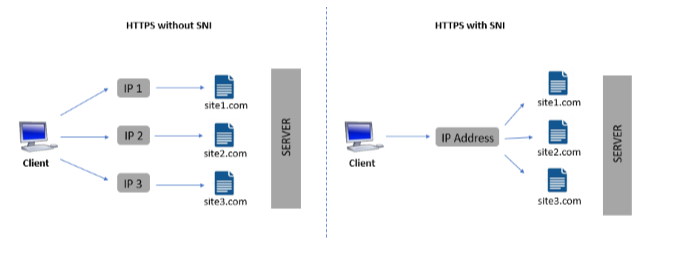
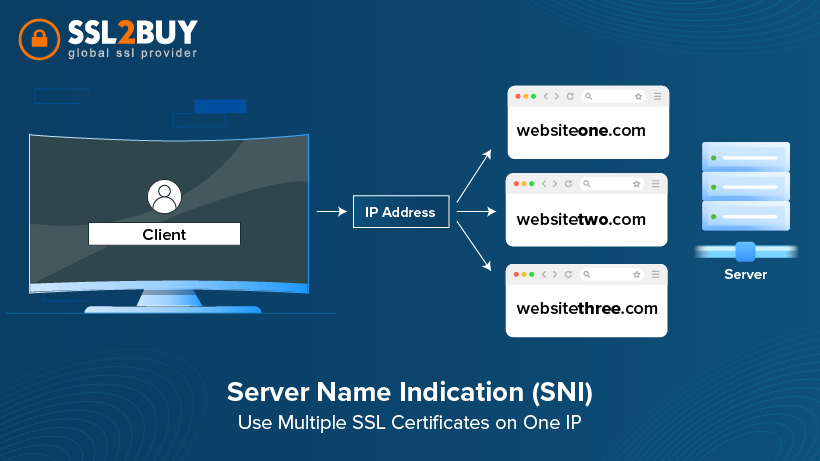
Here's the thing that trips people up. Before SNI existed, a single IP address could only serve one SSL certificate. If you wanted multiple websites on one server, each needed its own IP. That consumed IPv4 addresses faster than anyone anticipated. SNI solves this by embedding the hostname in the ClientHello message, allowing the server to pick the right certificate based on the requested domain. During a TLS 1.2 or 1.3 handshake, the client sends a ClientHello containing the server_name extension with the target hostname as a value. The server reads this before responding with its Certificate message. It then selects and presents the appropriate certificate for that domain. This happens in plaintext during the handshake, which creates the privacy concerns we'll get to later. The extension type is 0 in the TLS extension format. It carries a list of server names, though virtually every implementation sends exactly one. Some edge cases involve SNI with IP address literals, but most servers reject those or fall back to a default certificate. Wildcard certificates complicate things too - if you request foo.example.com but the server only has *.example.com, the handshake succeeds, but certificate validation might fail depending on the client's trust store.
Why This Actually Matters
Without SNI, running a web host would require purchasing separate IP addresses for each domain. With IPv4 exhaustion at 255.255.255.255 across the global pool, that approach became impossible around 2011. Today roughly 95% of HTTPS traffic relies on SNI. Cloudflare, AWS, Google Cloud - every major provider depends on it. The security angle is more nuanced than people realize. SNI leaks the hostname you're connecting to because it's sent unencrypted. This means anyone monitoring your TLS handshake can see which website you're visiting, even though the actual content remains encrypted. ISPs, corporate firewalls, and surveillance systems use this information extensively. I ran into a specific problem last year working with a legacy payment gateway that rejected SNI-enabled connections. The server was configured to only accept the deprecated single-IP hosting model. The workaround was forcing the application to use a dedicated IP address and configuring DNS to point exclusively to it. This added about $50/month to the hosting bill and required updating the load balancer rules, but it resolved the handshake failures immediately.
Common Pitfalls and Edge Cases
Certificate transparency logs sometimes reveal SNI values that organizations didn't intend to expose. If your internal services use SNI with private hostnames like api.internal.example.com, those appear in public CT logs when browsers send them during certificate validation checks. This happened to a fintech company I consulted with - their internal API hostnames were visible in public logs for three months before anyone noticed. Mobile carriers and some corporate networks block or modify SNI values. Android devices before version 7.0 had inconsistent SNI handling, causing certificate mismatches on certain VPN configurations. iOS has been more consistent but still drops SNI when using certain proxy modes. If you're building an app that needs reliable TLS connections across different network environments, test with SNI disabled as a fallback path. Another issue involves HTTP/2 and SNI. The protocol requires the :authority pseudo-header to match the SNI value. Mismatches cause connection resets in strict implementations. I spent two days debugging this with a custom API gateway that validated :authority against the TLS certificate subject but ignored SNI. The fix was adding SNI validation to the gateway's certificate chain verification logic.
Get the Full Details
Privacy Workarounds
ESNI (Encrypted SNI) was introduced in RFC 9001 as a solution, encrypting the server_name extension. Chrome and Firefox support it, but adoption remains limited because not all servers implement the corresponding ESNI public key publishing mechanism. Without ESNI support on both ends, the extension provides no privacy benefit. Oblivious SNI is another approach where a proxy intercepts the ClientHello, removes the plaintext SNI, and forwards the request through an encrypted tunnel to an OSNI-aware proxy that reveals the SNI only to the destination server. This adds latency and requires trusted intermediary infrastructure, but it eliminates the plaintext leakage. For most users, the practical solution is using a VPN or proxy that handles SNI encryption at the transport layer. Tools like Tor strip SNI before forwarding, but they introduce significant latency and aren't suitable for real-time applications. The tradeoff between privacy and performance usually forces a choice between full visibility and complete anonymity.
Implementation Details That Matter
Nginx configurations require the ssl_stapling and ssl_certificate directives to work properly with SNI. A common misconfiguration is specifying a default_cert without also configuring the SNI-aware certificate selection. This causes all requests to receive the default certificate, triggering browser security warnings for every domain except the primary one. AWS Load Balancers handle SNI automatically but have quirks with certificate rotation. When you update a certificate through ACM, the load balancer takes approximately 5 minutes to propagate the change across all availability zones. During this window, some regions serve the old certificate while others serve the new one, causing intermittent connection failures for clients with strict certificate pinning. Docker and containerized deployments often miss SNI configuration entirely. If you're running multiple services behind a reverse proxy in containers, each service needs its own certificate or you need wildcard certificates covering all subdomains. I encountered a deployment where 15 microservices shared a single certificate, but the SNI routing rules weren't configured in the ingress controller. The result was random certificate mismatches depending on which pod handled the request.
Legacy System Compatibility
p>Some enterprise applications still disable SNI support intentionally. Banking systems, government portals, and legacy ERP installations sometimes require dedicated IP addresses for compliance reasons. These systems predate SNI adoption and may not handle the extension gracefully, causing handshake failures with modern browsers that always send SNI.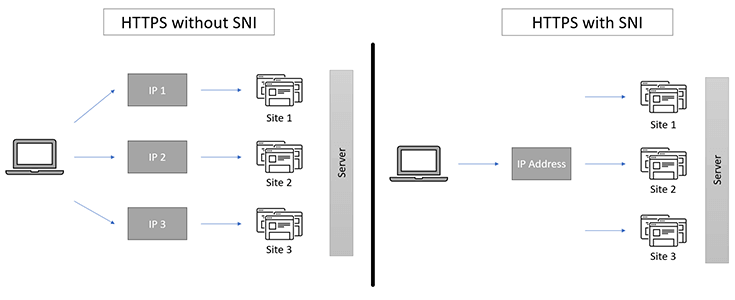
The workaround involves configuring proxy servers to terminate TLS connections without forwarding SNI to the backend. HAProxy and Envoy support this through the ignore_sni configuration option. However, this approach requires maintaining separate IP addresses for each service, which increases infrastructure costs and complicates DNS management. Testing SNI compatibility should be part of any TLS migration project. Use tools like openssl s_client with the -servername flag to verify that servers respond correctly to SNI requests. Check that certificate validation succeeds across different user agents, as some older clients send malformed SNI values that modern servers reject.