Getting Started With Sinai Cloud Login
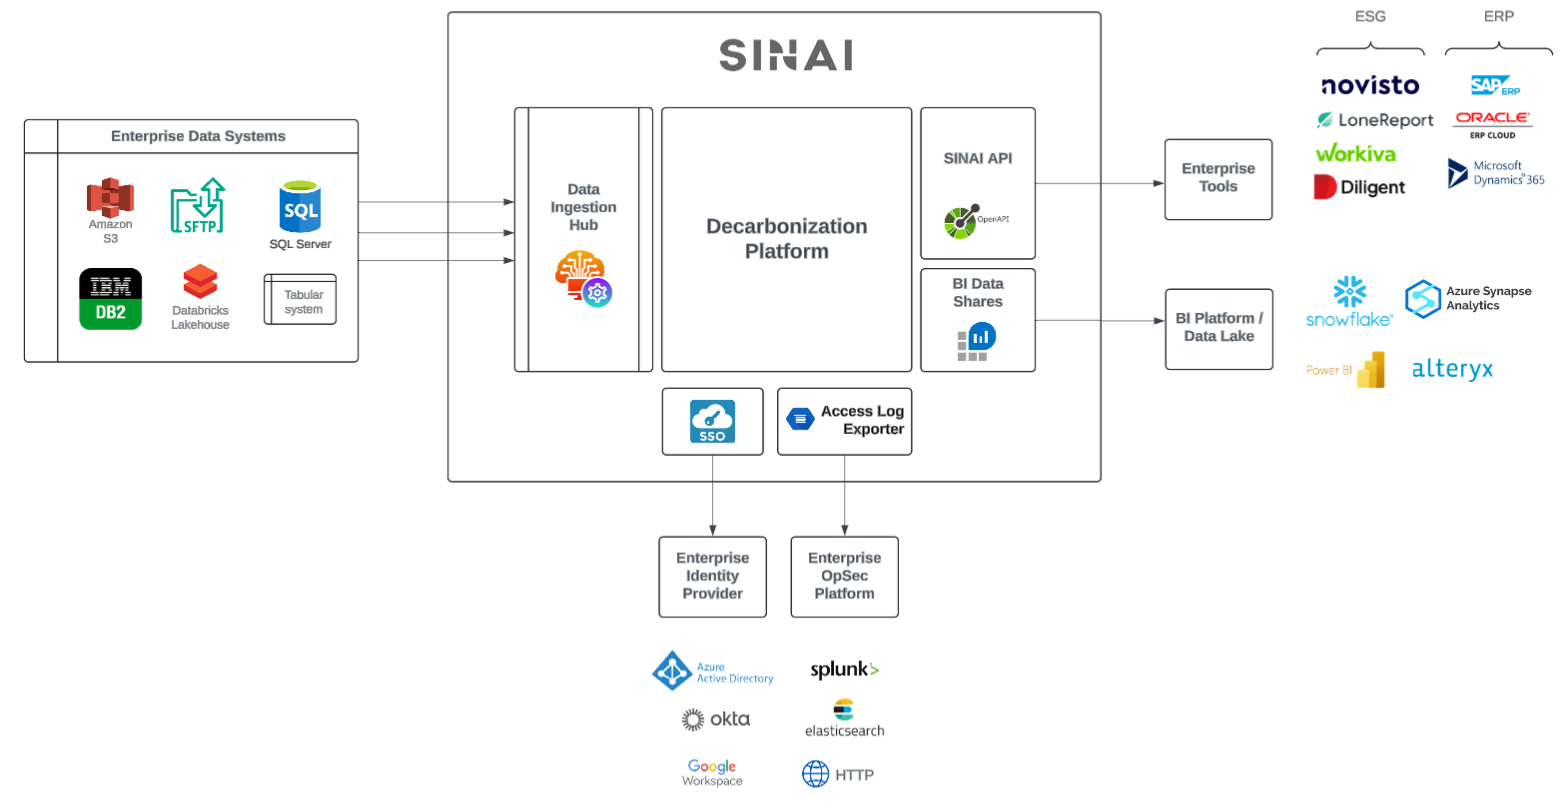
Most people approach Sinai Cloud Login Your Secure Gateway To Scalable Compliant Cloud Operations expecting a typical vendor dashboard experience. It is not. The interface is functional but deliberately sparse. You will spend more time configuring access policies than clicking through welcome screens. That is by design, and it matters when you are dealing with enterprise compliance frameworks. The core value here is centralized identity orchestration across multi-cloud environments. Instead of maintaining separate credential stores for AWS IAM, Azure AD, and GCP beyond a simple SSO layer, Sinai acts as the single enforcement point. Authentication passes through Sinai first, then policies are evaluated before any cloud session is established. The compliant cloud operations piece comes from the audit trail and policy engine that sits between you and your actual cloud consoles. I spent about three weeks setting this up for a client running workloads across AWS and Azure. The documentation covers the happy path well enough. Where things get rough is around conditional access rules tied to existing MFA implementations. If your organization uses hardware tokens or a custom RADIUS setup rather than a standard Duo or Okta integration, the pre-built connectors won't handle it cleanly. You need to configure a custom LDAP passthrough, which means writing the attribute mapping manually. I ended up spending a full day just on that because the example mappings in the guide assume standard Active Directory schemas. Once configured correctly, though, it works without issues.
How The Authentication Flow Actually Works
When a user attempts to access any integrated cloud provider, the request routes to Sinai first. The platform checks the user's identity provider, validates the MFA session, then evaluates the access policy attached to that user's role. Only after that evaluation completes does Sinai issue the temporary credentials or SSO token to the target cloud. This means you can enforce conditions like geolocation, device posture, and time-of-day restrictions before any cloud API call is even attempted. That is where the compliance angle becomes real — most cloud providers' native logging won't show you who authenticated from where or what device was used. Sinai captures that upstream. Here is something the marketing material glosses over: the credential rotation happens automatically for services, but not for human users in the way you might expect. Service accounts integrate through API key injection into Sinai's vault. Human accounts go through SAML or OIDC. Mixing the two in the same policy tree creates evaluation order bugs if you don't understand how the priority ladder works. Service account policies are evaluated first, then user policies. If a service account has a broader scope defined in the same OU as a restrictive user policy, the service account rule wins every time. I learned this when an automated deployment pipeline started getting blocked by a compliance policy meant for contractors. Took me about four hours to trace the issue back to OU inheritance.
Setting Up Your First Cloud Integration
Start with one cloud provider. Two at most. Adding AWS first is generally smoother because Sinai has native support for IAM Identity Center, which maps cleanly to their role structure. Azure requires you to sync your Entra ID groups explicitly — Sinai does not automatically pull group membership the way you might hope. You need to create the group mappings manually in the admin console, and the sync is not real time. It runs on a roughly fifteen-minute interval, so expect a delay when you add someone to an access group and try to test immediately. The installation itself is straightforward. You deploy the Sinai agent on a VM or container within your network, point it at your identity provider, and configure the cloud provider connections through their API. That part takes maybe twenty minutes if your API credentials are ready. The actual policy configuration is where the time goes. Plan for several hours on your first environment. I recommend writing out your role definitions on paper first. Trying to map them visually in the console leads to mistakes.
Get the Full Details

Common Pitfalls That Slow You Down
Session timeout misconfiguration is the most common issue I see. By default, Sinai sets session tokens to refresh every hour. For most cloud management tasks that is fine. For continuous deployment pipelines or long-running ETL jobs, you will start seeing intermittent authentication errors around the two-hour mark unless you adjust the refresh behavior. The fix is in the policy editor under advanced session settings. Set a longer idle timeout and enable persistent session validation. Another thing that catches people: Sinai does not support AWS STS session policies that reference resource tags. If your cloud access depends on tag-based permissions, you need to evaluate whether that constraint will break after the Sinai gateway sits in front of your flows. It will, unless you restructure your IAM policies to be attribute-based instead of tag-based. There is also a hard limitation around cross-region compliance reporting. If you run Sinai in us-east-1 but your AWS accounts span multiple regions with different compliance requirements, the audit logs aggregate into a single view. You can filter by region, but the reporting export function does not segment by regulatory framework. So if you need separate evidence bundles for SOC 2 and HIPAA workloads, you will be doing manual segmentation after export. It is a known gap that their roadmap mentions but has not shipped yet.
What It Handles Well and Where It Falls Short
Sinai excels at centralizing authentication across disparate cloud accounts. If you have fifteen AWS accounts and eight Azure subscriptions and each one has its own user management chaos, Sinai imposes order quickly. The policy engine is mature and the audit logging meets most regulatory requirements out of the box. Multi-tenant setups are also handled cleanly, which matters if you are a managed service provider. Where it struggles is flexibility in edge cases. Custom attribute mapping requires technical comfort with LDAP schemas. The UI is not particularly intuitive for non-technical administrators, and error messages during policy evaluation are vague. You will often see a generic "policy denied" response without enough detail to tell you which specific rule triggered it. Enabling verbose logging adds about ten percent overhead to authentication calls, which may or may not matter depending on your volume. Their support response time is reasonable — usually within a few hours for paid tiers — but they do not offer phone support, only ticket-based. If your environment is purely single-cloud and you already have a mature IAM setup, Sinai probably adds more complexity than value. You are better off sticking with your native cloud provider's IAM tooling and saving the implementation hours. Sinai pays for itself when you are managing five or more cloud accounts across two or more providers with separate compliance requirements.