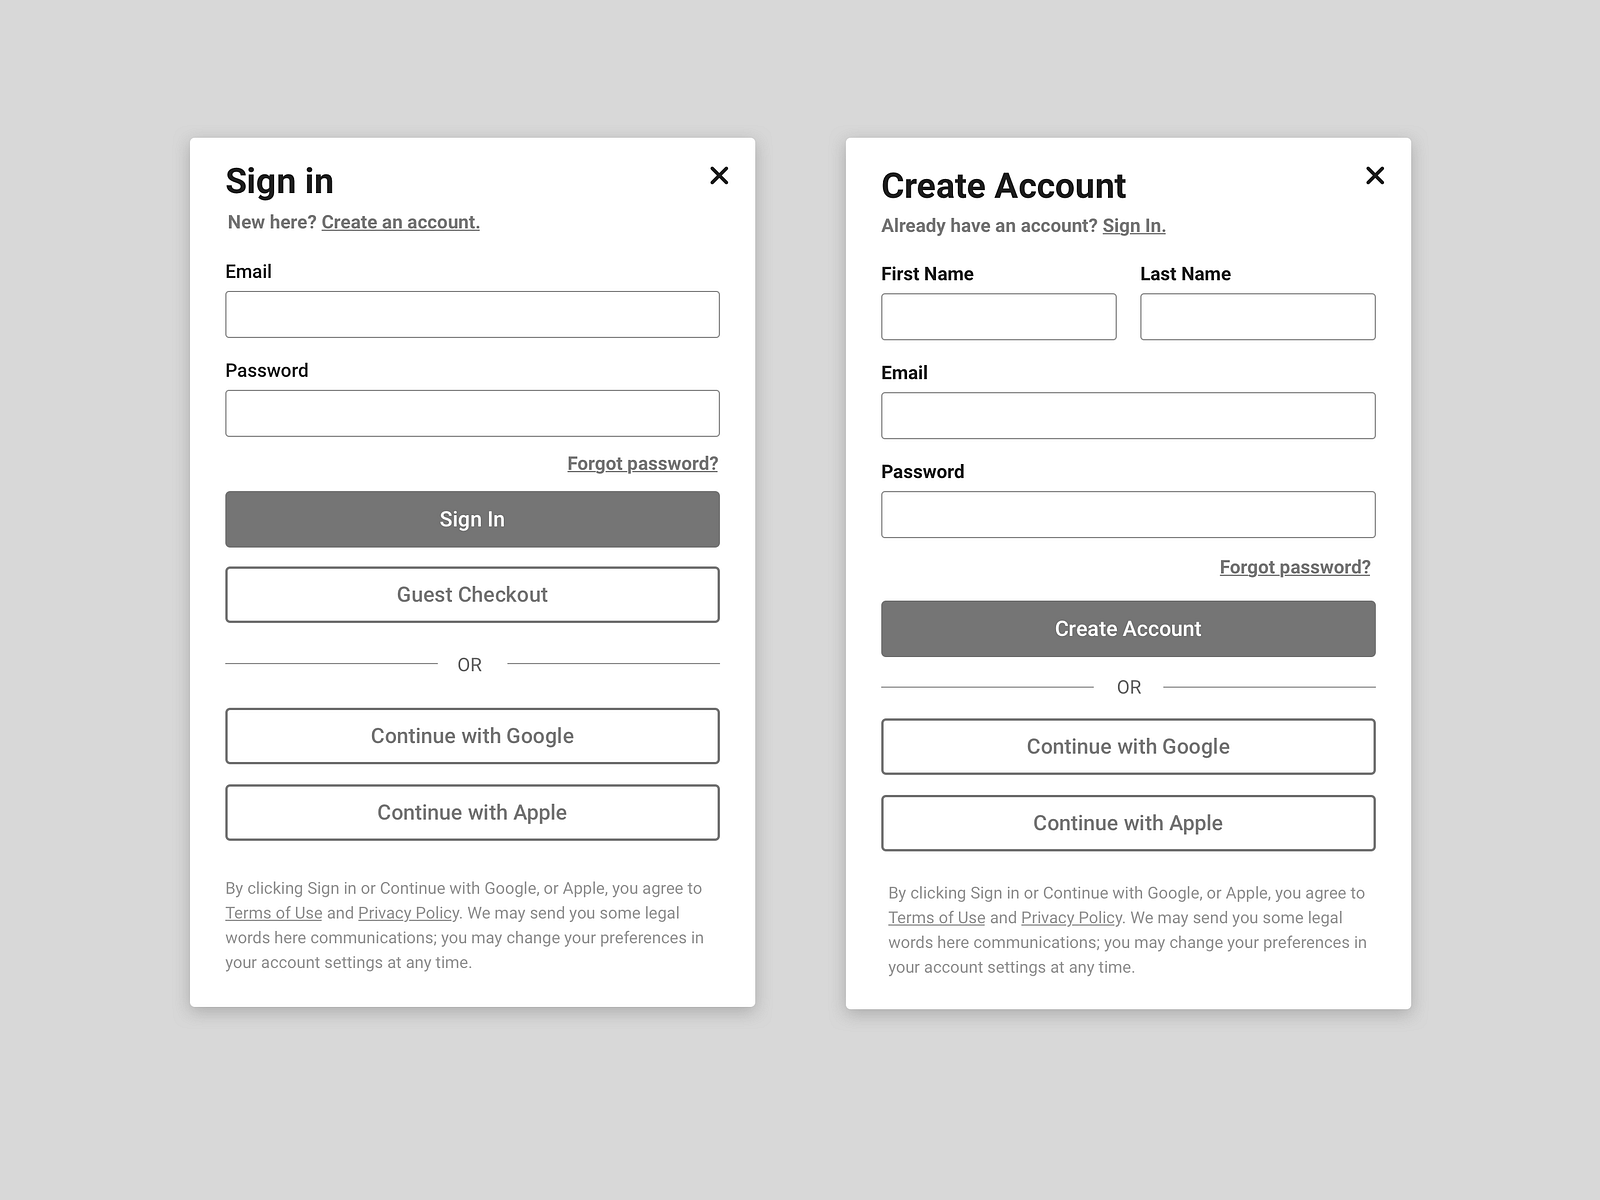
Let's Talk About Sign In vs Create Account
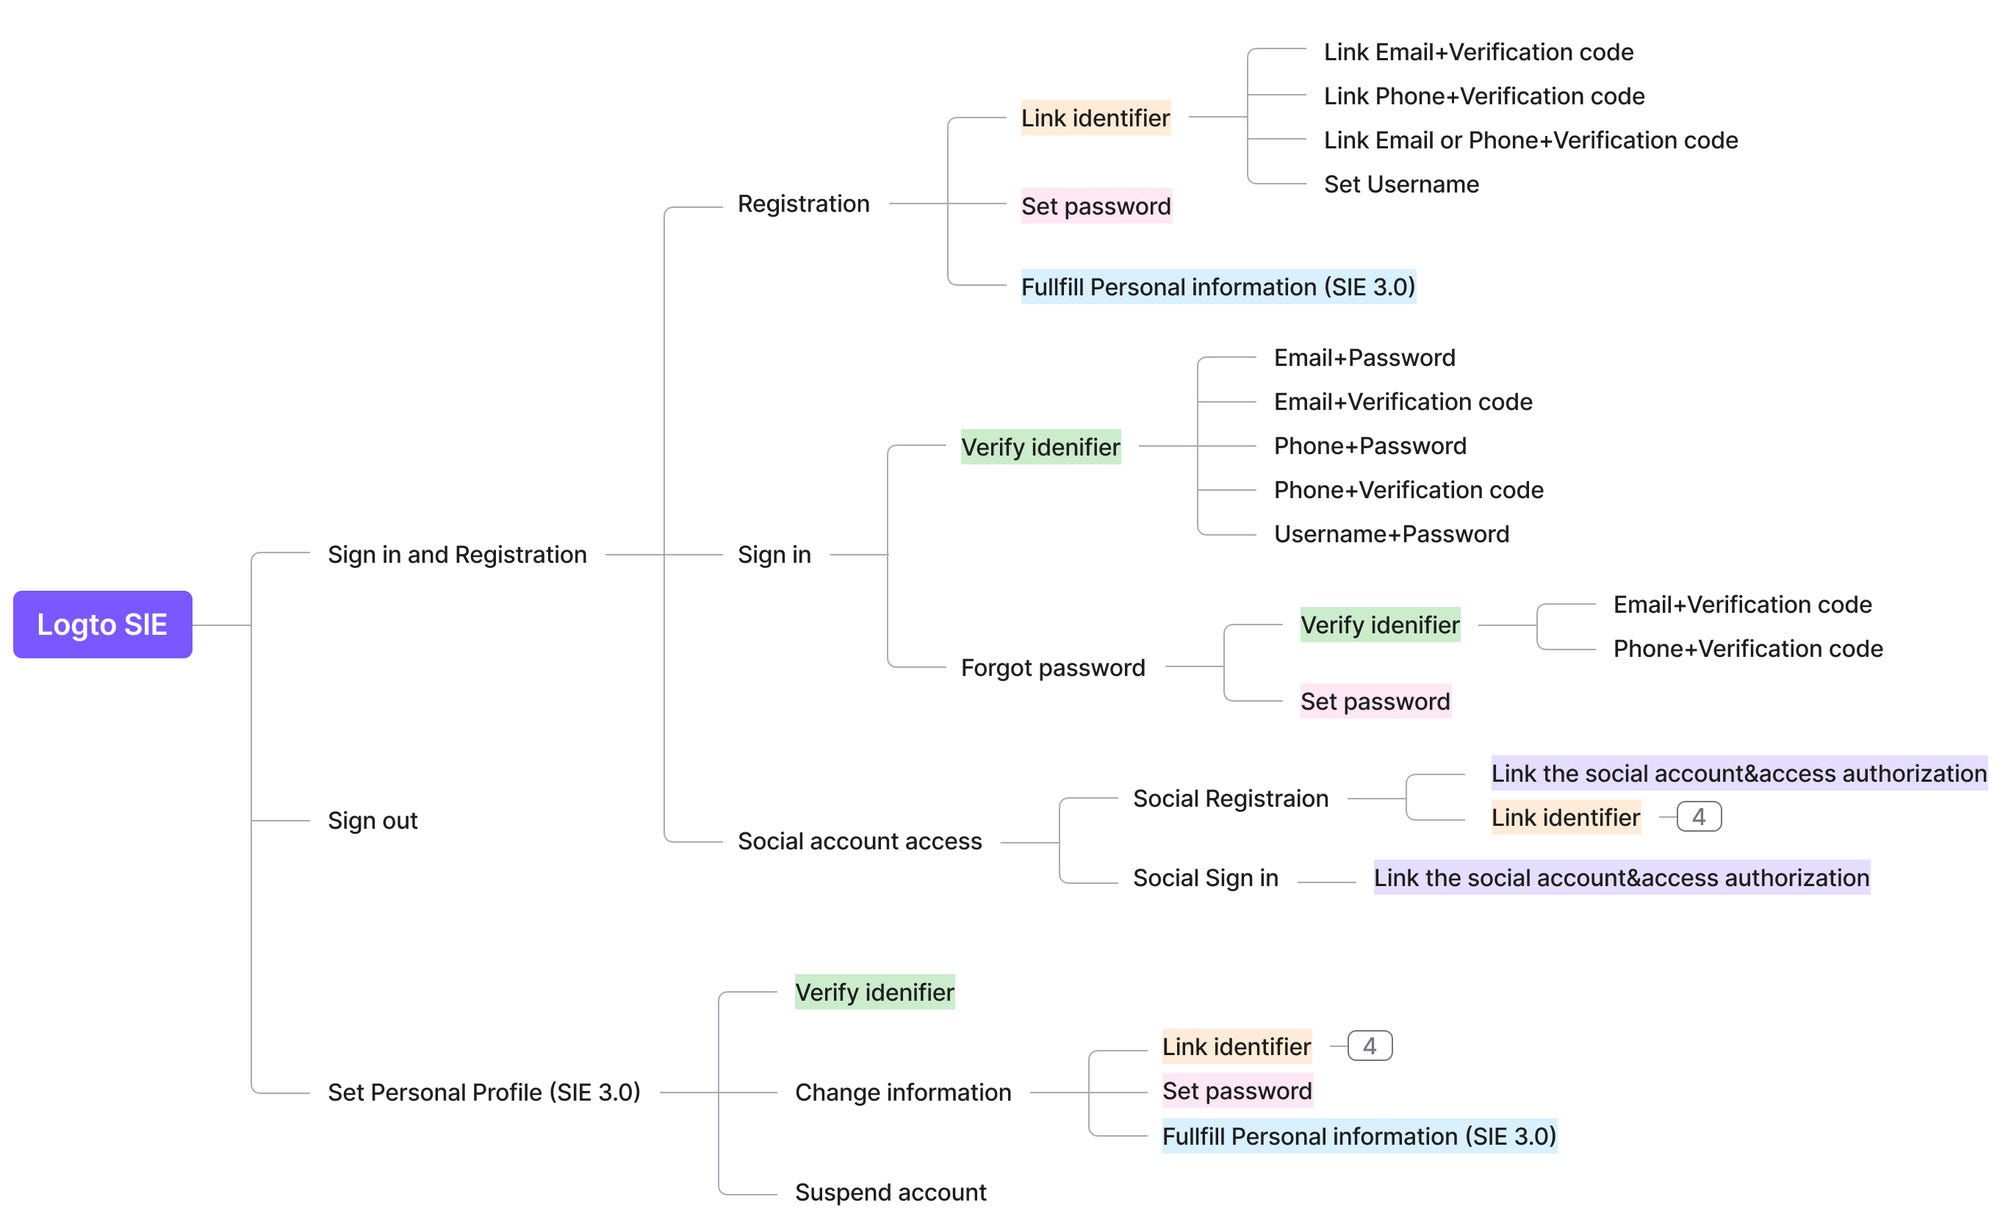
Most people treat the sign in and create account prompt as just a friction point on their way to whatever they want to do. It's not. It's a decision gate that determines how your data flows, how your identity is verified, and how much work your engineering team has to maintain downstream. The tradeoffs are real and usually hidden behind a very clean UI. When a product asks you to sign in, it's saying: I already have you in my system, give me proof of who you are. When it asks you to create an account, it's saying: I don't have a record for you yet, I need you to volunteer enough information for me to build one. Those two operations look similar on the surface but they trigger entirely different backend processes. Signing in typically means authenticating against an existing identity store. That could be your own database, Auth0, Firebase, Cognito, whatever. The flow checks credentials, issues a token, and maps the session to a user record that was created weeks, months, or years ago. It's fast because the heavy lifting already happened.
Creating an account means inserting a new row into your user table, hashing a password or provisioning an OAuth link, potentially running fraud checks, triggering welcome emails, and firing off attribution events to figure out where this person came from. Every one of those steps is a failure point. I've seen onboarding flows fail silently at the attribution step and still show the user a success screen. The account existed in the database but never connected to the marketing pipeline, so the cohort looked wrong for six months before anyone noticed. Here's what most teams miss. The create account path is actually the more dangerous one from a security perspective, not the sign in path. During sign in, you're verifying credentials against an existing record. During create, you're accepting new data without having established trust yet. Email validation is the bare minimum. Phone verification helps. But the real issue is duplicate creation. I ran into this at a company where we used email as the primary identifier. A user would start creating an account, hit the page, lose connection, and restart. The retry went through before the first attempt completed its async validation. We ended up with two accounts sharing the same email. One had their cart. The other had their payment method. When they signed in, the system picked whichever record was created last by milliseconds, which meant half the time they lost access to their saved items. The fix was a merge script that ran on login when duplicate emails were detected, combining the active session data from both records into one. Took about three weeks to build properly because we had to handle race conditions across four different services.
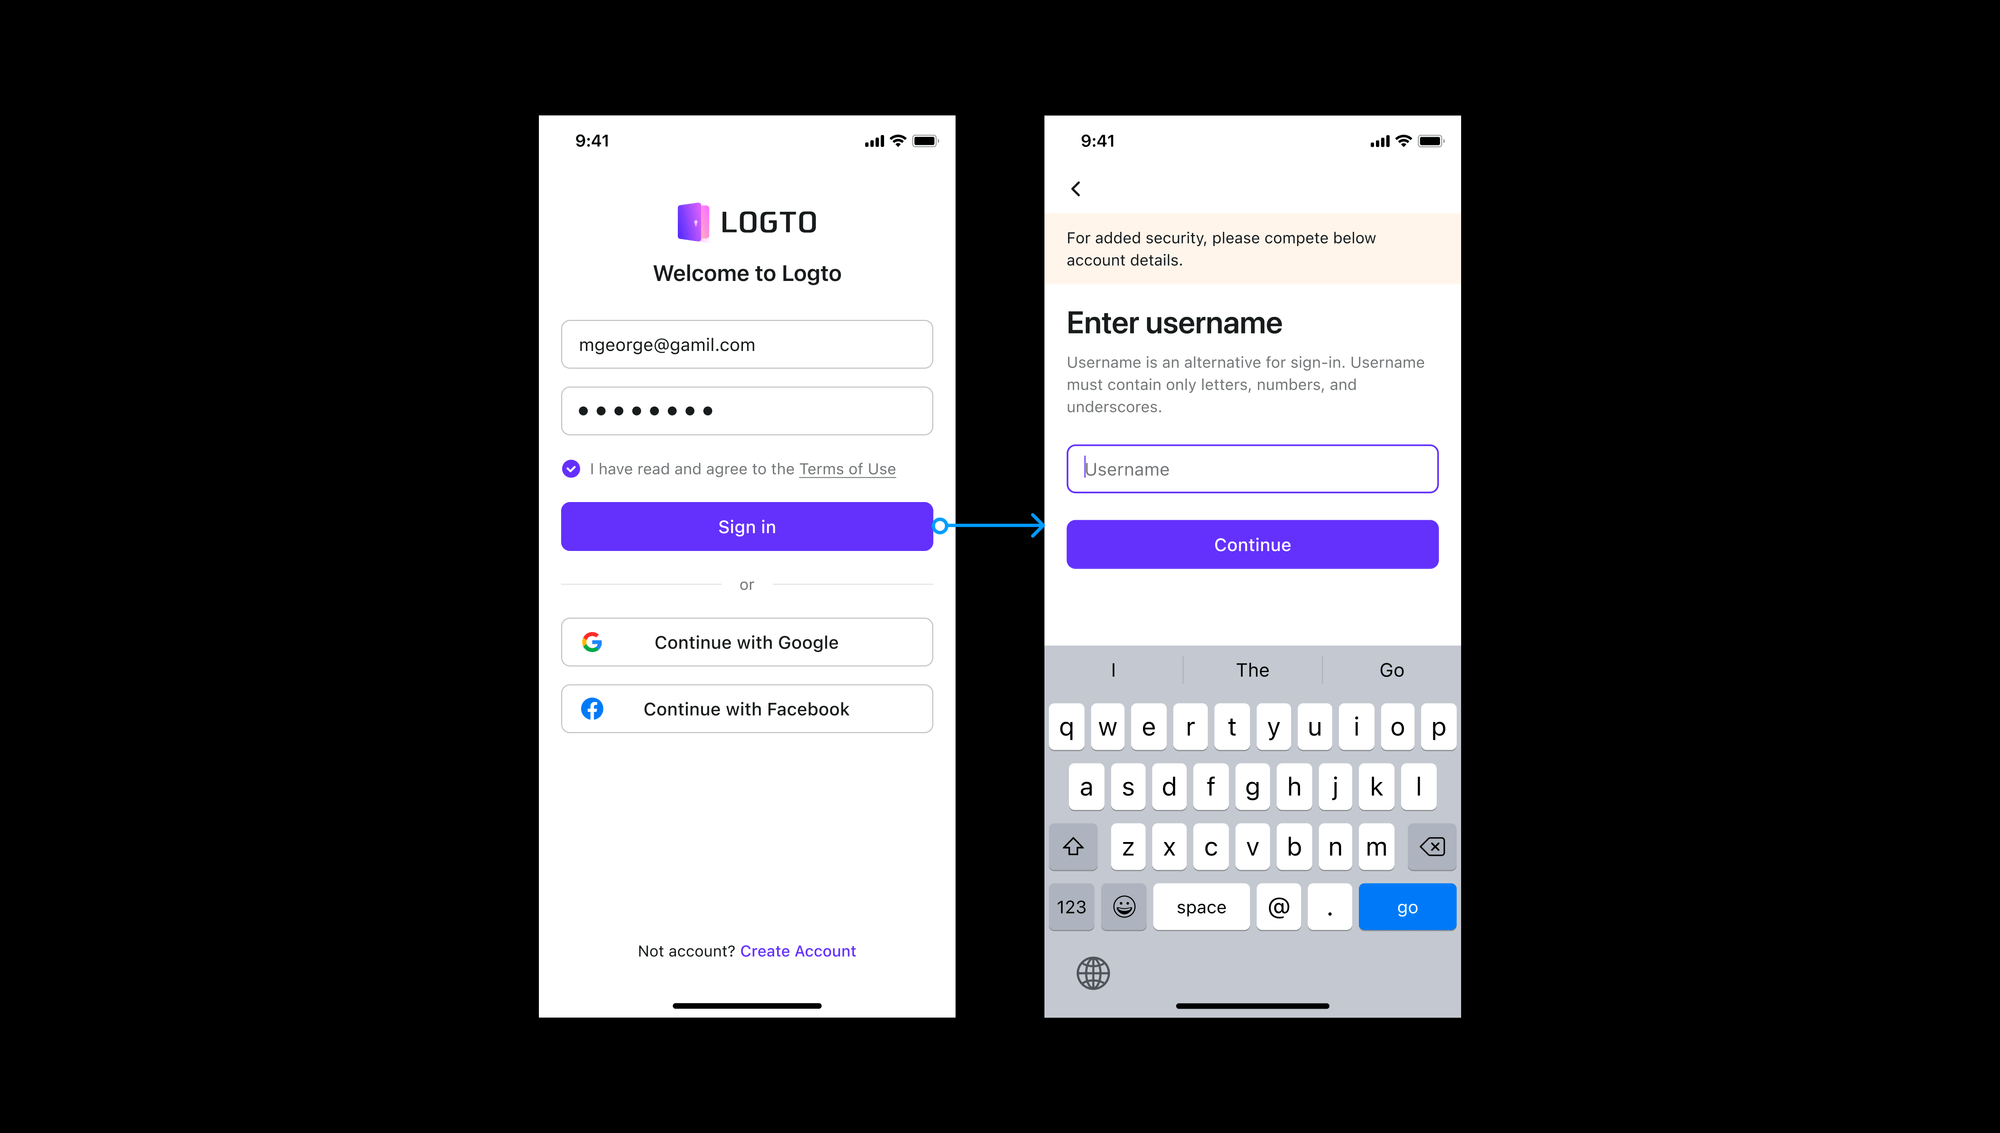
The sign in path has its own problems but they're more predictable. Brute force attempts, credential stuffing, session hijacking. These are well documented and most platforms have solutions baked in. Rate limiting. CAPTCHA challenges. Device fingerprinting. You add these and the sign in flow becomes relatively straightforward to manage. Create account is where things get weird. Social login creates a different category of issue. When someone signs up through Google or Apple, you're trusting a third party's identity assertion. That's convenient for the user and it cuts your registration friction significantly, but it also means you inherit whatever data quality problems exist in that provider's identity graph. Apple's privacy-focused sign in gives you a relay email address instead of the real one sometimes. Google might return a name that's just a first initial. Your system should handle gracefully incomplete or synthetic identity data or you'll end up with accounts that look like junk even though they're perfectly valid. There's a hidden tradeoff nobody talks about. The more friction you add to account creation, the more people will fake it. Not maliciously, just practically. If your form asks for date of birth, gender, phone number, and a custom password with special characters, a significant portion of users will fill it out with placeholder data just to keep moving. Then when you try to verify that phone number later, it fails. Now you have a verified account tied to a number that doesn't belong to them and your fraud signals are all noisy.
Get the Full Details

Conversely, if you make creation too easy with just an email, you get more fake accounts and your spam filter has to work overtime. The sweet spot depends entirely on what you're building. A casual content app can probably get away with email only. A financial product needs KYC-level verification and you accept the dropoff that comes with it. Another thing that trips people up is the concept of anonymous sessions. Before someone creates an account, they often interact with your product. They browse items, fill a cart, read articles. If you tie this activity to a device fingerprint or a session cookie, you can preserve their work when they eventually sign in. But if you're not careful about how you handle that transition, you lose data or worse, you merge two different people's activity together when they happen to share a network or a device. We had one case where a family WiFi network caused a parent's entire browsing history to get attached to their teenager's account after sign in. The recommendation engine went completely off the rails because the model started thinking a forty year old accountant was interested in teen fashion and gaming accessories. From an architecture standpoint, the cleanest approach separates identity from profile. Your identity system handles authentication. It answers the question of who is this. Your profile system handles the rest. Age, preferences, payment methods, order history. Keeping these decoupled means you can swap authentication providers without breaking the data model. You can also handle cases where someone changes their email or links multiple social accounts without creating duplicate user records.
The downside of that separation is complexity. You now have to manage cross-system lookups and keep the two in sync. A user updates their email in the identity layer and your profile layer needs to know about it. If you're using event sourcing for this, you might publish a UserEmailChanged event that your profile service subscribes to. That works well until the event fails to process and you end up with a stale profile. Again, something I dealt with directly. The fix was a reconciliation job that ran nightly comparing email addresses between the two systems and flagging mismatches for manual review. It caught about 0.3 percent of records but that 0.3 percent represented the majority of customer support tickets we were getting around login issues. Password policies are another area where teams make life harder for themselves. Requiring special characters, rotation every ninety days, minimum length restrictions. None of this meaningfully improves security according to NIST guidelines anymore, but companies still implement it because that's what they were taught. What actually matters is preventing reuse of compromised passwords. A simple check against the HaveIBeenPwned API during registration and sign in catches more real threats than any character complexity rule ever will. If you're building this from scratch, the practical order of operations is: get email verification working, add OAuth for Google and Apple, implement basic rate limiting on both flows, set up session management with proper expiration, and then worry about the fancy stuff like MFA and device trust scoring. Most products never need half the features they pile into their auth system on day one. The complexity becomes a maintenance burden and users pay for it with confusion and failed flows.
The real hidden cost of the create account path is attribution. Every signup is an opportunity to learn where the user came from, what they care about, and how likely they are to stick around. But if your tracking is broken, which it almost always is initially, you're flying blind. I recommend putting a lightweight analytics event on every step of the flow, not just the final submission. Abandonment at the password entry step tells you something different than abandonment at the email entry step. Fixing those dropoff points usually yields more revenue impact than any feature work you could ship in the same timeframe. Bottom line, sign in and create account are not interchangeable UX patterns. They serve different purposes, carry different risks, and require different levels of operational rigor. Treat them as distinct flows with distinct SLAs and you'll sleep better at night.