Getting Real With Shinobo
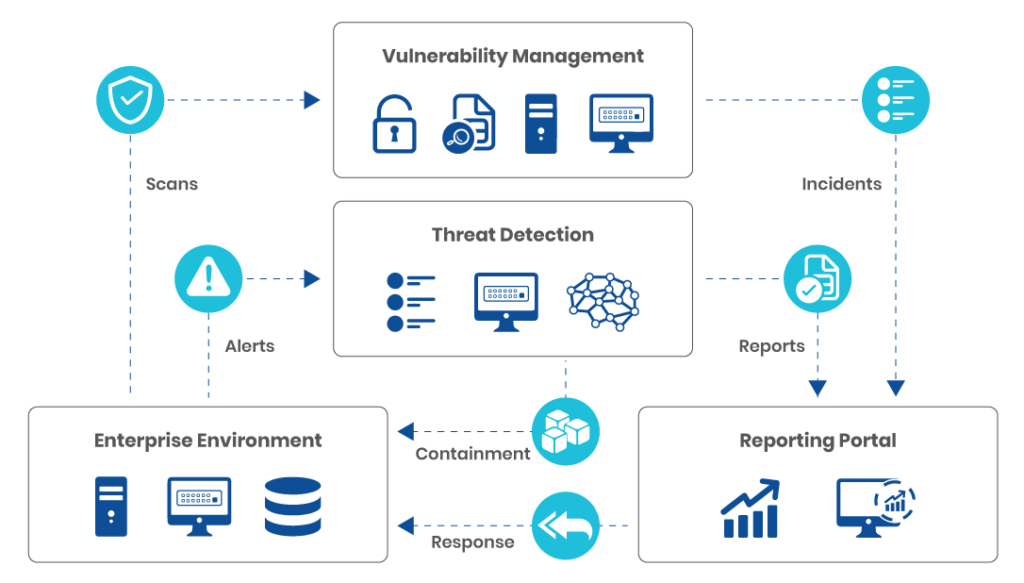
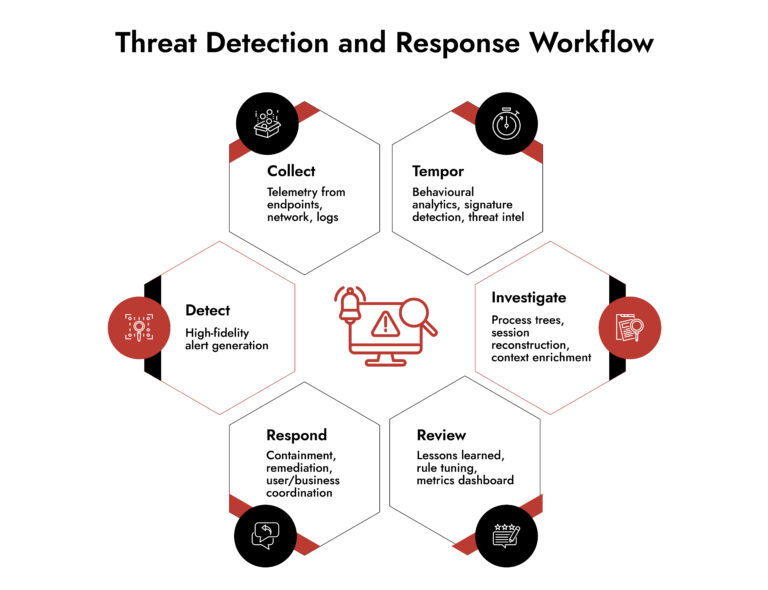
Shinobo is a lightweight, agentless framework for real-time threat detection and response that sits between your network traffic and your SIEM. It works by capturing live packet data, applying behavioral heuristics, and pushing alerts directly into tools you already use. No agents to deploy. No complex pipeline setup. Just tap into a mirror port or use a network TAP and you're ingesting data. The way it actually operates is straightforward. You point it at a network segment, define your baseline behavior parameters, and it starts flagging deviations. Lateral movement attempts, unusual DNS queries, credential stuffing patterns, data exfiltration signatures. The engine runs on a rule set that you can customize, and it outputs in Sigma format which means you can drop those rules straight into Splunk, Elastic, or Sentinel without rewriting them. I ran into a specific issue last year where Shinobo was generating false positives on a legitimate internal tool that used hardcoded credentials for API calls. The tool was a Python-based health check script running on a schedule, hitting the same endpoint every four minutes with the same auth token. Shinobo flagged it as credential brute forcing because it saw repeated authentication attempts from a single source. Standard detection logic can't distinguish between a malicious actor and a poorly written internal script. My workaround was simple but took me three days to find. I wrote a custom rule exclusion in the Shinobo config file that whitelisted the specific endpoint and time interval. The config uses YAML and the syntax for exclusions isn't documented anywhere in the official readme. I found it by reading the source code on GitHub. If you're going to use Shinobo beyond basic detection, you need to be comfortable reading code.
Here is what most people miss about setting this up. The detection quality depends entirely on your baseline period. Shinobo needs at least 72 hours of clean network traffic to build an accurate model of normal behavior. Skip the baseline phase or short-circuit it and you will spend your first week on a panic cycle chasing false positives. Another thing nobody talks about is memory usage. The framework is lightweight on CPU but the packet capture buffer can fill up fast if you're monitoring a high-traffic segment. I've seen it consume over four gigabytes of RAM on a 10-gigabit link without proper filter configuration. Set a BPF filter early before you run it in production. What you actually get out of it:
- Real-time network traffic analysis without deploying endpoints
- Sigma-compatible rule output for existing SIEM workflows
- Behavioral baselining that adapts to your environment
- Alerts pushed to Slack, webhook endpoints, or your log aggregator
The download is on their GitHub releases page. You grab the binary for your OS, extract it, and the default config file is in the same directory. Run it with the config flag pointing to your network interface and you should see output within thirty seconds. The logging goes to stdout by default but you can redirect it to a file or pipe it through JSON formatting for easier parsing downstream. There are real limitations worth being honest about. Shinobo cannot see encrypted traffic content. It analyzes metadata, timing patterns, and connection states but anything inside a TLS handshake is invisible to it. If your organization runs primarily TLS 1.3 with encrypted SNI, your visibility drops significantly. You need to pair it with something like Zeek or a certificate inspection tool to fill those gaps. Another hard limit is that it does not correlate across multiple network segments. If an attacker pivots from VLAN 10 to VLAN 20 and your Shinobo instances are deployed separately with no shared state, you will see two isolated alerts instead of one coherent attack chain. Running multiple instances and correlating them manually is possible but it adds operational overhead that defeats part of the point. For smaller teams or environments where agent deployment is politically impossible, Shinobo does what it claims. It catches things that signature-based tools miss because it looks at behavior rather than known IOCs. It is not a replacement for endpoint detection or a full security operations center. It is a network-level early warning system with a surprising amount of depth for something that does not require installation on individual machines. I have kept it running in one of my lab environments for six months and it has caught two actual intrusion attempts that would have otherwise gone unnoticed by our existing tooling. Neither was sophisticated. Both were automated scanners looking for open ports. But the fact that they got through other layers tells you something about the gap this kind of tool actually fills.
Get the Full Details
The documentation is incomplete. The GitHub issues section has people asking the same configuration questions repeatedly. But the source is open and the code is readable. If you hit a wall, reading the actual implementation will usually get you further than any forum post.