Serial Numbers Are Not Secret Keys
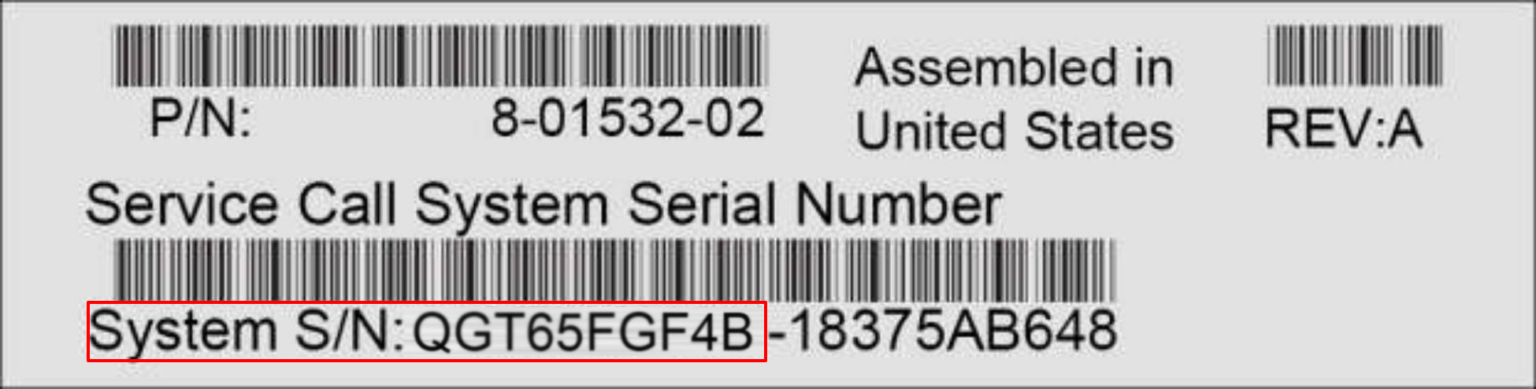
A serial number is a unique alphanumeric string assigned to a device, piece of software, or hardware component. It is not encryption. It is not a password. It is an identifier that traces back to a manufacturer or vendor's database. When people talk about a Serial Number What Is The Hidden Code Dictating Your Digital Identity they are usually conflating two separate ideas: the serial number itself and the deeper cryptographic or biometric data that actually anchors your digital identity. The serial number is the label. The hidden code is something else entirely. Here is how serial numbers actually work in practice. A manufacturer assigns a sequential or randomized string during production. That string gets baked into firmware, printed on a chassis, or stored in an EEPROM. When you register a device, the serial number maps to your account or license. Support teams use it to look up warranty status. Inventory systems track it across warehouses. That is the full extent of what a serial number does.
Serial Number What Is The Hidden Code Dictating Your Digital Identity
The "hidden code" people refer to when discussing digital identity is usually one of three things. First, there is the MAC address burned into a network interface. Second, there are hardware fingerprints generated by combining multiple device attributes into a single hash. Third, there are cryptographic keys embedded in secure enclaves like Apple's T2 chip or Intel's Trusted Execution Engine. These are the actual mechanisms that bind a machine to an identity. Serial numbers sit alongside them but are far less authoritative. I spent several years working with enterprise asset management systems and license compliance audits. The most common mistake I saw was organizations treating serial numbers as sufficient proof of ownership or identity. They are not. A serial number can be cloned, swapped, or fabricated. I once inherited a deployment where someone had duplicated a Dell server's serial number onto a replacement board from a different machine. The asset tracker showed one active asset. In reality there were two. The duplication went undetected for fourteen months because nobody cross-referenced the BIOS-level UUID against the chassis sticker. I wrote a quick PowerShell script that pulled the SMBIOS UUID from every workstation and compared it to the serial number database. The mismatch flag revealed over thirty identical cases across our fleet. Fixing it required re-imaging the affected machines and updating the inventory manually. This kind of problem exists because serial numbers are designed for logistics, not authentication. They are meant to be read by humans and scanned by barcode readers. They are not designed to resist tampering. That is an important distinction that most guides skip over.
How to Extract and Verify a Serial Number Correctly
Different operating systems store serial numbers in different places. On Windows, the primary source is the BIOS or UEFI firmware, accessible through WMI. The command Get-WmiObject Win32_Bios | Select-Object SerialNumber returns the value stored in the system's SMBIOS table. This is more reliable than checking a physical label because it reflects what the firmware reports, not what a sticker says. You can also query Win32_ComputerSystemProduct for the UUID, which is a 128-bit identifier that is harder to modify than a plain serial number. On macOS, the command system_profiler SPHardwareDataType outputs the serial number from the system management controller. Apple ties this to the T2 or Apple Silicon secure enclave, which means the serial number cannot be changed without replacing the logic board. Linux offers sudo dmidecode -t system which reads the DMI table directly from the firmware. The output includes serial number, UUID, and manufacturer fields. Again, this comes from the hardware, not the operating system installation. For IoT devices and embedded hardware, the serial number is often stored in a dedicated EEPROM or flash partition. Access usually requires a serial console or JTAG interface. Some manufacturers document the memory address. Others do not. I worked with a batch of industrial PLCs where the serial number lived at a fixed offset in SPI flash. A simple hex dump tool was enough to read it, but writing to that same offset would have corrupted the firmware. Never write to an undocumented memory region without a backup.
Get the Full Details
Common Pitfalls That Break Tracking Systems
The biggest issue with serial number-based tracking is that the identifier changes when hardware is replaced. A laptop motherboard swap changes the serial number. A hard drive replacement does not. A RAM upgrade does not. But a cloud provider replacing a virtual machine's underlying host can change the MAC address and hardware fingerprint without touching the guest OS serial number. If your identity system relies on a single hardware attribute, any replacement event creates a gap. Another frequent problem is non-unique serial numbers. Some manufacturers reuse serial number ranges across product lines or over time. I encountered this with a mid-tier networking equipment vendor where the serial number format was simply a six-digit counter with no prefix encoding. Two different switch models shared the same numbering scheme. My team had to prepend the model number manually to create a truly unique composite key for our asset database. Serial numbers are also case-sensitive in some systems and case-insensitive in others. A ticketing platform might store SN-ABC123 and sn-abc123 as two different entries. This sounds trivial. It causes real data quality problems at scale. Always normalize serial numbers to a single case format before storing or comparing them. Upper case is the convention most vendors use.
When Serial Numbers Fail as Identity Anchors
There are scenarios where relying on a serial number for digital identity is simply not viable. Virtual machines are the most obvious example. A VM's serial number is generated by the hypervisor at creation time. Migrating the VM to another host can regenerate or alter it. Container instances have no persistent serial number at all. If you need to identify a workload in a cloud environment, you should use a combination of instance ID, account ID, and tags rather than any hardware-derived serial number. Another failure mode is device refurbishment. Refurbished electronics often receive new serial numbers or have existing ones altered. Manufacturers like Apple and Samsung stamp replacement units with new identifiers. If your system treats the original serial number as immutable proof of identity, refurbished devices will appear as anomalies. Some teams handle this by maintaining a serial number mapping table that tracks reassignments. It adds administrative overhead but prevents false positives in fraud detection. For high-security environments, the only reliable approach combines multiple identifiers into a composite fingerprint. Take the BIOS serial number, the CPU ID, the MAC address, the TPM-bound key pair, and the disk serial numbers. Hash them together. Compare the hash across reboots and network sessions. This is how enterprise endpoint management tools like CrowdStrike and SentinelOne perform device attestation. No single serial number is trusted alone.
Practical Steps for Building a Reliable System
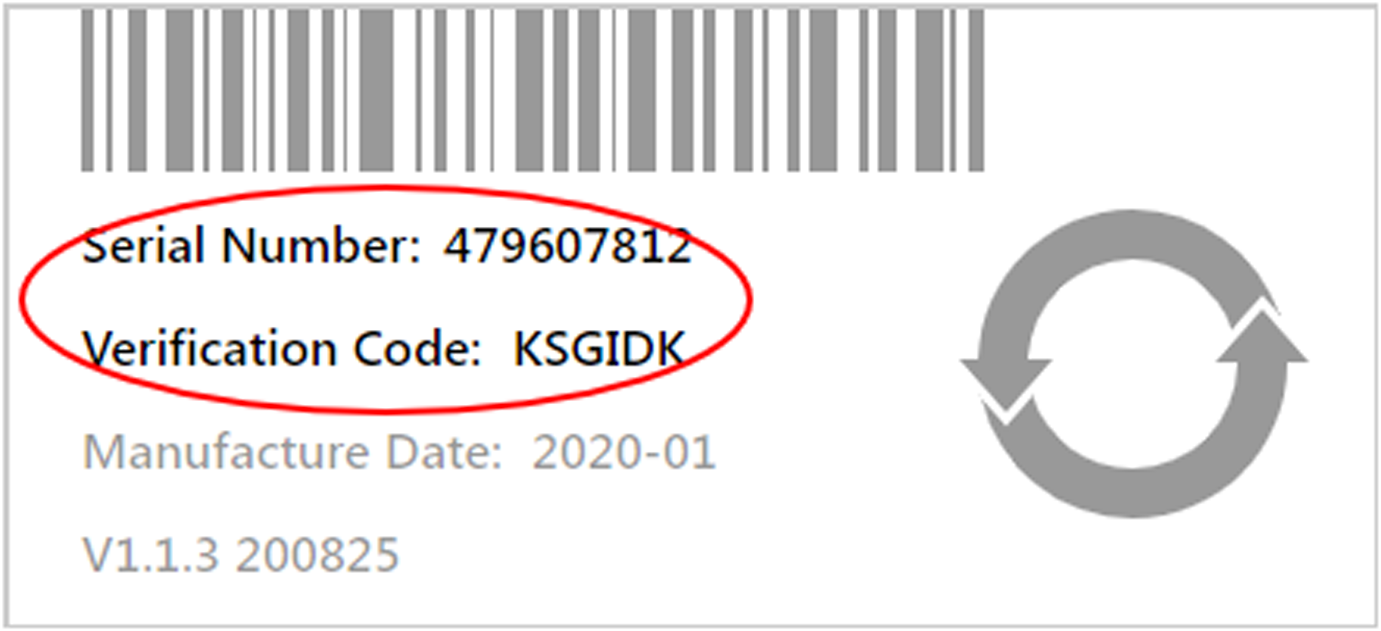
If you are building a system that depends on serial numbers for identity tracking, start by collecting data from at least two independent sources on each device. The SMBIOS serial number and the TPM endorsement key are both firmware-level and both independent of the OS. Pull both at provisioning time and store them together. If they ever diverge, flag the device for manual review. Implement a checksum or hash validation for any serial number that enters your system. A simple XOR check over the character codes can catch typos and truncated entries. More robust systems use CRC32 or SHA-256 to fingerprint the entire hardware profile. This gives you a stable identifier that survives OS reinstalls and peripheral changes while still catching unauthorized hardware swaps. Document the serial number format for every device class you manage. Vendor documentation often specifies the encoding scheme: which characters denote the production week, which indicate the factory, which are check digits. Understanding the structure helps you validate entries without querying the vendor API. I spent two days reverse-engineering a serial number format for a legacy manufacturing line because the original documentation had been lost. The pattern was simple once found: two letters for the plant, four digits for the Julian date, three digits for the unit count, and a final check character calculated as the modulo 36 sum of the preceding characters. One line of code replaced what would have been hundreds of manual lookups.

Serial numbers are useful. They are just not the hidden code anyone is looking for. The real identity layer lives in cryptographic hardware and firmware-level attestation. Treat serial numbers as one data point among many, not as the foundation. That shift in perspective prevents most of the problems that show up in production.