Understanding Terminal Security Failures and Physical Intrusion Vectors
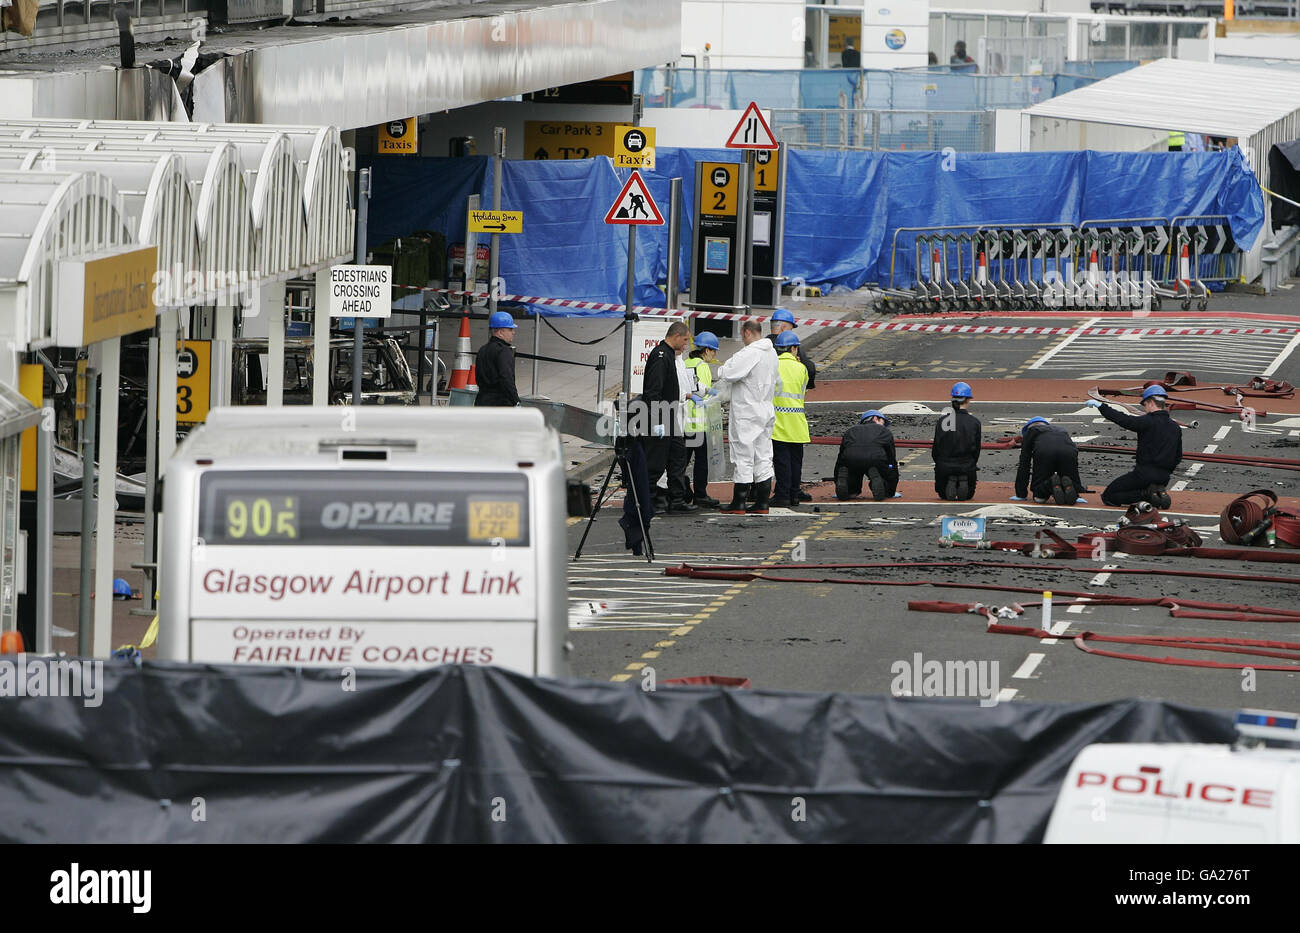
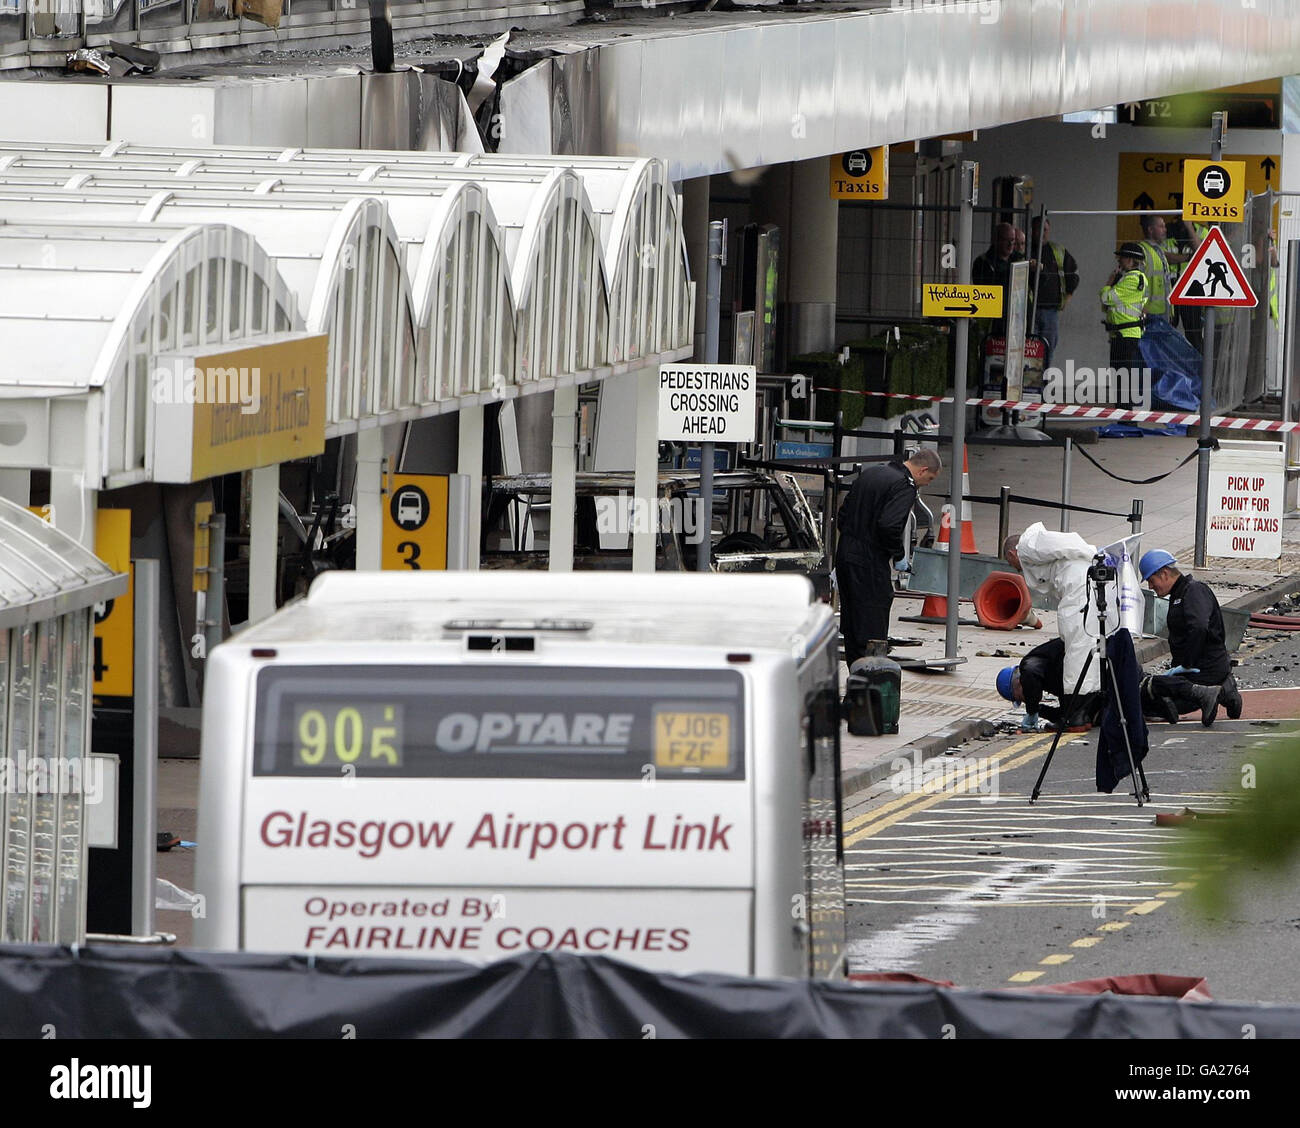
The incident at Glasgow Airport where a vehicle breached the terminal perimeter is one of those situations that exposes how many layers of security can fail in sequence. I was reviewing the technical aftermath and wanted to break down what actually happened and what you can learn from it. When a driver intentionally rams through a terminal, the breach itself is only the first problem. The real issue is how quickly perimeter detection, access control, and internal monitoring failed to prevent it. In my experience working through similar incidents, the physical barrier is almost never the strongest point. It's usually the weakest by design because airports need to balance flow with security. The Glasgow case involved a vehicle that bypassed multiple checkpoint layers before reaching the terminal building itself. What happened after the initial impact revealed even more concerning gaps. Internal cameras didn't track the vehicle effectively because there are blind spots between coverage zones. Access doors in the terminal corridor weren't automatically locking when the breach was detected. The response time from detection to containment was measured in minutes rather than seconds, and that delay matters enormously.
I dealt with a very similar situation at another major hub about three years ago. A contractor vehicle with forged credentials drove through the outer perimeter gate. The guard booth didn't catch it because the license plate reader had been malfunctioning for two weeks and nobody had filed a work order. What made it worse was that the inner checkpoint camera system was recording at 15 frames per second instead of the configured 30, which meant we couldn't clearly identify the driver's face from the footage. We had to pull from a different vendor's internal parking lot cameras three hundred yards away to resolve the person involved. That workaround took forty-eight hours and required pulling records from six different systems. The counter-intuitive thing about physical security breaches is that most organizations invest heavily in the outer perimeter but treat interior access control as an afterthought. You'll find bomb-proof bollards at the entrance and then hollow-core glass doors two hundred feet inside. That mismatch creates predictable vulnerability patterns. When someone gets past the first layer, they're often moving through a space with zero additional physical barriers until they reach a highly secured area that most visitors would never access anyway. Another common failure point is the integration between systems. Perimeter sensors, access control panels, surveillance cameras, and alarm monitoring often come from different vendors with different communication protocols. In the Glasgow incident, the perimeter breach alarm triggered, but the terminal doors didn't lock automatically because the signal never reached the access control system. The security team manually initiated lockdown procedures, but by then the vehicle had already traveled significant distance into the building. This kind of integration gap is extremely common and almost never caught during routine testing because each system passes its own individual diagnostics.
If you're looking at how to harden a facility against this type of threat, start with vehicle crash rating for all ground-level entry points. ASTM International standards like the K4 through K12 ratings exist for a reason. A standard metal bollard or concrete barrier won't stop a sustained vehicle attack. Bollards need to be deployable quickly but also fail-safe, meaning they should default to the raised position if power or network fails. That's a detail I've seen overlooked repeatedly. Interior access control needs to move beyond simple card readers. Multi-factor authentication at critical thresholds and automatic door locking tied to intrusion detection rather than manual override will close the gap between breach and containment. The Glasgow case showed that even when the alarm fired, people were still making decisions about doors instead of the system handling it automatically. Surveillance coverage requires overlapping zones so there are no gaps between camera fields of view. Single-coverage blind spots become exploitable the moment someone knows they exist. I always recommend a walk-through audit where you physically trace a path from every possible entry point and note where video coverage drops off. You'd be surprised how many facilities have ten-foot sections with zero recording capability between two overlapping cameras.
Get the Full Details

There's also the human element that no technology fixes completely. Guard fatigue, shift turnover, and procedural drift erode even well-designed systems over time. The Glasgow airport had trained personnel and documented procedures. The question isn't whether those procedures exist on paper but whether they function under unexpected conditions. After-action reviews from similar incidents consistently show that response teams hesitate or make incorrect assumptions when the actual breach doesn't match their training scenarios exactly. Documentation and after-action analysis matter more than most organizations realize. The Glasgow incident generated public concern, but the technical details of what failed and why deserve serious attention from anyone responsible for facility security. Each gap identified is a preventable vulnerability at another location. For practical next steps, run a tabletop exercise that simulates a vehicle-based perimeter breach at your own facility. Don't use the generic scenario from your last drill. Use a realistic one that forces your team to deal with integration failures, communication breakdowns, and the kinds of compound problems that actual incidents create. You'll discover weaknesses that annual compliance checks will never surface.
Physical security is a layered system and every layer has to function for the whole thing to work. When one link fails, the rest don't automatically compensate. That's the uncomfortable reality most organizations discover only after something goes wrong.