Setting Up Azure Key Vault Access From Python
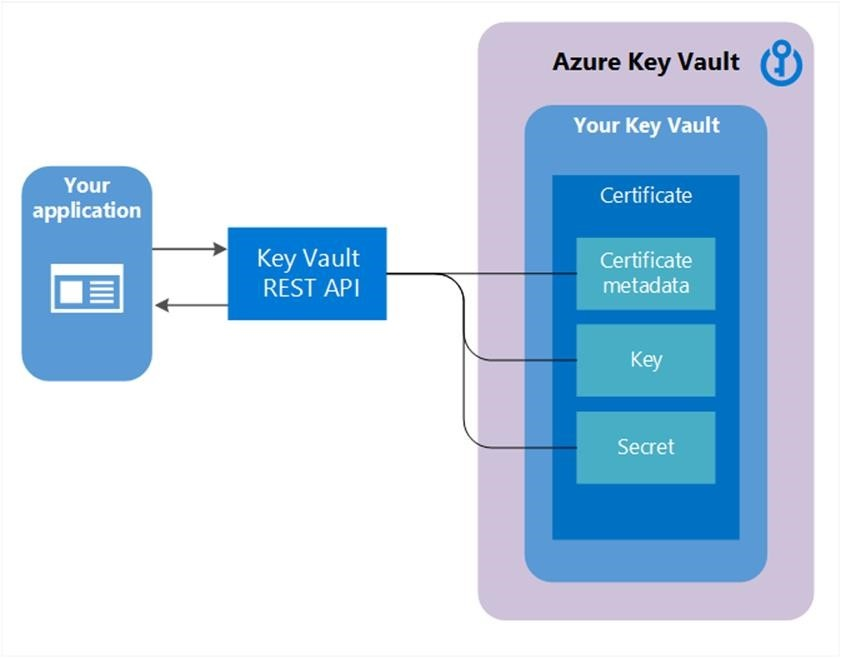
I spent two days last month debugging why our staging pipeline couldn't read secrets from Key Vault. The error message was cryptic, the authentication flow was partially documented, and the actual issue turned out to be something nobody mentioned in the official guides. I am going to walk you through how to do this properly, including the things that actually trip people up. Before writing any code, you need to understand what you are working with. Azure Key Vault is essentially a secure storage layer for secrets, keys, and certificates. It does not replace environment variables in every scenario, but it is the right tool when you need centralized secret management across multiple services. The azure-keyvault-secrets package from Microsoft is the standard way to interact with it from Python. It is not the only option, but it is the most maintained and the one I would recommend unless you have a specific reason to avoid it.
Secure Your Cloud Code Master Azure Key Vault With Python For Modern Developers
The basic flow is straightforward: authenticate, create a KeyVaultClient or SecretClient, and retrieve your secrets. But the authentication piece is where most people hit problems. There are three main ways to authenticate your Python application against Key Vault, and each has tradeoffs that matter more than Microsoft's documentation lets on. Method one: Managed Identity. If your Python application is running on Azure App Service, Azure Functions, or an Azure Container Instance, you can use Managed Identity. This is the cleanest approach because there are no credentials to store anywhere. You enable the managed identity on your resource, assign it the Key Vault Secrets User role in the vault's access policy, and then use the DefaultAzureCredential class. It picks up the managed identity automatically. In practice, this works perfectly about 90 percent of the time. The remaining 10 percent is when your local development environment conflicts with the production setup, or when the managed identity hasn't propagated yet after creation. Method two: Service Principal. This is the most common approach for CI/CD pipelines and local development. You create an Azure AD application, generate a client secret, and use those credentials in your code. The ClientSecretCredential class handles this. You will store the tenant ID, client ID, and client secret somewhere secure. I use GitHub Secrets for CI/CD and a .env file for local work, though anyone using a .env file in source control should feel the shame that comes with that decision.
Method three: Interactive browser login. The InteractiveBrowserCredential class opens a browser window and lets you log in interactively. This is fine for quick scripts and one-off tasks, but it is useless in any automated context. Do not attempt to use this in a production pipeline. It will hang and timeout. Here is what a minimal working setup looks like using a service principal: First, install the required packages:
Get the Full Details

pip install azure-keyvault-secrets azure-identity Then your code:
from azure.keyvault.secrets import SecretClient
from azure.identity import ClientSecretCredential

tenant_id = "your-tenant-id"
client_id = "your-client-id"
client_secret = "your-client-secret"
vault_url = "https://your-vault-name.vault.azure.net/"

credential = ClientSecretCredential(
    tenant_id=tenant_id,
    client_id=client_id,
    client_secret=client_secret
)

client = SecretClient(vault_url=vault_url, credential=credential)

secret = client.get_secret("my-secret-name")
print(secret.value)
That code will retrieve a secret from Key Vault. It is that simple in isolation. The complexity comes from everything around it. One thing that the documentation does not emphasize enough is secret versioning. When you update a secret in Key Vault, it does not overwrite the previous version. It creates a new version and keeps the old one. This is a security feature, but it means your get_secret calls need to account for this if you are ever doing version-specific lookups. By default, get_secret returns the latest version, which is what you want 99 percent of the time. But if you ever need to audit or roll back, you can call get_secret_version with a specific version ID. Here is the edge case I ran into that cost me two days. Our application was reading secrets from Key Vault in a Kubernetes cluster using a service principal stored as a Kubernetes secret. Everything worked in staging. In production, the application started failing with authentication errors that made no sense. The credentials were correct, the vault URL was correct, the role assignment was in place. The problem was that the service principal had been created in a different Azure AD tenant than the Key Vault resource. Azure allows cross-tenant access, but you have to explicitly configure it. The error message did not mention this at all. It just said authentication failed. The workaround was to either create the service principal in the same tenant as the vault, or configure the necessary cross-tenant permissions in both directories. I went with the first option because it was faster and less risky.
Another thing nobody tells you about rate limiting. Key Vault has soft limits on requests per second per vault. For most applications this is not a concern. But if you are deploying to multiple environments that all hit the same vault simultaneously, or if you are reading secrets in a tight loop during startup, you can hit those limits. The result is a 429 error with no obvious indication that rate limiting is the cause. The fix is simple: add a retry mechanism with exponential backoff. The azure-identity library includes built-in retry logic, but the azure-keyvault-secrets package does not handle retries by default. You need to wrap your calls or configure a custom policy. I use a simple decorator with ten retries and exponential backoff starting at one second. It handles everything cleanly. For caching secrets in your application, I would strongly recommend against calling Key Vault on every request. It adds latency and burns through your quota. A reasonable approach is to cache secrets in memory with a short TTL, maybe five to ten minutes. The secrets don't change that often, and if they do, a short cache window means you won't be using stale values for long. Just make sure your cache invalidation strategy is solid, or you will spend time debugging why a changed secret isn't being picked up. Encryption at rest and in transit is handled by Azure automatically. You don't need to do anything special for that. If you need customer-managed keys for additional control, you can configure that in the Key Vault settings, but it adds operational complexity that most teams don't need. Use Azure-managed keys unless you have a compliance requirement that demands otherwise.

There are scenarios where Key Vault is the wrong tool. If you are running a small personal project with a single environment and a handful of secrets, storing them in environment variables or a configuration file with proper access controls might be simpler and cheaper. Key Vault has a per-operation cost structure that adds up if you are making thousands of secret retrievals per minute. For high-throughput applications, the cost and latency implications are real. In those cases, consider using a dedicated secrets manager like HashiCorp Vault or moving the secrets closer to the application layer with runtime injection. Testing your Key Vault integration locally is another pain point that deserves attention. The easiest path is to use the Azure CLI with az login and let DefaultAzureCredential pick up your credentials. This mirrors production behavior closely. Some people set up a local Key Vault emulator, but it is not well maintained and doesn't cover all features. I found that using a separate local-only vault for development and staging separate vaults from production was the most practical approach. It prevents accidental access to production secrets and makes it clear which environment you are working in. The most important thing to remember is that Key Vault is not a configuration store. It is a secrets store. If you need to manage application settings, feature flags, or configuration that changes frequently, use Azure App Configuration instead. Trying to use Key Vault for general configuration management leads to architectural confusion and unnecessary costs. Keep the separation clear in your head and in your codebase.
Authentication failures are the most common error you will encounter, and they are almost always caused by one of three things: incorrect credentials, missing role assignments, or network restrictions on the vault. Check the access policies first. Then verify the credential. Then look at network rules. In my experience, about 80 percent of auth issues are resolved by checking whether the service principal actually has the Secrets User role assigned in the vault's IAM settings. It sounds obvious, but it is surprisingly easy to miss when you have multiple vaults and multiple principals. Secret rotation is another topic that deserves more attention. Key Vault supports automatic rotation for some key types, but not for arbitrary secrets. For secrets, you need to implement rotation yourself, typically by updating the secret value periodically and ensuring all consuming applications are updated to read the latest version. I have seen teams use Azure Functions triggered by a schedule to rotate secrets and notify downstream services. It is not elegant, but it works. There is no built-in secret rotation mechanism in Key Vault, and that gap causes problems for teams that treat rotation as a security best practice without realizing the additional work it requires. Monitoring and logging are essential but often overlooked. Enable diagnostic logging on your Key Vault to track secret access, failed authentication attempts, and quota usage. The logs go to Log Analytics or Event Hubs depending on your configuration. Without logging, you are flying blind when something goes wrong. The default retention period is short, so configure it appropriately if you need audit trails for compliance purposes.
Using Python with Azure Key Vault is not complicated, but it is not trivial either. The gaps between documentation and reality are where the real work happens. Understanding authentication flows, handling rate limits, managing secret versions, and knowing when to reach for an alternative tool are the skills that separate a working implementation from a production-ready one. Start simple, test thoroughly in a non-production environment, and build up from there. The two days I lost to a cross-tenant authentication issue would have been twenty minutes if I had known about it beforehand.