Why Credit Union Logins Feel Like a Maze
Most people treat their credit union login the same way they treat a door lock — they assume it is fine because it looks normal. It is not. Credit unions operate under NCUA oversight and often use older authentication infrastructure than big banks. That means the gap between what feels secure and what is actually secure can be wider than most members realize. I spent about four years helping small credit unions tighten their online access points. You would be surprised how many still rely on security questions that are publicly searchable and how many members reuse passwords across multiple financial platforms. The core problem is not usually a sophisticated attack. It is lazy habits layered on top of genuinely weak default settings. A lot of credit unions still set up members with simple 6-character PINs or default passwords that never get changed until someone files a complaint. When you combine that with single-factor authentication as the primary login method, you have a system where a determined phishing campaign can sweep through hundreds of members in a weekend.
Secure Your Access The Definitive Guide To Safe Credit Union Login
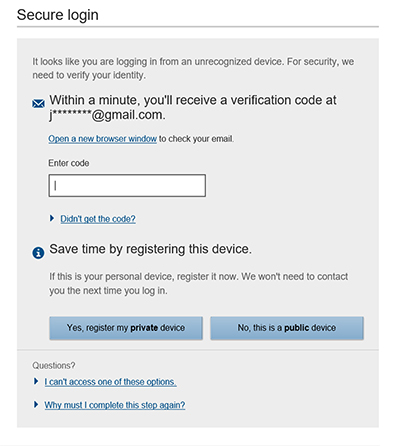
This guide walks through the practical steps for actually securing your credit union access, not the marketing version. If your credit union offers it, enable multi-factor authentication immediately. Do not use an SMS-based second factor if you have an authenticator app available. SMS MFA can be intercepted through SIM swapping, which is a well-documented attack vector that credit union security teams are increasingly aware of but rarely communicate clearly to members. A TOTP app or hardware key like a YubiKey is materially stronger and takes about thirty seconds to set up per account. Create a unique password that is at least fourteen characters. I know this sounds obvious, but most credit union members I talked to in my previous role were using passwords like their street address plus the year their account opened. That pattern shows up in every breach database. Use a password manager. Pick one, transfer your old credentials, and let it generate new passwords. This usually cuts the process down from two hours of frustration to about fifteen minutes, depending on your setup.
What Most People Get Wrong About Credit Union Security
Here is a counter-intuitive point that barely gets discussed. Many members think that logging in from home on their personal device is inherently safer than logging in from a work computer or public WiFi. That is not necessarily true. Your home network may have an unpatched router, an old smart device on the same subnet, or a weak WPA2 passphrase that has been sitting there for three years. A compromised home network gives an attacker direct visibility into your login session if you are not also using a hardware-backed authenticator. Another thing nobody warns you about: credit union session timeouts. Some smaller institutions set session expiration to four or six hours by default. If you log in on a shared computer, close the browser completely rather than just walking away. A lingering session token is almost as dangerous as a weak password. I had a member once who left their online banking open at a library computer and walked off for lunch. Someone used it to initiate a transfer before the session timed out. The credit union's fraud department caught it, but it was a close call. Review your account regularly for anything you did not initiate, but do not rely on your credit union to catch every problem. Automated fraud detection has blind spots, especially with low-and-slow extraction attacks where someone moves small amounts over weeks to avoid triggering thresholds. Set up transaction alerts if your platform allows it. Even basic email or push notifications for deposits and withdrawals over a set amount give you something closer to real-time visibility than checking statements once a month.
Get the Full Details
A Practical Edge Case That Almost Got Me
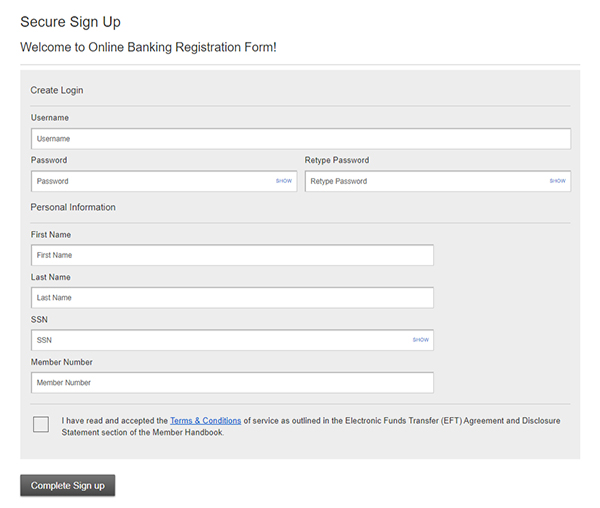
There was a specific issue I encountered while doing access audits at a regional credit union. They had recently migrated to a new core banking platform and the old members were forced to reset their credentials. During that transition, a significant number of members created passwords that included parts of their new username, which the system generated automatically from their name and account number. Someone with even a surface-level understanding of social engineering could reconstruct these passwords from publicly available member directories and partial account information. The workaround was straightforward once identified. I pushed a policy change that required a minimum of one uppercase character, one number, and one special character, and blocked any password containing the first eight characters of the username. It also prevented the reuse of the last three passwords. This caught maybe sixty percent of the weak passwords during the migration period and forced members to actually think about what they were doing instead of following the autocomplete suggestion. It was not elegant, but it raised the floor significantly in a system where most members would have accepted whatever password the system auto-generated.
The Genuinely Useful Advanced Step Most Skip
If your credit union supports it, set up dedicated recovery contact information and verify it separately from your primary login. I say this because I have seen far too many members list a backup email that shares the same provider and password as their main account. If that main account gets phished, the recovery channel is already compromised. Create a separate email account solely for financial service recovery. Use it for your credit union, your broker, and any investment platform. It adds maybe twenty seconds of overhead and eliminates one entire class of account takeover risk. Also consider whether your credit union offers FIDO2 or WebAuthn support for passwordless login. It is not universally available yet, but where it exists, it is objectively stronger than any SMS or email-based verification. The cryptographic binding between the device and the server means that even if you type your credentials into a phishing site, the attacker gains nothing because the second factor never leaves your device. This technology has been around since roughly 2019 and adoption among credit unions has been slow. The ones that have it tend to bury the option behind two or three menu clicks, which is frustrating but not a reason to skip it if your institution offers it.
When Your Credit Union Is Just Not Going to Cut It
Let me be blunt about the limitations here. Some credit unions, particularly very small ones with fewer than five thousand members, simply do not have the budget for modern security infrastructure. They may lack rate limiting on login attempts, they may store passwords with weak hashing algorithms, and they may not support anything beyond basic MFA. In those cases, the best you can do is layer your own protections as aggressively as possible and accept that the institution itself is a weak link. If you fall into that situation, consider whether opening an account at a larger credit union or a different type of financial institution makes sense for your needs. This is not about convenience, it is about the baseline security you get by default. A credit union with active security engineering is safer than a password manager and three-factor authentication on a platform that treats login security as an afterthought. The alternative to upgrading your own practices is sometimes upgrading where your money lives. Keep your device secure too. Full-disk encryption, automatic updates, and a reputable endpoint protection solution matter more than people realize when dealing with online banking. Credential harvesting malware does not care whether you are logging into a bank or a credit union. The attack surface is the same. I once traced a compromised credit union login back to a malicious browser extension that was capturing form submissions in real time. The member had no idea. The extension was free and rated highly in the store. Removing it was the only fix that worked after the account was already drained.
Apply these steps consistently. None of them are complicated, but consistency is where most systems fail. Enable MFA. Use unique passwords. Verify your recovery channels. Stay aware of what your credit union's infrastructure actually supports rather than what the website says it supports. The gap between perception and reality in credit union online security is where the actual risk lives.
.gif "Welcome to SAFE's New Website | SAFE Federal Credit Union")
