Building a Payment Flow That Doesn't Make People Close Your Tab
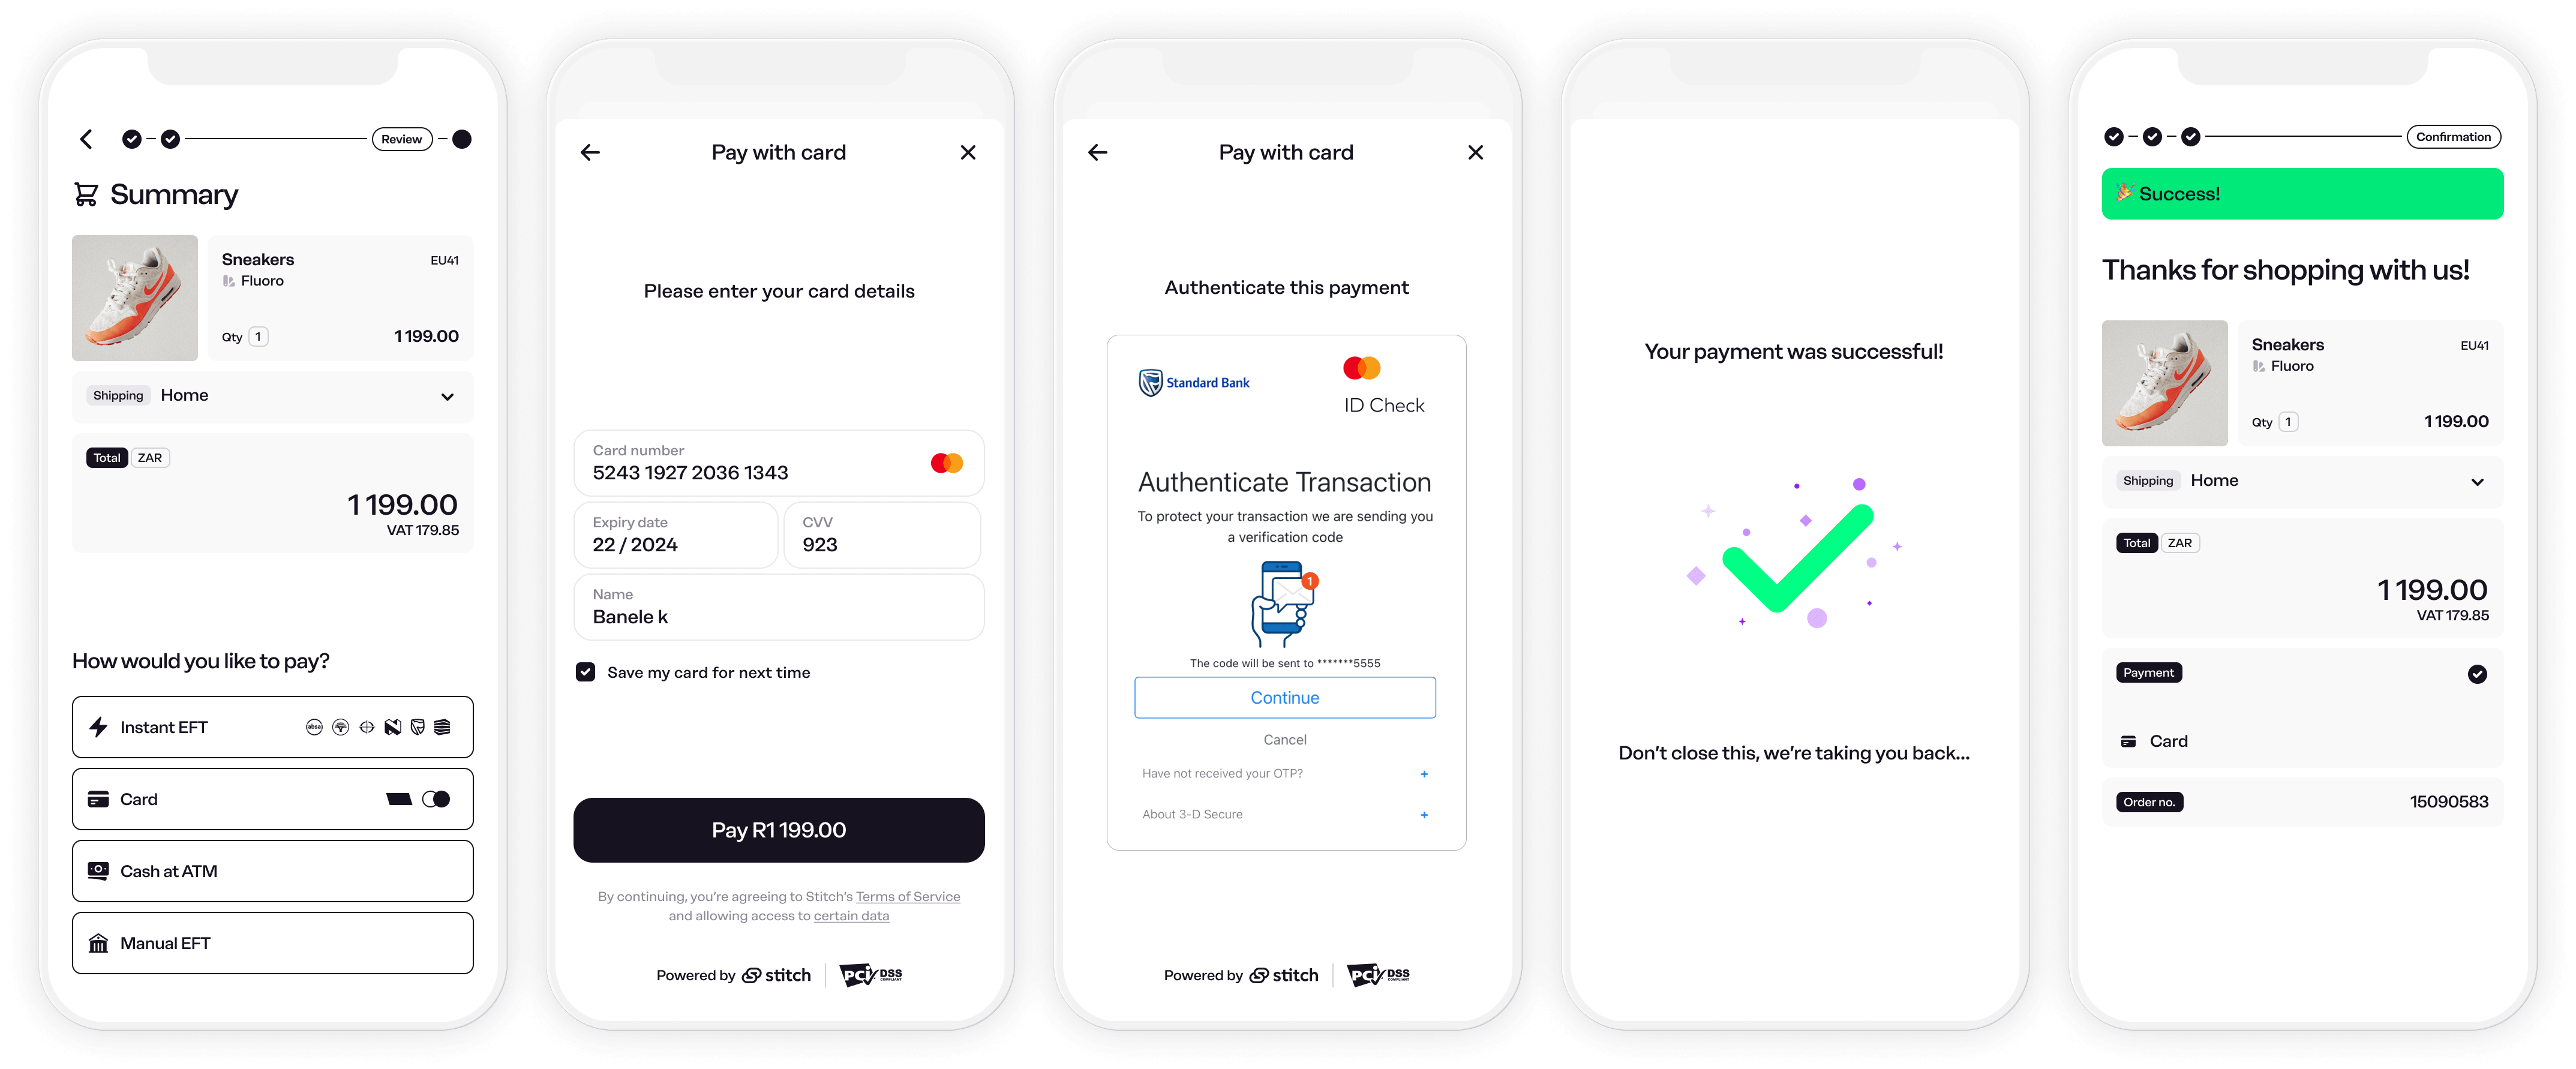
I spent three weeks debugging a checkout page where cards were being declined at random. The error codes pointed to the payment gateway, but the real issue was in how we formatted the request. Turns out some issuers reject requests that don't include the proper merchant category code alongside the billing address validation. I learned that the hard way when a client lost about two percent of their transactions on a Tuesday afternoon. The fix was straightforward once I stopped chasing the gateway logs and looked at what we were actually sending. Most people building these flows don't account for the fact that different card networks have different expectations about field ordering and currency formatting.The actual work of integrating credit card payments involves more than just pasting a Stripe or PayPal SDK into your checkout page. You need to handle tokenization properly, manage 3D Secure challenges without losing the user, and understand what happens when a card expires mid-purchase. The best implementations I've seen treat payment collection as a second-class citizen and then wonder why conversion drops off. A well-built checkout flow should take under thirty seconds from card entry to confirmation, assuming the card isn't flagged for fraud review. That window shrinks further if you're not collecting unnecessary address lines. The terminology in this space gets padded with marketing language, but the mechanics are pretty grounded. What people mean when they talk about frictionless checkout is really about reducing the number of form fields, pre-filling known data through saved payment methods, and handling declines gracefully before the user even sees an error page. The contactless payment wave has accelerated expectations. Users now expect to tap their phone, enter a code, or use biometric verification and be done. Anything slower feels broken by comparison. I built a system once where we tried to optimize for speed by skipping postal code validation. Conversion went up three percent on mobile, but chargebacks jumped by twelve percent over the next quarter. The postal code wasn't the fraud vector. It was the CVV mismatch rate that mattered. Issuers are getting stricter about requiring all three authentication factors for cross-border transactions. If your checkout flow can't present the CVV prompt cleanly, you'll lose customers to competitors who handle it better, even if your prices are identical.
Tokenization And The Fields That Actually Matter
Here's what most developers miss about card tokenization. The token itself is worthless without the proper vault mapping. When you call a payment gateway's create token endpoint, you get back a reference string that links to the card data stored in their PCI-compliant vault. The token is what you send to your server, not the card number. Simple enough. But the edge case comes when you need to do recurring billing or update the card details after the first charge. I ran into this with a subscription service. The initial signup went fine. The first monthly charge went fine. Then the user updated their card through the provider's customer portal. Our system kept trying to charge the old token and got declining responses. The workaround was setting up a webhook to listen for card updates and refreshing the token reference on our end. Most tutorials skip this part because it doesn't happen in happy-path demos. It happens to everyone who runs a business for longer than six months. The fields you should collect during checkout are minimal. Card number, expiry, CVV, and billing zip code if you're doing AVS checks. Name is optional if the card has it on file. Email is for receipt purposes but shouldn't block payment. Anything else is friction you're imposing on your own customers. Address line two, phone number, company name. Collect all that and watch your cart abandonment climb. The data has to be legitimate to be useful. Fake or abandoned addresses don't prevent fraud. They just annoy legitimate buyers.
Handling 3D Secure Without Losing Sales
3D Secure is the authentication step where cards get verified through the issuer. Version 2.x added the possibility of frictionless flow when the risk score is low. The problem is that some issuers still force the challenge flow even when the transaction looks safe. I've seen checkout pages spin for forty seconds while the user waits for a push notification they never receive because their banking app is logged out on another device. The practical fix is to implement asynchronous authentication. Instead of blocking the checkout page while the 3DS challenge completes, you can redirect the user to a verification page or show a pending state. Once the issuer responds, your backend processes the final charge. This approach usually cuts the perceived wait time in half. Users don't notice that the actual cryptographic exchange is happening in the background. Another thing people don't tell you about 3D Secure is that it changes your liability. With the authentication in place, the fraud liability shifts from you to the issuer. That matters more for high-ticket items or digital goods where chargebacks hurt. The trade-off is the drop-off rate during the challenge. Plan for a five to eight percent decline in completion when you enable strict 3DS policies. Some of those are fraudulent attempts you're catching. Some are legitimate customers who gave up waiting. The balance depends on your average order value and your tolerance for chargeback risk.
Get the Full Details
The Decline Code That Actually Means Something
Payment declines come with error codes. Most of them are useless for determining what went wrong. Declined means declined. The helpful codes are the ones that tell you whether to ask for a different card or whether the user should call their bank. I keep a reference sheet for the common ones. Insufficient funds means exactly that. Do not retry the same card five times. Each retry is a decline and might trigger a fraud flag. Do offer to save the attempt and let the user add a different payment method. Card expired means the user needs to update their card in their account settings. This is recoverable if you catch it early and prompt them before the next billing cycle. Issuer unavailable means the bank's systems are down. Nothing you can do. Retry in an hour or offer an alternative payment method. The code that surprises people is the one that says the transaction requires additional authentication. This usually means the issuer's fraud system flagged the purchase. The user might need to call their bank or approve it through their app. There's no API response for this. You show a message asking the user to verify with their bank and give them a link to your support page. I've seen some checkout flows treat this the same as a generic decline and just show an error. That loses the customer for no reason.
What Happens When The Gateway Goes Down
I learned about gateway reliability the hard way. We had a flash sale scheduled. Traffic spiked to four times the normal rate. The payment gateway started returning timeout errors. Our checkout page showed a spinner and then an error message that didn't explain what was happening. Sales dropped to zero for twenty minutes while we figured out whether it was us or the provider. The solution is to implement a fallback strategy. Maintain a second payment gateway account with a different provider. Route traffic to the backup when the primary returns errors above a certain threshold. The routing decision should be automatic, not manual. I've seen teams waste hours diagnosing a problem that a simple failover would have resolved in seconds. There's also the question of idempotency. When a gateway times out, you don't know whether the charge went through. Charging the card again creates a duplicate transaction. Proper idempotency keys prevent this. Generate a unique key for each payment attempt and send it with every request. The gateway will return the original result instead of processing a new charge. This is standard practice for any system handling real money. The documentation always mentions it. The implementations rarely get it right.
Mobile Checkout And The Finger Problem
Inputs are harder to fill on mobile. The number pad that appears for card entry is usually adequate. The problem is the layout. Narrow screens force awkward scrolling. Users miss fields or submit incomplete forms by accident. I've measured conversion rates on mobile versus desktop for the same checkout page. Mobile conversion is typically thirty percent lower. Some of that is network latency. Most of it is the friction of entering card details on a small screen. The fix involves optimizing the form layout for touch. Make inputs tall enough for finger taps. Use appropriate input types so the right keyboard appears. Card number should trigger the numeric keypad. Expiry should use a date picker. CVV is three digits. Billing address can be auto-populated if the user has stored addresses in their browser or payment app. Apple Pay and Google Pay handle most of this automatically. Offering them as options usually improves mobile conversion by ten to fifteen percent. There's also the question of autofill. Modern browsers and operating systems can fill card details from saved payment information. This works best when you structure your form fields according to the HTML autofill specification. The attribute values tell the browser which field expects which data. Without them, autofill falls back to pattern matching and often fills the wrong field. I spend time checking that my form markup matches the standard. It's boring work. It pays for itself in reduced support tickets.

Chargebacks Are A Feature Of The Business
Every merchant accepts that some portion of revenue will come back as chargebacks. The rate varies by industry. Digital goods tend to have higher dispute rates because there's no physical delivery to confirm. The question is how you handle them. Most platforms provide a dashboard for responding to disputes. The response window is short. Missing it means automatic loss of the dispute and the funds. I've seen teams panic when chargebacks spike. The first reaction is to tighten fraud detection and block more transactions. This reduces chargebacks but also reduces sales. The better approach is to analyze the patterns. Are the disputes coming from a specific region? A specific card type? A specific product? The data tells you whether the problem is fraud or customer confusion. Sometimes the fix is clearer refund policies or better order confirmation emails. Sometimes it's actually fraud and you need stronger authentication. The chargeback rate that triggers alerts from payment processors is usually one percent of transactions. Above that and you might get flagged for enhanced monitoring or even account termination. I keep the rate below half a percent by addressing disputes quickly and providing clear evidence of delivery or service completion. The evidence needs to be timestamped and verifiable. Screenshots don't cut it. Server logs with IP addresses and user agents do.
Testing Without Spending Real Money
Payment integration requires testing. The testing cards provided by gateway documentation let you simulate different scenarios. Card number 4242 4242 4242 4242 usually approves. 4000 0000 0000 0002 declines for insufficient funds. 4000 0000 0000 9995 declines for lost card. These are standardized across most providers. The problem is that testing only covers your own integration. It doesn't tell you whether the user's bank will accept the transaction. I run tests in a staging environment that mirrors production. The staging gateway account uses sandbox credentials. Transactions don't move real money. The responses are identical to production. This is where I validate error handling, retry logic, and the fallback routing. After staging passes, I run a small set of live transactions using low-value amounts. One dollar tests cover the full authentication flow. I reverse them immediately after confirming they process correctly. This catches integration issues that only appear with real cards. The mistake most teams make is skipping the live test phase. The sandbox environment is too clean. It doesn't exercise the same fraud detection systems or network paths as production. Live testing reveals timeout patterns, decline code variations, and timing issues that sandbox testing never shows. The cost is negligible. The risk of going to production untested is not.
Accepting Multiple Payment Methods
Credit cards are not the only option. Digital wallets, bank transfers, buy now pay later services, and regional payment methods all compete for attention at checkout. Adding each one requires separate integration work. The maintenance burden grows with each option. I've seen checkout pages with twelve payment methods and conversion rates worse than pages with three. Too many options cause decision paralysis. The user closes the tab and goes elsewhere. The practical approach is to start with the methods your audience actually uses. Analyze your existing transaction data. See which payment types have the highest completion rates. Add the ones that are missing if they represent a significant segment. Remove the ones that are rarely used or have high decline rates. The optimal set changes over time as user preferences shift and new methods emerge. Review the data quarterly and adjust accordingly. There's also the question of pricing. Some payment methods cost more to process. Credit cards carry interchange fees that can run two to three percent of the transaction. Digital wallets sometimes have lower fees but higher decline rates. Bank transfers are cheap but slow. The margin impact matters for low-ticket items. A five dollar product with a two percent processing fee leaves less than four dollars after costs. The math changes the acceptable payment method mix.
Security Beyond The SSL Certificate
SSL encrypts the connection between the browser and your server. It does not protect against compromised servers or insider threats. Card data should never touch your application code unless absolutely necessary. Use hosted payment fields or iframes provided by your gateway. The data goes directly from the user's browser to the gateway. It never passes through your infrastructure. This removes you from the PCI compliance scope in most cases. I've seen teams store card numbers in their databases for convenience. This is a compliance nightmare. PCI DSS requires encryption at rest, access logging, regular audits, and segmentation of cardholder data environments. The cost of maintaining that infrastructure usually exceeds the benefit. Hosted fields solve the problem without sacrificing user experience. The gateway handles the sensitive data. You handle the transaction result. Logging is another area where teams slip up. Transaction IDs, approval codes, and amount data are fine to log. Card numbers, CVVs, and full track data must never appear in logs. I've reviewed codebases where the error handling accidentally included card details in stack traces. Those traces sometimes ended up in centralized logging systems. Auditors flag that immediately. The fix is to sanitize all payment-related data before logging and to use structured logging that separates transaction metadata from card information.
The After-Sales Experience
Payment collection is the beginning of the relationship, not the end. Receipts need to be clear and timely. Refund policies should be easy to find and execute. Dispute resolution processes should be documented and accessible. I've seen merchants lose customers not because of the payment process but because of the post-purchase experience. A confusing receipt or a refund that takes weeks to process creates the same frustration as a declined card. Automated receipts reduce support volume. Send them immediately after payment confirmation. Include the transaction ID, amount, payment method last four digits, and a summary of what was purchased. Link to your return policy and support contact. The email should look professional and match the brand. Generic transactional emails feel like a mistake and make customers second-guess whether their payment went through. Refund processing time varies by payment method. Credit card refunds typically take five to ten business days to appear on the customer's statement. Digital wallet refunds are faster. Bank transfers depend on the institution. Set expectations upfront. Tell customers how long refunds take and what they should see on their statements. The uncertainty causes more support tickets than the refund process itself.
When To Walk Away From A Gateway
Payment gateways change terms. Fees increase. Support quality degrades. Features get deprecated. I've watched teams stick with providers long past the point of returning value because switching costs feel high. The switching cost calculation should include the opportunity cost of missed features and the operational cost of working around limitations. If a competitor offers better rates, better tools, or better support, the switch is usually worth the migration effort. The migration process itself is not trivial. You need to update integration code, test the new provider, and coordinate with your accounting team on changed payout schedules. I recommend testing the new provider alongside the old one for a period before switching. Route a small percentage of traffic to the new gateway and compare performance. Once you're confident, redirect the rest. The downtime is minimal if you plan it carefully. There's also the question of multi-provider strategies. Some teams maintain relationships with two gateways and split traffic between them. This provides redundancy if one provider has an outage and can optimize for cost by routing transactions to the cheaper provider when performance is equal. The complexity of managing two integrations is the trade-off. For high-volume merchants, the redundancy and cost savings justify the overhead. For smaller operations, a single provider is usually sufficient.

Measuring What Matters
Conversion rate is the obvious metric. The metrics beneath it tell the real story. Time to first decline. Percentage of transactions requiring 3D Secure. Average dispute response time. Chargeback rate by payment method. These breakdowns reveal where the friction lives. I track them weekly and set thresholds that trigger investigation. A sudden spike in declines might indicate a gateway issue. A gradual increase in 3DS challenges might indicate changing issuer behavior. A rising dispute rate might indicate a product or service problem. The data needs to be complete. If you're only measuring successful transactions, you're missing the decline reasons. Capture the decline code and the reason when possible. Many gateways return rejection reasons that explain whether the decline was due to fraud, insufficiency, or technical error. Store this information with the transaction record. It becomes valuable when patterns emerge or when you need to appeal a dispute with evidence of the original decline. Performance monitoring extends beyond the checkout page. The payment gateway response time affects the user experience directly. If the gateway takes more than two seconds to respond, users notice. Implement timeouts and fallbacks. Show a loading state while waiting. Display an error if the timeout is exceeded. Never leave the user staring at a spinner indefinitely. I've built fallback pages that activate when the gateway response time exceeds a threshold. The page explains the situation and offers alternative payment methods or a callback to try again later.

