The Current State of Twitter Login Through Chrome
Logging into Twitter via Chrome has gone through a rough patch. The platform changed how it handles sessions, cookies, and third-party authentication. What used to take two clicks now involves juggling multiple tabs, sometimes a verification code, and occasionally a CAPTCHA that asks you to identify bicycles or crosswalks. I've been managing Twitter accounts for clients for years, and the friction keeps increasing. Seamless Access Or Privacy Tradeoff Twitter Login Via Chrome Redefined is really about finding where convenience ends and your data starts getting sold to advertisers. Chrome remembers your login. That's the whole value proposition. But it also means Google can see which accounts you're authenticated with, when, and for how long. Twitter's own session tokens get stored in your browser profile, and those cookies have a lifespan depending on whether you check "Remember me."
How the Login Flow Actually Works Now
Open Chrome, go to x.com or twitter.com, enter your credentials. If you have 2FA enabled, you'll get a prompt for your authenticator app or a text message. Chrome may offer to save your password the first time. After that, it autofills. The session stays alive until the cookie expires or you log out manually. That's the basic version. The complicated part is what happens in the background. Twitter sets several cookies beyond the session token. Some track your activity across other sites via embedded widgets. Chrome's autofill feature uses data stored locally, but it also syncs to your Google account if you have that turned on. That sync is optional, but most people never check the setting.
Setting Up a Cleaner Login Experience
If you want less friction without giving away everything, there are steps you can take. Not all of them are obvious. This is the single most effective change. Go to the profile icon in the top right of Chrome, click "Add," and create a separate profile named something like "Twitter" or "Social." This profile won't share bookmarks, passwords, or browsing history with your main one. When you log into Twitter here, the cookies stay contained. It takes about three minutes to set up and five seconds to switch between profiles afterward. Navigate to chrome://settings/cookies and set it to block third-party cookies. This stops Twitter's tracking pixels from reading your activity on unrelated sites. You'll still log in fine. Third-party cookie blocking has been the default in Chrome for a while now, but some older settings might override it. Double-check the toggle.
Get the Full Details
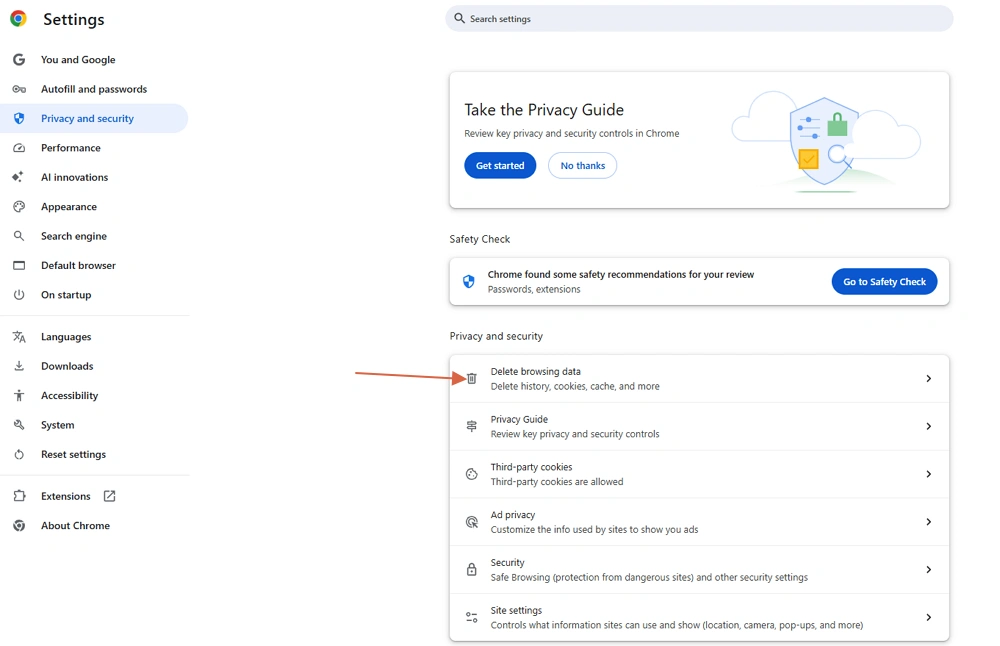
Chrome's password manager is convenient until it isn't. Go to chrome://settings/passwords and toggle off "Allow Chrome to save passwords" if you don't want Twitter credentials leaving your device. Alternatively, use a dedicated password manager like Bitwarden or 1Password. I switched to a local password manager specifically because I noticed my Chrome profile was syncing login data to Google's servers even after I disabled cloud sync in the obvious settings menu. There's a separate checkbox buried under Chrome sync settings that controls password syncing independently. Missed it for months. Incognito mode doesn't save cookies, history, or passwords. It's useful if you're accessing Twitter from a shared computer or just don't want a persistent session. Close the window and the session dies immediately. The downside is you log in every time. For most people this is fine. I ran into a real issue last year when I blocked third-party cookies and disabled password autofill on a work machine. Twitter's login page started failing on the second authentication step. The problem was that Twitter's fraud detection system uses cookies from subdomains like ads.twitter.com to verify the session wasn't bot-generated. Block those, and the login loop triggers. The workaround was adding an exception specifically for *.twitter.com and *.x.com in the third-party cookie block list. It lets the legitimate auth flow through while still blocking cross-site trackers. Takes about two minutes to configure once you know what domain patterns to allow.
Another problem: Chrome's "Autofill" feature sometimes pre-fills old or incorrect passwords if you've changed your Twitter password recently but Chrome hasn't updated its stored credentials. I've seen this happen after a password reset. The fix is to delete the saved Twitter entry from chrome://settings/passwords before logging in again, then save the new one when prompted. Not a big deal, but easy to overlook.
The Privacy Reality Check
Even with all these adjustments, Twitter still collects data. Blocking cookies and using a separate profile limits what Chrome shares, but the website itself tracks page views, interaction patterns, and device information. Chrome's Incognito mode doesn't hide your activity from Twitter. It only prevents the browser from storing it locally. If privacy is a serious concern, the browser-level tweaks only get you so far. Twitter's own terms and data practices still apply regardless of how you log in. I've found that combining a dedicated Chrome profile with a lightweight email alias for account creation reduces the amount of personal data attached to the account significantly. Most people don't realize Twitter links accounts through phone numbers and email addresses. Using a throwaway email for secondary accounts changes what Google and Twitter can correlate about you.

Alternative Approaches
Some people switch to Firefox specifically to avoid Chrome's ecosystem. Firefox has stronger built-in privacy defaults and doesn't integrate with a search engine's advertising network in the same way. The login experience is functionally identical, but the data trail looks different. Others use the Twitter mobile app instead of the browser entirely. The app has its own permissions model and doesn't rely on browser cookies. It does require granting location and notification access on most devices, which some users find worse than the browser tradeoff. There's no perfect setup. The dedicated profile approach with third-party cookies blocked covers most practical needs. It reduces Chrome-side data leakage without breaking the login flow, and it keeps your Twitter session isolated from whatever else you're doing in the browser. That isolation is usually worth the extra click of switching profiles.