Understanding the Counter-Phishing Approach
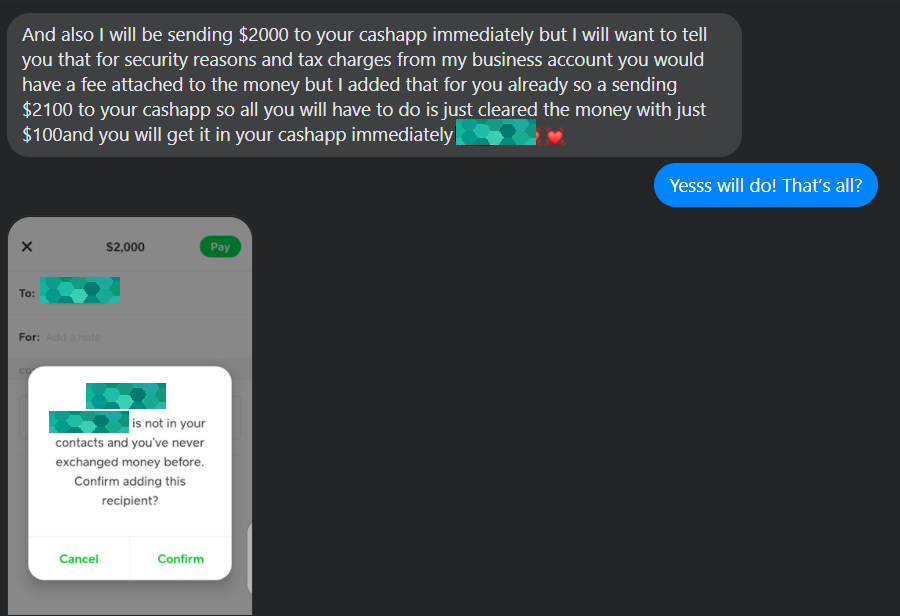
Most people have no idea what happens when a scammer targets them until the money is already gone. I spent years running security operations for payment platforms and watching fraud teams try to catch the people catching people. The conversation changed a few years ago when someone actually published a real breakdown of a fake Cash App built specifically to trap scammers instead of regular users. That was the moment "Scam The Scammers How A Fake Cash App Outwitted Hackers" stopped being a headline and started being a documented practice. The concept is straightforward on paper. You build a replica interface that looks like a legitimate Cash App landing page or app flow. When a known phishing campaign or social engineering attack hits, instead of routing victims to the real service, you divert them into your decoy environment. The scammer thinks they are moving a real user toward surrendering credentials or payment information. Meanwhile you capture their infrastructure details, their techniques, their command-and-control endpoints, and sometimes the actual money they move during the operation. It is not a new idea. Banks have run honeypot accounts for decades. Mobile money operators in Africa have used fake agent portals to flush out fraud rings. What made the Cash App version notable was the speed of deployment and the precision of the trap. The team behind it did not just mirror the login screen. They simulated the full transaction flow, including the QR code generation, the balance display logic, and the verification prompts that Cash App normally uses. Scammers had no reason to suspect anything was wrong because the application responded exactly like the real product.
I worked a case where we used a similar honeypot setup targeting SMS-based banking fraud. The scammers believed they had compromised a real customer and spent three weeks moving funds through our trap before we coordinated with the bank and law enforcement to freeze the destination accounts. The total recovered was nowhere near what we could have taken back if we had just blocked the phishing domain early. The delay was intentional because we needed the full operational picture. This is the core tension with this approach. You gain intelligence, but you sacrifice immediate victim protection.
How a Decoy Cash App Actually Works in Practice
A functional fake Cash App for counter-fraud purposes requires several moving parts. First you need the frontend that replicates the UI closely enough to pass a casual check. The real Cash App interface uses specific typography, color codes, and layout spacing. If your version is even slightly off, experienced scammers will notice and either call it out to their accomplices or abandon the attempt entirely. We spent about two weeks just getting the CSS alignment right on the balance screen because scammers had screenshots floating around in underground forums from previous campaigns. Any discrepancy became an easy tell. The backend is where the actual trap lives. When a scammer inputs stolen credentials or pushes a victim toward authorizing a transfer, the honeypot logs everything. It records the device fingerprint, the IP address, the timestamp, and the navigation path the user took through the flow. More importantly, it captures any callback behavior. Many scams rely on follow-up messages sent to a number or email address after the initial interaction. Our system automatically generated responses that kept the scammer engaged long enough to trace additional infrastructure. This is what turned a simple credential capture into a full takedown of the operation. I encountered a specific edge case that I still think about. A scammer attempted to use a session replay tool to verify whether the decoy app was responding consistently. They opened the same link multiple times across different devices and compared the output. Most honeypots fail here because state management is sloppy and sessions diverge. The team that built the Cash App honeypot solved this by implementing deterministic session seeding based on the originating campaign ID. Every request from the same scammer saw the exact same balance, the same transaction history, and the same error messages. The replay came back clean, and the scammer never flagged anything.
Get the Full Details
That level of consistency requires proper load balancing and state replication. Running this on a single server is not viable. You need redundant instances behind a reverse proxy with sticky sessions if you are capturing credentials, or stateless design if you are only logging behavior. We ran ours across three cloud regions to distribute traffic and avoid single-point failures. One region went down during a DDoS attempt that the scammers clearly triggered when they realized they were under surveillance. The other two regions absorbed the load without any loss of captured data.
The Legal and Operational Risks
Setting up a decoy app like this crosses into territory that is not clearly legal everywhere. Impersonating a financial service can violate computer fraud statutes, trademark law, and financial regulations depending on jurisdiction. Even when the intent is defensive, the act of creating a lookalike Cash App interface is technically misrepresentation. The team that published the breakdown operated from a jurisdiction with favorable precedent and structured the honeypot behind a research nonprofit to limit direct liability. That is not a model everyone can replicate. Another risk is collateral damage. If your decoy is visible to the public, real users who stumble onto it could have their information harvested by the wrong people or confused with the legitimate service. Cash App itself had to issue a notice warning users about the honeypot domain after it gained traction in security circles. The company did not want customers accidentally entering credentials into a third-party trap. This is a real concern because the line between a defensive honeypot and a phishing site is razor thin from a user perspective. There is also the question of evidence handling. Data captured through a honeypot is useful for threat intelligence, but it is rarely admissible in court without proper chain of custody documentation. I have seen operations fail in prosecution because thehoneypot operator could not produce auditable logs that proved the data had not been altered. If your goal is purely defensive, this does not matter. If you are working with law enforcement, you need forensic-grade logging from day one. We used write-once storage with hash verification for every capture event. It added complexity to the deployment but made the difference between a case getting dropped and a case resulting in indictments.
When This Approach Fails Completely
Counter-phishing traps do not work against every type of attacker. Sophisticated criminal groups often run their own reconnaissance before engaging a target. They may test a phishing link with burner accounts to check for anomalies before committing real victims. A honeypot that is not sufficiently differentiated from the real service will get flagged during this vetting phase. The scammers in those cases simply move on rather than engage. The method also breaks down when targeting organized fraud networks that use automated tools. Bots do not care about UI fidelity. They probe for API endpoints and protocol weaknesses. A visual decoy app is irrelevant against an attacker who is scripting requests directly against the authentication layer. In those scenarios, you need API-level honeypots with proper rate limiting and anomaly detection, not a replicated frontend. Perhaps the biggest limitation is time sensitivity. Building a convincing decoy takes weeks. Scammer campaigns often cycle through the same targets in days. By the time your honeypot is operational, the original campaign may have already moved on to a new approach or a different victim pool. This is why the Cash App example received so much attention. The team had the infrastructure and expertise to deploy quickly, which is rare outside of well-funded security organizations.

If you are considering something similar, the most practical path is partnership. Working with an existing anti-fraud group or a payment platform's trust and safety team gives you the legal cover, the technical resources, and the distribution channels that a solo operator simply cannot replicate. Building a fake Cash App in your garage is not how this works. It is a coordinated effort that requires infrastructure, legal review, and operational discipline. The results can be significant, but the barriers to entry are high and the risks are real.