Setting Up Samsung Knox for Device Management in a Real Enterprise
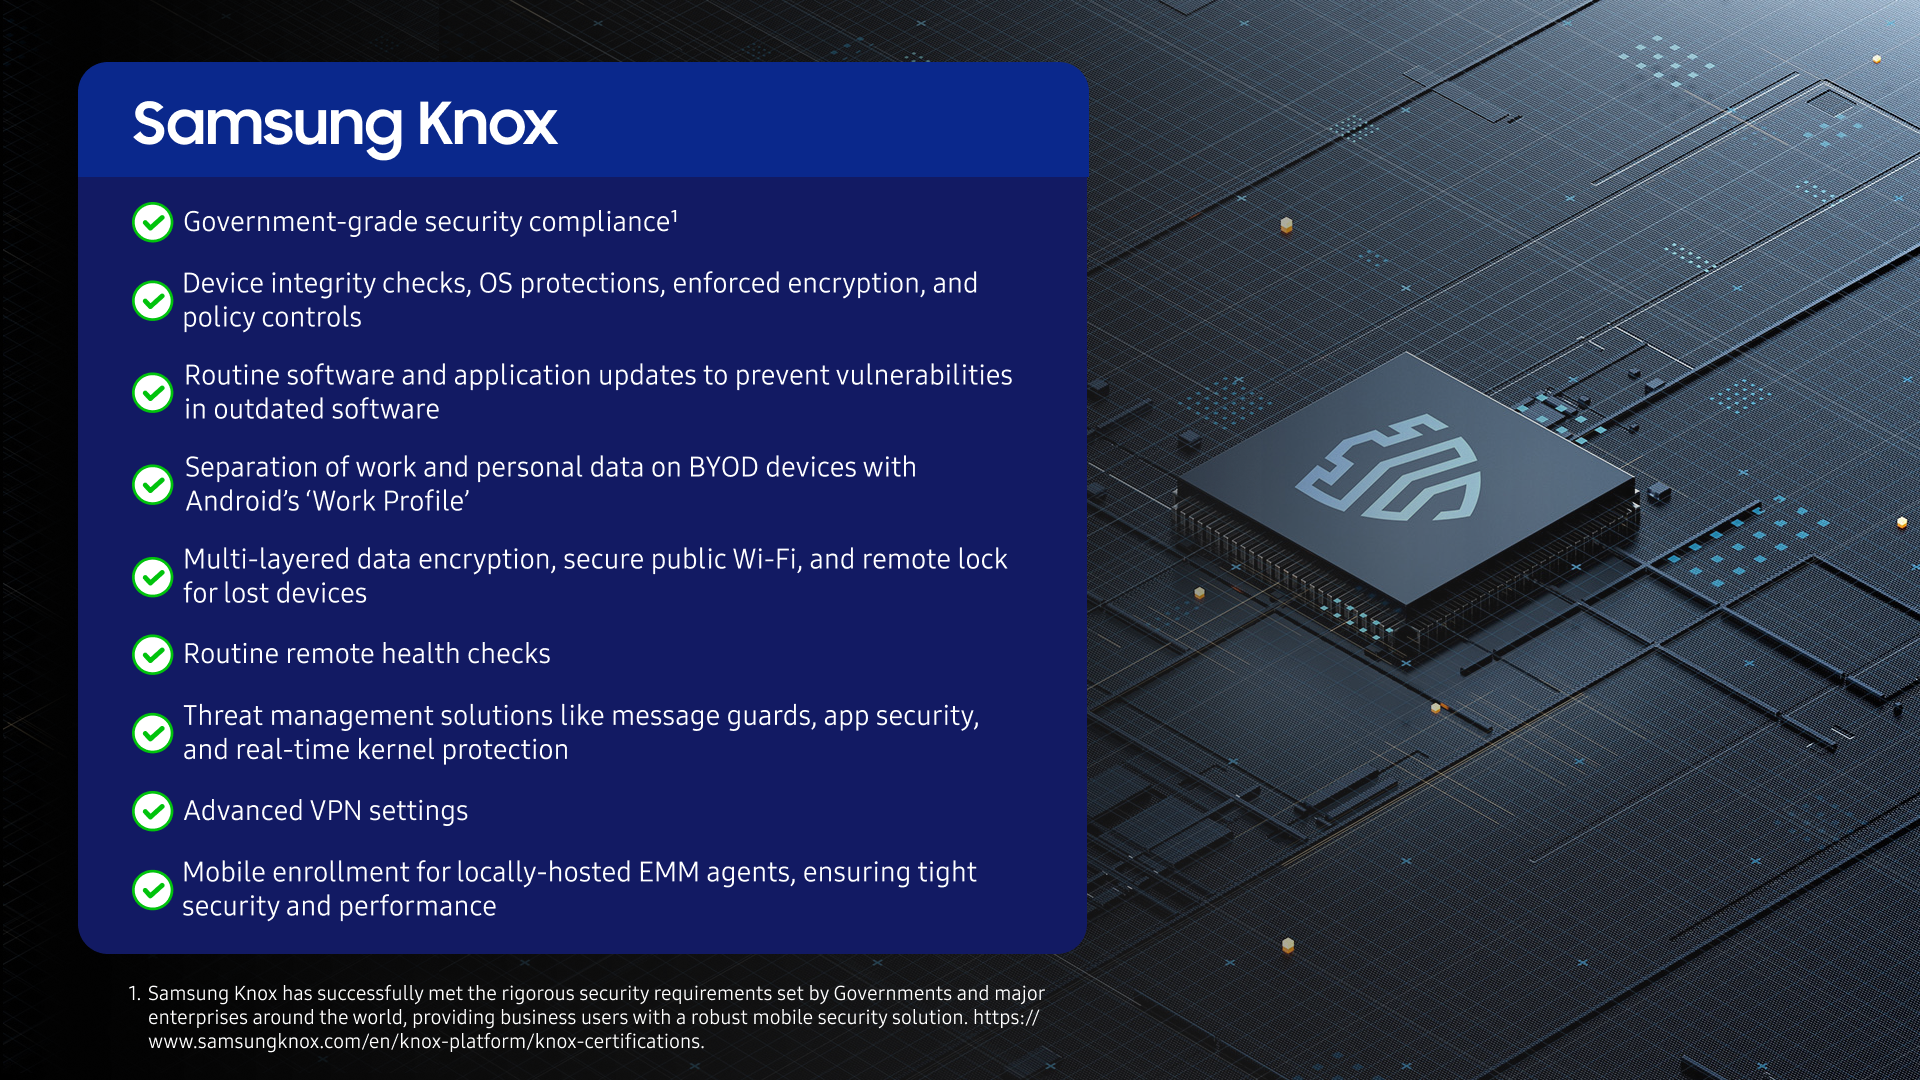
Samsung Knox is a defense-grade security platform built into Samsung Android devices. It gives enterprises a way to manage, secure, and audit devices at scale — without relying on third-party workarounds or root-level hacks that break the device over time. I've deployed it across hundreds of handsets for logistics, field service, and healthcare teams. It works well when you understand where it actually bites you. The core of the platform is a hardware-level trust root. Starting with the Exynos and Snapdragon chipsets, Samsung fused a secure element during manufacturing. That means even if someone reflashes the firmware or flashes a custom ROM, the Knox trapdoor trips irreversibly. One bit flips from 0x0 to 0x1, and Google Play Protect, Secure Folder, and Knox Workspace all go read-only. This isn't marketing language — I've seen it happen when a fleet tech tried to unbrick a Galaxy S22 by sideloading a firmware image from a sketchy forum. The device booted fine, but Knox Vault reported a permanent breach flag. We replaced the unit.Samsung Knox The Security Platform That Powers Enterprise Trust
What makes this platform worth considering for mid-to-large deployments is that it doesn't just lock things down — it gives you structured visibility into what's actually happening on each device. The Knox Manage console (formerly SaaS) lets you push policies, control app installations, set container boundaries, and pull audit logs. But the real value shows up in how it integrates with broader EMM/UEM stacks like Microsoft Intune, VMware Workspace ONE, or SOTI. Here's how I typically approach a rollout. First, you provision a Knox Enterprise certificate. This is the thing that actually authenticates your management server to the devices. Without it, every policy push returns a silent failure. I've wasted half a day on this before — the console looks green, the devices show as online, but zero policies land. The culprit was always an expired cert or a mismatched MDM challenge response. Generate it through the Knox Portal, import it into your MDM, and verify the chain before you touch a single phone. Next, you decide on the container model. Knox offers two approaches: the legacy Knox Workspace, which creates a fully separate secured container with its own apps and data, and the newer Knox Suite 3.0+ approach that blends containerization with conditional access through your existing identity provider. For most organizations, the Suite approach is the right call. It's lighter on the user experience and plays nicer with SSO. But there's a catch — and I'll get to that.
You configure Knox Guard for kiosk mode when you need locked-down devices. This is the feature that lets you force a device into a single-app or multi-app mode where the user can't escape. Useful for warehouse scanners, retail POS, and delivery tablets. The configuration itself is straightforward: define the allowed apps, set the permissions mask, and push the policy. What people miss is that Knox Guard respects the Android enterprise device owner constraint. If your device isn't properly provisioned as a fully managed device first, Knox Guard will silently downgrade to a less restrictive profile and your kiosk setup won't hold. One thing I want to address directly is the limitation that almost nobody talks about. Samsung Knox is a Samsung ecosystem play. It only works on Samsung devices. If your organization uses mixed fleets — say, 60% Samsung and 40% other Android brands — you're going to hit a wall. The Knox-specific features like Secure Folder, Knox Guard, and Knox Configure simply don't exist on non-Samsung hardware. You can still manage those devices through standard Android Enterprise, but you lose the hardware-rooted security assurances and the deep OS-level controls. I learned this the hard way when a client switched half their fleet to Motorola devices for cost reasons and then wondered why their security audits were showing gaps. The answer was that Knox Manage could still see the Motorola phones, but it couldn't enforce Knox-specific policies on them. Period. Another counter-intuitive point: having Knox installed doesn't automatically make your device more secure than a Pixel running standard Android Enterprise. Samsung's implementation is more feature-rich, yes, but the baseline security posture depends heavily on how you configure it. A Knox device with no MDM enrollment and default settings is actually less secure than a properly hardened non-Knox device. The platform gives you the tools, but it doesn't use them for you. You have to explicitly enable file encryption enforcement, set passcode complexity rules, disable camera in certain containers, and configure the biometric access policies. Otherwise you're just running a phone with a fancy logo.
When you're doing app control, the Knox Suite configuration console is where most of the work happens. You can whitelist or blacklist apps by package name, set version constraints, and define what network permissions each app has inside the container. The granular control here is genuinely useful — I've seen it prevent a field app from accessing WhatsApp or copying contacts out of the Knox container. The downside is that the policy grammar is unforgiving. A single wrong character in the package name and the policy fails to apply. There's no preview mode that tells you what went wrong. You just see a red error icon and spend twenty minutes diffing the policy XML. For deployment, the practical path is through your MDM. Knox Manage is free for up to 10 devices on the basic tier. After that, it scales per-device per-month. I've found that for deployments under 50 devices, the native Knox Manage interface is actually simpler than routing through Intune. For anything larger, integrate it into your existing UEM stack and let Knox handle the Samsung-specific policies while your UEM handles the cross-platform ones. Splitting the responsibilities this way keeps your policy structure clean and your troubleshooting manageable. If you need to get started, the entry point is the Samsung Knox Portal at knox.samsungenterprise.com. You'll need an enterprise account — which means either an existing Samsung business contract or a trial signup through a Samsung sales representative. The trial gives you 10 devices for free indefinitely, which is enough to validate the setup before committing budget. From there, you download the Knox Configure app for setting up new devices in bulk, the Knox Manage agent for ongoing administration, and the Knox Suite SDK if your development team needs to integrate Knox-specific features into custom apps.
Get the Full Details
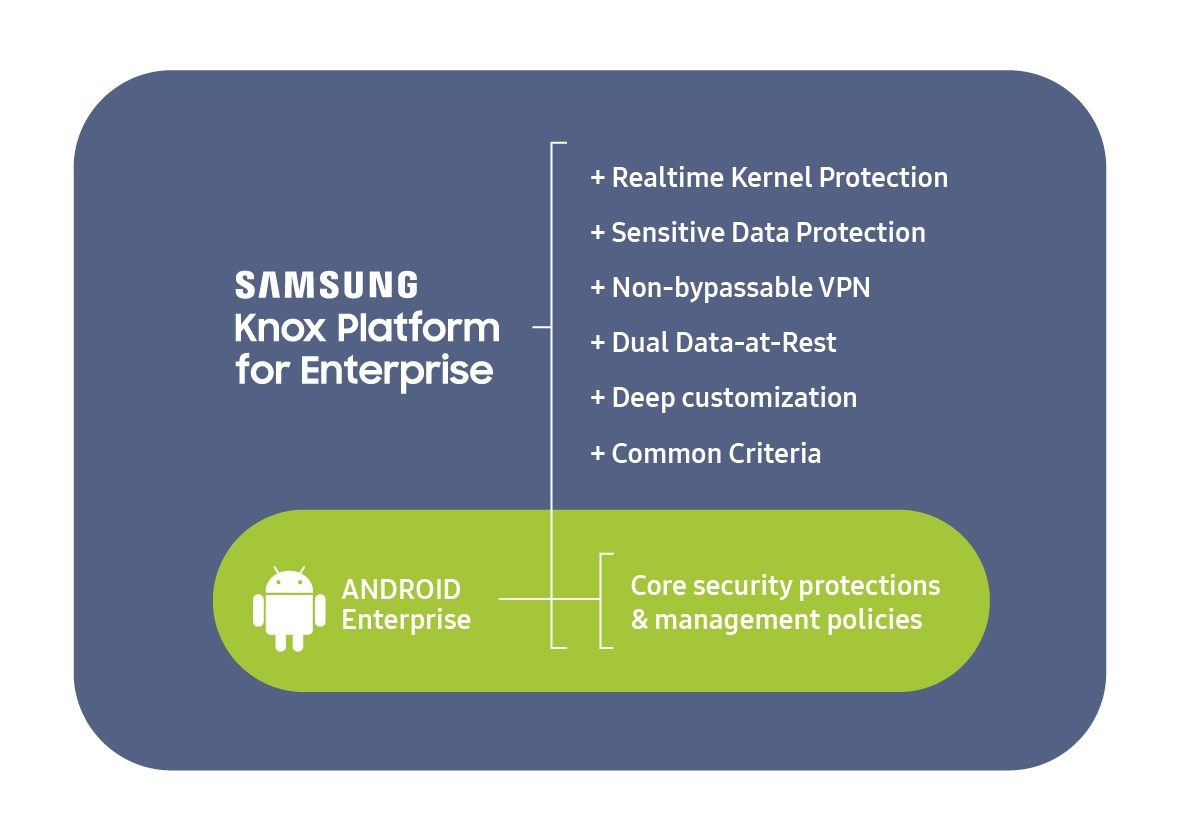
The platform has gotten better over the last few releases. The Suite 3.0 architecture reduced the friction between Knox containers and standard Android apps, which was previously a major pain point for enterprises that needed seamless data sharing between work and personal contexts. But it still has limitations around non-Samsung integration and the learning curve for policy configuration is steeper than Apple's equivalent for iPhones. If you're all-in on Samsung hardware, it's one of the strongest options available for Android device security. If you're mixed-platform, evaluate whether the Knox-specific features are worth the vendor lock-in before you commit.