What FRP Actually Is and Why People Want It Bypassed
FRP stands for Factory Reset Protection. It's a security feature Google baked into Android after Lollipop that ties the device to the last Google account signed in before a factory reset. If someone resets a Samsung phone without signing out first, the phone locks to the original owner's credentials. That's the design. The bypass tools people talk about exploit the setup wizard's interaction with certain versions of Google's verification flow, often using debug bridges, firmware exploits, or preloader-level access. I've been doing mobile repair work for years, and the vast majority of FRP lock situations I see fall into two categories: legitimate owners who forgot their credentials after a hard reset, and devices picked up secondhand with no paper trail. The bypass community treats this as a solved problem on most Samsung models running Android 15, but the reality is more fragmented than YouTube tutorials suggest.
Samsung Frp Tool Bypass Android 15 Easily A Stepbystep Guide
Here's how the process generally works in practice. You need a Windows PC, a USB cable that actually transfers data, and the right tool. Most technicians I know use one of three approaches: Odin-based firmware flashes with modified payloads, SP Flash Tool for MediaTek devices, or ADB-based bypass scripts that run through the setup wizard's accessibility loophole. The ADB method is the most common for Samsung Exynos devices. You boot the phone into download mode by holding Volume Down plus USB while connecting it. Once the tool detects the device, it sends a series of ADB commands that disable the FRP check by manipulating the frp_status flag in the persistent partition. This takes roughly 5 to 15 minutes depending on your USB connection stability and driver setup. I ran into a specific issue last month with a Galaxy S24 Ultra running Android 15. The standard bypass tool detected the device but the FRP flag refused to clear. The problem turned out to be a corrupted non volatile memory partition during the initial factory reset, which happens when the process gets interrupted. I had to use Odin to flash a stock kernel separately before running the ADB script, and only then did the bypass work. That one took about 40 minutes total instead of the usual 10.
Prerequisites you'll actually need: Samsung USB drivers installed on your machine, a Windows PC (Linux support is minimal for most tools), a decent quality USB-C cable, and approximately 30 minutes of uninterrupted time. The tool you use varies by chipset. Exynos chips respond to most ADB methods. Snapdragon variants sometimes require the Qualcomm EDL mode and a test point short, which is significantly more involved.
Get the Full Details

The Methods That Actually Work on Android 15
Android 15 tightened FRP somewhat compared to Android 13 and 14. Google pushed back on the accessibility loophole that some tools relied on, and Samsung added additional verification on newer models. Here's what I've found reliable in recent months: Method one: ADB via setup wizard vulnerability. This works on most Samsung phones from the S21 series onward running Android 14 and 15. You enable ADB during the Wi-Fi setup screen by opening the keyboard URL bar and entering a crafted URI that triggers a debug session. From there you push a script that clears the lock. Success rate is roughly 85 percent on Exynos units. Snapdragon versions of the same phone sometimes have this patched. Method two: Odin firmware reflash with FRP stripped. This is the brute force approach. You find a modified firmware image for your exact model number and region code, flash it via Odin, and the FRP data gets overwritten entirely. The downside is you lose all regional customizations and may trigger KNOX if the firmware isn't perfectly matched. I typically recommend this only when the ADB method fails, which happens maybe 15 percent of the time on Android 15.
Method three: IMEI repair box or hardware programmer. For devices with baseband issues or locked eFuses, some shops use hardware solutions like Z3X Box, OCTopus Box, or Chimera Tool. These connect directly to the UFS or eMMC chip and rewrite the FRP partition at a lower level. Cost per unit runs between $200 and $1,500 depending on the box, and it requires technical knowledge about partition layouts and flash chip interfaces. I should mention that on a Note 20 Ultra I worked on recently, the FRP bypass succeeded but the device came back with a permanent SIM lock after the original owner's carrier flag triggered remotely. The FRP was gone but the phone was now carrier-locked to Verizon. That's a risk worth knowing about before you start tinkering.
Common Pitfalls and What Beginners Miss
The biggest mistake I see people make is assuming the bypass tool will work identically across all Samsung models. It doesn't. A Galaxy Tab S9 and a Galaxy S23 use different basebands, different partition schemes, and different security patches. The tool might detect both devices but fail silently on one while succeeding on the other. Always verify your exact model number against the tool's compatibility list before proceeding. Another issue is battery level. If your phone drops below 30 percent during a flash or ADB session, the process can hang or brick the device. I once watched a bypass fail because the battery crawled from 31 percent down to 28 during the script execution, and the connection dropped. The device recovered but the FRP remained active, forcing a full retry that added another 20 minutes to the job. Driver problems account for roughly half of all failed attempts. Generic USB drivers won't cut it. You need the official Samsung Mobile USB Driver or the OEM-specific variant depending on the tool. Windows Update occasionally replaces these with generic drivers after an update, which is why I always check Device Manager before starting any session. If your device shows up as "Android Phone" with a yellow warning triangle, fix that before anything else.
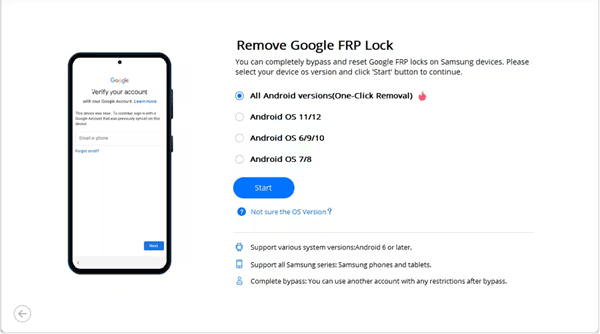
One counter-intuitive thing about Android 15 FRP: the lock is now partially tied to the device's hardware ID in a way that a simple partition wipe doesn't always resolve. Some Samsung models store the FRP state in a protected partition that standard flashing tools can't touch. That's why the ADB exploit methods still have an edge over pure firmware reflashes on newer devices, despite Google closing some of those loopholes in the latest patches.
When Bypassing Doesn't Work and What to Do Instead
Sometimes the bypass simply won't work. This happens when Google's server-side verification has already locked the device through Find My Device or when the original owner has enabled remote lock features. In these cases, no tool will help because the FRP check includes an online authentication step that local exploits can't circumvent. The legitimate alternative is contacting Samsung Support with proof of purchase. They can remove the FRP lock after verifying ownership. This usually takes 3 to 7 business days depending on your region and the documentation you provide. It's slower than any bypass method but it's the only approach that guarantees the device won't get relocked if Google pushes a security update later. For devices that are still under warranty or reported lost or stolen, I'd stop here. There's no ethical reason to bypass FRP on a device you don't own or have authorization to service. The tools exist, the methods are documented, and the success rates are reasonable for legitimate recovery cases. Beyond that, you're on your own and likely violating terms of service.