Getting Into Your Payroll Portal Without Losing Your Mind
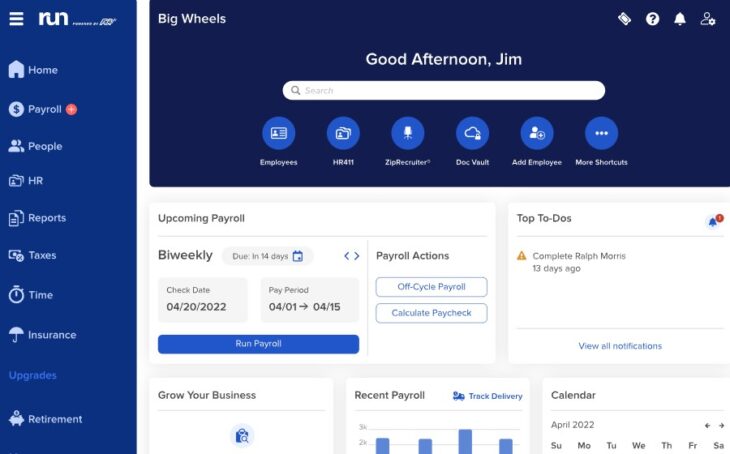
The ADP payroll login page looks the same as it did five years ago. The URL redirects you somewhere in the runADP family depending on your employer's specific configuration. Some companies use their own branded subdomain, others push you through a shared gateway. You type in your credentials, get hit with a multi-factor authentication prompt, and hope the session doesn't time out before you finish running the hourly reports. Here is how it actually works on the ground. When you hit the login page, you are authenticating against ADP's identity provider, which then issues a session token scoped to your employer's organization ID. Your company might require SSO through Okta, Azure AD, or a direct ADP credential set. The flow diverges sharply depending on which route your HR department chose when they set up the account. I learned this the hard way in 2022 when a client switched from direct login to SAML-based SSO without updating their internal documentation. Three payroll cycles of people being locked out before someone noticed the mismatch. The fix was straightforward once we found it: the administrator had to update the Assertion Consumer Service URL in the SAML configuration, but the blame was assigned to whoever hadn't tested the transition properly. The authentication is only the first hurdle. After you get in, the portal routes you to one of several dashboards depending on your role. Timeclock managers see attendance data. Payroll administrators see the run queue. Employees see their own pay stubs. This role-based segmentation is controlled at the organization level, not the user level, so if someone in your company has broader access than they should, it usually traces back to how the org was structured during implementation rather than a security flaw in the platform itself.
Session management is where most people run into trouble. ADP sessions typically last between 15 and 30 minutes of inactivity, then expire. The platform will usually warn you around the ten-minute mark, but if you have multiple tabs open and the background tab expires silently, you lose any unsaved data in that tab. I keep a second monitor dedicated to the payroll run dashboard now. It saves me from losing progress when I am comparing multiple pay group runs side by side. Before I did that, I lost an entire half-finished correction batch once because I left the tab sitting open while I stepped away for a team call. Multi-factor authentication is non-negotiable now, and it changes how you interact with the system. If your company uses the ADP app for MFA, you need the phone nearby every time you log in. There is no way around it. Some administrators try to work around this by requesting SMS fallback codes, but that is getting rare as vendors drop SMS as an acceptable second factor. The push notification method through the app is faster and more reliable anyway, but you do need a device with battery life and cellular or data coverage. I have seen payroll periods delayed because an administrator's phone died overnight and they could not authenticate the next morning. Password resets go through a separate flow that is completely detached from the main login page. If you forget your password, you click the forgot password link and wait for an email or text. The reset link is valid for a limited window, usually one hour. If you miss that window, you have to start over. This sounds trivial but it causes real problems during payroll deadlines when people are rushing and closing tabs too quickly. Keep the reset email accessible in a separate browser window so you are not hunting for it under time pressure.
There are limitations worth acknowledging. ADP's web interface is functional but sluggish on large datasets. Pulling a report for a company with ten thousand or more employees across multiple business units can take two to three minutes to render, sometimes longer during peak hours between Thursday and Saturday of a payroll cycle. The platform is not designed for bulk data export through the browser. If you need to pull large sets of data regularly, the ADP REST API is the proper tool, but accessing it requires your company to have an API-enabled account and a developer or administrator who can manage the OAuth tokens. Most mid-market employers do not have either, so they are stuck working within the performance constraints of the web interface. Another issue that does not get discussed enough is the mobile experience. The ADP mobile apps exist, but they are purposefully simplified. You can view pay stubs and request time off. You cannot run payroll or make system-wide changes from the mobile interface. If your company relies on managers approving timecards or adjusting schedules while they are away from their desks, the mobile tools will frustrate you. I worked with a distribution company where warehouse supervisors needed to approve overtime edits on the floor. They ended up printing the approval forms and walking them to the payroll office just to get the changes processed in time for the run cutoff. The platform also has a notorious quirk with time zone handling. Payroll data is processed according to the company's defined payroll calendar and time zone settings, but employee timeclock entries are recorded in local device time unless your time clock hardware pushes UTC. If you have employees in different time zones, you need to verify that your timekeeping integration is normalizing timestamps correctly. I spent an afternoon reconciling discrepancies that turned out to be a three-hour offset between two facilities that were both supposed to be on Eastern time but one facility's time clocks were set to Central. The payroll ran correctly because the system used the facility's configured zone, but the reports showed inconsistent hours across locations and it took two cycles to catch the configuration drift.
Get the Full Details

For administrators managing the system, the organization setup page is where everything connects. Your business units, job codes, pay elements, deduction mappings, and tax setups all live there. Changes to this structure affect live payroll runs, so there is a deliberate lag between when you submit a change and when it becomes active. Most structural changes take effect on the next scheduled pay period. If you make a mistake mid-cycle, you cannot simply undo it for the current run. You have to document the error, correct the configuration, and apply the fix starting the following period. This means your testing discipline matters more than most people realize. I always create a test pay group in the preview environment before moving changes to production, even for small tweaks like updating a withholding allowance table. Security-wise, ADP maintains SOC 2 Type II certification and the platform supports role-based access controls, audit logging, and IP restriction rules at the organization level. Your company can lock access to specific office IP ranges if they choose. However, the responsibility for configuring these controls correctly falls on the employer's IT or HR team, not on ADP. I have seen companies leave their payroll portals open to the internet with no IP restrictions because nobody thought to enable the feature. It is not ADP's fault, but it is a real risk that exists in a significant number of implementations. If you are trying to access payroll data and the standard login paths are not working, the first thing to check is whether your employer has moved to a different deployment model. ADP has been migrating customers from the older Workforce Now portal to the newer Vantage platform, and the login URLs are different between the two. Some companies have not completed the migration yet, so you may encounter links that point to legacy endpoints that no longer accept new sessions. The workaround is to contact your company's ADP account representative or the internal HR helpdesk and ask which portal your organization is currently assigned to. They will give you the correct base URL, and from there the login flow is standard.