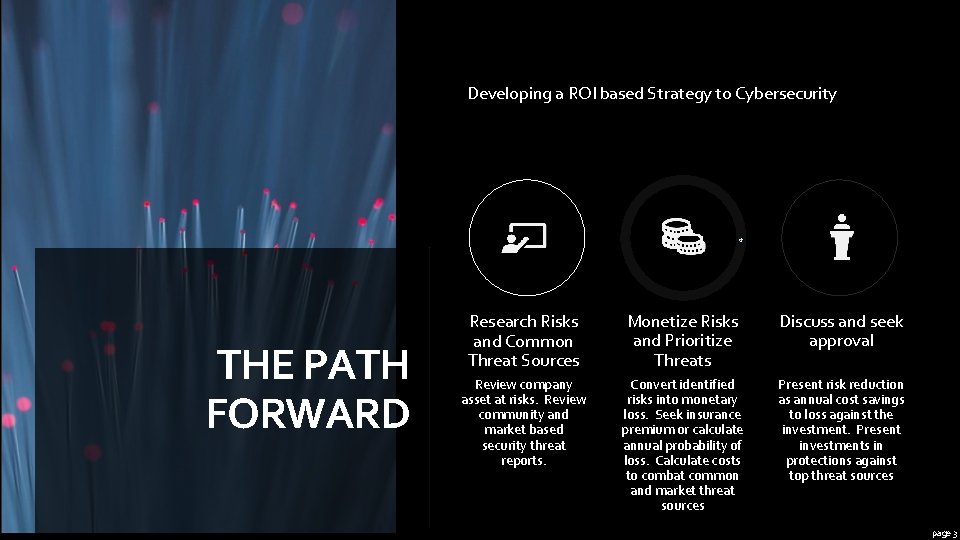
Why Your Cybersecurity ROI Calculations Are Probably Wrong
Most people compute cybersecurity ROI by taking the cost of a tool, subtracting it from the estimated cost of breaches, and calling it a day. That approach produces numbers that look good on paper and fall apart the moment anyone asks for proof. I have spent enough years watching security teams present spreadsheets to boards that nobody actually believes, so I will walk through how this is supposed to work when you stop hiding behind optimistic assumptions. The standard formula is straightforward enough: (Benefits minus Costs) divided by Costs, multiplied by 100. Benefits in cybersecurity usually come from avoided losses, operational savings, and compliance value. Costs include licensing, deployment, staffing, and ongoing maintenance. The hidden part is that most organizations only count the costs and treat the benefits as theoretical. Here is the practical reality. A vulnerability scanner might cost eight thousand dollars annually. If it prevents one breach that would have cost two hundred thousand dollars, your ROI looks like 2400 percent. That number means absolutely nothing unless you can prove the scanner prevented the breach, which you cannot, because the breach did not happen. That is the core problem with cybersecurity ROI measurement. You are calculating returns from events that never occurred, using assumptions that are rarely stress-tested.
I ran into this head-on when a client wanted me to justify a fifteen-thousand-dollar-per-year endpoint detection and response platform. The traditional SLE and ARO method gave us a theoretical annualized loss expectancy that made the tool look like a bargain. The board asked a simple question: what incident would this specifically prevent? I had no concrete answer because the telemetry showed the organization had already been breached three times in two years and the tool would not have caught any of them. The workaround was to stop using pure ROI and switch to a risk reduction framework that measured detection coverage improvement over a ninety-day baseline. We tracked mean time to detect before and after deployment, false positive rates, and incident containment time. The tool itself did not produce a dramatic ROI number, but the operational metrics proved the platform was moving the needle in measurable ways. That story got funded faster than any spreadsheet ever has. The counter-intuitive part that beginners miss is that the most accurate ROI in cybersecurity comes from measuring what you cannot prevent, not what you prevent. Organizations that focus exclusively on breach avoidance inflate their benefit side with hypothetical loss estimates from sources like IBM's Cost of a Data Breach report, which typically cites averages around four million dollars globally. That average is useless for any specific company. A mid-sized manufacturing firm with ten million in annual revenue does not face the same exposure as a multinational bank. Your actual risk calculation should start with your own historical incident data, your industry-specific loss curves, and a realistic assessment of your assets. If you do not have internal incident data, you should collect it for six months before trying to calculate ROI for any new tool. Spreadsheets built on third-party averages get rejected by anyone who knows how finance works. Another thing that trips people up is the treatment of compliance as a benefit. Many teams factor in regulatory fine avoidance as positive ROI. The problem is that fines represent a worst-case scenario that only materializes if you are already in a breach situation and then fail to notify properly. Counting compliance savings as a recurring benefit is double-counting. The compliance value is real, but it belongs in a separate category, not mixed into your primary ROI calculation. I separate it into its own line item and label it clearly as compliance offset rather than return on investment.
Hard costs are usually easy to catalog. Software licensing, hardware, cloud storage for logs, staffing hours for management and tuning, alert fatigue mitigation through SIEM integration, and the inevitable annual price increases from vendors. Soft costs are where budgets get killed without explanation. Training time, policy updates, change management friction, and the productivity hit during the first three months of deployment when analysts are working twice as hard. I always add a twelve percent overhead buffer to every tool budget to account for these hidden operational drag factors. Without it, the ROI number looks too clean and someone will always question it later. There is a specific edge case that breaks most ROI models and deserves attention. When you are evaluating a tool that integrates with existing infrastructure, the integration effort can exceed the tool cost itself. I worked with a team that chose a five-thousand-dollar threat intelligence feed because it appeared inexpensive on paper. The integration required custom API development, log format mapping across three different systems, and two weeks of a senior analyst's time. The total deployment cost landed at twenty-three thousand dollars in the first year. The ROI model they had built assumed a clean plug-and-play deployment and completely missed this. The lesson is to include integration cost as a capitalized expense in year one, not as an invisible overhead. Most ROI calculators do not include this field, which is why real-world results never match projections. When calculating the benefit side, you should use the annualized loss expectancy method rather than single-event estimates. SLE equals asset value multiplied by exposure factor. ARO is the annual rate of occurrence. ALE equals SLE multiplied by ARO. This gives you a dollar figure that represents expected annual loss from a specific threat. When a security control reduces that ALE, the difference between the old ALE and the new ALE is your quantified benefit. This method forces you to be explicit about your assumptions instead of hiding behind vague breach cost numbers.
Get the Full Details
One limitation that nobody talks about is that ROI in cybersecurity becomes unreliable below a certain spending threshold. If your security budget is under one hundred thousand dollars annually, the signal-to-noise ratio in your data is too low to produce meaningful ROI calculations. Tool purchases at that level tend to be tactical replacements, not strategic investments, and the statistical sample size of incidents is too small to draw conclusions. In those environments, you should shift from ROI to risk prioritization using a simple impact versus likelihood matrix. The matrix does not give you a percentage return, but it gives you a defensible way to allocate limited resources. Another scenario where ROI completely fails is when evaluating cybersecurity culture and awareness programs. Training reduces human error, but human error causes approximately seventy-four percent of breaches according to Verizon's DBIR data, and there is no direct causal link you can trace from a training module to a prevented phishing click. The benefit is diffuse, distributed across the organization, and temporally disconnected from the intervention. For these programs, measure completion rates, simulated phishing click rates, and self-reported incident awareness trends. Present those as supporting evidence alongside your quantitative ROI for tool-based controls, not as a standalone return metric. If you want a practical way to build this without getting lost in theory, here is the process I use. First, inventory every security tool and calculate its total annual cost including licensing, staffing allocation, and integration overhead. Second, identify the specific threats each tool addresses and assign a realistic ARO based on your own incident history, not industry averages. Third, estimate the SLE for each threat using your actual asset values and business impact data. Fourth, calculate the baseline ALE for each threat. Fifth, estimate the control effectiveness percentage after deployment based on vendor documentation and independent lab results adjusted for your environment. Sixth, calculate the reduced ALE and derive the annual benefit. Seventh, compute ROI using the standard formula and present a range that accounts for assumption uncertainty.
I keep my models in a single spreadsheet with two tabs. The inputs tab contains every assumption with sources cited inline. The outputs tab shows the final ROI alongside a sensitivity analysis that varies the top three assumptions by plus or minus twenty percent. This shows decision-makers exactly which variables matter most and where your model is most fragile. It also prevents the common failure mode where a single optimistic assumption inflates the entire calculation. The numbers rarely impress anyone in a boardroom unless you frame them correctly. A thirty-five percent ROI on a firewall upgrade sounds weak next to a two thousand percent ROI on a new EDR platform, but the firewall upgrade may be addressing a threat with a higher ARO and lower false negative risk. The apparent disparity in percentage terms hides the actual dollar value at stake. Always include the absolute dollar benefit alongside the percentage. It changes the conversation immediately. There is also a timing issue that distorts ROI. Security tools often show poor performance in the first ninety days during the tuning phase, then improve significantly as analysts learn the alert patterns. If you calculate ROI at month two, you will underestimate the tool's value. I use a twelve-month rolling calculation and explicitly note the ramp-up period in the model documentation. Review the ROI again at month six and month twelve with actual operational data rather than projections. This is the only way to catch the discrepancy between predicted and real performance.
Finally, the biggest mistake is treating ROI as a one-time exercise. It should be recalculated quarterly with updated incident data, adjusted AROs, and current licensing costs. Vendors raise prices. Your threat landscape changes. Tools degrade in effectiveness as detection strategies evolve. A tool that showed a forty percent ROI last year might show negative ROI this year if the alert volume increased without a corresponding increase in blocked threats. The model has to breathe and adapt, or it becomes a static document that nobody trusts.