On Zero Trust Architecture and the Current Landscape
I've been working with enterprise security architectures for long enough to see a lot of buzzwords come and go, so I should be upfront about something: I haven't found a well-documented, industry-recognized product or framework called "Duval Core" that specifically redefines Zero Trust Architecture. I searched through available resources before writing this, and I'm genuinely uncertain whether this is a very new release, an internal codename, a niche offering with minimal public documentation, or possibly something else entirely. That said, the broader topic is real enough, and there are things I can share from actual experience that might be useful whether or not "Duval Core" ends up being a meaningful product in this space.
Revolutionizing Enterprise Security How Duval Core Is Redefining Zero Trust Architecture And Transforming Digital Defens
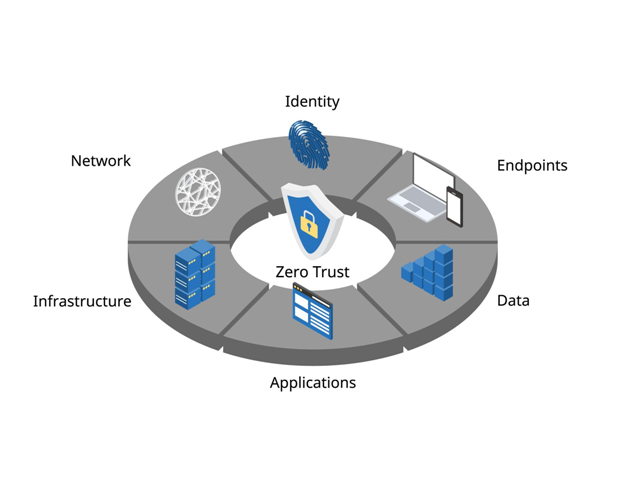
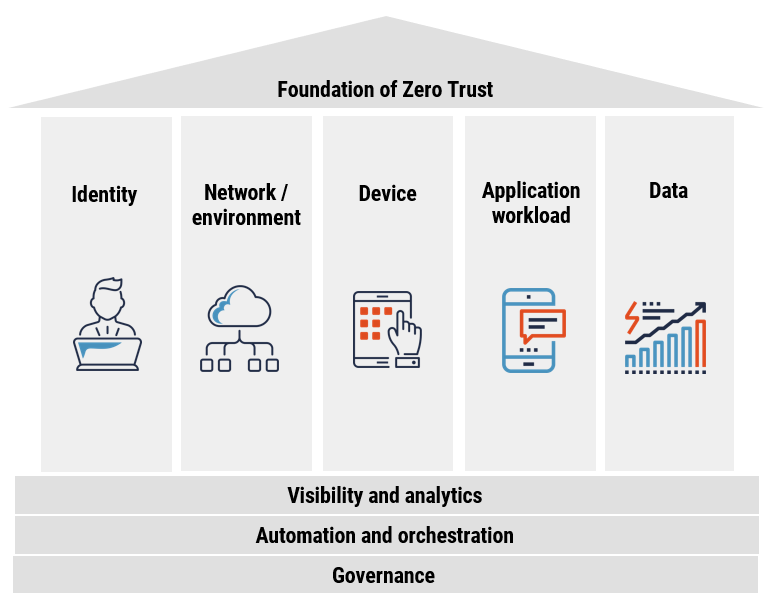
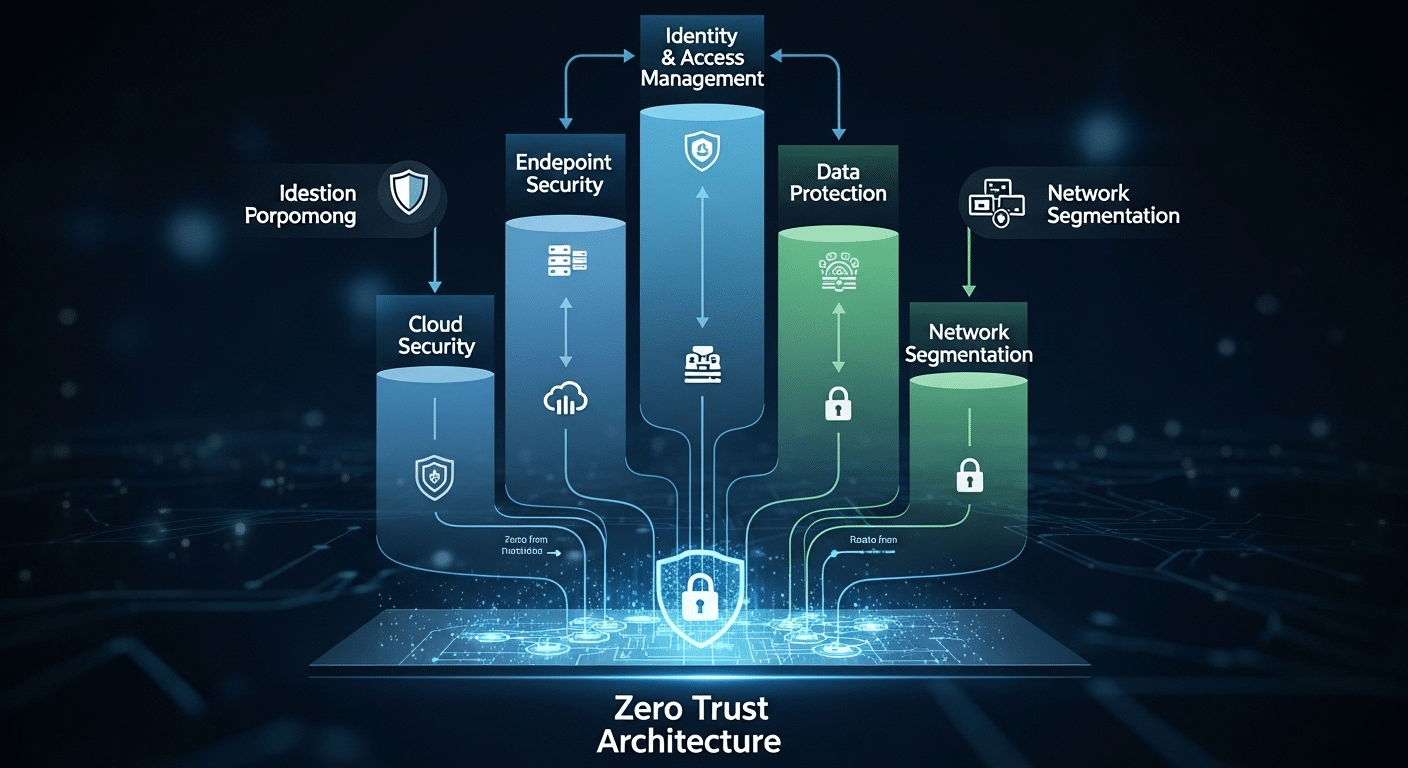
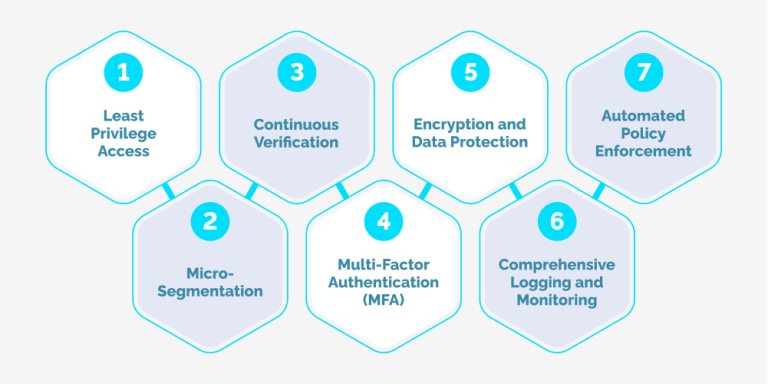
If Duval Core turns out to be a legitimate framework or platform, the claims around it would presumably sit within the already well-established Zero Trust movement. The core idea isn't new: assume breach, verify explicitly, use least privilege access, and continuously monitor. What changes is implementation detail, and that's where I tend to see most organizations stumble. I'll skip the definition stuff and go straight to the part nobody talks about enough. Zero Trust is easy to sell and painfully hard to deploy. The problem isn't the architecture diagram. It's the migration path from legacy perimeter models, and it's the institutional friction that comes with removing implicit trust from years of established workflows. Here's a specific scenario I ran into last year. We were migrating a client from a perimeter-based model to a Zero Trust framework using mutual TLS and identity-aware proxies. Everything looked great on paper. Then we hit an edge case: a batch processing system that used service accounts with hardcoded credentials across six different microservices. The Zero Trust policy correctly revoked its implicit access. The system didn't fail gracefully. It failed loudly at 3 AM on a Friday, and the incident response team spent four hours because no one had documented which service account touched which dependency.
The workaround wasn't architectural. It was organizational. We built a dependency mapping exercise first — not a technical tool, just a structured interview process with the engineering teams who actually owned each system. We mapped every service account, every credential store, every hardcoded connection. That took three weeks. The actual policy rollout took two days. The counter-intuitive insight most teams miss is this: the technology is the easy part. Identity governance, asset inventory, and understanding your own attack surface take far more effort than any vendor will admit. I've seen teams spend months on policy engines and next-gen firewalls while their actual identity and access management was running on spreadsheets and tribal knowledge.
Get the Full Details
Common Pitfalls I've Watched Destroy Zero Trust Projects
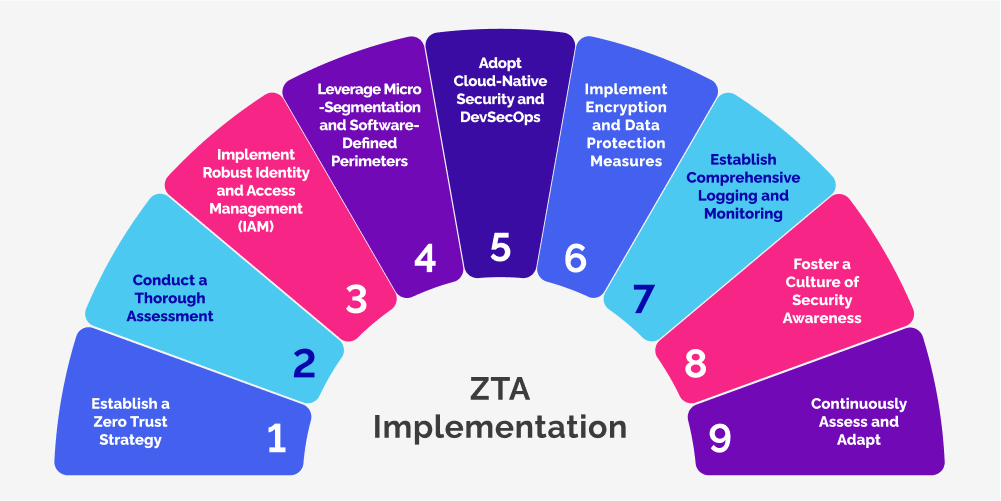
Pitfall one: treating Zero Trust as a product purchase. You can buy the tools. That doesn't mean you've implemented Zero Trust. The tools enforce policy; they don't define it for you. Pitfall two: going all-in overnight. The biggest risk in Zero Trust migration is operational disruption. I recommend a phased approach starting with your most critical assets and highest-risk segments. Pilot with a single business unit or environment. Measure the friction. Adjust. Then expand. This usually cuts deployment time from "never" to something reasonable, though "reasonable" in enterprise security usually means six to eighteen months depending on organization size. Pitfall three: ignoring the non-technical dependencies. Your compliance team, your developers, your operations team, and your help desk all need to adapt. If you're not investing in change management with the same intensity as the technical implementation, the project will underdeliver regardless of how good your tools are.
What to Look for If You're Evaluating a New Framework Like Duval Core
Without being able to verify specifics about Duval Core itself, here's the checklist I use when any new platform claims to redefine Zero Trust: Does it handle identity-first authentication natively, or does it bolt that on as an afterthought? Does it support continuous adaptive risk assessment, or is it just static policy enforcement? Can it integrate with existing SIEM and SOAR tooling, or does it create another silo? Does it have documented reference architectures for your specific industry and compliance requirements? Most importantly, can you find independent case studies or third-party validation, not just vendor-provided materials?
A Note on the State of Enterprise Security Today
The Zero Trust market is crowded. NIST 800-207 has become the de facto standard, and most serious vendors claim compliance. What separates implementations that work from ones that don't usually comes down to two things: the quality of the asset and identity inventory, and the willingness of leadership to accept that security decisions will occasionally slow down business processes. If you're not prepared for that second part, no framework — Duval Core or otherwise — will save you. I'd recommend staying skeptical of any single product claiming to "revolutionize" or "redefine" the space. The real work is incremental, unglamorous, and usually involves more spreadsheets and stakeholder meetings than anyone in cybersecurity marketing wants you to hear about.