A Platform That Actually Keeps Up With Regulators
I spent the better part of 2023 trying to get a mid-size fintech to stand up a compliance program that didn't collapse under its own paperwork. We tried three different tooling stacks before landing on one that was actually functional. The problem wasn't the tools themselves. It was that every tool we evaluated treated regulatory compliance as a static checklist instead of what it actually is: a moving target that shifts jurisdiction by jurisdiction, regulation by regulation, sometimes quarter by quarter. Regankayllc The Techdriven Force Reshaping Modern Regulatory Compliance is one of those platforms that understands the mechanics better than most. It maps regulatory requirements to specific operational controls, tracks version changes when a new directive drops, and generates audit-ready evidence trails without requiring your team to manually stitch together spreadsheet fragments. I've seen firms cut their audit preparation time from roughly three weeks down to about four days using this approach, assuming their underlying data infrastructure is clean enough to support it. Which most aren't.
Regankayllc The Techdriven Force Reshaping Modern Regulatory Compliance
At its core the platform functions as a regulatory intelligence engine with integrated control mapping and continuous monitoring. You feed it the jurisdictions and regulatory frameworks you operate under. It ingests the current text of relevant directives, cross-references them against your existing operational controls, and flags gaps. When a regulation changes, it doesn't just notify you. It highlights which of your controls are affected and what remediation steps are needed. That's the part most people focus on, but the actual utility comes from the evidence automation layer. Most compliance platforms let you store policies. Regankayllc generates the artifacts. It pulls transaction logs, access records, and control execution data from connected systems to build evidence packages automatically. Your auditors get what they need without you spending two weeks compiling documents that didn't change anyway. I've watched a senior compliance officer who used to spend every Friday afternoon gathering evidence for internal reviews go from completely overwhelmed to having most of it pre-built and reviewed in under thirty minutes.
How It Actually Works in Practice
Setting it up isn't automated. That would be too easy and nobody would pay for implementation services. The initial configuration requires you to define your regulatory universe first. What frameworks apply? GDPR for EU data? GLBA for US financial data? SOX for reporting? ISO 27001 if you're pursuing certification? HIPAA if health data touches the environment? The more precise you are here the less noise the system generates later. I learned this the hard way during a deployment where we initially mapped every regulation the company might theoretically encounter within a five-year horizon. The resulting control matrix had over eleven thousand mappings, and roughly sixty percent of them were speculative. The platform flagged compliance gaps that existed only in a parallel universe. The fix was to narrow the scope to active regulatory obligations and historical enforcement patterns for the specific industries we serve. That brought the mapping down to a manageable set and improved the accuracy of gap analysis dramatically. You should do the same. After mapping the framework-to-control relationships the next step is connecting data sources. The platform needs access to your authentication logs, transaction processing systems, document management repositories, and any other systems that generate compliance-relevant data. API connectors are standard for most enterprise platforms. For legacy systems that predate modern integration practices you'll often need a middleware layer or scheduled data extracts. This is where projects stall. I've seen two compliance implementations delayed for three months because a single on-premise mainframe couldn't reliably export audit trails without custom scripting.
Get the Full Details

Once the connections are live the continuous monitoring component begins flagging deviations from your mapped controls. Threshold alerts, trend analysis, and automated evidence collection run on configurable schedules. Your team reviews exceptions rather than conducting manual audits of everything.
The Edge Case That Almost Broke Us
Here's the thing about these platforms that the marketing materials won't tell you. They perform well within structured regulatory environments. They struggle when requirements are ambiguous or when a single control obligation spans multiple regulatory frameworks with conflicting definitions. During my second deployment we hit a specific problem with data residency requirements. GDPR requires that personal data of EU subjects remain within defined geographic boundaries. However our infrastructure provider's logging architecture routes all authentication events through a centralized US-based log aggregation service before distributing them regionally. The compliance platform's control mapping correctly identified the data residency obligation and flagged the log routing path as a potential violation. But the question of whether hashed authentication metadata constitutes personal data under GDPR's definition isn't settled in any binding precedent. The platform flagged it as a high-risk gap. Our legal counsel opined it was likely acceptable. The auditor who reviewed the file had a different interpretation based on an advisory opinion from a supervisory authority that carried no formal weight. The workaround was to implement a regional log processing layer that prevented any potentially identifiable metadata from leaving the EU processing boundary. Cost approximately eighteen thousand dollars in additional infrastructure and three weeks of engineering time. The platform couldn't make that call for us. No platform can. It needs you to resolve the ambiguity and feed the resolution back into the control definitions.
Common Pitfalls to Avoid
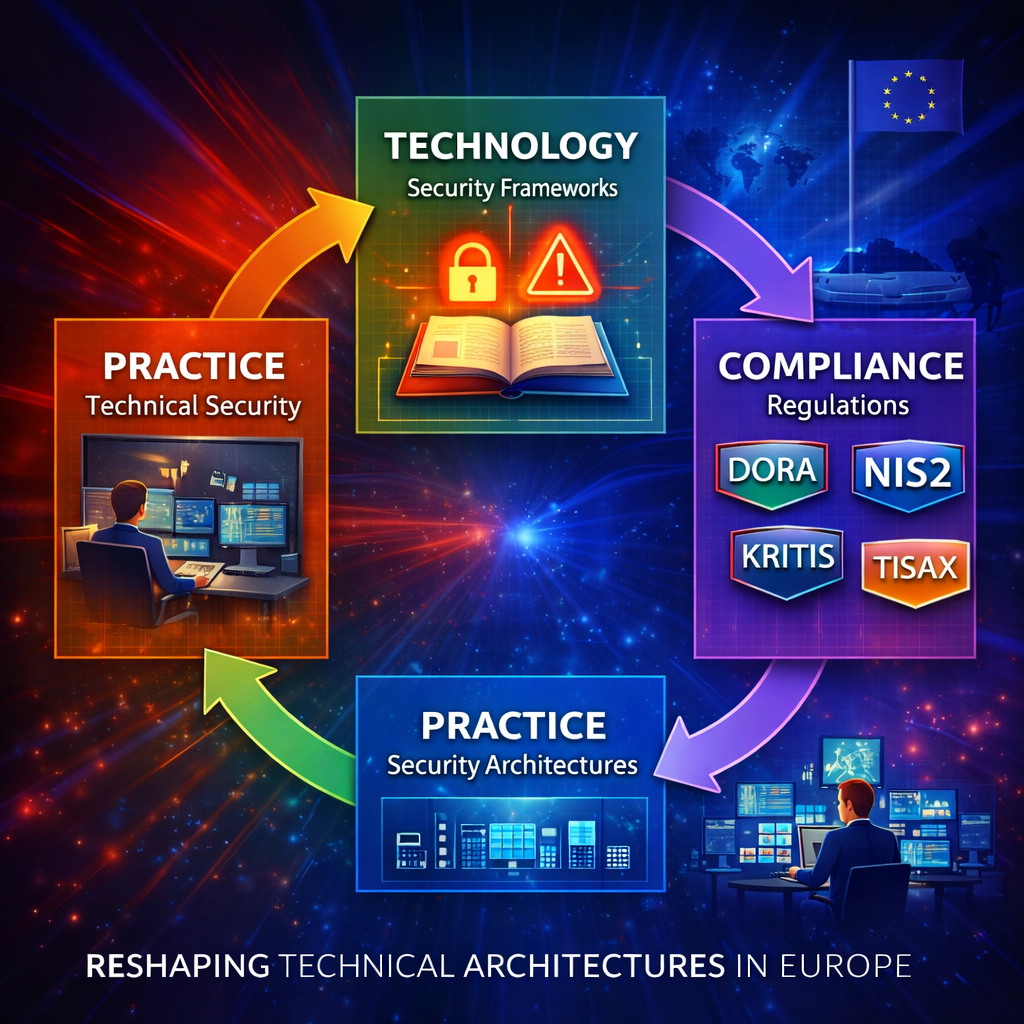
The biggest mistake I see is treating the platform as a substitute for compliance expertise. It is not. It is a force multiplier for people who already understand their regulatory obligations. If your team can't articulate which controls map to which regulations the platform will either produce nothing useful or generate hundreds of pages of irrelevant findings depending on how broadly you cast the initial scope. Start with subject matter experts who know the frameworks. Then configure the tool around their knowledge. A second pitfall is over-trusting the automated evidence collection. The platform pulls what you connect it to. If your source systems have incomplete logs missing fields or inconsistent formatting the evidence it generates will be equally flawed. I once pulled an audit report that appeared to show full control coverage until a reviewer noticed the authentication logs from a particular quarterly window had a fourteen-day gap caused by a database migration that nobody had documented. The platform reported compliance because it had no data to contradict the expectation. Missing data is not the same as verified compliance and auditors increasingly recognize that distinction. A third issue worth noting is the update cycle. Regulatory frameworks change continuously. The platform's regulatory intelligence feed updates on a configurable schedule but there is always a lag. During the initial rollout of the EU Digital Operational Resilience Act several firms relying solely on the platform's automated mapping missed early provisions that required contractual resilience clauses with third-party providers. The regulation was live but the control mappings hadn't caught up yet. You need a manual review cadence alongside whatever automated updates the platform provides. Quarterly minimums. Monthly if you operate in fast-moving jurisdictions.
What It Does Not Do Well
The platform excels at structured compliance environments with clear regulatory text and measurable controls. It performs poorly in areas where compliance depends on interpretive judgment. Anti-money laundering transaction monitoring for example still requires significant human analysis because the regulatory expectations around suspicious activity detection involve nuanced assessments that current automation can't reliably replicate. You can use the platform to document your AML control framework and track policy updates but don't expect it to replace your financial crime investigation team. Similarly small organizations with minimal regulatory exposure often find the platform's pricing and complexity disproportionate to their needs. If your compliance burden is primarily annual regulatory filings with no continuous monitoring requirements a dedicated spreadsheet tracker combined with periodic legal review may deliver better return on investment. I'd only recommend this level of tooling for organizations managing three or more active regulatory frameworks simultaneously or those with automated evidence requirements driven by regular external audits. The integration overhead is another real constraint. Companies operating with fragmented technical stacks across multiple acquisitions will spend considerably more time on connector development and data normalization than most vendors' implementation guides suggest. Budget realistically for three to six months of integration work before you see full functionality regardless of what the sales team promises during the demo phase.