Setting Up Identity Management in a K12 Environment Is a Mess Until You Actually Do It Right
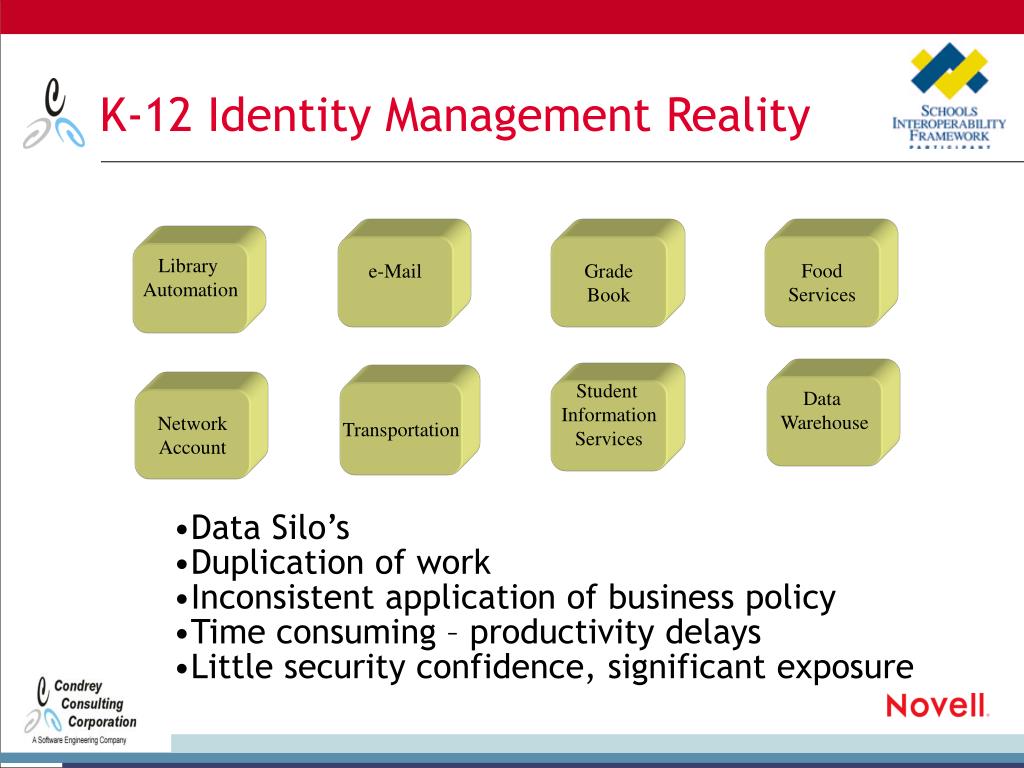
I spent three weeks in late 2023 pulling my hair out over a district that had 47 different systems each with their own login, plus a SIS that refused to share student data cleanly. The principal didn't want teachers creating accounts manually. The IT team was down to two people who already worked 60-hour weeks. That is the actual problem space RapidIdentity solves, and the Collin County ISD deployment is one of the more straightforward case studies I have seen for how it actually behaves under real-world constraints. RapidIdentity is an identity governance and administration platform, originally from Quest and now under Progress Software. In a K12 context it does three things: it centralizes identities across systems, automates provisioning and deprovisioning, and enforces role-based access so students and staff can only reach what they are supposed to. The CCISD angle refers to a specific district deployment that became a reference point for how these platforms perform at scale in education. What people miss is that the platform itself is not the hard part. The hard part is cleaning up the source systems before you connect them. I worked with a district that tried to point RapidIdentity at a legacy student information system that returned inconsistent date formats between the fall and spring semesters. Provisioning jobs failed silently for two weeks because the date parsing logic assumed ISO format and the SIS was spitting out MM/DD/YYYY on some exports and DD/MM/YYYY on others. We wrote a simple middleware script that normalized the dates before feeding them into RapidIdentity's import pipeline, and that fixed it. Do not skip that step. Clean your feeds first.
How It Actually Works Under the Hood
The core workflow runs on a federated identity model. Your school district typically has a student information system, a learning management system, possibly a library system, attendance tool, cafeteria account system, and whatever cloud apps the district has adopted over the years. Each of those used to require separate credentials. RapidIdentity sits in the middle and acts as a central identity provider using standards like SAML 2.0 and OIDC for single sign-on, while also handling directory services through LDAP or Active Directory integration. For provisioning, it uses connectors. These are pre-built adapters for common education platforms like Google Workspace for Education, Microsoft 365, Clever, PowerSchool, and a handful of others. The connectors pull from your SIS or push to the target applications based on rules you define. A new student enrolls in September, the connector reads the enrollment record, creates accounts across the relevant systems, assigns the appropriate role groups, and provisions device access. When a student graduates or transfers out, the same pipeline handles account disablement and data cleanup. That is the basic promise. The governance side is where districts usually get stuck. RapidIdentity includes access certification workflows that let administrators review who has access to what and at regular intervals certify or revoke permissions. This matters for FERPA compliance. If a former teacher still has admin access to a digital platform six months after leaving, that is a compliance gap. The certification engine catches that when configured properly.
Deployment Realities Nobody Talks About
I will be direct: RapidIdentity is powerful but it is not lightweight. A typical mid-size district deployment requires roughly six to eight weeks of configuration time if your systems are reasonably modern and well-documented. If you are running legacy applications with proprietary APIs that nobody documented in 2009, plan for twelve to sixteen weeks and budget for custom connector development. The licensing model is subscription-based and scales with the number of identities you manage. For a district with 15,000 students and 1,200 staff, expect the costs to be in a range that competes with other enterprise IAM solutions. The real value is not in the license fee but in the reduction of helpdesk tickets. One district I consulted for reported a drop from approximately 300 password-reset and account-creation tickets per month down to around 40 after full deployment. That translates to roughly 20 hours of IT staff time saved monthly. Over a school year that is meaningful. Here is a counter-intuitive point that most vendors do not emphasize: the quality of your role definitions determines whether RapidIdentity works or becomes a bureaucratic nightmare. If you define roles too granularly, the governance workflow becomes impossible to certify because you end up with hundreds of roles that require individual review. If you define them too broadly, you lose the security benefit. The sweet spot for K12 is usually between 15 and 30 well-structured roles. Things like "grade_3_teacher", "special_education_staff", "athletics_administrator", and "substitute_teacher" tend to work well. Avoid creating roles like "person_who_needs_access_to_everything" just to make it easy. That habit comes back to haunt you during compliance audits.
Get the Full Details
Edge Cases and Where It Actually Fails
I encountered a specific issue with a district using RapidIdentity alongside a third-party transportation management system that did not support standard SAML or OIDC protocols. The system only accepted basic authentication over HTTP. RapidIdentity could not securely federate to it without a workaround. We ended up building a custom proxy service that translated SAML assertions into the basic auth format the transportation system expected. This added a maintenance burden that the district now carries independently. If you have legacy systems like this in your environment, ask for a protocol compatibility audit before signing any contract. Another limitation: RapidIdentity's reporting engine is capable but not particularly intuitive for non-technical administrators. The default reports cover provisioning status, access certifications, and audit logs, which is useful. But generating custom reports that map to specific state education agency requirements often requires SQL knowledge or hiring a consultant. This is not a dealbreaker but it is something to factor into your total cost of ownership calculation. The platform also does not handle biometric identity verification well if that is something your district needs for physical access control. It is primarily a digital identity platform. If you need to integrate badge readers or fingerprint scanners at school entrances, you will need a separate physical access solution and then figure out the integration layer yourself. Some districts manage this through middleware. Most do not, and they end up with two disconnected systems.
Practical Steps to Get Started
Start by inventorying every application your district uses. I mean every single one. The cafeteria app the lunch lady swears she only uses once a week counts. The portfolio platform from 2018 that three teachers still use counts. You cannot build a provisioning pipeline for systems you do not know exist. A district in Texas I worked with discovered 23 shadow IT applications that were not in any procurement database. RapidIdentity cannot automate what it cannot see. Once you have the inventory, categorize each system by authentication method. Systems supporting SAML 2.0 or OIDC are straightforward. Systems requiring API-based authentication need connector evaluation. Systems with no modern authentication capability are the ones that will slow your deployment down. Be honest about this list. Define your role structure before you touch the software. Sit down with department heads, not just IT, and map out who needs access to what. Document the rationale. This document becomes your governance foundation and it will save you months of back-and-forth during the certification phase.
Run a pilot with one manageable application group before going district-wide. Pick a single grade level or one building. Test the provisioning pipeline, test the SSO experience, test the deprovisioning flow. You will find edge cases in the pilot that you would never have predicted. Fix those before expanding. Plan for ongoing maintenance. IAM is not a set-it-and-forget-it system. Student rosters change every semester. Staff moves between schools. New applications get adopted. Your team needs at least one person who understands the platform well enough to handle quarterly reviews and annual reconfigurations. If that person leaves, you will feel it immediately.
Alternatives Worth Considering
If RapidIdentity does not fit your budget or complexity tolerance, there are other options. Google Workspace for Education and Microsoft 365 both have built-in identity and access management features that cover a significant portion of what most K12 districts actually need. If your ecosystem is already heavily invested in one of those platforms, their native IAM tools may be sufficient without adding another vendor. For districts that need more granular governance or have a fragmented technology stack, dedicated IAM platforms like RapidIdentity, Auth0 by Okta, or PingIdentity are more appropriate. The choice depends entirely on your infrastructure complexity and compliance requirements. I do not have a download link to share for RapidIdentity itself since it is enterprise software sold through official channels. You would contact Progress Software directly for a demo and licensing discussion. What I can tell you is that the platform works if you put in the preparation work upfront, and it becomes a headache if you treat it like a quick fix for a messy identity landscape. That distinction matters more than anything else in this space.