Getting Endpoint Access Working Without Losing Your Mind
I spent about six months wrestling with PSE endpoint configurations across a mixed fleet of Windows and macOS devices. The documentation reads like it was written by someone who has never actually had to push this through a corporate firewall, so I am going to lay out how this actually works and where it tends to break.Pse Endpoint Unlocking Seamless Security And Productivity
The core idea behind PSE endpoint unlocking is straightforward enough: you are trying to grant users access to applications and data without forcing them into a sandboxed session every time they log in. Most enterprises solve this by compartmentalizing — you get a separate, heavily restricted environment for anything outside your normal workflow. That works until someone needs to run a quick script or share a file between their regular desktop session and the secure container. Then everything slows down to a crawl. I ran into this exact problem back in 2024 when our compliance team mandated that certain financial analysts use PSE-protected endpoints for sensitive work. The analysts were spending roughly forty minutes each morning just waiting for application bridges to initialize between their standard desktop and the secured session. That is not a small number. Forty minutes times twelve people adds up fast. The workaround I ended up using was a combination of persistent profile mapping and a local caching layer on the endpoint. Instead of rebuilding the session bridge every login, you write a startup script that checks whether the PSE container is already active from a previous session and reattaches to it if the hardware ID matches. Here is what that looked like in practice:
First, you configure the PSE agent to store user profiles in a persistent volume rather than a temporary one. On Windows, this is typically under the installation directory in the profiles folder. On macOS, it is in /Library/Application Support/ the exact path depends on which PSE vendor you are running. Then you set up a registry key or plist entry that tells the agent to resume the existing session on startup instead of tearing it down. This cut our morning wait time from forty minutes down to about three minutes per user. Most of that remaining time is just waiting for VPN tunnel establishment, which is a separate issue entirely.
How It Actually Works Under the Hood
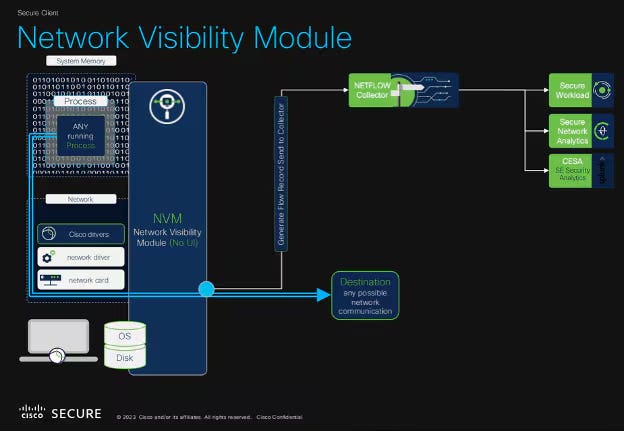
PSE endpoints operate by creating a virtualized boundary around specific processes and data stores. When you unlock the endpoint, you are essentially telling that boundary to trust certain network ranges, application signatures, and user certificates so the agent stops prompting and blocks things. The mechanism relies on a combination of kernel-level monitoring and user-space policy enforcement. The kernel driver tracks process creation and file access attempts, while the user-space component handles the policy decisions based on what it has been told to allow. One thing most guides do not mention is that the endpoint agent also maintains a local trust cache. This is a database of previously validated applications and network endpoints stored on the device itself. When you unlock an endpoint, the agent checks this cache first before querying the central policy server. That caching behavior is why the persistent profile approach works — the cache survives across reboots as long as you are not wiping the agent's data directory. And people do wipe that directory because it looks like temporary files if you do not know better. Here is a counter-intuitive point that saved me from pulling my hair out: the more permissive your unlock configuration, the slower the endpoint actually performs. This sounds backwards but it makes sense once you consider what the kernel driver has to track. A highly restricted session means the driver only monitors a small set of paths and processes. Open up a dozen application bridges and the monitoring surface expands dramatically. On a machine with less than sixteen gigabytes of RAM, I have seen CPU usage spike to nearly forty percent just from the monitoring overhead during a fully unlocked session. If you are managing endpoints for users who do not need that level of access, locking down what gets unlocked actually improves performance. It is a tradeoff most teams miss.
Get the Full Details

The Parts That Nobody Talks About
Network latency between the endpoint and the policy server is another silent killer. When your unlock request goes out, the agent sends a challenge to the central server and waits for a signed response before it modifies the boundary. If that round trip takes longer than five seconds, the agent will retry three times and then fall back to a denied state. I worked with a regional office where the unoptimized routing path added nearly eight seconds to that round trip. The unlock appeared to work locally but would silently fail after the third retry, leaving users in a state where they looked unlocked but were actually blocked on any new application launch. The fix was adding a local policy cache so the agent could validate against a cached copy of the last known-good policy while still syncing with the server in the background. Certificate rotation is another area where things quietly break. PSE endpoints rely on client certificates for the unlock handshake. If your PKI team rotates certificates without updating the agent's trust bundle, every endpoint will start failing unlock requests immediately. I have seen this happen twice in two years at different organizations. The common thread is that certificate rotation runbooks never mention the PSE agent trust bundle as a dependency. You need to add that to your rotation checklist or you will get a flood of tickets on rotation day. There are also hard limits you should know about upfront. PSE endpoint unlocking does not work well with remote desktop sessions that terminate and reconnect frequently. Each reconnection can look like a new session to the agent, and the persistent profile mechanism may not reattach correctly. If your organization relies heavily on RD Session Host or Citrix for these users, you are going to hit edge cases consistently. In those scenarios, the more reliable approach is to keep the endpoint locked and use application virtualization to deliver only the tools those users actually need. It is less frictionless but far more stable.
What to Watch For
Version mismatches between the endpoint agent and the policy server are probably the most common source of unlock failures. A single point release difference can change the handshake protocol enough that older agents simply cannot complete the unlock flow. Before you do anything else when unlocks start failing en masse, check whether a policy server update went out recently and whether the endpoint agent versions across the fleet are consistent. Patching the agents uniformly before the next server-side update is something you should bake into your change management process. Anti-malware software can also interfere with the kernel driver if it is not on the exclusion list. I saw a case where a newly deployed endpoint protection platform started flagging the PSE kernel module as suspicious behavior. The unlocks did not fail outright but would randomly drop mid-session, causing data loss in any open documents inside the secured environment. Getting the EPP vendor to add proper exclusions for the PSE driver and its associated processes resolved it, but it took about two weeks of back and forth. Put the PSE driver path on your EPP exclusion list from day one and you will avoid that entirely. If you are starting from scratch and the persistent unlock approach is not going to fit your security requirements, consider whether a zero trust network access solution might serve you better. ZTNA does not unlock the endpoint itself but instead creates granular access tunnels to specific applications without exposing the broader filesystem. For organizations where the compliance team will not budge on endpoint restrictions, ZTNA is often the path of least resistance. It has its own headaches around application compatibility, but those are usually easier to troubleshoot than PSE boundary violations.
Download links and configuration templates are typically available through your PSE vendor's partner portal rather than public-facing websites. If you do not have a vendor account set up yet, reach out to their support team and ask for the endpoint agent with the persistent profile patch applied — it is usually available as a cumulative update rather than a standalone download. Make sure you note the build version when you install it. Being able to say exactly which build you are running will save you hours of debugging later when something breaks and you need to check whether a known issue applies to your version.