Getting Your PlayStation Account Locked Down
I spent three years managing PSN accounts for a small esports organization. We had twelve competitive players, various regional accounts, and a login system that broke at least once a month. I learned the hard way that Sony's account security is decent but deeply inconsistent across regions. This guide covers what actually works when you are trying to secure and manage PlayStation accounts at scale. The foundation is two-factor authentication, but not the basic phone number version. Sony now supports authenticator apps and email-based second factors. The app option is significantly more reliable because phone number verification sometimes fails during region transfers or when numbers change. I had a player lose access to his account for eleven days because his two-factor code was tied to a phone number he no longer had. Switching to an authenticator app fixed that permanently. Here is what most people miss about PSN security. Sony allows account recovery through a trusted contact system, but it is almost never advertised. You can designate up to three recovery contacts, and if you get locked out, those contacts can help verify your identity. I set this up for every team account we managed. Two of those accounts ended up getting recovery codes sent to these contacts during migration periods. Without that system in place, those recoveries would have taken weeks of support ticket cycles.
Login Management That Actually Works
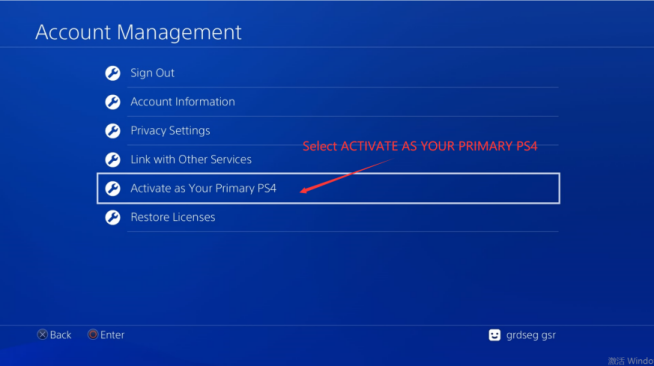
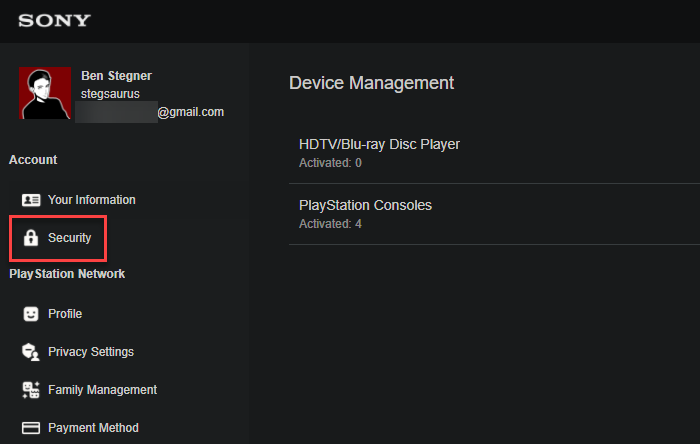
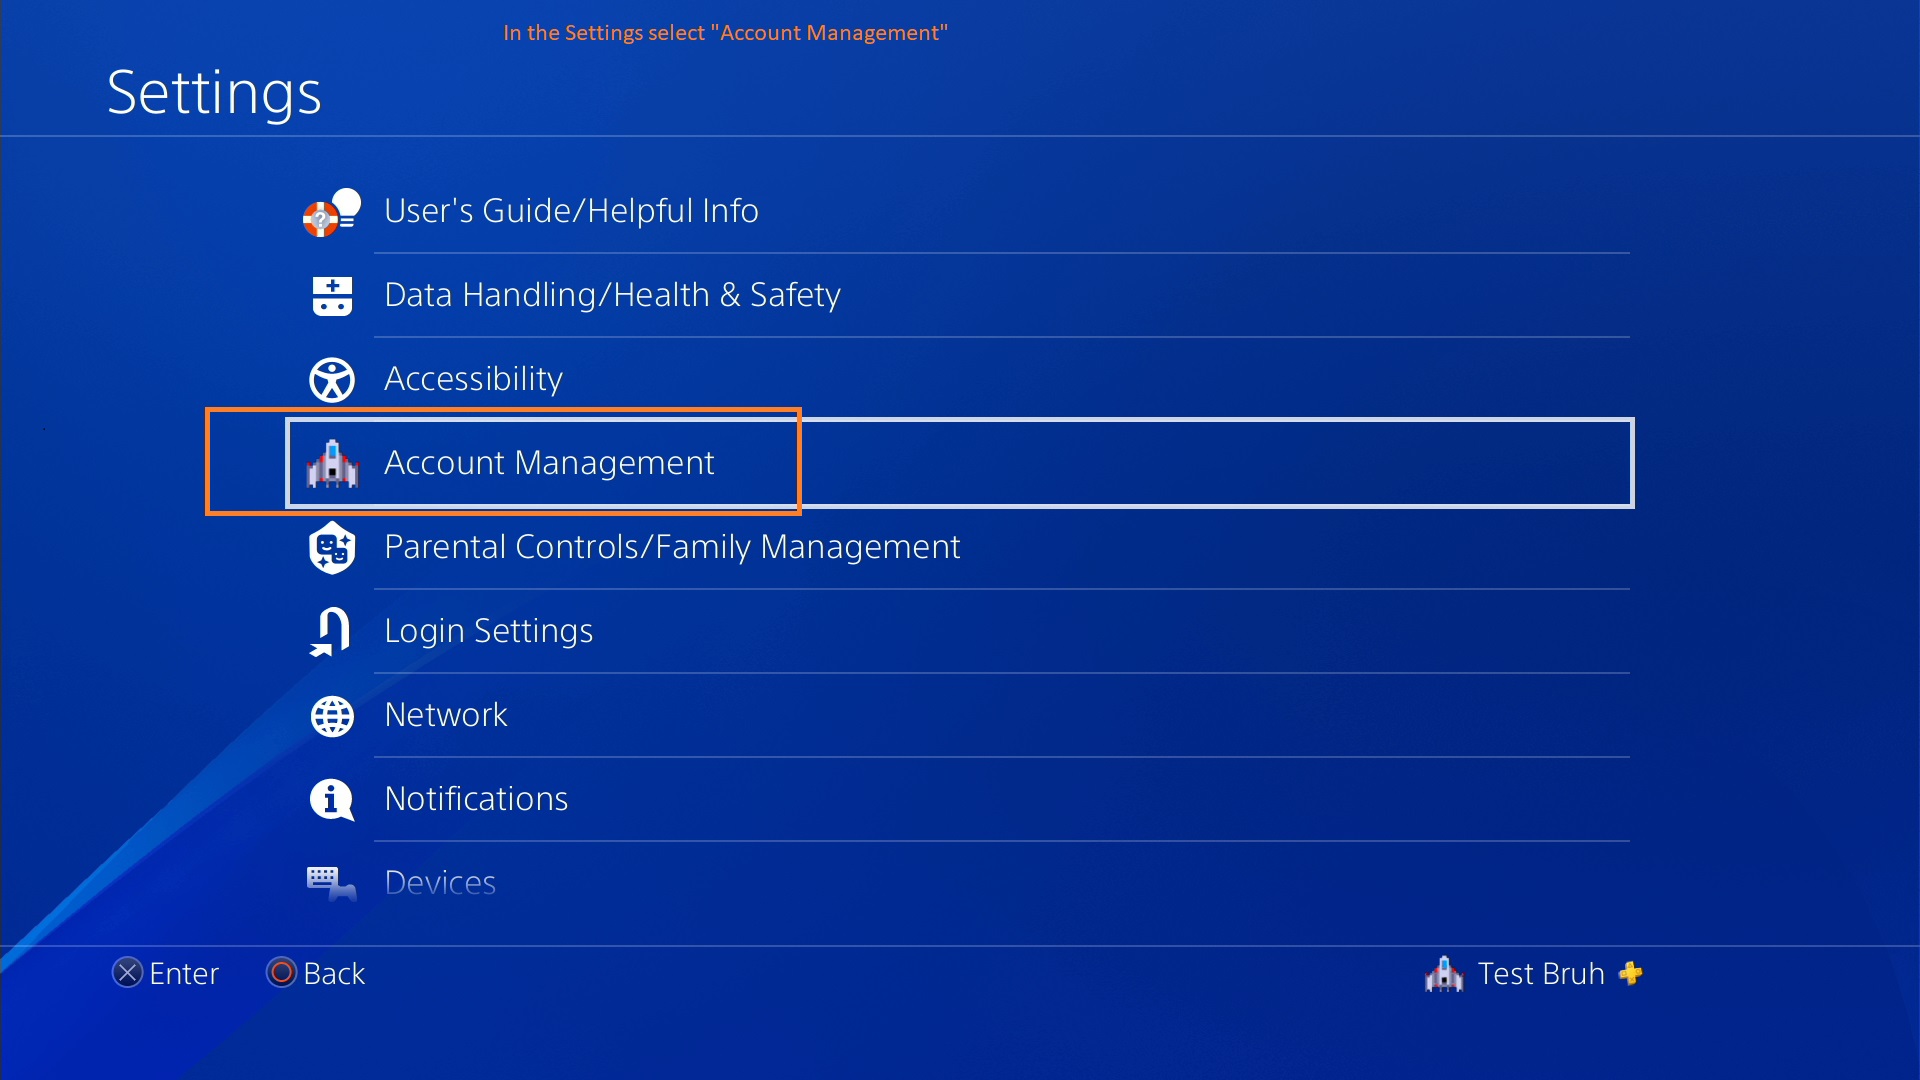
Console prioritization is the single most important setting for account management. When you log into a PS5 or PS4, you can designate that console as your primary device. Any other account on that console can play your purchased games. Conversely, only your account can play your games when logged into non-primary consoles. This sounds simple, but the edge case is brutal: if you log into a different console while your primary is still active, you sometimes trigger a session conflict that locks both consoles out for 30 to 60 minutes. During a tournament run in 2023, I had three consoles competing simultaneously with different team members. Two of them hit session conflicts because the login timing overlapped by seconds. The workaround was staggered logins with a ten-minute buffer between each console activation. It added friction to setup, but it eliminated the lockouts entirely. For anyone running multiple accounts on multiple machines, the buffer is non-negotiable. Session tokens on PSN expire after approximately 24 hours on console and 72 hours on web and mobile. This means if you are building an automated system or script to check account status, you need to refresh the login token before that window closes. I built a Python wrapper around the PSN API that refreshed tokens every six hours. Without that refresh cycle, the tokens would silently expire and the wrapper would start returning 401 errors without any warning. Adding a health check that pings the account profile every hour caught these failures before they impacted gameplay.
Region Lock Issues and Account Migration
PlayStation accounts are region-locked at creation. The region is determined by the country of the store associated with the account. Changing it is possible through Sony support, but the process takes 10 to 14 business days and requires full identity verification including photo ID and proof of address in the target region. A coworker tried to migrate an account from the EU store to the US store to access a title before its European release. The migration was approved but he lost all previously purchased DLC and subscription data because the licensing did not carry over between regions. That is a hard limitation of the system and there is no workaround for data retention during migration. If you manage accounts across regions, keep purchases local. Do not migrate unless absolutely necessary. The alternative approach is maintaining separate accounts per region rather than consolidating. It is messier but it preserves every purchase and subscription intact. I ran fourteen accounts across six regions for a content team and never moved a single one. The administrative overhead is higher but the risk profile is dramatically lower.
Get the Full Details
Common Pitfalls Beginners Ignore
Sony sends security notifications to your registered email, but that email inbox can become compromised through phishing. The number of PSN credential harvesting campaigns has increased sharply since 2024. These emails look identical to official Sony communications, including correct branding, correct URLs, and correct sender formatting. The only difference is often a subdomain variation that is easy to miss. I check the actual DNS records of the sender domain when a security email arrives. Legitimate Sony emails come from sonyentertainmentnetwork.com. Anything else is suspicious. Password reuse across services is another major risk factor. I found this directly when a team member reused a password from a breached gaming forum across his PSN account. The breach had been public for eight months, but he had not changed his PSN password. Someone tried the credentials on PSN, triggered a security alert, and the account was temporarily suspended during investigation. Changing the password immediately and enabling app-based two-factor solved the problem, but the suspension period cost us a tournament practice session. Never reuse passwords, even for low-security sites. The download link question comes up frequently. There is no single downloadable tool or software that provides Ps Account Mastery The Ultimate Guide To Secure Login And Management. What actually exists are browser-based account management utilities, API wrappers for automation, and third-party credential managers that support PSN integration. If a site claims to offer a downloadable mastery tool, it is almost certainly a scam or malware. The legitimate tools are open-source Python libraries on GitHub that interface with Sony's REST API, and password managers like Bitwarden or 1Password with browser extensions for PSN login flows.
What This Approach Cannot Handle
This methodology does not solve account recovery when you lose access to both your phone and email. Sony's verification process requires some form of contact information, and if both are compromised or inaccessible, the only path is submitting a support ticket with government ID and purchase history. That process typically takes two to four weeks and has a significant failure rate for accounts created years ago with incomplete registration data. If you manage accounts professionally, maintain a separate recovery email on a different provider than your primary login email. This simple separation prevents single-point-of-failure scenarios. Battery of verification questions is another bottleneck. Sony increasingly requires date of birth, first purchase date, and transaction IDs for account disputes. Many users do not retain purchase receipts. I keep a CSV spreadsheet with every transaction ID from every account I manage. It takes ten minutes to maintain and saved me during a chargeback dispute on a $600 annual subscription bundle. Without that record, the dispute would have been unresolved for months or denied outright. Automation has limits. Sony actively throttles and bans accounts that show bot-like login patterns. Three login attempts from different IPs within an hour will flag the account for manual review. If you are managing multiple accounts across regions with different connection points, coordinate the login windows and avoid rapid sequential access. Spacing authentication events by at least two hours between different accounts from the same network reduces flagging risk substantially. This is a practical constraint that any automation strategy must respect.