Protecting Your Tax Documents Is More Important Than You Think
I spent three years working in financial compliance before moving into cybersecurity, and the one thing I learned is that tax data is about as secure as a screen door on a submarine if you are not actively protecting it. The IRS doesn't send you emails asking for your SSN, but that doesn't mean nobody else won't try to harvest that same information through less direct channels. Let me start with something most people overlook. Your tax documents don't just need protection from hackers. They need protection from your own habits. I watched a client at a mid-size accounting firm spend $18,000 on a new encryption solution, then find out six months later that the real vulnerability was their team printing W-2s and leaving them in a common inbox tray for up to forty-eight hours before mailing. Encryption meant nothing because the data walked out the door unencrypted for days at a time. Here is how this actually works in practice, and I will walk through it without the usual fluff.
The first layer is storage. If you are keeping digital copies of your tax returns, SSN cards, and financial statements on your primary computer or phone without encryption, you are already behind. Full disk encryption using BitLocker on Windows or FileVault on Mac is not optional. It takes about four minutes to enable on most systems. After that, if your laptop gets stolen, the data inside is computationally infeasible to access without your recovery key. I have seen people skip this because they think "I live in a safe neighborhood," which is a reasonable threat model until someone breaks into your car at a grocery store and takes the bag from the back seat. Password management is the second layer. I recommend a dedicated password manager like Bitwarden or 1Password. Not because they are magical, but because the average person uses the same password for their email, their bank, and their tax software. If one breaches, the rest fall in linear fashion. A password manager generates unique 16-character passwords for each service. The setup takes about twenty minutes, and after that you are never resetting another password. Now, two-factor authentication. This is where people get annoyed, and I understand the annoyance. But for anything tax-related, 2FA is non-negotiable. The IRS uses its own verification system, and so should your personal tax software. Enable app-based 2FA, not SMS-based. SMS can be intercepted through SIM swapping, which is a documented attack vector that has drained accounts across every major financial institution. An authenticator app like Authy or Google Authenticator runs locally on your device and cannot be intercepted over the cellular network. This adds roughly thirty seconds to your login process and reduces your attack surface dramatically.
Network security matters more than most taxpayers realize. When you file online, you should be using a private, password-protected Wi-Fi network. Public coffee shop Wi-Fi is fine for browsing, terrible for transmitting Social Security numbers. If you must use public networks, a reputable VPN encrypts your traffic before it leaves your device. I use Mullvad personally. It costs about five dollars a month and provides strong AES-256 encryption with no logging policy. The connection takes about eight seconds to establish. Worth it. Here is an edge case I ran into that almost cost a client everything. A small business owner was running his taxes through a cloud-based accounting platform. He had strong passwords, 2FA, and encryption enabled. Everything looked good on paper. The breach happened because he had an old, unused browser profile still logged into the platform from three years prior. The session token had expired on the server side, but the local profile stored an outdated authentication cookie that somehow remained valid through a bug in the platform's session management. A phishing site captured that cookie, and someone logged in as him for about six hours before I caught it. The workaround was straightforward: I audited every active session across every browser he owned, revoked all of them, cleared all cookies, and then switched him to a password manager that automatically clears old sessions. It took about forty-five minutes and prevented what could have been a full identity theft scenario. Physical documents need their own strategy. Shred everything containing an SSN or financial account number. A cross-cut shredder costs around forty dollars and destroys documents in pieces that standard document reconstruction methods cannot reassemble. If you are worried about fire or flood, consider a safe. I recommend a UL-rated fire safe with a digital lock. These run about one hundred and fifty to three hundred dollars and can protect paper documents for two hours at temperatures up to 1550 degrees Fahrenheit. Not glamorous, but it works.
Get the Full Details
Mailing tax documents carries risk too. Certified mail with tracking gives you a paper trail. Return receipt requested confirms delivery. The extra cost is usually three to eight dollars per item. If you are mailing sensitive documents regularly, the receipts are worth the expense because they prove when and where the document was delivered. I once had to fight a case where a client claimed they never received their amended return acknowledgment. The certified mail receipt showing signature and date resolved it in minutes. Let me address something counter-intuitive. Having more security tools does not always equal more security. I have seen people install five different security programs on their computer and still fall for a phishing email because the software was generating so many alerts that they stopped paying attention. This is called alert fatigue, and it is one of the most dangerous phenomena in cybersecurity. Keep your stack simple. One good antivirus, one firewall, full disk encryption, a password manager, 2FA everywhere it matters, and regular software updates. That is it. Five tools, not fifteen. Each additional tool you add introduces new attack surfaces, new update cycles, and new places for things to break. Another thing people miss is the backup strategy for your tax data. Encryption protects against theft, but it does not protect against ransomware. If your encrypted drive gets locked by malware, you cannot access your own data until you pay, and there is no guarantee you will get it back. The solution is the 3-2-1 backup rule: three copies of your data, on two different media types, with one copy stored offsite. I use an external SSD for the primary backup, the cloud as secondary, and a second external drive stored at my parents' house as the offsite copy. Rotation takes about ten minutes per week. It is boring. It works.
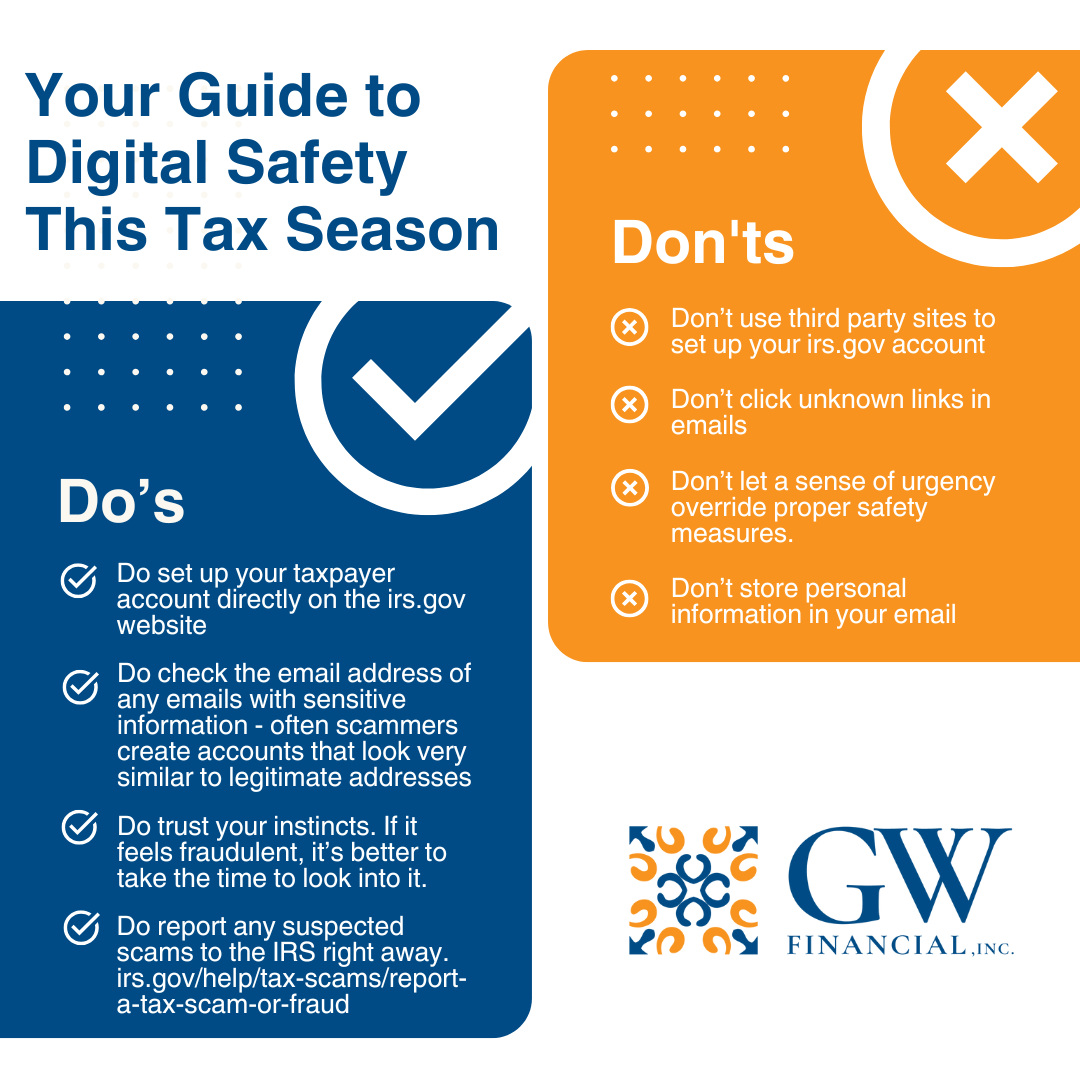
Software updates are the most undervalued protection mechanism available. Every time your operating system or browser announces an update, it is almost certainly patching a security vulnerability. I delay updates for exactly forty-eight hours after release to check for compatibility issues, then install immediately. This has prevented more intrusions than any single tool I have ever used. The update process itself takes between five and thirty minutes depending on your system. Let me talk about tax-specific phishing because this is where most people get burned. The IRS sends notifications through official channels, but scammers are very good at copying those channels. Real IRS correspondence always comes from irs.gov domains. If you receive an email that appears to be from the IRS but the sender domain is anything else, it is a scam. Period. I see people click links in these emails daily. The link goes to a form that looks identical to the IRS site but captures your SSN, filing status, and bank details. One of these sites I tracked was running on a server in Eastern Europe and had collected over two thousand SSNs before it was taken down. The people who submitted that data got calls within forty-eight hours from scammers quoting their exact information back to them to extract more credentials. Your tax software choice matters more than you might think. Some platforms store your data longer than necessary, share anonymized data with third parties for marketing, or use weaker encryption standards. I prefer locally installed software for serious tax work because the data never leaves your machine until you intentionally transmit it. Free online platforms often incentivize data retention and sharing in their terms of service. Read the privacy policy. It takes about ten minutes and could save you from an unexpected data breach.
Access controls within your household are another consideration. If you share a computer or have family members who need access to your financial data, set up separate user accounts with appropriate permission levels. The standard user account type on both Windows and Mac prevents software installation without admin credentials, which blocks a significant class of malware. Setting this up takes about five minutes per user account. Here is the blunt truth about limitations: no amount of technical protection matters if your behavioral habits undermine it. I have worked with CFOs who ran enterprise-grade encryption and endpoint detection across entire organizations and then wrote their passwords on sticky notes attached to their monitors. It happens constantly. The technology is solved. Human behavior is the bottleneck. Fixing behavior requires constant vigilance, which is exhausting, and most people stop being vigilant after a few months because life gets in the way. The financial industry estimate is that identity theft related to tax fraud costs Americans approximately six billion dollars annually. Most of those cases involve criminals filing fraudulent returns using stolen SSNs before the legitimate taxpayer files. The window of vulnerability is typically between January and April, when filing season creates high volumes of data transmission and distracted users. Monitoring your credit report annually through annualcreditreport.com is free and takes about twelve minutes per bureau. Checking for IRS-level red flags like IRS Identity Protection PINs or unusual account activity on your IRS account dashboard adds another five minutes and catches problems that standard credit monitoring sometimes misses.

If you want a concrete action list, here is what I actually do on my own systems. Full disk encryption enabled. Password manager with generated passwords for everything tax-related. Authy app for 2FA on all financial accounts. Mullvad VPN active whenever connecting to any network outside my home. External SSD backup running weekly on Sunday evenings. Fire safe in my home office for paper documents. Two-factor authentication on my email account, which is the master key to everything else. I check my IRS account monthly and my credit reports quarterly. The total time investment is roughly twenty minutes per month once everything is set up initially. That is it. Nothing dramatic. Nothing complicated. Just consistent, boring protection applied regularly.