How to Set Up and Use Polis Def for Real-World DeFi Security
I've spent years working on DeFi security audits, and one thing keeps coming up across different protocols: trust assumptions that don't actually exist in practice. That is the space Polis Def Nextgen Defi Security Protocol Redefining Trust In Decentralized Finance operates in. It is not a magic bullet. It is a framework that attempts to replace opaque governance and single-point failure modes with something auditable and modular. At its core, this is a next-generation security layer for DeFi protocols. It bundles together several mechanisms: multi-signature governance with time-locked execution, on-chain insurance pools, real-time anomaly detection, and formal verification bridges between contract upgrades. The idea is to make security transparent rather than something you just trust a team to do honestly. Most people understand multisigs. What they miss is the execution layer. Polis Def adds a delay mechanism where any governance proposal must sit for a configurable period before it can be executed. This gives users time to react if something goes wrong. It also means the protocol needs to have proper treasury buffers for that window, which most implementations skip.
Getting Started: Download and Initial Configuration
You can find the Polis Def repository at their official GitHub page. The smart contracts are written in Solidity and require OpenZeppelin libraries version 4.9 or later. Make sure your development environment has Foundry installed if you plan to run the test suite. Clone the repo and run the standard setup commands. The configuration file is where things get interesting. You need to set your desired threshold for multisig signers, the timelock delay in seconds, and which oracle network the protocol will use for external data feeds. I would recommend starting with a conservative timelock of at least 24 hours for anything handling more than 100 ETH in total value locked. Deployment requires you to set up a governance token first. Polis Def does not create its own governance token. It works with existing ERC-20 or ERC-721 tokens, but the token needs to have standard transfer functions and sufficient liquidity. If your token is a rebasing token or has custom transfer logic that modifies balances outside of standard transfers, you will run into issues with the voting delegation system. This tripped me up on a project last year. The workaround was writing a simple wrapper contract that normalized the balance calls before passing them to Polis Def's voting module.
How the Security Layer Actually Works Under the Hood
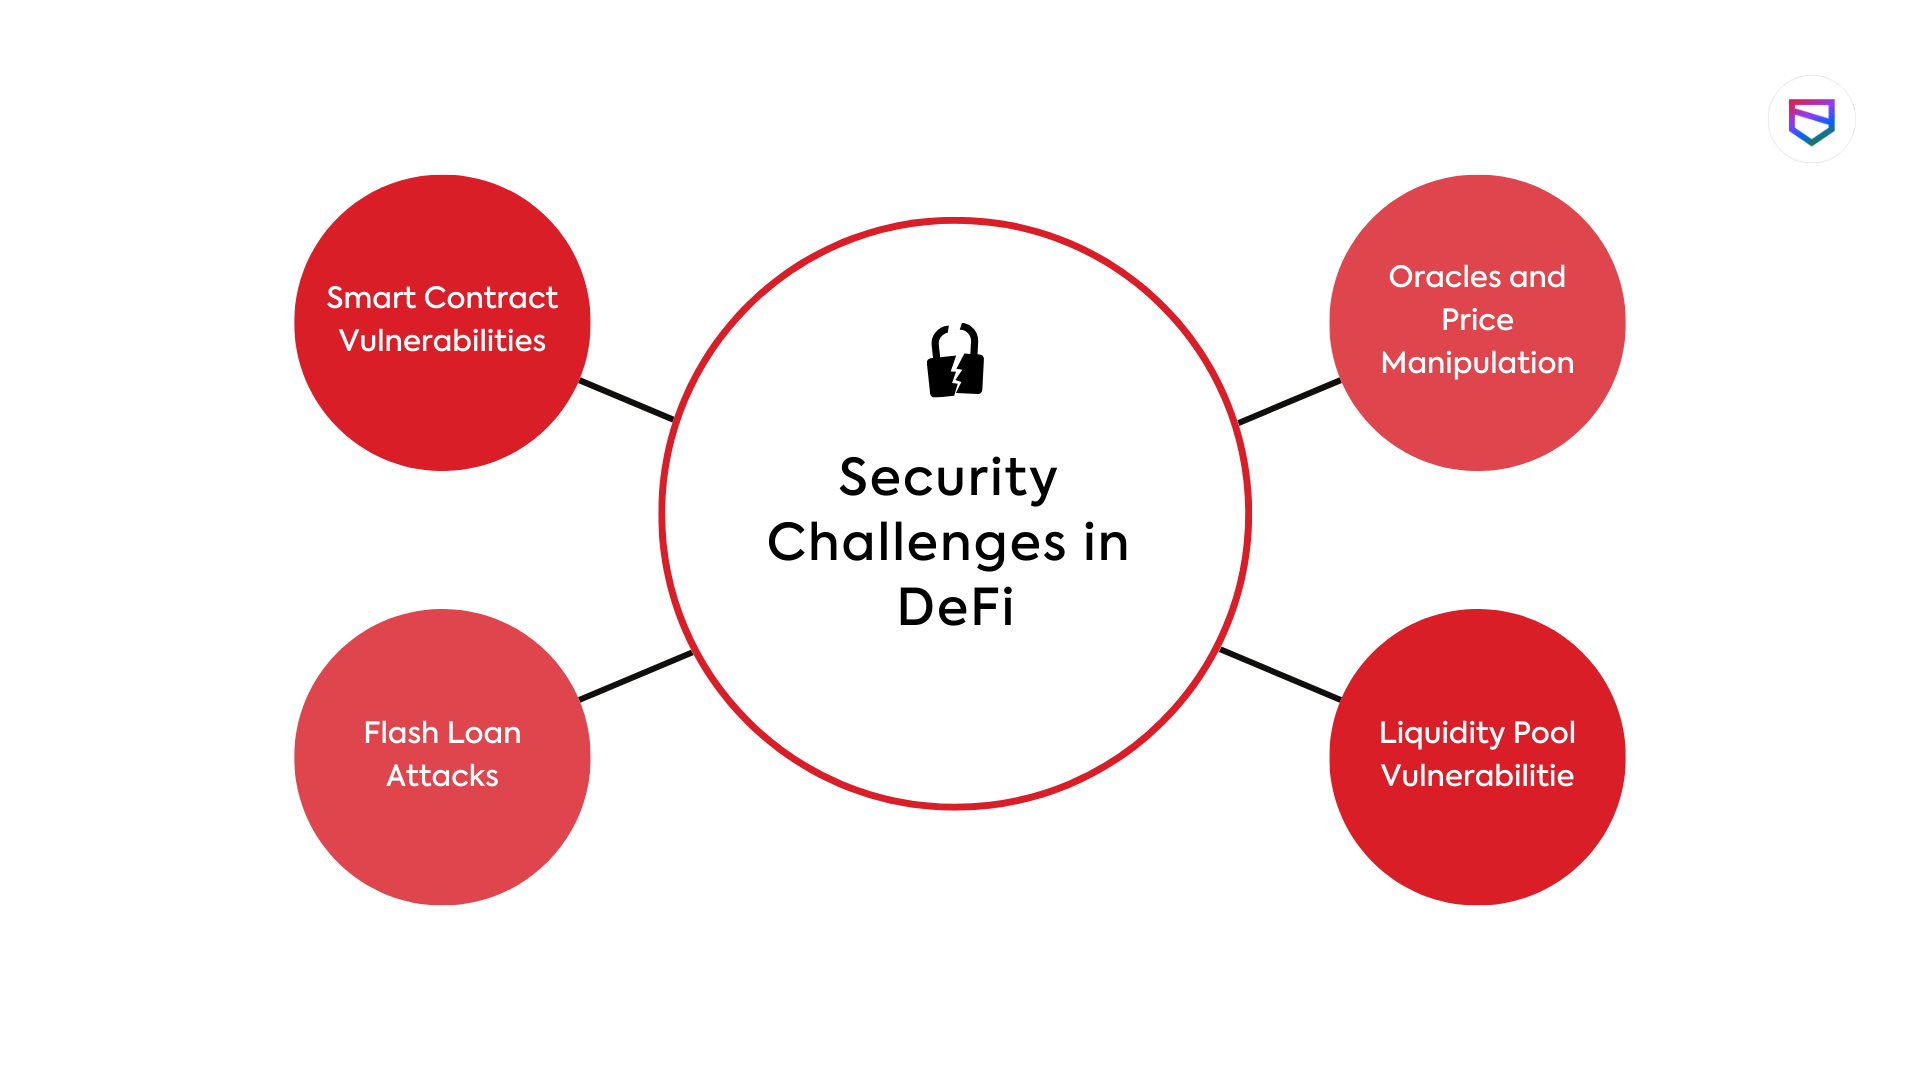
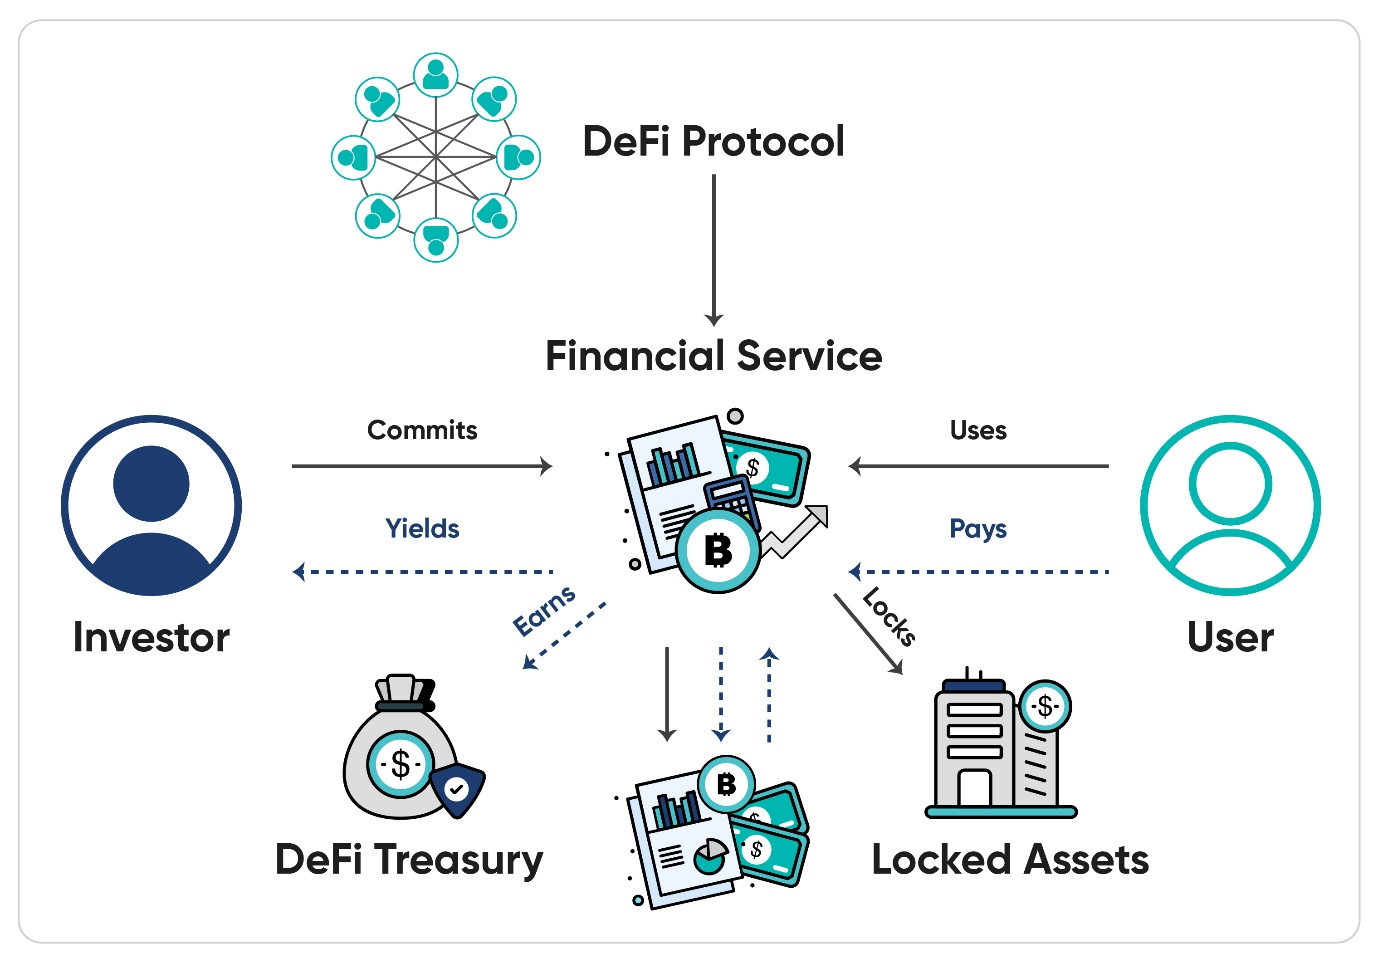
The anomaly detection module is probably the most overlooked component. It monitors transaction patterns across the protocol and flags deviations from normal behavior. Things like unusual withdrawal amounts, rapid successive calls to different functions, or gas price spikes that suggest a frontrunning attempt. The system does not auto-revert transactions. It alerts and can trigger a temporary pause if configured to do so. Here is the part nobody mentions: the pause mechanism is a double-edged sword. I once watched a protocol pause correctly after detecting a flash loan attack, but the pause lasted three days because the community could not agree on how to resolve it. By the time they unpased, the attacker had already drained a secondary vault. The lesson was simple. Always test your pause and unpause workflows with real stakeholders before deploying to production. Document clear escalation procedures. Without them, a security feature becomes a hostage situation. The insurance pool works differently from traditional insurance. There is no underwriter. Contributors stake tokens into a shared pool and earn a percentage of protocol fees. When a verified exploit happens, claims are paid from that pool. The key word is verified. Claims go through a multi-stage review process that includes on-chain evidence submission and community voting. This process takes time, usually between 48 to 72 hours for straightforward cases.
Get the Full Details
Common Pitfalls and Things Beginners Miss
First, most teams treat Polis Def as a plug-and-play solution. It is not. The integration requires modifying your existing contract architecture to support the governance hooks and timelock checks. If your protocol uses a custom upgrade pattern, you will need to adapt it to work with Polis Def's verification bridge. Skipping this step means your upgrades are not actually secured by the protocol. Second, the oracle dependency is real. Polis Def relies on external data feeds for certain features. If your chosen oracle network experiences a delay or a fork, some security features may not activate correctly. I recommend running at least two independent oracle sources and having a fallback configuration ready. This added about two weeks of development time on my end but saved us during a major Ethereum network congestion event where one oracle stalled for nearly four hours. Third, gas costs. The additional layers of security verification add overhead. Expect your transaction costs to increase by roughly 15 to 30 percent compared to a baseline protocol without Polis Def. For high-frequency trading applications, this can be significant. For slower-moving governance-heavy protocols, it is manageable.
When Polis Def Is the Right Choice and When It Is Not
Use Polis Def when your protocol has complex governance needs, handles significant value, and requires a transparent security model. It is particularly useful for lending platforms, DEX aggregators, and yield protocols that need both speed and accountability. Do not use it for simple utility tokens, low-value experimental projects, or protocols where fast execution is more important than security layers. The timelock and verification steps add friction that can kill the user experience on fast-moving applications. In those cases, a simpler multisig setup with a dedicated audit firm relationship might serve you better. Be honest about your protocol's actual needs rather than copying what other projects are doing. The Polis Def documentation is reasonably thorough, but the community forums move fast and some older threads reference deprecated versions of the contract interface. Always check the version number against your deployed contracts. I have seen multiple projects accidentally integrate with outdated modules because someone followed a tutorial that was six months old.
Security in DeFi is still an incomplete problem. Protocols like Polis Def move the needle, but they do not solve everything. The human element, the governance decisions, the economic incentives behind the insurance pool, these remain the parts that require actual thought rather than automated solutions. Set up your polis def nextgen defi security protocol correctly, test it thoroughly, and keep your emergency procedures updated. That is the work that actually matters.