Setting Up pfSense at Scale Is Not Like Setting It Up at Home
You can download the ISO from the official site and have a basic firewall running in about twenty minutes if you are doing a single interface setup for a small office. Most people stop there and assume they understand the platform. That assumption gets you into trouble pretty quickly. The software itself is stable. The complexity comes from what you actually try to make it do. I have deployed this across roughly forty different sites over the past eight years, mostly for mid-sized companies that needed proper segmentation without paying enterprise licensing per seat. The core install is straightforward. You flash it to a USB drive using Etcher or Rufus, boot the target hardware, and walk through the wizard. But the wizard only configures the basics. What you actually need to configure comes after that initial setup phase. The licensing side of things used to confuse people. There is a free community edition and a paid version called pfSense Plus. For most businesses the community edition covers everything you need unless you require certain enterprise support features or specific commercial extensions. The Plus version adds things like built-in support contracts and some managed features, but the underlying packet filtering logic is essentially identical between the two. I typically recommend starting with the community edition and upgrading only if you hit a wall. I have never seen a company actually need Plus to do serious network security work.
One thing that catches people off guard is the hardware requirement. This software does not run well on potato-grade mini PCs unless your throughput needs are very low. I learned this the hard way. I installed it on an old Intel NUC with 4 gigabytes of RAM and an Atom processor at a client site that had around eighty endpoints and a 500 megabit WAN connection. The box would idle fine, but the moment we enabled deep packet inspection with Suricata and ran VPN through it, the CPU would peg at one hundred percent and actual throughput dropped to about eighty megabits. The fix was swapping to a board with an Intel Celeron J4125 and bumping RAM to eight gigabytes. After that change, we saw nearly line-rate performance even with all inspections enabled. Don't sleep on VLAN configuration either, because that is where the real segmentation power lives. You can carve your network into separate broadcast domains using virtual LANs on a single physical interface. I recently set this up for a dental clinic that needed their clinical devices completely isolated from their guest Wi-Fi. The trick is getting the trunk configuration right on the upstream switch. If your managed switch does not have the correct VLAN tagging set on the port going to pfSense, none of the virtual interfaces will come up and you will spend an hour wondering why nothing works. Check the switch side first. Always check the switch side first. Rule order matters more than most guides mention. pfSense evaluates firewall rules top to bottom and stops at the first match. This means a broad permit rule near the top will silently override specific deny rules further down. I fixed a misconfiguration once where someone had placed a "allow all traffic from the guest network" rule above a specific block rule for a certain subnetwork. The block rule was never hit. The guest users could reach everything they shouldn't have been reaching. Moving the deny rule above the allow rule took about three seconds and solved the entire problem.
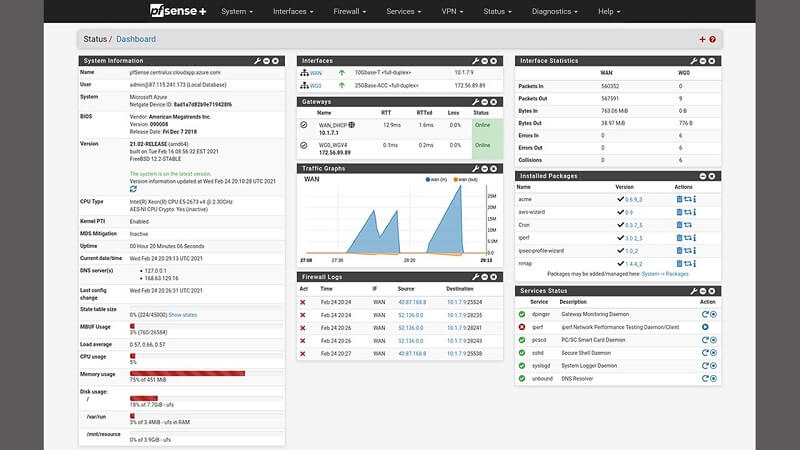
There are some features worth paying attention to that people overlook. CARP gives you high availability by running two firewalls in sync. If the primary box dies, the secondary takes over in about five seconds with minimal disruption. Setting this up requires both boxes to be on the same hardware generation ideally, and you need a dedicated HA interface between them. The failover process itself works reliably. I have tested it by pulling power from the primary unit during business hours and the secondary caught the traffic without anyone noticing. The configuration replication handles most settings automatically once you define the CARP group. Logging and reporting are solid but basic. The built-in traffic graphs give you enough visibility for most monitoring needs. If you want deeper analytics you can push logs to an external Syslog server or a SIEM platform. I usually recommend setting up a separate server for log aggregation because storing everything on the firewall itself fills the CF card or SSD relatively fast depending on traffic volume. A dedicated log server running something like Wazuh or Graylog paired with pfSense gives you audit trails that actually survive a reboot. VPN configuration is another area where people make mistakes. OpenVPN and WireGuard are both supported. WireGuard is faster and simpler to set up. OpenVPN has broader compatibility. I typically deploy WireGuard for site-to-site tunnels because the handshake is faster and the crypto overhead is lower. For remote access, I still lean toward OpenVPN because it handles more edge cases with varied client environments. Certificate management for OpenVPN is where most people stumble. You need a proper PKI infrastructure. Using built-in certificate authority tools in pfSense is easier than it sounds and saves you from buying external CA licenses for internal use.
Get the Full Details
The package system is where pfSense diverges from most alternatives. You can install Snort or Suricata for intrusion detection, Squid for proxying, VyOS integration packages, and various monitoring tools. I usually enable Suricata in inline mode for production environments because it actively blocks threats rather than just alerting on them. The rule updates from OISD or custom feeds can add significant load to the system depending on how aggressive your feed selection is. Start with a moderate rule set and add more once you understand what each category actually triggers on. Empty your alerts inbox weekly or you will stop reading them entirely. I speak from experience here. There are genuine limitations worth acknowledging upfront. The web GUI is functional but clunky. Complex multi-WAN setups require careful policy routing configuration that can take hours to get right even for experienced admins. Multi-WAN failover without proper gateway monitoring will cause intermittent connectivity issues that are frustrating to debug. The software also does not scale infinitely. Once you go beyond roughly two hundred thousand NAT entries or very heavy deep packet inspection workloads, you start hitting performance walls that require either hardware upgrades or moving to a different solution entirely. In those cases, consider alternatives like OPNsense for a more modern GUI experience or running a commercial platform like Sophos XG if you need dedicated vendor support and do not want to manage the stack yourself. Maintenance is not zero effort. You need to apply firmware updates regularly. The auto-update feature exists but I recommend reviewing each update changelog before enabling automatic upgrades in production. A bad update can break your configuration or introduce compatibility issues with installed packages. I keep a snapshot of the working configuration before every major update. The export feature makes this trivial and takes about thirty seconds. Restoring from a backup after a failed update is also straightforward if you have the XML file saved.
Documentation is extensive but scattered across multiple URLs and community forums. The official wiki covers most scenarios. The community forums are active but quality varies. I bookmarked the most useful threads during my early deployments and still reference them occasionally. Reddit has a pfSense subreddit that is more current than the old forums for real-world discussions about specific issues. GitHub hosts the source code and issue trackers if you want to dig into bug reports. The download link for the latest stable release is at pfsense.org/download. You can also grab it from major mirrors if the main site is slow. Choose the 64-bit version for any reasonably modern hardware. The 32-bit build is legacy at this point and lacks some performance optimizations. Write the image to a USB drive, insert it into the target machine, and boot. The installer asks about disk size and partition layout. For most deployments the default layout works fine. You can customize it if you need a specific disk arrangement but most people do not. After the install completes, you connect to the default interface at 192.168.1.1 and log in with the credentials printed on the console after installation. Change the default password immediately. The default admin username is also well known so changing it is worth doing too. From there you configure your interfaces, set up DHCP ranges, and begin adding rules. I recommend starting with a single deny-all rule at the bottom of every chain before you add any permits. This creates a clean baseline where only explicitly allowed traffic flows through. Then add rules from the bottom up, which is the opposite of how most people think about it but matches how the engine actually evaluates them.
Backup your configuration after every meaningful change. Export it to a secure location. Test your restoration process at least once before you actually need it. I lost a configuration once because I assumed the automatic backup feature was sufficient and it had a bug in an older version that silently failed to write the file. Recovering from a manual backup taken twelve hours prior cost me three hours of reconfiguration work. That did not happen again. Monitoring matters more than most people invest in. Set up alerts for interface errors, memory pressure, and disk usage. Configure email notifications or integrate with a monitoring platform like Zabbix or PRTG. I had a client whose primary WAN link was degrading due to a failing SFP module on their upstream router. pfSense showed normal throughput but interface error counters climbed slowly over several days. The alerts caught it before the link actually dropped. Without those metrics I probably would not have noticed until someone reported the outage. The community edition receives security updates on a regular schedule. Check the announcement page monthly at minimum. Patching is not optional if you are running this in a production environment. Unpatched firewall software is worse than no firewall because it gives a false sense of security. The team behind pfSense is generally responsive to critical vulnerabilities and releases patches quickly. I have never waited more than forty-eight hours for a security fix on a serious issue.
For organizations that want managed services instead of doing it all internally, several companies offer pfSense deployment and management packages. These range from one-time setup projects to ongoing monthly managed service agreements. If your IT team is small and network security is not a core competency, a managed provider can be cost-effective. Just verify that the provider actually understands the platform deeply and does not just rely on automated deployment scripts. I have seen both approaches and the difference in quality is noticeable during incident response. Migration from other platforms is possible but plan for downtime. Moving from Cisco ASA or Fortinet to pfSense requires careful rule translation because the syntax and evaluation logic differ. I typically map out all existing rules, replicate them in pfSense, test in a parallel environment, then flip traffic during a maintenance window. Rushing a migration causes more problems than it solves. A proper cutover with rollback capability prepared takes about four to six hours for a typical small business setup.