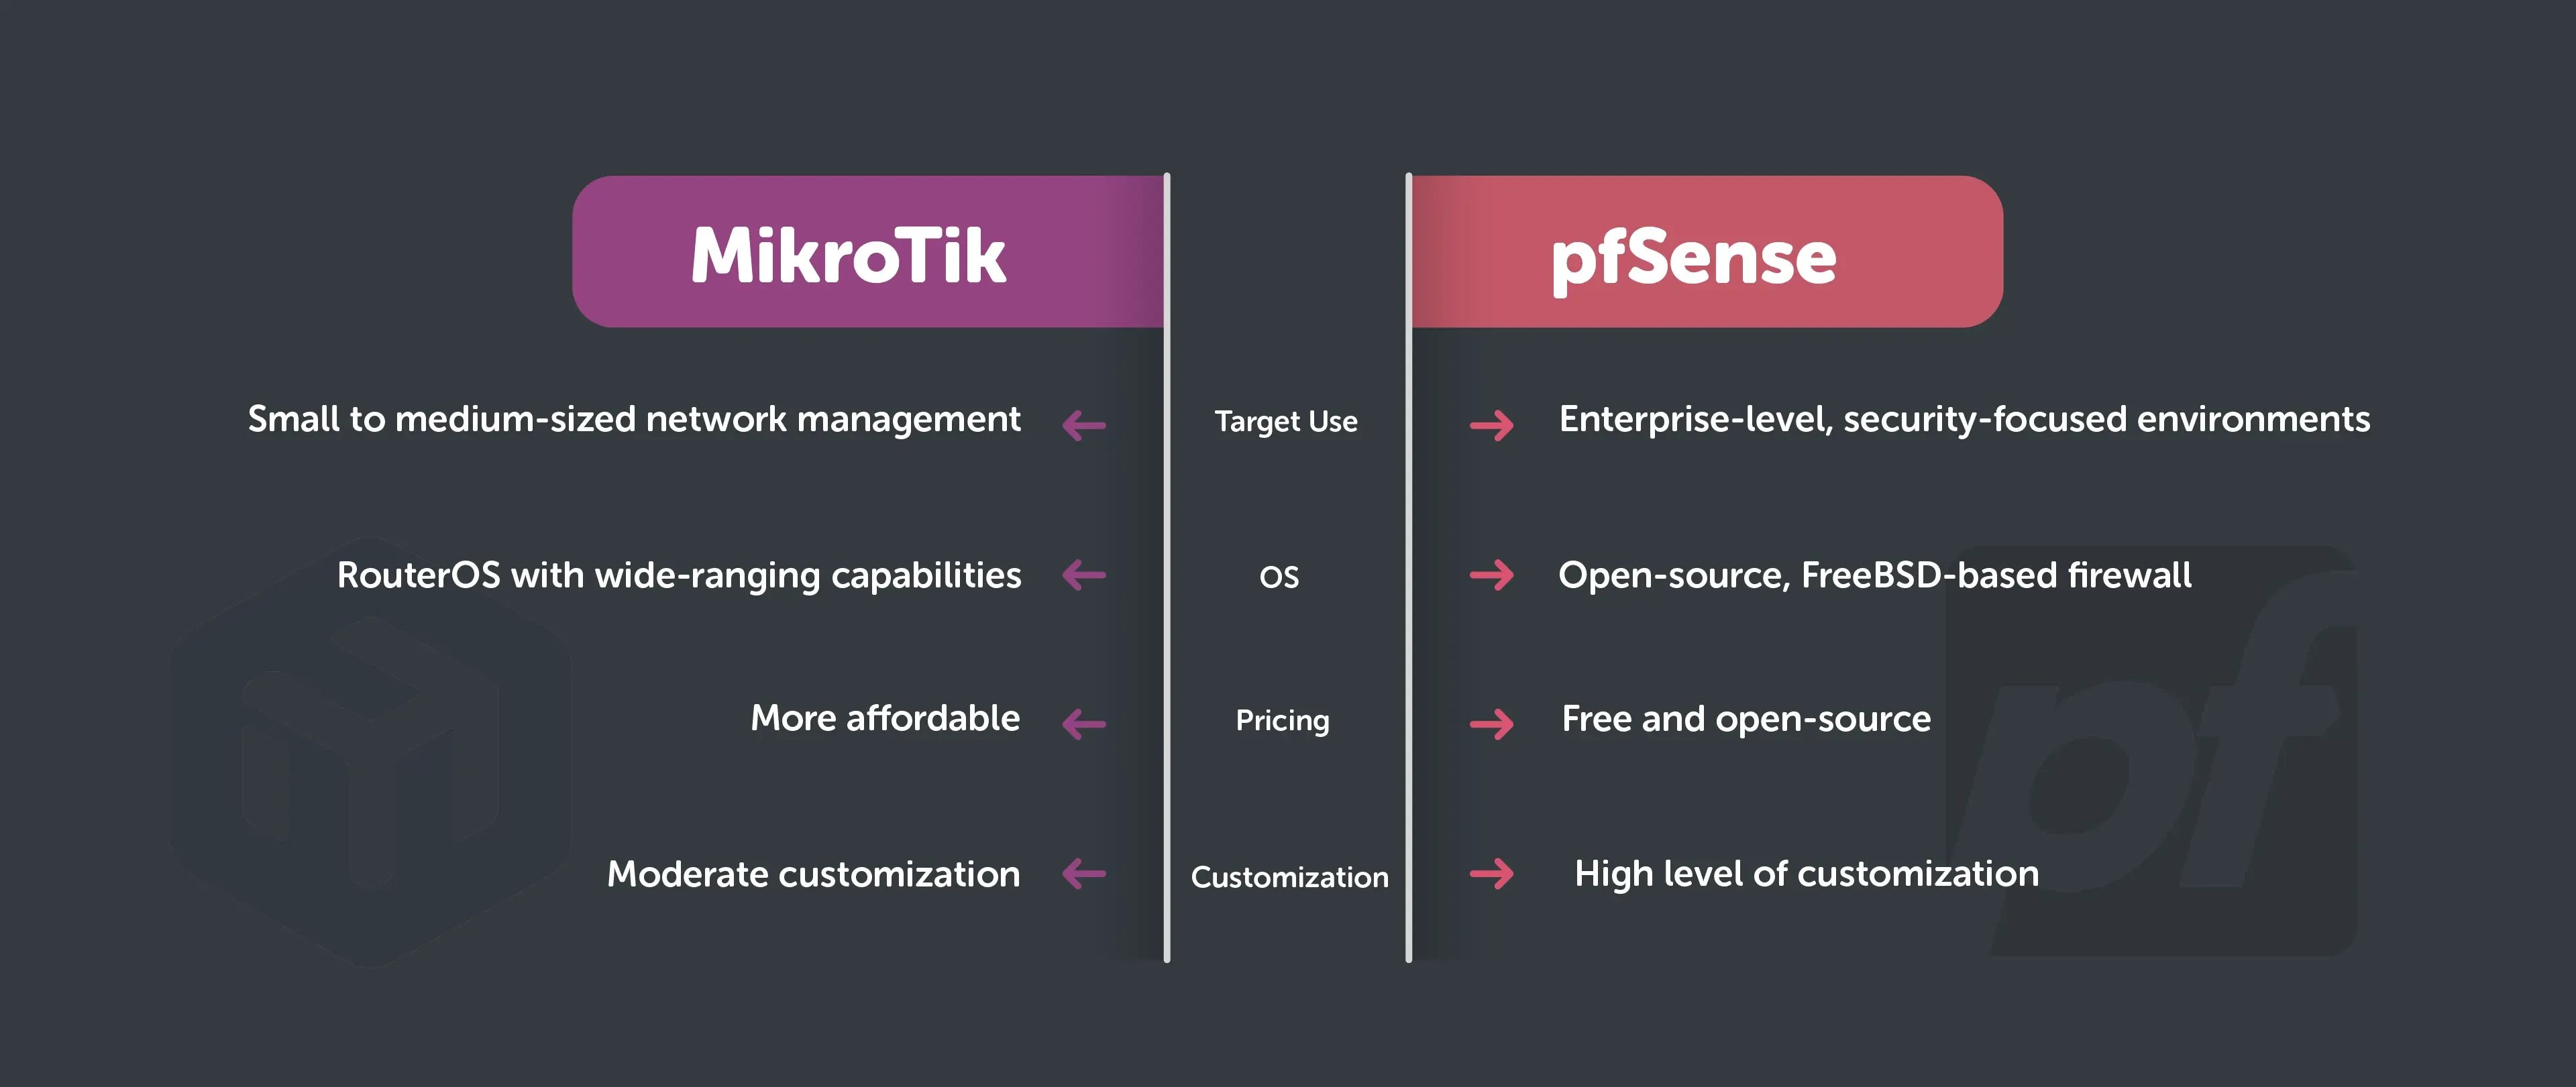
Choosing a firewall for your lab or office is mostly about picking which headaches you want to deal with
I've run both Pfsense and MikroTik in production for years, sometimes simultaneously on the same network. Here's what I've learned without the sales pitch. The short version is that Pfsense gives you a web interface that works out of the box and a community that has probably already solved whatever problem you're facing. MikroTik gives you a router that can do the same things if you're willing to read the manual and type commands in Terminal or navigate the Wizard.
Pfsense And Mikrotik A Network Security Showdown
Let me start with something that caught me off guard. I had a client who migrated from MikroTik to Pfsense and immediately complained that NAT was "slower." It wasn't. The default MTU on Pfsense VLANs is 1500, and their ISP requires 1492 on PPPoE. Packets were getting fragmented at the firewall and reassembling slowly on the other side. I found it by running tcpdump on the WAN interface and looking at the DF bit. Setting the MTU to 1480 on the WAN interface fixed it. Nobody talks about this in the setup guides. Both products handle the basics identically: stateful packet inspection, ALG modules, port forwarding, VLAN tagging, and DNS interception. Where they diverge is in how deeply you can modify the behavior and how much you have to know to get there. Pfsense is FreeBSD-based. That means everything under the hood ispfSense is open source and the base OS is Netgate's fork of FreeBSD. You get pf for packet filtering, which is a BSD stateful firewall. The GUI wraps around it and generates rules automatically. When the GUI fails or generates wrong rules, you SSH in and look at /tmp/rules.debug to see what actually got deployed. This file is your source of truth, not the browser interface.
MikroTik runs RouterOS, which is their own OS with its own scripting language and a very different approach to firewall rules. RouterOS uses the mangle table for traffic marking and routing decisions before the filter table even sees the packet. Pfsense doesn't separate things this way. If you're coming from Pfsense to MikroTik, the first thing you'll misconfigure is the order of operations in the mangle table and wonder why your QoS rules aren't applying. There's a specific MikroTik behavior that trips people up constantly. The router has a feature called PCQ (Per Connection Queuing) that works well until you enable the "simple queues" feature at the same time. They fight over bandwidth allocation and you end up with one queue eating all the bandwidth while the other does nothing. I spent three hours debugging a home lab where the download queue seemed to max out at 5 Mbps regardless of how much bandwidth was available. The fix was disabling simple queues entirely and relying on PCQ alone. Don't mix them. Pfsense has something similar but less dangerous. If you enable both Snort and Suricata on the same interface, they don't conflict but they do share CPU cycles. On a machine with an older AMD APU, enabling both will make the web proxy unusable because the IDS engines are eating all the available cores. Stick to one and allocate at least 2GB of RAM dedicated to the IPS engine. I run Suricata on a separate VM with dedicated NICs and it works fine.
Get the Full Details
Here's a practical comparison that matters if you're actually deploying one of these. For a small office with 20 to 50 users, Pfsense on a used Dell Optiplex with an i5 and 8GB RAM will handle a basic setup with VPN, VLAN segmentation, and content filtering without breaking a sweat. The OpenVPN server in Pfsense uses OpenSSL by default, which is solid. WireGuard is available as a plugin now and performs better on low-power hardware. If you need IPSec site-to-site, Pfsense handles it but the Phase 1 and Phase 2 negotiation can fail silently when the pre-shared key contains special characters. I had this happen with a $%^ key that worked in my notes but failed on the remote end. Use alphanumeric only. MikroTik can do the same thing on a RB5009UG+S+IN for less than the price of the RAM upgrade. The hardware is faster per dollar, but you'll spend more time writing the configuration. A complete MikroTik setup with VLANs, DHCP, IPsec, and wireless usually takes me about 4 hours the first time. Pfsense takes 30 minutes to install and maybe 2 hours to configure properly the first time. After that, Pfsense is faster because the GUI handles most of the rule generation.
The real difference shows up when something breaks. With Pfsense, you can restore from a config backup through the web interface in about 5 minutes. The backup is a single XML file. MikroTik uses export scripts that are harder to read and restore from. I keep both systems configured and I swap between them when I'm troubleshooting because each one exposes different problems in the network. One thing Pfsense does better that people overlook: the package repository. Captive portal, NGINX proxy manager, HAProxy, vnStat, and dozens of other packages install with a click. MikroTik has a similar ecosystem through scripts on the forum, but you have to find the script, read it to make sure it isn't doing something malicious, paste it into the router, and hope it doesn't conflict with your existing configuration. It works, but it's slower. There's also the logging question. Pfsense stores logs in /var/log and you can forward them to a syslog server or view them through the web interface. The default log retention is aggressive and fills up disk space fast if you're logging everything. I set mine to rotate at 100MB with 5 backups and that's usually enough. MikroTik logs to RAM by default and writes to disk only when you configure the logger. If you forget, your logs disappear on reboot. This happened to me once during an incident investigation and I lost three hours of traffic data. Always configure the log file target before deploying in production.
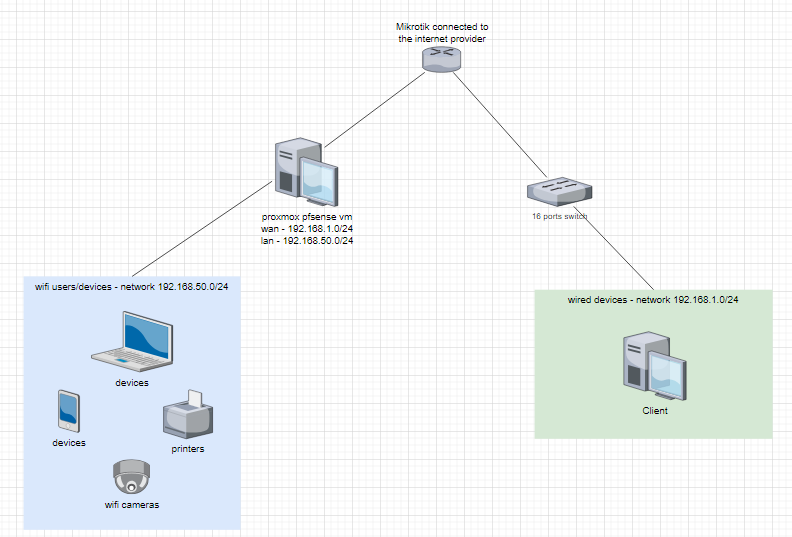
If you're starting fresh and want the fastest path to a working firewall with VPN and VLANs, Pfsense is the answer. If you're building a network with lots of routing complexity, multiple ISPs, and want to squeeze every megabit out of consumer-grade hardware, MikroTik is worth the learning curve. Neither one is wrong. They just solve different parts of the problem. I run Pfsense at the edge of my network and MikroTik for the internal routing between buildings. The Pfsense box handles inbound traffic inspection and VPN termination while the MikroTiks handle inter-building VLAN routing and QoS. It's not a hybrid setup you'd find in any tutorial. It's what I ended up with after trying to make one platform do everything and failing. Both will serve you well if you understand what they're good at and where they stumble. The worst outcome is picking one because someone online said it's better and then wondering why your network isn't performing.