Getting Parrot OS Right Without Burning Through a Weekend
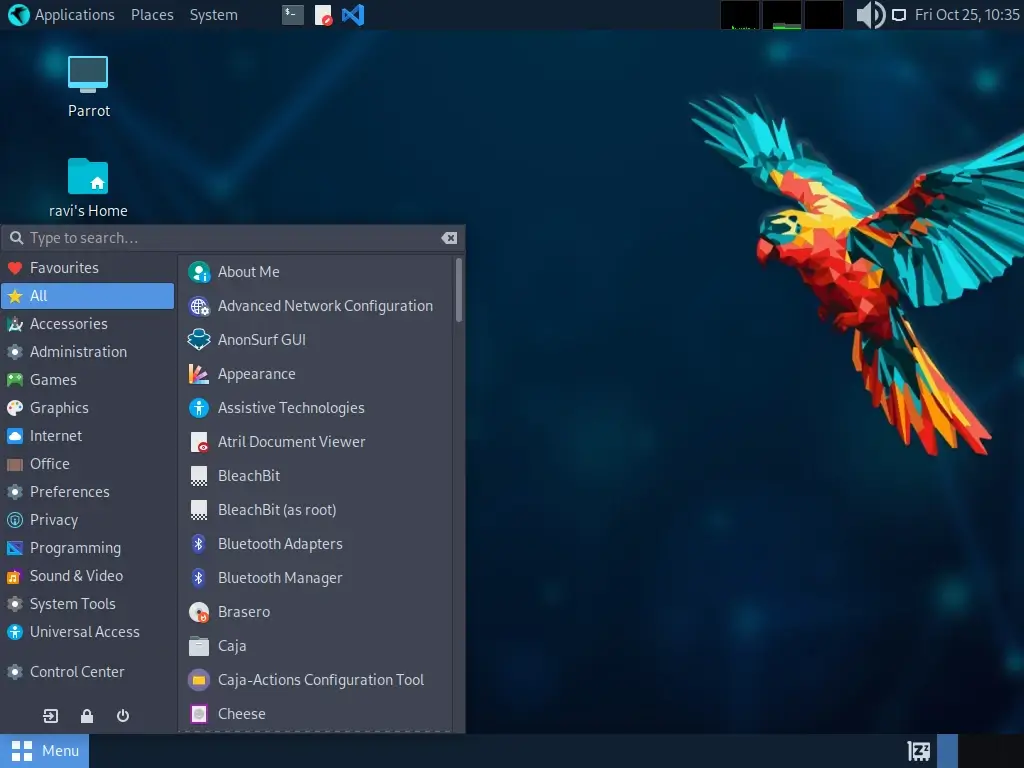
Most people download Parrot OS thinking they're getting a magic bullet for privacy or pentesting, then hit the wall within a day because their hardware doesn't cooperate or they don't understand what they actually downloaded. I've walked through this enough times to know where it goes wrong. Let's just cover the practical reality of running this distro without the marketing gloss. Parrot OS comes in two main flavors: the Home edition and the Security edition. They share the same MATE desktop base built on Debian Stable, but the Security edition ships with roughly 400 preinstalled tools for penetration testing, digital forensics, and reverse engineering. That's the difference. If you just want a private desktop, grab Home. If you need aircrack-ng, burpsuite, wireshark, john, and a dozen other security tools ready to run out of the box, Security is what you want. Both run on XFCE or MATE depending on your hardware. The Security install is heavier because of those tools. Here's a counter-intuitive thing nobody tells you: the Security edition isn't actually harder to use than most general-purpose distros. It's Debian underneath, so package management works exactly how you'd expect. The real friction shows up in two places. First, the live USB encryption setup can trip people up if you try to preserve sessions across reboots without reading the on-screen prompts carefully. Second, some of the preinstalled tools assume you're running as root or have properly configured sudo, which creates confusion for users coming from Kali where the default behavior is different.
I ran into a specific issue last year when trying to use parrot-upgrade on a fully updated Security installation. The system reported that some packages were being held back, which usually means a dependency conflict. In this case, it was a kernel header mismatch between the Debian stable repo and some of Parrot's custom security tool repositories. The workaround was running apt-get install --fix-broken followed by apt-get dist-upgrade, then rebooting into the newest kernel. After that, the held-back packages resolved themselves. It happens maybe once every six months for me, but it's worth knowing about because the default apt upgrade command leaves things in a messy state if you don't catch it.
Installation That Doesn't Break Things
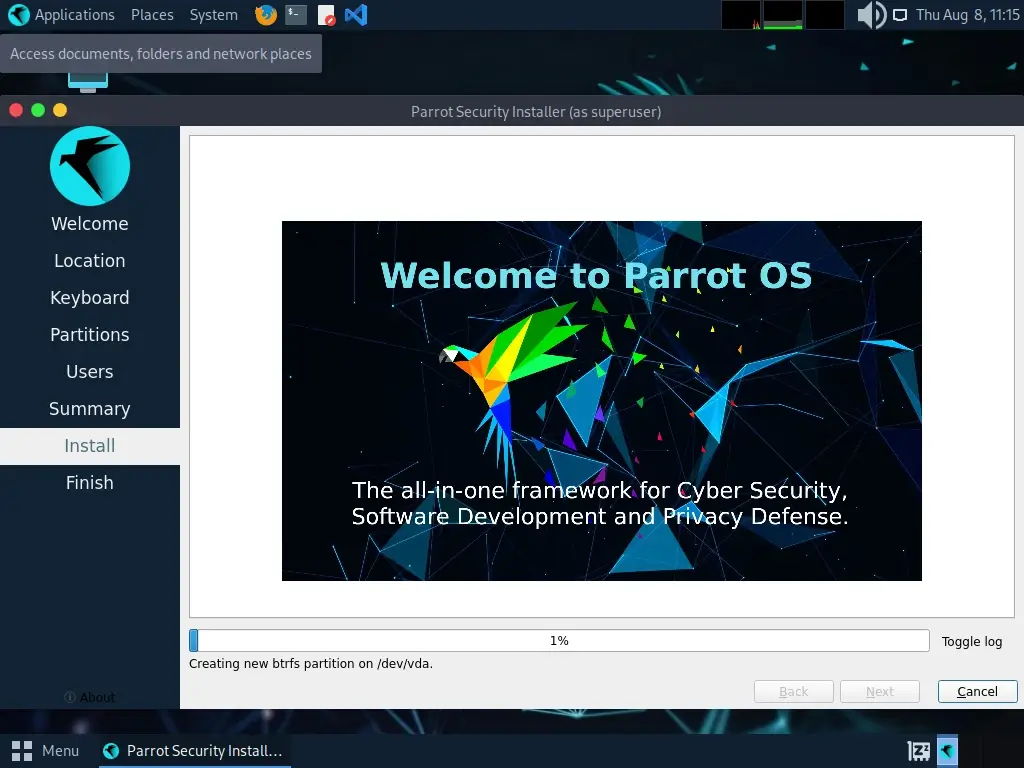
Write the ISO to a USB stick using either Rufus on Windows, dd on Linux, or Etcher. Parrot's ISO is around 3.5 gigabytes, so make sure your USB drive is at least 8 gigabytes. Boot from it. The installer is standard Debian Anaconda, which means it's reliable but not particularly clever. During the partitioning step, choose guided mode if you're installing alongside another OS. The manual partitioning option gives you more control but requires you to understand mount points, swap, and EFI boot partitions. If you don't, use guided. One detail that matters and gets skipped: when the installer asks about the GRUB bootloader, make sure it installs to the correct disk. I've seen people accidentally overwrite their Windows bootloader because they selected the wrong drive during this step. Double-check that the target is /dev/sda or /dev/nvme0n1, not a partition like /dev/sda1. The bootloader always goes to the disk, never to a partition. After installation, run these commands in order. They take about three minutes on a normal connection and prevent most post-install headaches:
Get the Full Details

sudo apt update && sudo apt full-upgrade -y This refreshes your package lists and updates everything to the current Debian Stable point release. Then run sudo apt install -y parrot-misc to pull in any missing Parrot-specific utilities that the base install might have skipped. Finally, sudo apt autoremove cleans up orphaned packages from the initial install.
Network Security Basics That Actually Matter
Parrot OS includes firewall configuration tools by default, but they're not configured out of the box the way you might expect. The most important first step after installation is setting up UFW or nftables depending on your comfort level. For most users, UFW is sufficient and far easier to manage. Run sudo ufw default deny incoming and sudo ufw default allow outgoing to start with a closed inbound policy. Then add specific rules for the services you actually need, like sudo ufw allow 22/tcp for SSH if you're using the system as a server. Another thing that catches people off guard: Parrot OS includes AppArmor by default on the Security edition, but not all the profiles are enabled for the preinstalled tools. This isn't a flaw, it's a design choice because security tools often need broad system access. Still, you should run sudo aa-status after installation to see what's actually protected. The output will show you which services have active profiles and which don't. For anything running on this machine that isn't a security tool, enabling AppArmor profiles is worthwhile. Encryption is where Parrot actually shines compared to other distros. The installer offers full disk encryption during setup, and it works properly. When you choose this option, you'll enter a passphrase at boot and the entire disk gets encrypted with LUKS. The downside is that you cannot recover data if you lose that passphrase. There's no backdoor, no recovery key stored in the cloud, nothing. I had a user once who lost their passphrase and spent two weeks trying to brute-force a 12-character password before giving up. Use a passphrase manager and write the password down somewhere physical. It sounds obvious, but I've seen it fail repeatedly.
The Tool Ecosystem Without the Hype
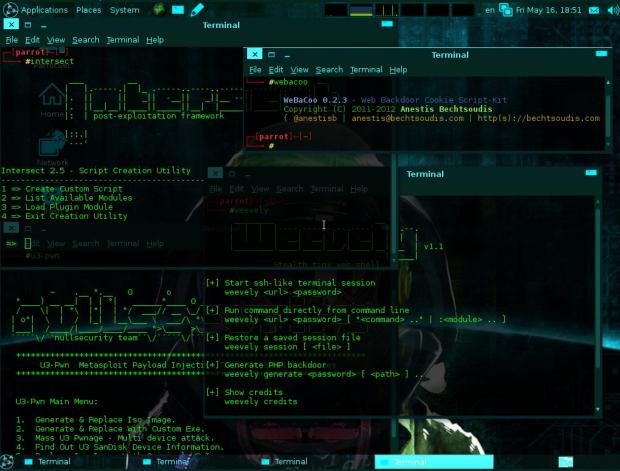
The Security edition ships with tools organized into categories. Network tools include nmap, tcpdump, and bettercap. Wireless tools include aircrack-ng, wash, and reaver. Web application tools include burpsuite, skipfish, and dalfox. Forensics tools include autopsy, binwalk, and foremost. Reverse engineering tools include ghidra, radare2, and crackmal. Each category has tools that are genuinely useful and tools that are redundant because similar functionality exists elsewhere. Here's what I'd actually recommend keeping installed versus what you can safely remove. Keep nmap, burpsuite, aircrack-ng, radare2, and ghidra. These are the tools I use regularly and they're well-maintained. Consider removing parrot-livestream if you're not doing CTF competitions, and parrot-welcome can go too since it's just a splash screen. The total disk space saved is minimal, maybe 200 megabytes, but it reduces attack surface by removing unused binaries from your system. A practical tip about tool updates: Parrot's security tools update on a different schedule than Debian Stable packages. Running apt update alone might not get you the latest version of a tool like ghidra or radare2 because those come from Parrot's own repository, not Debian's. Check cat /etc/apt/sources.list to see which repositories are active. You should see entries for both debian.org and parity.os sources. If one is missing, your tools won't update properly.
Common Mistakes That Wipe Your Setup
The biggest mistake I see is disabling the firewall after installing Parrot because "pentesting tools need network access." This is backwards reasoning. Those tools work fine with the firewall enabled. Disabling it just makes your machine visible to everything on your network, which defeats the entire purpose of running a security-focused distro. Keep UFW active and configure rules as needed. Another mistake is mixing repositories. People add Kali's repository to their sources.list because they want a specific tool, then run apt upgrade and break their entire system. Parrot and Kali are both Debian-based but use different package versions and dependencies. Mixing them creates dependency conflicts that are painful to resolve. If you need a Kali-specific tool, use a Docker container instead. docker pull kalilinux/kali-rolling gives you the full Kali environment without touching your Parrot installation. The third mistake is running security tools without understanding privilege escalation. Many Parrot tools require root. Some work as a normal user. Running everything as root because "it just works" is how you accidentally destroy your own system. I've seen users run a mass scanning tool with root privileges that modified firewall rules they didn't intend to touch, locking themselves out of their own SSH session. Always check the manual page before running a tool with elevated privileges. man nmap takes five seconds and prevents a lot of problems.
When Parrot Isn't the Right Choice
Parrot OS is excellent for penetration testing and privacy-focused daily driving on older hardware. It's not ideal if you need cutting-edge software that requires newer libraries than Debian Stable provides. The Debian Stable base means packages are older but more stable. If you need the latest version of Python, the latest kernel for hardware support, or bleeding-edge security tools, you'll spend more time fighting the package manager than doing actual work. In that case, Arch Linux with a security toolkit or Debian Testing with Parrot's repositories might serve you better. It's also not great as a primary workstation for non-security work. The preinstalled tools are fine, but the system isn't optimized for productivity workflows like video editing or 3D rendering. The MATE desktop is lightweight, which is good for battery life on laptops, but it lacks some of the polish and integration that GNOME or KDE Plasma offer. If you need a do-everything machine, something like Ubuntu or Fedora with security tools added manually makes more sense. The real value of Parrot OS is that it removes the setup overhead. Instead of spending four hours installing and configuring security tools on a fresh Debian install, you get a working system in twenty minutes. That time savings is real and measurable. But it comes with the trade-off of a less current software base and occasional repository friction that only becomes obvious after you've been running the system for a few months.
Download the ISO from the official Parrot website. Avoid third-party mirrors. The file is large enough that corrupted downloads are common from unofficial sources, and starting fresh after a bad install is more time-consuming than just waiting for the direct download to complete.