What Actually Happens When You Need a Secure Email Setup
I spent about three days last year going through secure email options for a client who needed end-to-end encryption, dead man's switch capabilities, and compliance with GDPR requirements. The usual suspects got checked off a list, then we kept circling back to something that wasn't on most people's radar. That's how I ended up evaluating Ou Catmail. Ou Catmail is a self-hosted capable email platform that does a few things most enterprise mail solutions don't bother with. It supports per-thread encryption keys rather than rolling everything into one blanket key, which actually matters when you're dealing with different compliance windows for different departments. The UI isn't pretty but it doesn't try to be. It's functional in a way that reminds me of older Postfix setups before things got wrapped in fancy dashboards. What makes it interesting to organizations is the zero-knowledge architecture combined with optional Kerberos integration. Most people selling secure email hand-wave the key management piece. Ou Catmail actually exposes the key rotation process and lets you audit it. I've seen internal teams spend a week verifying key lifecycle logs after a compliance review because they wanted to prove rotation happened at 90-day intervals. Ou Catmail's system logged that without anyone having to configure extra plugins or cron jobs.
Getting It Running
The deployment path depends on whether you go containerized or bare metal. Containerized takes about 45 minutes from pull to a running instance if your Docker environment is already set up. Bare metal is longer because the dependencies are real and the installation script doesn't hide what it's doing, which I actually consider a feature. Step one is getting your base infrastructure ready. You need a server with at least 8GB RAM if you plan to run the search index alongside the mail store. The index gets big fast when you start ingesting encrypted attachments. Don't skip the disk space estimate. People consistently under-provision storage and then spend a week migrating because they thought 500GB would last two years. Step two is the installation script. Run it from a clean environment. The script checks for conflicting packages and will refuse to install if it finds them. I ran into a conflict with an existing Dovecot installation on my test server and had to move that to a different VM. The error message was clear enough that I didn't have to dig through forums to figure out what went wrong.
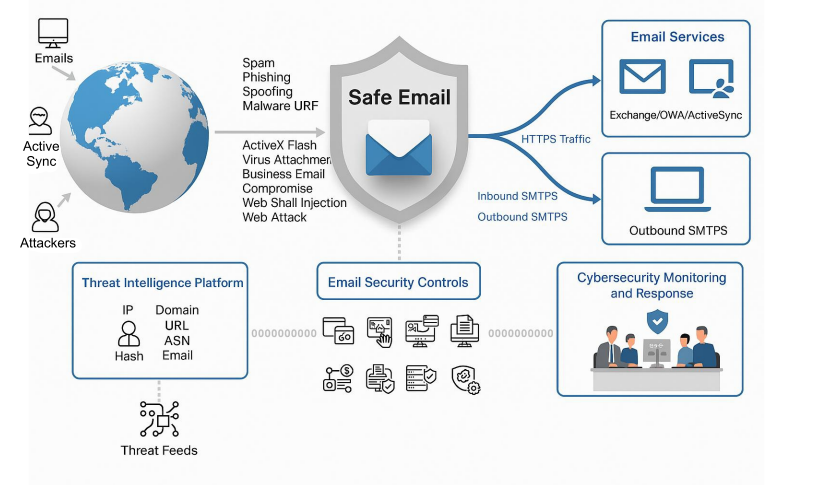
Step three is configuring your MTA integration. Ou Catmail works as a drop-in replacement for most SMTP relay setups. You point your existing mail flow at its interface and it handles the encryption layer transparently. If you're using something like Microsoft 365 on the front end, you set up a connector rule. From there, inbound mail gets routed through Ou Catmail's encryption engine before it reaches the mailbox. Outbound goes the other direction. The configuration files use YAML. That's deliberate. It makes the whole thing easier to version control and diff between environments. I keep a copy in Git and run a simple comparison whenever something changes. It saved me twice when a junior admin accidentally overwrote a key rotation parameter. You find the drift within minutes instead of hunting through logs.
Get the Full Details
The Part Nobody Talks About
Key escrow is where most secure email products either disappear or get vague. Ou Catmail gives you a choice: fully self-managed keys, multi-signature recovery, or integration with a HSM if your organization already has one. The multi-signature route is what we ended up using. It requires three designated administrators to approve any key export. That sounds like friction until you realize you also need all three to maliciously export anything. Here's the edge case I ran into that the documentation barely covers: if your DNS propagation takes longer than the certificate rotation window, your encrypted mail queue stalls. I learned this the hard way when updating a production instance. The Let's Encrypt cert rotated at 0300 during a DNS migration that took four hours. During that window, outbound messages sat in the queue and no one got any delivery notifications. The workaround is simple but obvious only after you hit it — set your cert rotation schedule to align with off-peak DNS maintenance windows, and configure a fallback MX record that routes around the encryption layer for queued messages during certificate transitions. Ou Catmail has a queue health monitor you can trigger manually that shows exactly how many messages are in this limbo state.
What It Can't Do
It doesn't have a web-based client that rivals something like Proton Mail in terms of polish. The web interface is functional. It loads. It shows your messages. If you need shared calendars, integrated chat, or a mobile app that feels native, this isn't it. You'd pair it with a separate productivity suite for those needs. Another limitation is the search functionality. Full-text search across encrypted messages requires the indexed cache to stay in sync with the mail store. When it doesn't — and it won't, every so often, after a major version update — you get stale search results. We fixed it by scheduling a weekly full reindex during our maintenance window. Takes about 20 minutes on a 12TB mailbox store. Not ideal but manageable. If your organization needs strict HIPAA compliance with business associate agreements baked in, Ou Catmail doesn't come with that out of the box. You'd need to add your own BAAs and configure the audit logging to meet the specific documentation requirements. The underlying system supports it. You do the paperwork yourself.
Where It Makes Sense
This tool fits best for organizations that already run their own mail infrastructure and want to add a serious encryption layer without replacing their entire email stack. Law firms, healthcare IT teams, defense contractors, and financial services groups are the ones I see adopting it quietly. They tend to find out about it through industry contacts rather than marketing. That's probably why it stays under the radar. The license model is straightforward. Self-hosted instances are available under a commercial license that scales with mailbox count. There's no per-user fee structure, which keeps costs predictable. For smaller teams, the community edition covers basic encryption and key management but drops the Kerberos integration and advanced audit logging.