Time Sync in Ottawa: What Actually Works
Most people in Ottawa don't think about time zone synchronization at all until something breaks. A server logs a meeting at 9:00 AM when it actually happened at 3:00 PM. A scheduling tool double-books a conference room. A forensic analysis of system events becomes impossible because the timestamps don't align across systems. These problems are real and expensive. Ottawa Ontario Canada Time Zone Synchronizing The Nations Capital With Precise Time isn't just about setting your clock right. It's about ensuring every system, service, and person operates from the same reference point. The national capital is a hub for government operations, financial services, telecommunications, and critical infrastructure. If any of those systems drift, the ripple effects show up fast.
Ottawa Ontario Canada Time Zone Synchronizing The Nations Capital With Precise Time
The practical approach starts with NTP — Network Time Protocol. That's the standard most people already use without realizing it. Windows does it by default. Linux does it by default. iOS and Android do it by default. The question isn't whether to use it, it's whether your implementation is correct. Here's what I learned the hard way. In 2019 I was consulting for a mid-size healthcare organization that ran three separate databases across two physical buildings in Ottawa. Each database server had NTP enabled but pointed to different upstream pools. One hit the local NRC Canada pool. Another hit an international pool. A third was set to a corporate NTP server that hadn't been maintained since 2014. The result was a 1.8-second drift between systems during audit season. Not catastrophic on its own. But when you're reconstructing a patient medication timeline for a regulatory review, 1.8 seconds is enough to make two independent events look simultaneous when they weren't. The fix wasn't complicated. I pointed all servers to the same pool — pool.ntp.org with the -g flag for GNU NTP to allow large initial adjustments — and set the NRC's Canadian time servers as a secondary fallback. server 0.ca.pool.ntp.org, server 1.ca.pool.ntp.org, server time.nrc-cnrc.gc.ca. Done. The drift dropped to under 10 milliseconds within 24 hours.
But there's a catch that most guides skip. NTP assumes a reasonably symmetric network path. In Ottawa, that's usually fine for enterprise LANs. It's not fine if you're syncing through a VPN that routes through a data center in Vancouver or through a satellite link. Latency asymmetry introduces systematic error. I've seen setups where the VPN encrypted traffic added 40 milliseconds one way and 120 milliseconds the other. The NTP algorithm can compensate partially, but not completely. In those cases you need to either route time sync traffic directly or use a local stratum-2 server as a trusted intermediary. Another thing people miss: clock discipline matters more than clock accuracy in the short term. A disciplined clock that drifts predictably is easier to work with than one that jumps around. The NTP panic threshold (the maximum offset allowed before NTP refuses to adjust) is typically 128 seconds. If your clock has drifted past that, the daemon won't touch it. You have to manually set the time once using something like chronyd -q or ntpd -q, let it stabilize, then restart the service normally. For systems that need higher precision than NTP provides — financial trading platforms, scientific instruments, broadcast equipment — you'd look at PTP (Precision Time Protocol, IEEE 1588). PTP can achieve sub-microsecond accuracy on a properly configured LAN. The tradeoff is that it requires managed switches that support hardware timestamping and a dedicated grandmaster clock. Most Ottawa offices don't need this. The government buildings down Wellington Street sometimes do.
Get the Full Details

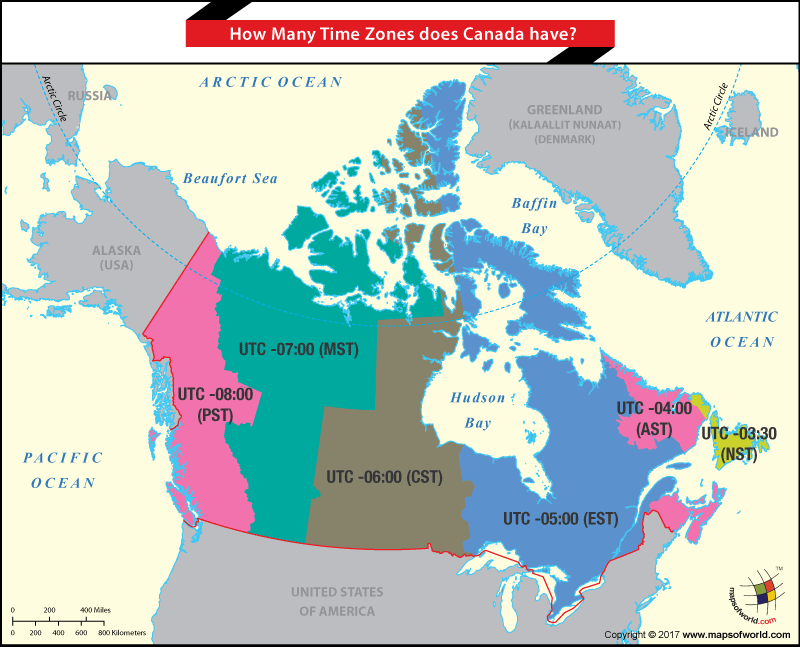
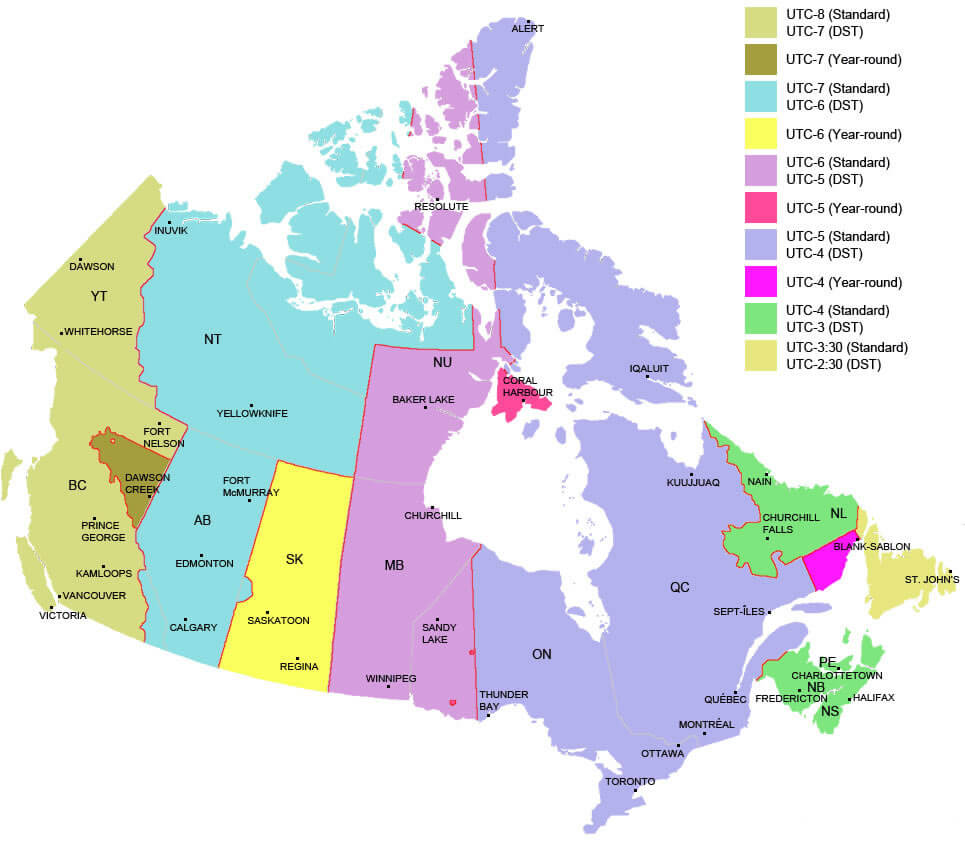
There's also the daylight saving time question. Ottawa observes Eastern Time, switching between EST (UTC-5) and EDT (UTC-4). The spring-forward and fall-back transitions are where most manual time zone configurations fail. I've seen Docker containers hardcoded to UTC that logged correctly until DST hit, at which point their local time interpretation became wrong while their UTC time remained fine. The hosts themselves were still synced. It was the application layer that broke. The workaround is simple: never rely on the system clock for local time representation in software. Store everything in UTC. Convert to local time at the presentation layer only. If you're managing a single workstation, the built-in time settings in Windows or macOS are adequate. Check that automatic time zone detection is on, verify that the NTP server is set to time.windows.com or equivalent, and run w32tm /query /status every few weeks to confirm your offset stays under 500 milliseconds. That's well within acceptable range for general use. For server environments, I recommend chrony over the older ntpd on Linux. Chrony handles intermittent connectivity better, warms up faster after a reboot, and works correctly on virtual machines where NTP traditionally struggled with clock speed changes. CentOS, RHEL, and Ubuntu all ship it as the default time service now. The configuration is straightforward: define your upstream servers, enable the local stratum if you're acting as a time reference for other machines on your subnet, and monitor with chronyc tracking.
The one scenario where all of this falls apart is when you're dealing with air-gapped systems or systems behind strict firewalls that block UDP port 123. I worked on a project for a federal agency where the time sync requirement crossed a classified boundary. The solution was a time-signaling appliance — a physical device that receives GPS-derived time and outputs NTP on a dedicated VLAN. No network path needed. Just a line-of-sight GPS antenna on the roof. Those things cost about $3,000 to $8,000 depending on the spec. Not something you pick up at a big-box store. For most people in Ottawa, getting your time right comes down to three things: use a single reliable NTP source, verify it's working periodically, and never hardcode local time into your applications. The rest is detail work for specific environments. If you need a tool to check your current sync status on Windows, w32tm /stripchart /computer:localhost /samples:5 will give you a five-sample deviation readout. On Linux, chronyc stats or ntpq -p shows your active peers and offsets. Both commands take about ten seconds to run and tell you everything you need to know about whether your system is actually synchronized or just pretending to be.