Why These Two Certs Confuse People
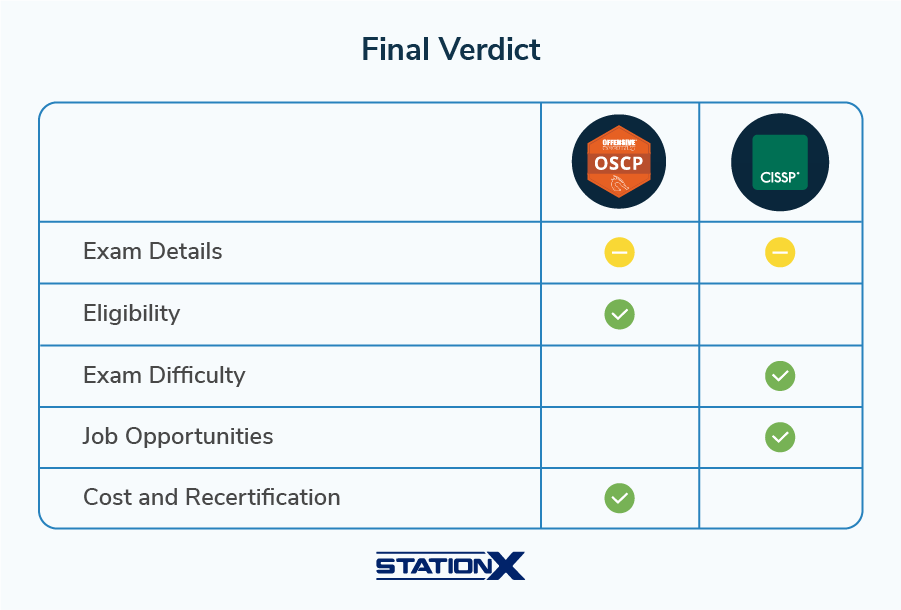
You'll see a lot of comparison articles that treat OSCP and CISSP like they're competing for the same job, which they aren't. One tests whether you can break into a network. The other tests whether you can design a security program for an enterprise. They live on opposite ends of the spectrum and hiring managers use them for completely different reasons. The OSCP is a hands-on, 24-hour practical exam run by Offensive Security. You get a virtual environment, you try to compromise multiple machines, and you write a report. There's no multiple choice. You either get in or you don't. The CISSP is a (currently computer-adaptive) multiple-choice exam covering eight domains of security practice, administered by (ISC)². It's knowledge breadth, not hands-on depth. I spent three weeks grinding HackTheBox machines for my OSCP attempt. I failed on the first try because I kept going down rabbit holes on a single box instead of moving to the next one. The exam rewards time management more than technical brilliance. That single insight changed everything. Once I switched to a rotation strategy, hitting each machine for maybe 20 minutes before bouncing, I cleared it on my second attempt. The pass rate after remediation is roughly 65 percent, not the 10 to 20 percent some people throw around online.
The CISSP is a different beast entirely. It's not about knowing every tool or command. It's about thinking like a manager. The exam will ask you what a security professional should do, not what you'd actually do in a real incident. There's a huge difference. I remember one question asking about the order of operations when responding to a data breach. The expected answer was always about process and policy first, not technical containment. It felt wrong if you were thinking operationally. That's the trap. The CISSP exam wants you to answer through the lens of risk and governance, even when your instinct says otherwise. Prerequisites matter more here than most people realize. For the OSCP, Offensive Security doesn't formally require anything before you take the exam. They recommend the Penetration Testing with Kali Linux (PWK) course, but they won't turn you away. For the CISSP, you need five years of documented experience in at least two of the eight domains, or four years plus a certification like the CCSFP or CEH. If you don't have the experience, you can still pass and become an (ISC)² associate, but you won't earn the full credential until you document your hours. I knew someone who passed the CISSP at 23 with no experience and had to wait three years before they could actually call themselves a CISSP. That detail trips people up constantly. The cost difference is significant too. The OSCP exam bundle runs around $1,649 and includes 90 days of access to the PWK lab environment. You can extend lab access for another $549 if you need more time. The CISSP exam is $749, but you also need to pay an annual maintenance fee of $125 and commit to 40 CPE credits per year to keep the certification active. Over a decade, that adds up to nearly $2,000 in maintenance costs alone. The OSCP doesn't expire, though some employers prefer it to be less than three years old when they see it on a resume.
Here's something most comparison pieces won't tell you: the CISSP is often a hard requirement for certain government and defense contractor roles in the US, specifically under DoD Directive 8570. It's a gatekeeper credential. You can be the best pentester in the room, but if a job posting says CISSP required, your resume gets filtered out. The OSCP, on the other hand, gets you past the technical screen for red team and penetration testing roles. It signals that you can actually do the work. One counter-intuitive thing about the OSCP is that the report matters as much as the compromise. I lost points on my first attempt not because I missed boxes, but because my report format didn't meet their strict requirements. They want a very specific structure: executive summary, methodology, findings with proof, and a remediation section. If your screenshots are cropped wrong or your evidence isn't clearly labeled, they can mark it invalid. It's not a suggestion, it's a grading rubric. Read the OSCP Exam Policies document before you touch a single box. The CISSP has its own hidden complexity. The adaptive exam means the difficulty adjusts in real time based on your answers. If you're answering correctly, the questions get harder. If you're answering incorrectly, they get easier. This makes score comparison across different test dates nearly impossible. You can't say you scored higher than someone who took the exam last month because the baseline shifted. The minimum passing standard is set at 330 out of 500, but that number means different things depending on how the algorithm calibrated your section.
Get the Full Details
Study time expectations are wildly different. For the OSCP, plan for 100 to 200 hours of lab work if you're starting from scratch, spread over two to three months. The work is exhausting. You'll be reading PDFs at 2 AM, running nmap scans that return nothing, and feeling like you're learning nothing. That's normal. The lab environment is intentionally challenging. For the CISSP, most people budget 100 to 150 hours of structured study over six to eight weeks using a resource like Sybex's official study guide or Ian Phillips' video course. There's also a practical consideration about career stage. Early-career security professionals, say zero to five years in, will get far more ROI from the OSCP. It teaches you actual skills and proves you can operate in a hands-on capacity. Mid to late career professionals, especially those moving into management, compliance, or architecture roles, benefit more from the CISSP. It's a signal that you understand the business side of security, not just the technical side. I worked with a team member who held both certifications and tried to use the CISSP to justify skipping hands-on training for a technical role. It didn't work. The CISSP doesn't teach you how to exploit a buffer overflow or pivot through a segmented network. It teaches you how to write a risk assessment for one. Similarly, I've seen OSCP holders struggle in boardroom settings where the conversation is about compliance frameworks and security governance. The certifications complement each other, but neither covers the other's territory.
The job market reality is straightforward. In the US and many other markets, a CISSP-certified security manager will typically earn more than an OSCP-certified penetration tester at similar career levels. But that's partly selection bias, since the CISSP correlates with seniority. Entry-level pentesters with OSCPs often out-earn entry-level security analysts who happen to hold a CISSP, though the gap narrows quickly as experience accumulates. If you're trying to decide which one to pursue first, ask yourself what your next job actually requires. Check the job postings. If they mention penetration testing, Burp Suite, Metasploit, and "red team" in the same sentence, go for the OSCP. If they mention risk management, governance, compliance frameworks like NIST or ISO 27001, and "security program," the CISSP is the play. Don't chase prestige. Chase relevance to the role you're targeting. One final practical note about the CISSP exam format change. As of April 2024, (ISC)² moved to a new adaptive testing format for the CISSP. The old CAT (computerized adaptive testing) model is gone. Now every candidate gets a fixed set of questions, but the test still adjusts difficulty mid-exam based on your responses. This means the experience feels different than it did even two years ago. Study resources that focused heavily on the old adaptive strategy may need revision. Stick to materials published after 2024.
Neither certification is a shortcut. Both demand real effort, and both are respected for different reasons. The confusion only happens when people treat them as interchangeable. They aren't.