The Reality of Getting Certified in Penetration Testing
Most people walk into this decision blind. They see a job posting that says OSCP preferred and assume that is the only path forward. It is not. The landscape has shifted in the last five years, and the assumption that one certification solves everything will cost you time and money. I spent three days on a practical lab last year hitting a wall with a PostgreSQL enum that should have been trivial. The service was running on a non-standard port inside a VM that had no internet access. Every search I ran required a VM reimage because my local tools kept conflicting with the provided Kali environment. I ended up writing a small Python script that grabbed the service banner and pushed it to a reachable staging server through a manual HTTP tunnel so I could search offline documentation. Took forty minutes. That is the kind of thing these exams do to you.
Oscp Vs Certifications Which Path Is Right For Your Cybersecurity Career
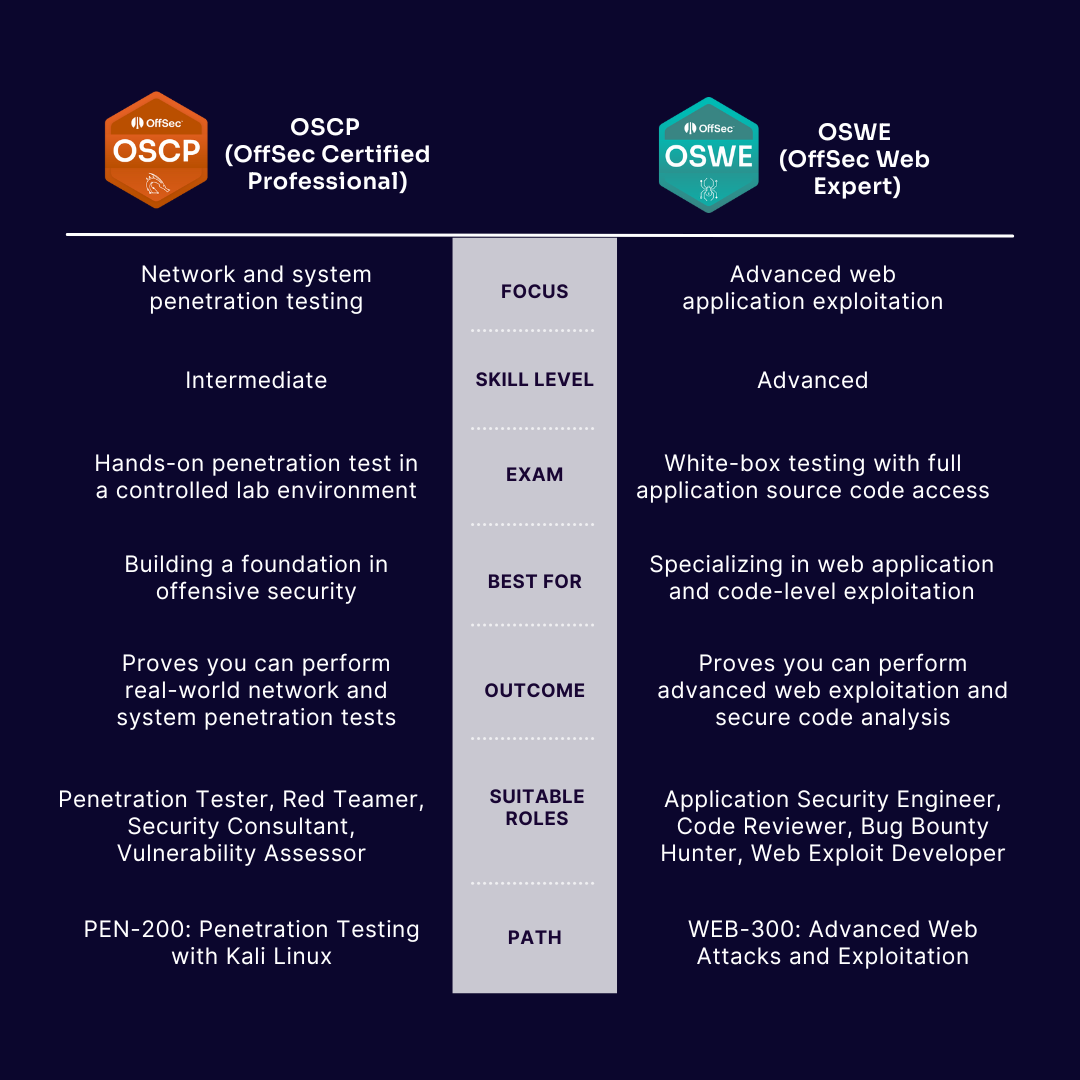
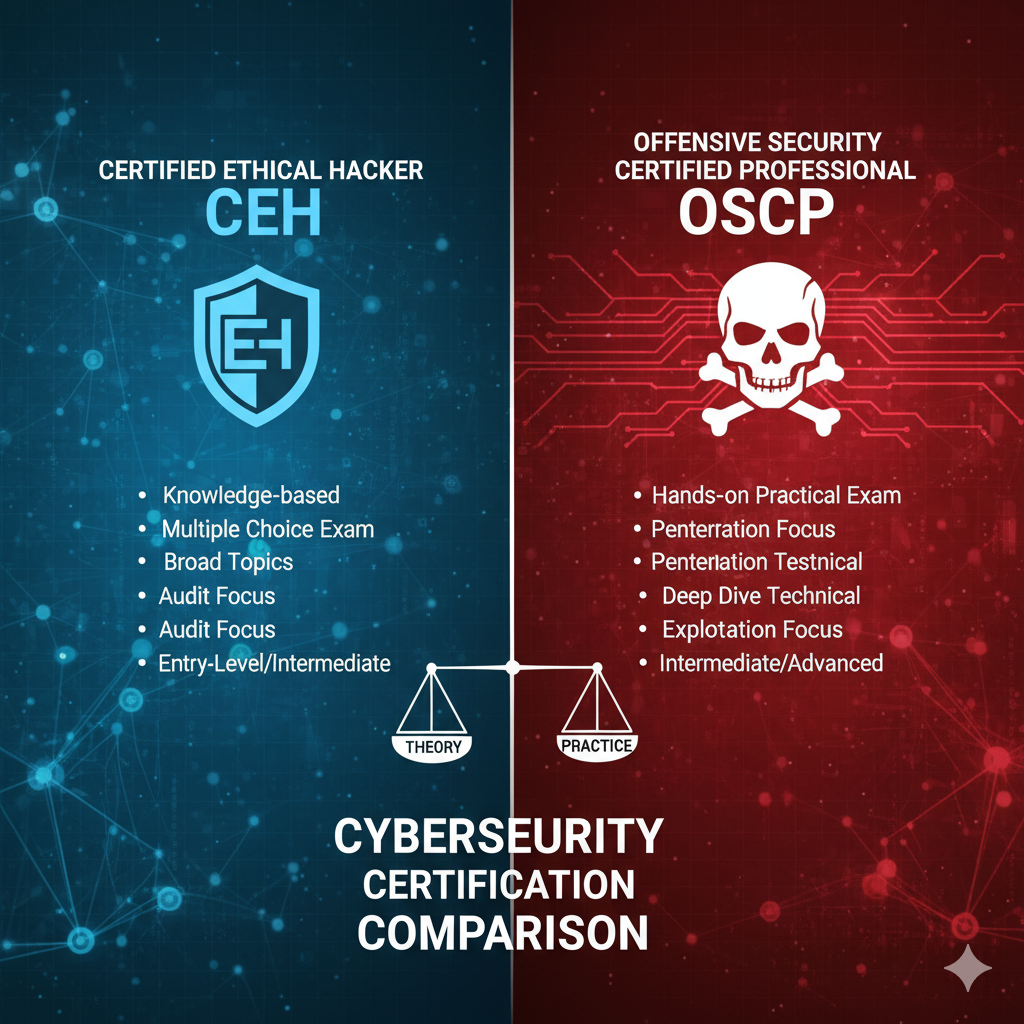
The OSCP, officially the Penetration Testing with Kali certification from Offensive Security, is a hands-on exam. You get 24 hours to compromise five to seven machines and then another 24 hours to write a professional report. The pass rate hovers around 65 percent on first attempts, though that number varies depending on how much practical experience you bring with you. The exam is designed to test your ability to persist when standard tooling fails, not just your knowledge of individual exploits. Other certifications occupy different spaces. The CompTIA PenTest+ covers the same theoretical ground but asks it in multiple-choice and performance-based question format. It takes about two weeks to study for if you already have a Security+ or equivalent foundational knowledge. You can take it at a Pearson VUE center. The GPEN from SANS goes deeper into methodology and reporting structure, and the price tag reflects that route. The CEH is largely useless for actual penetration testing work despite its name. It tests recognition of tools and concepts rather than the ability to execute them. The practical difference between these options becomes obvious when you sit in an interview. An OSCP tells a hiring manager you can sit down in front of an unknown network and figure out a path to a shell without guidance. A PenTest+ tells them you understand the terminology and the compliance frameworks behind testing. Neither is wrong. They signal different things.
I once worked with a junior analyst who held the OSCP but could not write a clean executive summary for a client engagement. Their technical work was solid, but the report they produced read like a raw notes dump. The engagement manager had to rewrite half of it before it went to the customer. The OSCP does not test report quality beyond the requirement to submit something readable. That gap exists in every hands-on cert right now. Here is a detail most guides skip. The OSCP lab environment includes a mix of Windows and Linux boxes, but the difficulty distribution is uneven. In my experience, roughly 60 percent of the machines on the exam lean toward traditional privilege escalation paths on Windows. The remaining 40 percent throw in Linux misconfigurations, Docker escapes, or kernel exploits that require more effort. If you have only practiced Windows chains, you will hit a wall on the Linux side that most study guides underrepresent. The GIAC OSWE takes a different angle entirely. It focuses on web application exploitation rather than network-level attacks. You receive source code and must find and exploit vulnerabilities in it. This is worth considering if your target role is web app security rather than general penetration testing. The OSWE pass rate is lower than the OSCP because the scope is narrower and the bar is steeper, but it maps directly to roles that pay a premium.
Get the Full Details

Let me address what I would tell someone who is asking this question today and has zero professional experience. Start with the Network+ and Security+ if you do not already hold them. They are not glamorous, but they fill the gaps that will slow you down later. Then move to the OSCP if your goal is general offensive security. If you already have the foundations and want to break into web app security specifically, go straight to the OSWE or a series of bug bounty platforms like Hacker One or Bugcrowd to build a public profile. The portfolio matters more than the cert in that lane. There is a real downside to the OSCP that few people mention. The exam is hard on your schedule. You get a 90-day access window to the online labs. Most people spread their study over six to eight weeks, putting in four to six hours daily. Some burn out by week five because they treat it like a part-time job when it requires more mental stamina than that. I know people who bombed the exam because they pushed for a second attempt too quickly without addressing the root cause of their first failure, which was usually weak note-taking discipline rather than lack of technical skill. The exam format itself changed recently. The old 24-hour exam with a pass mark of 700 out of 1000 points is gone. The current version uses a points-based system across multiple challenge types, and the threshold adjusts based on the exam form you receive. The reporting portion still carries significant weight. You can technically pass the technical portion and still fail the course because your report does not meet Offensive Security standards. I have seen this happen more often than the forums would suggest.
Cost is another factor. The OSCP bundle runs roughly 1,600 dollars, which includes the course materials and the exam attempt. Study resources outside the official curriculum add another two to four hundred dollars on average for books, third-party lab subscriptions, and practice exam platforms. The SANS route at a similar level costs ten times that amount. The GIAC certifications run around 8,500 dollars per exam when paid out of pocket. Budget matters, and assuming your employer will cover it is a gamble unless it is written into your contract. One counter-intuitive insight: having multiple lower-tier certs sometimes looks worse to technical hiring managers than having a single strong one. A resume stacked with CompTIA certs but no hands-on proof signals that the candidate collects credentials rather than builds skills. The OSCP earns respect because of the effort required to clear it. Pair it with something like a modern cloud security credential if you want to signal breadth, but avoid the credential hoarding trap. If you are working full-time while studying, block out a consistent window each day. Inconsistency is the fastest way to lose retention. I tracked my progress using a simple spreadsheet where I logged each lab machine, the techniques I used, the ones that failed, and the exact commands that finally worked. That spreadsheet became the primary reference during the exam itself. I brought it into the exam room because the format allows external notes. Having your notes organized is as important as knowing the material.
The field is moving toward practical validation anyway. Employers are tired of seeing paper certifications that do not correlate with ability. Platforms like PentesterLab and TryHackMe have made foundational practice accessible, and the newer Practical Security Professional certifications from vendors like eLearnSecurity are gaining traction for specializing in web application testing. The ecosystem is fragmenting in a way that makes the OSCP still relevant but no longer the only credible option.