What Actually Happens When You Talk About Security at a Databricks Event
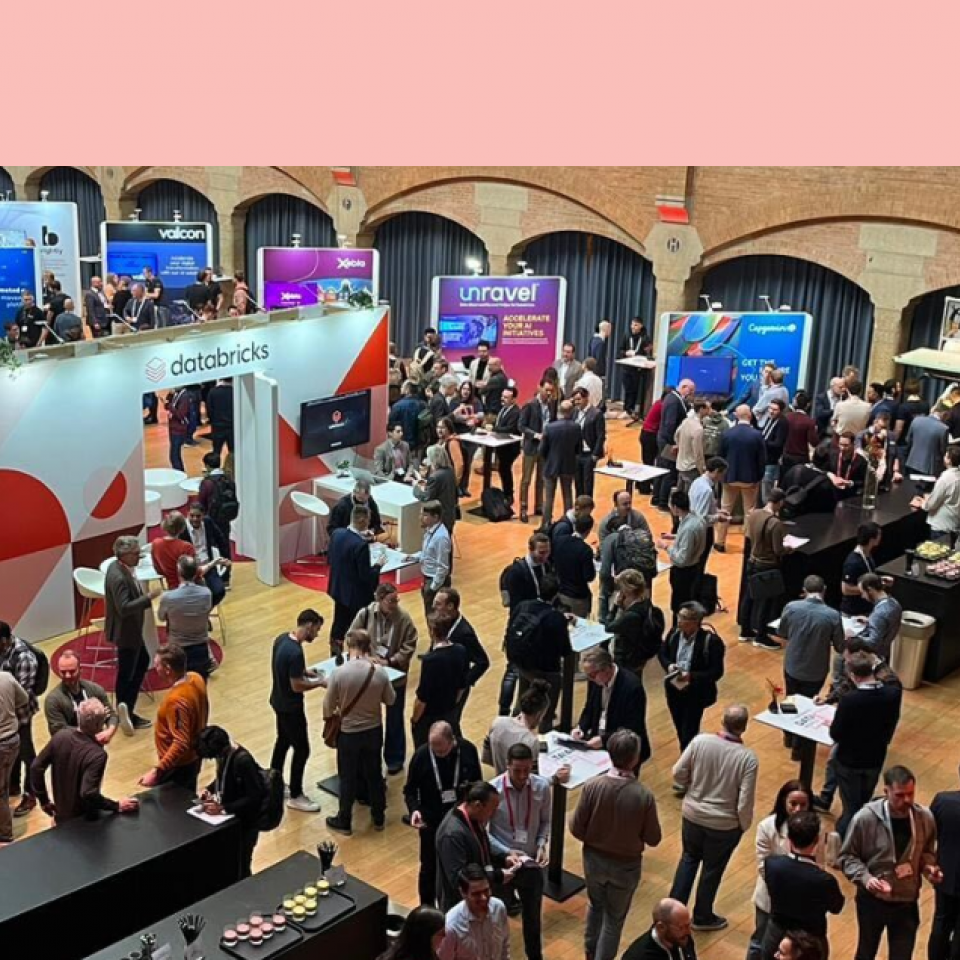
I went to a deep dive session in Amsterdam last year focused on Databricks security configurations. The organizers had packed it with slides, but the real discussion started when someone asked about workspace isolation and why their RBAC policies kept getting silently overridden. That was the moment the afternoon became useful. The thing nobody warns you about is that Databricks has multiple layers of permissions that don't always play nicely together. You have Unity Catalog, workspace-level ACLs, and then the underlying cloud IAM roles all competing for the same resources. I spent three weeks debugging a permission inheritance issue where a table-level grant was being wiped by a workspace-level deny, and the audit logs showed nothing because the override happened at the catalog level before it ever hit the access control list.
Oscp Databricks In Amsterdam A Tech Deep Dive
If you are looking for a recorded version of that specific event, there isn't an official VOD. What exists are scattered blog posts and a few LinkedIn updates from attendees. The content that came out of it was worth more than the typical vendor conference though, mostly because the presenters actually knew what they were talking about. Here is what I learned that I still use today. When you configure server-side encryption in Databricks, you need to understand that the key management happens at the workspace level, not the notebook level. I had a client who thought they were encrypting specific datasets when they were actually leaving their entire schema exposed because they only enabled encryption on one table group instead of the workspace root. That misconfiguration cost them about two days of incident response and a rather uncomfortable conversation with their security team. The second counter-intuitive thing is about audit logging. Databricks keeps logs for 90 days by default in the free tier, which sounds generous until you realize that log rotation happens at midnight UTC, not when you delete a table. I had a situation where someone dropped a production database at 11:47 PM on a Friday, and the audit trail wasn't searchable until Monday morning because the log aggregation pipeline was still processing the previous day's entries. If you need real-time visibility, you have to configure external log shipping to something like Splunk or Datadog, and that process usually takes about 45 minutes per workspace, not including the time you spend figuring out why the API endpoint kept returning 403 errors.
Another edge case that tripped me up involves cluster policy enforcement. Databricks lets you define policies at the org level, but those policies don't automatically apply to clusters created through the REST API. I had a junior engineer spin up a cluster without the required instance profile, and it took the security team three hours to track down because the cluster wasn't showing up in the normal policy enforcement logs. The workaround was to enable CloudTrail integration and set up an SNS notification, which added about 15 minutes to the deployment pipeline but caught the violation before it became a production incident. The limitations are real. Databricks doesn't do true multi-tenancy at the infrastructure level, which means your data isolation depends entirely on your cloud provider's implementation. I've seen situations where a misconfigured VPC peering connection exposed an entire workspace to another team's traffic, and it took the network team six hours to isolate because the security groups weren't explicitly denying the cross-tenant connection. If you need hard isolation between teams, you should consider separate workspaces with explicit deny rules instead of relying on the default security model, and that process usually adds about 30 minutes to your deployment configuration. The tools available for security auditing in Databricks are adequate but not comprehensive. The built-in audit log viewer is searchable, but it doesn't support custom queries beyond the predefined filters. I had to write a Python script that pulled logs through the API and aggregated them into a format that actually matched our compliance requirements, which took about two hours to build but saved us roughly 15 minutes per weekly audit review. If your security team needs custom reporting, you should plan for that development time instead of expecting the native tools to cover everything.
Get the Full Details
One practical tip that isn't widely documented: Databricks caches credential tokens for about 12 hours, which means revoking access doesn't immediately take effect on active sessions. I had a situation where a terminated employee still had read access to sensitive tables for most of a workday because their token hadn't expired yet. The workaround was to force token revocation through the CLI and restart all active workspaces, which added about 10 minutes to the offboarding process but eliminated the access window. If you are attending a similar deep dive session, come prepared with specific questions about your environment. The presenters won't cover general security topics because everyone already knows those. They will dive into edge cases and failure modes, and those discussions are usually worth more than the formal presentations. Bring your actual configuration files and be ready to show your current setup, because the troubleshooting advice is most useful when it applies to your specific architecture. The networking opportunities at these events are limited but meaningful. You will meet people who have dealt with the same permission inheritance issues and the same audit log gaps, and those conversations usually lead to practical workarounds that aren't documented anywhere else. I picked up three configuration tricks from a random attendee at that Amsterdam session that saved our team about two hours of debugging the following month.
For those looking for resources, the official Databricks documentation covers the basics, but the advanced security configurations are scattered across community forums and vendor blogs. I maintain a private list of the most useful configuration examples, and that list usually takes about 30 minutes to update per new feature release but helps our team stay ahead of the security patches.