
Getting Your Systems Locked Down Without Losing Your Mind
Most people treat cybersecurity like a product you buy and install. That's wrong. It's a continuous state of adjustment, and the tools you pick either help you maintain that state or they add complexity you don't need. Osci Powersc sits somewhere in between — useful if you understand what it actually does and where it falls short. I've spent years watching teams pile on security tools until their infrastructure is unmanageable. The ones that survive are the ones that focus on what matters. Powersc from Osci isn't a silver bullet, but it handles a specific gap that most commercial suites ignore. It focuses on persistent threat detection at the process and script level, which is where a lot of modern attacks live once they get past the perimeter. The way it works is by monitoring execution patterns rather than relying on signature databases. Traditional AV looks for known malware files. Powersc looks for behavior that doesn't belong, which means it catches novel attack vectors that haven't been cataloged yet. I ran into this firsthand during an engagement last year when a client's network was getting hit by a custom PowerShell-based implant. Their existing tools — EDR, SIEM, network IDS — were all blind to it because the payload was legitimate binaries with malicious scripts. Powersc flagged the anomalous process tree within twenty minutes of deployment, something the other tools missed entirely over a three-week period.
The setup isn't trivial. You'll need to deploy the collector agents across your endpoints and configure the behavioral baselines for your specific environment. A fresh install out of the box will generate a lot of noise. I typically spend the first week tuning thresholds and building allow lists for known legitimate processes in each environment. Budget about two days of hands-on time for a medium-sized deployment, more if you have heterogeneous systems. Here's something most documentation doesn't emphasize: the detection quality drops significantly if you don't properly profile your environment before enabling aggressive detection modes. I've seen teams enable full monitoring on day one and then spend a week drowning in false positives until they disable the tool altogether. Profile for at least four hours across different workload types before switching to production sensitivity settings. The dashboard is functional but dated. It gets the job done if you know what you're looking for, but it lacks the intuitive visualization that newer platforms offer. You'll probably want to pipe the logs into your SIEM anyway for correlation with other security events.
There are real limitations you should know about. Powersc doesn't cover container or Kubernetes environments natively, so if your infrastructure runs primarily in cloud containers, you'll need supplemental tooling. The agent footprint is moderate but not negligible — expect about 300MB of disk usage and occasional CPU spikes during baseline learning phases. Cloud telemetry integration exists but feels bolted on compared to the depth available for on-premises endpoints. Another thing beginners miss: Powersc works best when combined with good endpoint hygiene. If your systems are running outdated software with known exploits, no amount of behavioral monitoring will save you from a straightforward drive-by compromise. Patch management and least-privilege access still matter more than any detection tool. For those looking to get started, the Osci website offers a trial version that includes thirty days of full functionality. I'd recommend using that trial period strictly for evaluation and baseline profiling rather than attempting a production rollout. The licensing is per-endpoint, which can get expensive at scale, so do the math on your total endpoint count before committing.
Get the Full Details
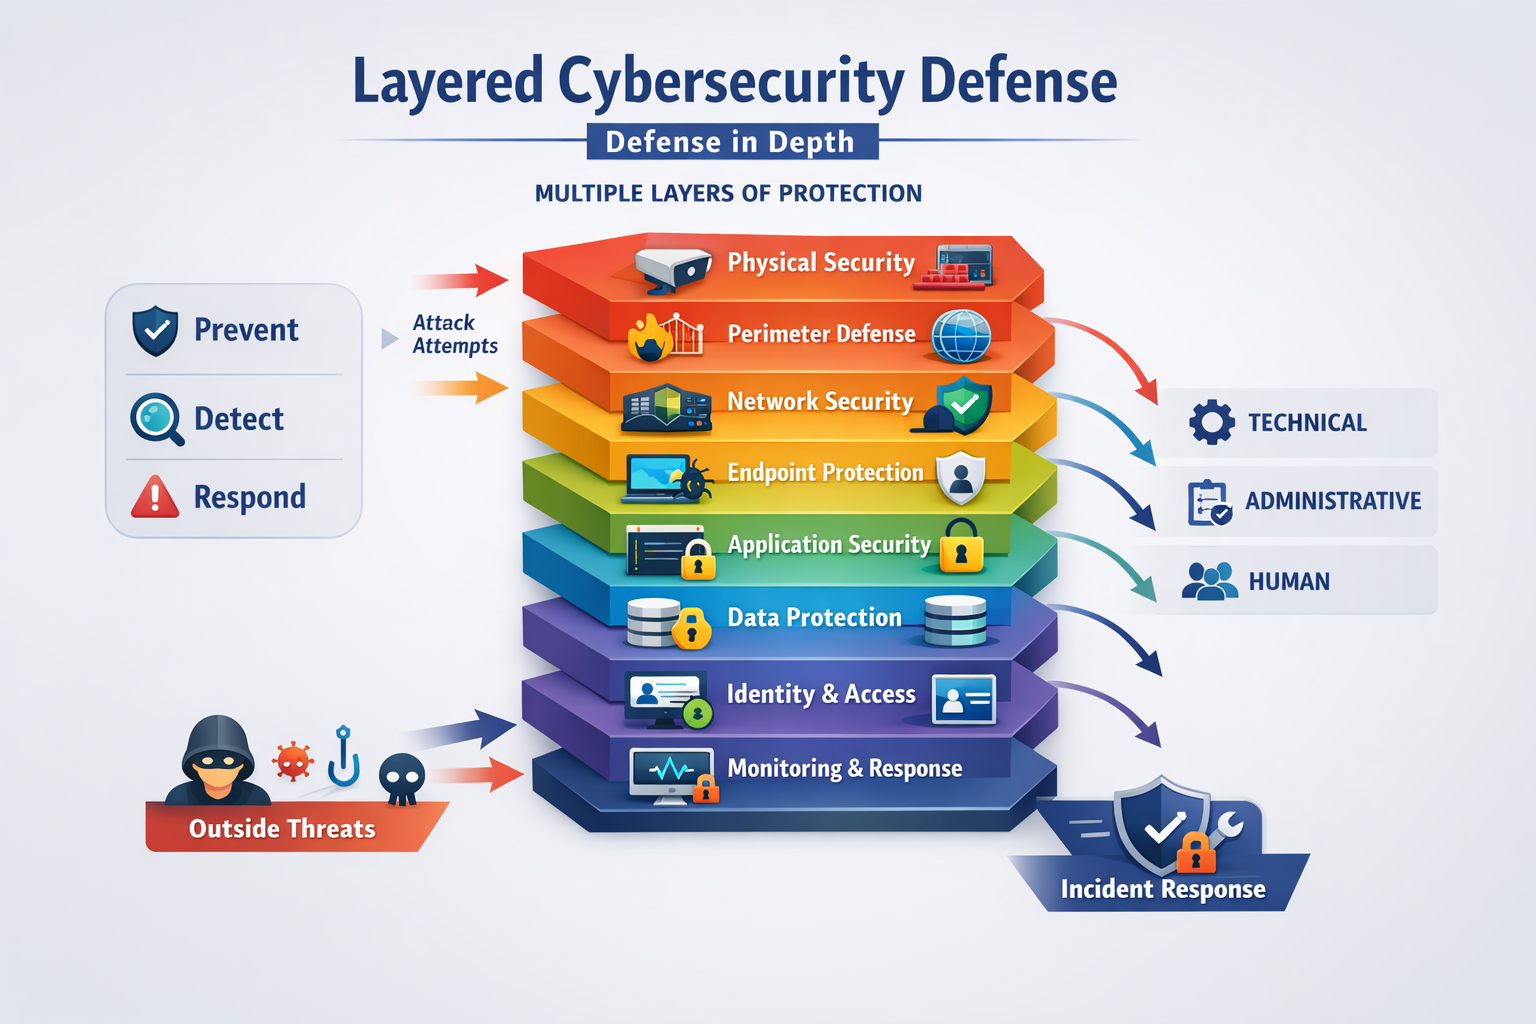
If your environment is primarily cloud-native with heavy container usage, you might be better served by tools like Trend Micro Cloud One or Prisma Cloud that have deeper cloud workload visibility built in from the ground up. Powersc excels in hybrid or on-premises environments where process-level threat detection fills a real gap. The key takeaway is that no single tool secures a system. Powersc handles the unseen layer — the stuff that slips past traditional defenses — but it needs to be part of a layered approach. Deploy it where behavioral monitoring adds value, tune it properly, and don't let it create a false sense of complete security.


