What Open Source Operating Systems Actually Give You
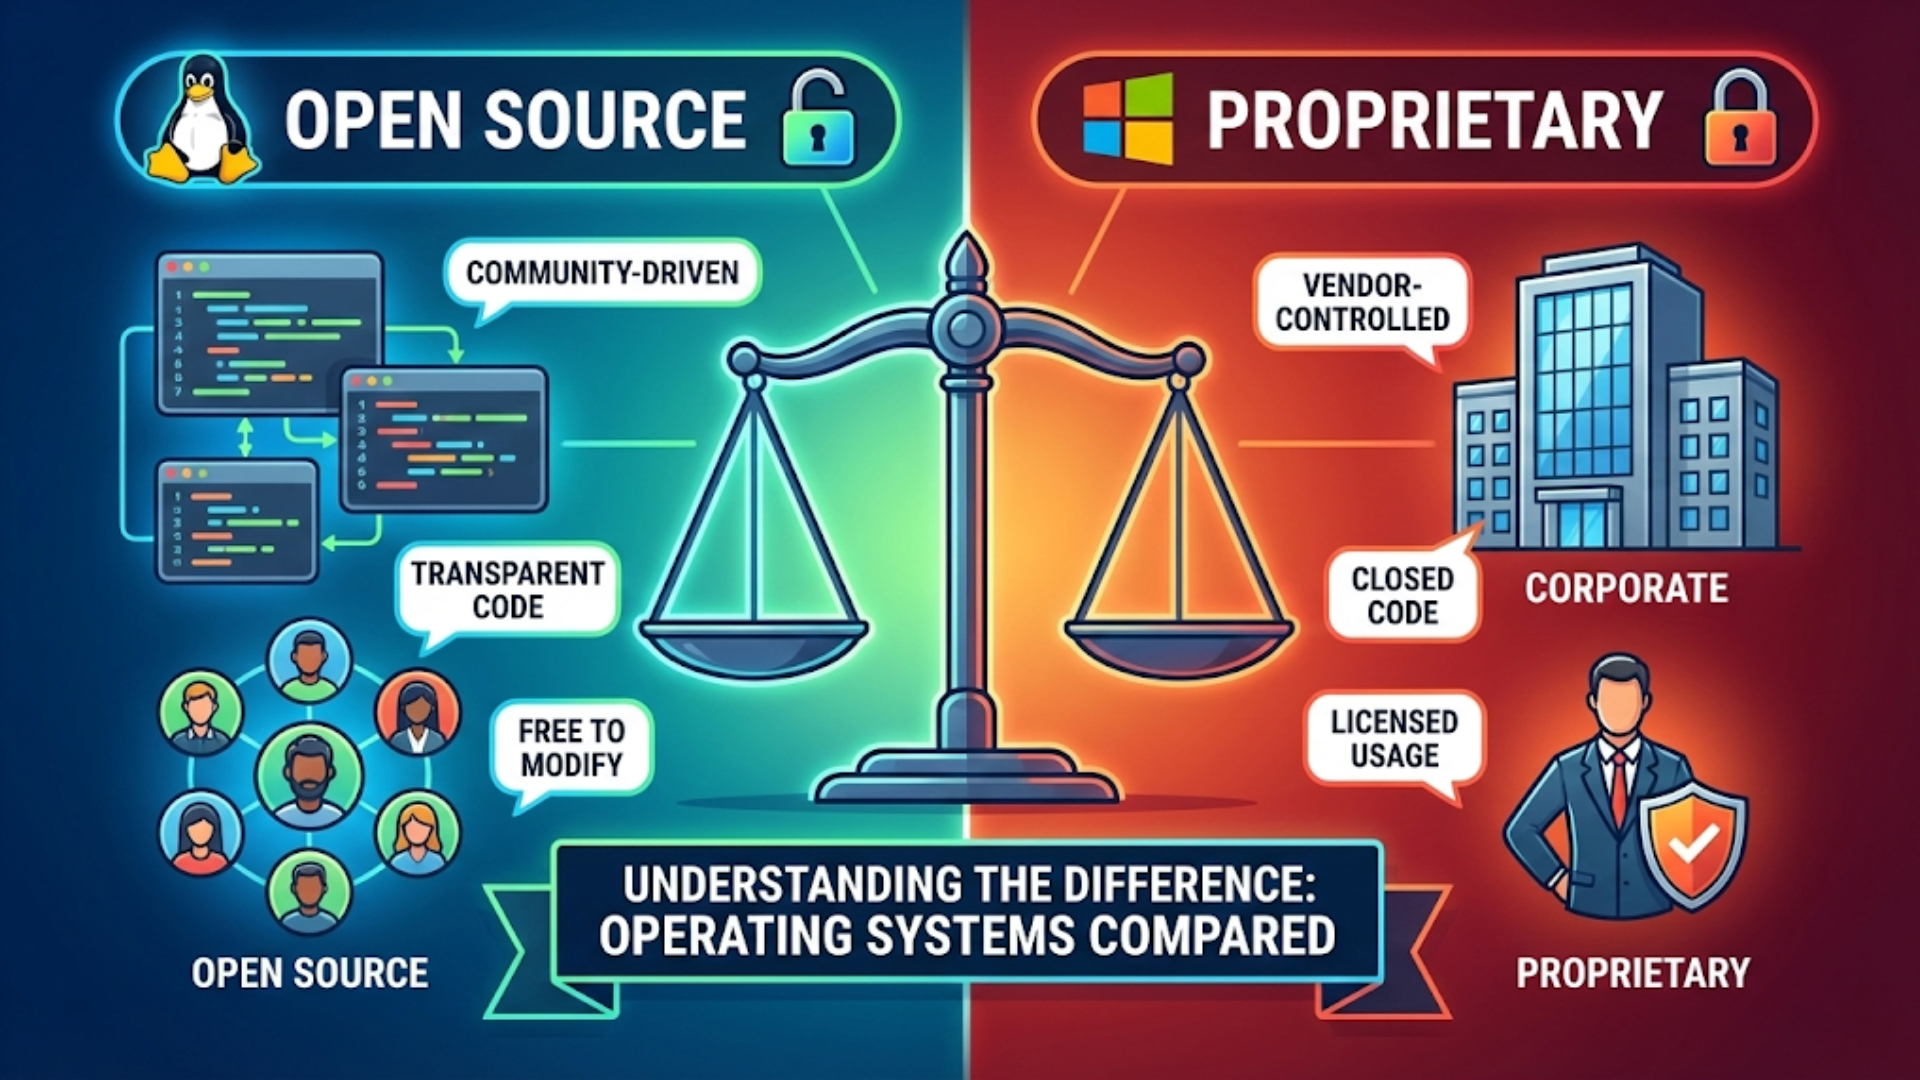
I spent six months running a Debian-based custom install on a fleet of thin clients at a small web shop. Not because it was trendy, but because the commercial licenses were eating into margins and the machines didn't need anything beyond a browser and an SSH session. What I learned wasn't about ideology. It was about maintenance windows, driver support, and the fact that "free as in beer" and "free as in speech" are two entirely different cost calculations. Open source operating systems are distributions where the kernel, system libraries, and often the desktop environment or server stack are released under licenses that permit modification and redistribution. Linux is the dominant family, but there's also FreeBSD, OpenBSD, NetBSD, Haiku, and a growing number of niche projects. The power unlock isn't mystical — it's the ability to strip a system down to exactly what you need, patch security issues without waiting for a vendor release cycle, and run the same OS from an embedded device to a cluster of bare-metal servers. In practice, the main benefit surfaces during incident response. When a vulnerability drops in a closed-source OS, you're usually waiting for a vendor patch. With an open source stack, you can pull the source, apply the fix yourself, rebuild the affected package, and deploy it across your environment in hours instead of days. I did this with a NULL pointer dereference in a custom kernel module on a production media streaming box. The vendor wouldn't touch it for six weeks. I patched it in a Tuesday afternoon.
The tradeoff is that nobody is holding your hand through it. Package management across distributions isn't uniform. A Debian-based system uses apt and .deb files. An Arch-based one uses pacman and PKGBUILDs. A RHEL derivative uses dnf and RPMs. If you're managing a heterogeneous fleet, this fragmentation becomes a real operational headache. I learned that the hard way when three different backup scripts failed on three different OS flavors in the same week.
Getting Started Without Breaking Anything
Start with a well-documented distribution if you're new to this. Debian Stable or Ubuntu LTS will give you predictable behavior and long support cycles. Avoid rolling release distros like Arch or openSUSE Tumbleweed for production work until you understand how package updates can unexpectedly change library versions and break compiled software. I made that mistake in 2019 when a glibc update on Arch broke a legacy Python service that my company depended on for internal reporting. The fix involved recompiling the service against the new ABI and rewriting three configuration paths. Took me two weekends. If you want to experiment safely, use a virtual machine first. VirtualBox, QEMU, or even multipass on Ubuntu will let you spin up a clean instance, break it, and delete it without affecting your host system. I routinely test new kernel parameters and systemd service configurations in VMs before touching anything on physical hardware. For server deployments, consider AlmaLinux or Rocky Linux if your workflow depends on RHEL compatibility. They're binary-compatible with RHEL and receive security patches for ten years. Fedora Server is another option if you want newer packages and don't mind a shorter support window. I run Fedora on my personal servers and AlmaLinux in production because the risk profile is different.
Get the Full Details
The Hidden Complexity Layer
Most people stop thinking about the OS after they get a desktop that launches applications. But the real complexity lives in the layers below. Init systems differ — systemd dominates now, but some distributions still support OpenRC or SysVinit. Container runtimes like Docker and Podman interact differently with cgroups and namespaces depending on the kernel version and apparmor vs. selinux profiles. If you're deploying containers, understanding how your OS handles namespace isolation matters more than you'd expect. Network management is another area where assumptions fail. NetworkManager is the default on most desktop distros, but server editions often use static configuration or systemd-networkd. Migration between these systems can cause temporary downtime if DNS resolvers aren't configured correctly during the transition. I had a staging server lose external connectivity for forty-five minutes because I swapped NetworkManager for systemd-networkd without updating the resolved.conf search domain. Filesystem choice also matters more than casual users realize. ext4 is the default everywhere, but XFS handles large files and parallel I/O better on servers. Btrfs offers snapshots and compression but has a more complex recovery path if something goes wrong. I switched a media server from ext4 to XFS and saw a 30 percent improvement in sequential write throughput for large video files. The same server on Btrfs with compression enabled actually slowed down because the CPU overhead of zstd on thousands of small metadata operations outweighed the space savings.
When Open Source OS Isn't the Right Call
Some workloads still require proprietary stacks. GPU compute with CUDA is NVIDIA-only and Linux-supported, but not all driver versions are open source. Some enterprise ERP systems only certify on Windows Server. Gaming on Linux has improved dramatically with Proton and the Steam Deck, but anti-cheat software in multiplayer titles frequently blocks Linux entirely. If your work depends on any of these, an open source OS will add friction that may not be worth the cost savings. Hardware support is another boundary. Some Wi-Fi cards, fingerprint readers, and exotic USB devices have no Linux drivers or only poorly maintained ones. I once spent three days trying to get a Realtek RTS522A card reader to work on a Dell laptop running Debian. The kernel driver existed but had a bug that caused hangs under heavy I/O. The workaround was blacklisting the module and using an external USB authentication device instead. That's the kind of problem you don't encounter with a commercial OS that has a support ticket system.
What Actually Changes When You Commit
The real shift isn't technical — it's cultural. You stop treating the operating system as furniture and start treating it as a tool you can modify. This changes how you approach troubleshooting. Instead of waiting for a vendor to acknowledge a bug, you read the source. Instead of accepting a default configuration, you audit it. Instead of assuming a feature exists because a marketing page says it does, you verify it in your own environment. I keep a personal wiki of the quirks I've encountered across Debian, Ubuntu, Fedora, and Arch. Not because I expect to forget them, but because each distribution makes different default choices and those choices compound over time. A journalctl setting that works on Fedora might not have the same syntax on Debian. A firewall rule that functions under firewalld breaks under nftables without adjustment. These details matter when you're migrating between systems or debugging a production issue at 2 AM. The ecosystem around open source operating systems has matured significantly over the past decade. Documentation is better. Community support is wider. Commercial backing from companies like Canonical, Red Hat, and SUSE means critical infrastructure isn't going to disappear overnight. But maturity doesn't equal simplicity. The work still falls on you, and the payoff is proportional to how much you invest in understanding the stack underneath your applications.