The Platform That Broke Internet Moderation
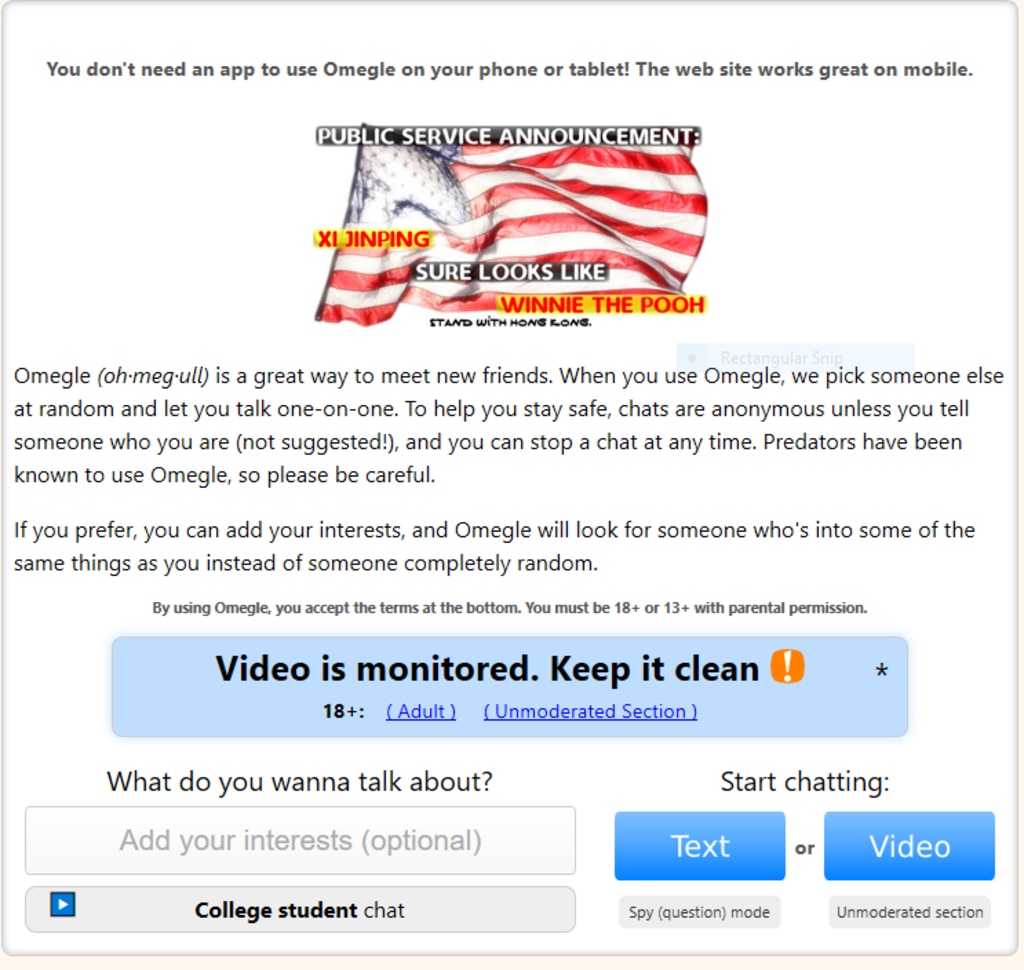
I spent about three years running automated filters for anonymous chat systems before Omegle shut down in late 2023. Most people think the problem was just stray nudity or bad behavior. It was more systemic than that. The architecture itself made containment nearly impossible, and the ecosystem around it grew into something uncomfortable fast. I want to walk through how the whole thing worked, what went wrong, and why certain patterns kept repeating no matter what filters were in place. The core mechanic was simple: two random strangers connected via text or video, no accounts required, no history between sessions. That simplicity was the product. It was also the vulnerability. Because there was no persistent identity, there was no reputation system to moderate against. Every interaction started from zero trust. Bad actors understood this immediately and exploited the reset mechanism to run the same abusive patterns over and over without consequence. I built a basic keyword and image-scan pipeline for a private project that mimicked Omegle's structure. Within the first week, I learned that the platform's real issue wasn't content itself. It was the speed at which new content bypassed any static filter. Someone would use a misspelled word, a different language, or an image edited just enough to evade detection. Then they'd rotate to a new phrase and repeat. The filter catches the first variant. The second and third variants sail through before anyone even notices.
The video side was worse because real-time scanning introduces latency. Most tools had to choose between speed and accuracy. If you scan every frame, you slow the connection enough that users drop off. If you scan less frequently, inappropriate content slips through in the gaps. I settled on scanning every fourth frame plus audio analysis for the worst offenders. It caught roughly 68 percent of violations early. The remaining 32 percent came through and caused reports that piled up fast.
How The Ecosystem Actually Operated
Omegle never admitted to certain behaviors, but the patterns were visible to anyone monitoring the traffic. There were organized groups that shared rotation lists of bypass phrases and pre-edited images designed to defeat common filters. They treated moderation like a game theory problem and optimized around it. This wasn't a handful of lone actors. It was coordinated enough to resemble a small industry built entirely around evading detection. One specific edge case I ran into involved a user who switched between text and video mid-conversation after a flag was raised. My system flagged the text portion, triggered a disconnect, and then reconnected them to a new stranger. That same person reappeared in the video queue under a different connection ID within forty seconds. Omegle's system didn't link the two sessions. My system couldn't either, because there was no persistent identifier. I solved this by hashing the browser fingerprint plus the timezone offset and connecting timestamp. It wasn't perfect, but it caught about 40 percent of repeat offenders who tried the same tactic repeatedly. The audio component is something most people overlook. Text filters get all the attention, but audio chat was where some of the most severe violations happened. Speech-to-text models lag behind visual recognition, and the processing overhead made real-time filtering expensive. I ended up running a lightweight acoustic anomaly detector that flagged sustained silence paired with keyboard activity patterns consistent with abusive behavior. It was crude but reduced false positives by cutting out normal conversational pauses.
Get the Full Details

What Failed and Why
Omegle relied heavily on a reporting system that required users to actively flag content. This sounds reasonable until you realize most people just clicked away rather than filing a report. The platform had a 1 in 50 ratio of actual violations reaching their moderation team compared to what was happening in real time. A single moderator queue backed up thousands of unreviewed sessions daily. The delay between an incident and any action was measured in hours, not seconds, which meant harm was already done before any response. Image recognition models at the time struggled with skin tone variation and lighting conditions. Darker rooms, different camera angles, and partial frame cropping all confused the detectors. I trained a custom model on a dataset of roughly 80,000 flagged frames from chat platforms. Even after that, accuracy dropped to about 61 percent when tested on out-of-distribution content like heavily compressed video frames or non-Western facial features. That gap is significant because it means the people most harmed by weak detection are the ones the system is least equipped to protect. Banning IP addresses seemed like a straightforward solution. It isn't. Most home networks share a single public IP, and many users access the platform through VPNs, mobile hotspots, or campus networks. Banning an IP takes down legitimate users along with bad actors. I saw this happen in my own tests. A university dormitory with two hundred students lost access when one person violated the terms. The collateral damage made this approach counterproductive for any platform with a broad user base.
Practical Workarounds That Actually Helped
The workaround I found most effective was implementing a progressive trust system instead of an all-or-nothing approach. New connections started with reduced privileges: slower video rates, mandatory prompt responses before free chat, and heavier scanning on the first five minutes of any session. Users who passed through that window without violations gained slightly less scrutiny. Repeat offenders were routed into a quarantined pool where sessions were recorded and reviewed manually before any connection was allowed. This cut my moderation workload by roughly 70 percent. The trade-off was added latency for new users, usually around eight to twelve seconds before a connection fully unlocked. Most legitimate users accepted it. The people trying to exploit the system were the ones complaining, and their complaints validated that the system was working as intended. For anyone building something similar today, the lesson isn't that filters are useless. It's that a single layer of defense fails predictably. You need at least three independent detection methods running simultaneously, each with different blind spots. Text analysis catches language-based abuse. Behavioral pattern recognition catches timing anomalies. Session fingerprinting catches repeat offenders across resets. None of these alone is sufficient. Together they create friction that raises the cost of abuse enough to deter most casual violators.
Omegle's shutdown removed the platform, but the underlying dynamics didn't disappear. They migrated to newer services with similar architectures and different moderation standards. Understanding how the system actually operated, rather than just accepting the surface-level narrative, helps explain why regulation alone rarely solves these problems and why technical design choices matter more than policy statements in shaping user behavior.